Just got back home last night after visiting the beautiful city of Mechelen Belgium, where i had the opportunity to speak at this years @brucon conference (AfterDark). Many thanks to the conference team for giving me that opportunity, and for putting on such an amazing event.
Excited to announce i well be speaking at @brucon next Thursday Sep 24 in the BruCON After Dark track at 8pm. My talk will be "CatSocks - Cellular AT Command Socks5 Injection Application" So please join me for my After Dark session at 8pm - https://t.co/5UaqvqmzoK
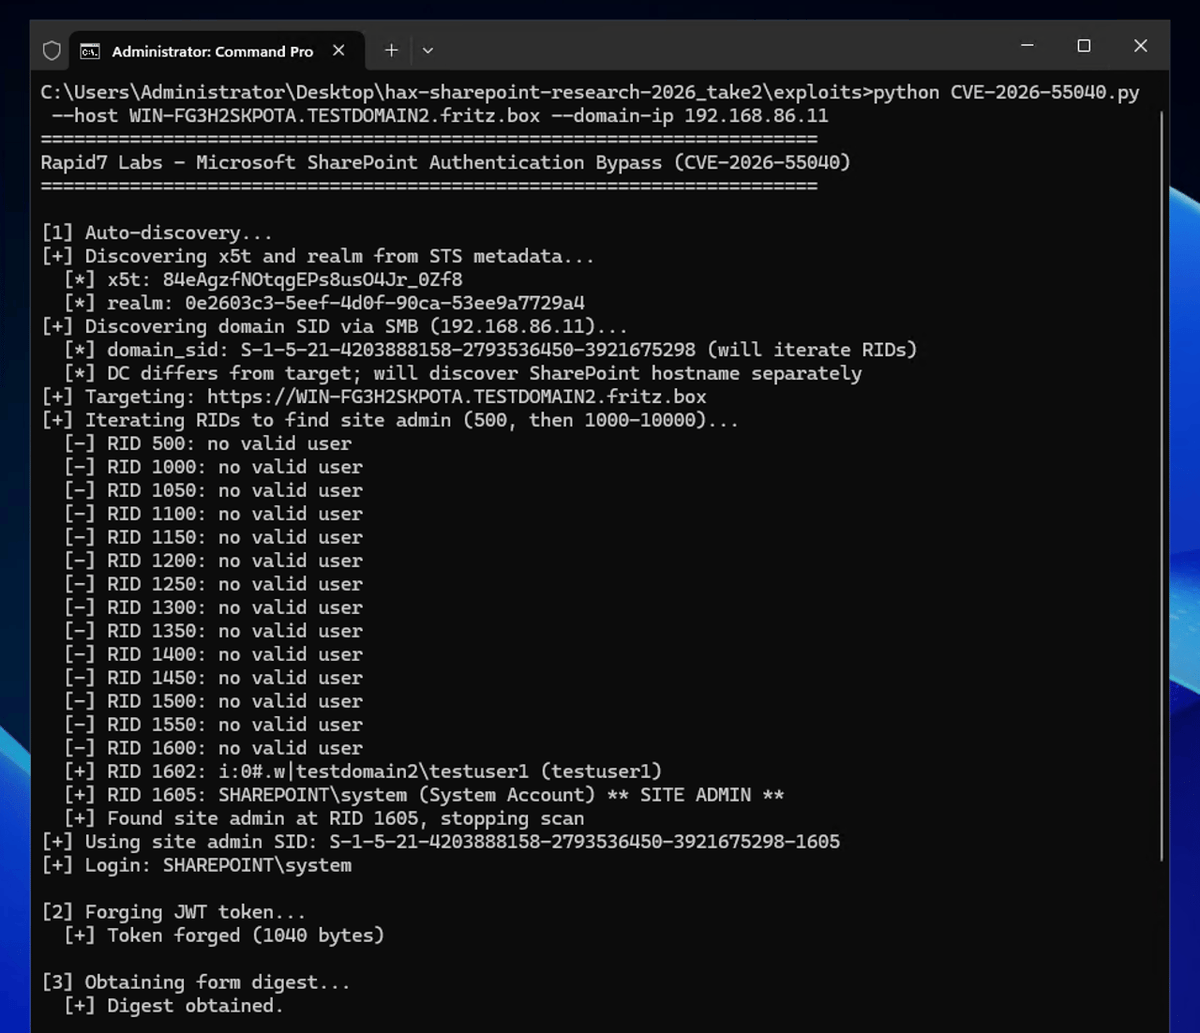
🚨 In July 2026, while conducting a 0-day research project against Microsoft #SharePoint, Rapid7 Labs discovered 2 new vulns that, when chained together, achieve unauthenticated RCE against a SharePoint server.
Join @Percent_X & Carlota Bindner at #IoTVillage to learn about MitM inter-chip attacks and cellular hardware defense in "Weaponization of Cellular Based IoT Technology"!
🗓️ Saturday of DEF CON | 16:30 - 17:30 📍 Stage 3
Been attending @defcon since DC10. Not sure if I am in a rut or addicted. Each year I sware I hate Vegas and not going back, but 30 days later I am planning for the next. This will be 9th year with @IoTvillage running hands-on hardware hacking. Looking forward to seeing everyone
🔓Thanks to an exposed server, Rapid7 researchers managed to pull down an attacker's entire toolkit: staged payloads, lure templates, testing files, campaign artifacts & more.
That sloppiness offered a rare view of a malware delivery pipeline, end-to-end: https://t.co/rVjy4QeZmx
I will be @CackalackyCon in Raleigh, NC on May 15–17, where I’ll be speaking https://t.co/FVjDeVIHUF
Also, a couple of my @rapid7 penetration team members and I will be running hands-on hardware hacking exercise. So join us and learn some fun hardware hacking techniques.
So just got back yesterday from #RSAC where i presented "Exploiting Cellular IoT Pathways to Compromise Trusted Access". I had an amazing time. Also, @CarlotaBindner and I released a new white paper on the subject. Please check it out- https://t.co/2GiioiwF51
Make room in your RSAC itinerary for Principal Researcher (IoT) Deral Heiland's session on how hardware hacking techniques exploit cellular IoT to gain trusted access & how organizations can better defend against these risks.
Get the details: https://t.co/xrYzhkV40A | @Percent_X
@dcuthbert He was brilliant mind and will be missed. He once helped me with editing and technical reviewing on a research paper i was writing years ago on exploiting Xerox firmware process attacks. His insight and guidance was amazing.
RSAC Conference is less than a month away, and I’m excited to announce that I’ll be speaking on March 24, 2026 at 1:15 PM PDT.
🎤 NCS-T09 – Exploiting Cellular IoT Pathways to Compromise Trusted Access
Session details: https://t.co/GHfvytudZ5
I hope to see everyone there !
I have starting to prep the @rapid7 hands-on hardware exercise for @defcon@IoTvillage. I have a plan and have started acquiring the needed devices and tools. More detail will be posted as we get closer to #hackersummercamp
CyberBay Conference in Tampa Florida is only a month away. Please join me on March 12th for a discussion on building out an IoT embedded device security testing program - https://t.co/IkIMBJ9Mpx
🚨 On 2/6/26, #BeyondTrust disclosed a critical RCE vulnerability affecting its Remote Support (RS) and Privileged Remote Access (PRA) products.
The flaw has been assigned CVE-2026-1731 and a near-maximum CVSSv4 score of 9.9.
More in the Rapid7 blog: https://t.co/2JDdnujQFd
@nmatt0 Me and a @CarlotaBindner have been doing research in this area also, we released a white paper and spoke at @BlackHatEvents
https://t.co/GR8Vg5LZiE
https://t.co/S7u7isAt8U
We will be releasing a white paper soon on weaponization of cellular for RSAC26
Keep up the good work !