CVE-2023-27997 tracks a RCE flaw in Fortigate SSL-VPN devices and reports suggest it is likely already being actively exploited. Update your devices asap!
Patches released in FortiOS firmware versions 6.0.17, 6.2.15, 6.4.13, 7.0.12, & 7.2.5. #xortigate
https://t.co/qcgPcVQFg4
Some say they feel nervous to use a password manager -- if that feeling is leading you to be less safe & reuse passwords (which btw is the easiest way for me to hack you bc that pw gets breached), then try this trick:
🧂Salt your password manager passwords🧂
Here's the trick:
⚠️ Patch now: CVSS 9.8 (Critical) SQLi in QNAP NAS, likely to be exploited by threat actors such as the operators of Deadbolt Ransomware as well as RaspberryRobin
https://t.co/OIr26KUrCa
Scans report by @censysio
https://t.co/FcZ0kVLydl
Seeing lots of confusion about LastPass breach of encrypted vaults.
The biggest risks for actually unlocking the vaults are:
- phishing your master password
- you having an ultra weak password, or something already known (ex: cred reuse or in a wordlist)
🧵1/n
DraftKings users saying accounts are hacked & stealing large sums from bank accounts. Many claim 2FA enabled so while it's possible this hack was cred stuffing + 2FA code stealing or SIM swap, could also mean DraftKings themselves are dealing w/ compromise.https://t.co/WabfEmcJbb
Excellent write-up about the recently patched #bufferoverflow vulnerability (CVE-2022-3602 & CVE-2022-3786) in #OpenSSL!
Affects clients using OpenSSL 3.0.0 - 3.0.6. “Note: OpenSSL 3 is not the same as SSLv3. This vulnerability exists only in OpenSSL Version 3 and not SSLv3.”
Interesting write up dissecting the behavior of multiple #malware operations after exploiting CVE-2022-22954 (a RCE vulnerability in #VMware Workspace ONE Access) to gain access!
This was patched back in April, but it’s still being actively probed for…
https://t.co/i61WcBaEEz
"Fortinet is aware of an instance where this vulnerability [CVE-2022-40684] was exploited, and recommends immediately validating your systems against the following indicator of compromise in the device's logs: user="Local_Process_Access"..." #patchnow
https://t.co/ZGCw0syapW
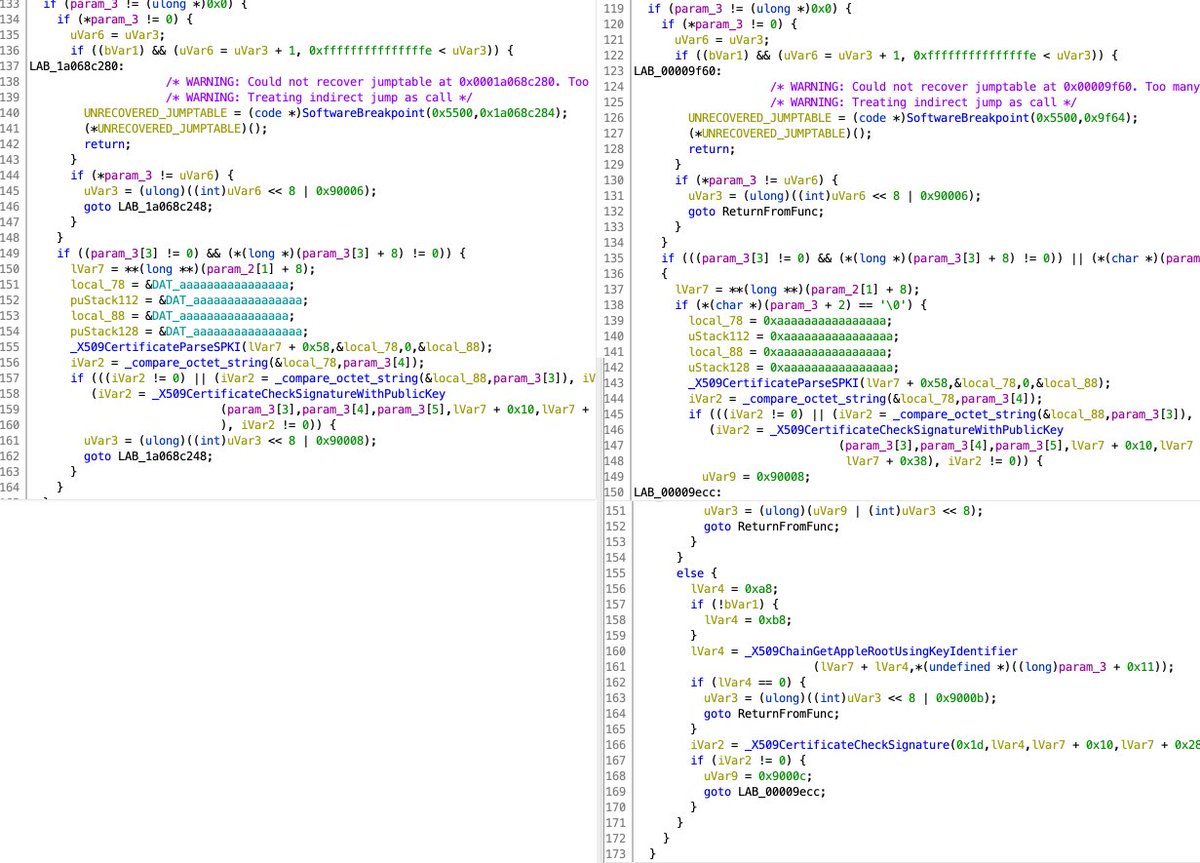
CVE-2022-26766: the CoreTrust bug
"For years, macOS allowed any root certificate when checking code signatures, making code signing completely useless."
// bug discovered by @LinusHenze
// writeup by @zhuowei
https://t.co/vuC4mcxwim
If you rely on Fortinet’s FortiGate firewall or FortiProxy then you need to update ASAP!
A critical authentication bypass vulnerability was discovered (CVE-2022-40684) allowing attackers to gain administrative control via malicious HTTP/HTTPS requests…
https://t.co/4U8pjhuHSC
Excellent 🧵 discussing the two recently discovered zero-day vulnerabilities in Microsoft’s Exchange Server: CVE-2022-41040 (server-side request forgery), and CVE-2022-41082 (remote-code execution).
Read the equally excellent more in-depth write-up here: https://t.co/Dy8cJIRsfR
Good article discussing the recent successful #phishing attack against Uber.
Key takeaway: “So far, the only forms of MFA that are phishing-resistant are those that comply with an industry standard known as FIDO2. It remains the MFA gold standard.”
https://t.co/wUROJ2MR7U
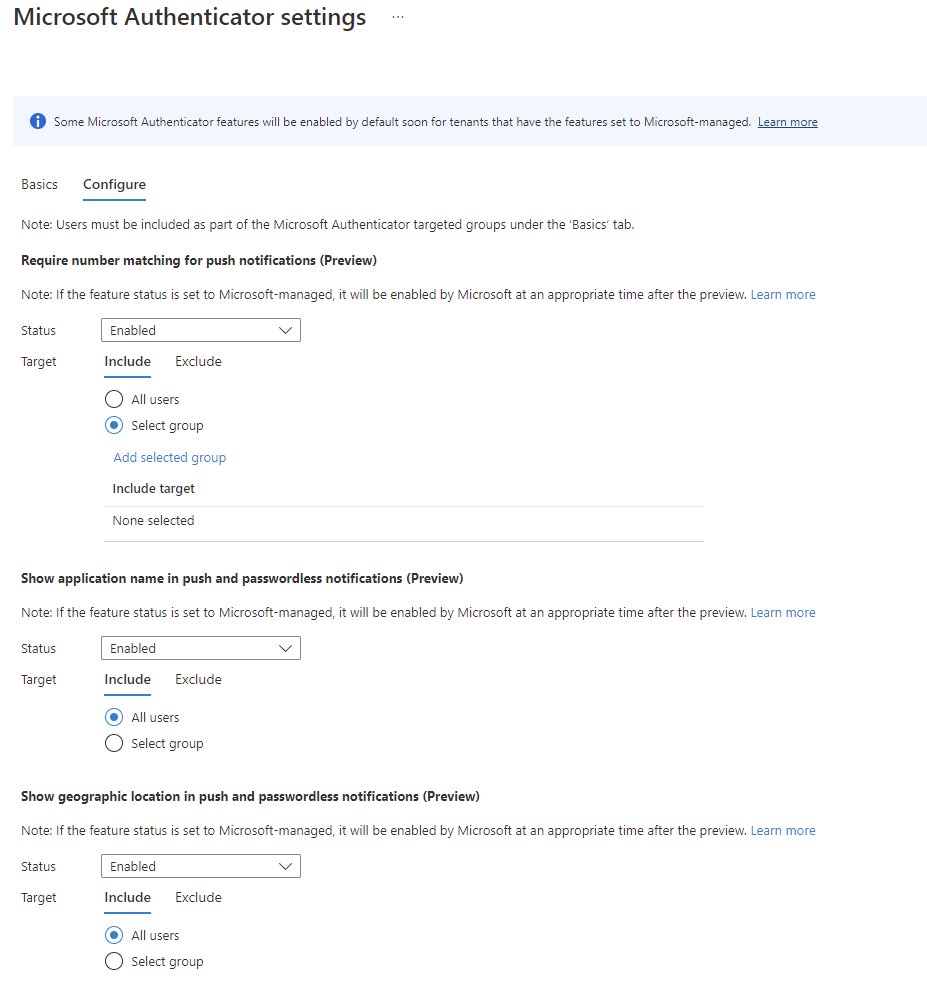
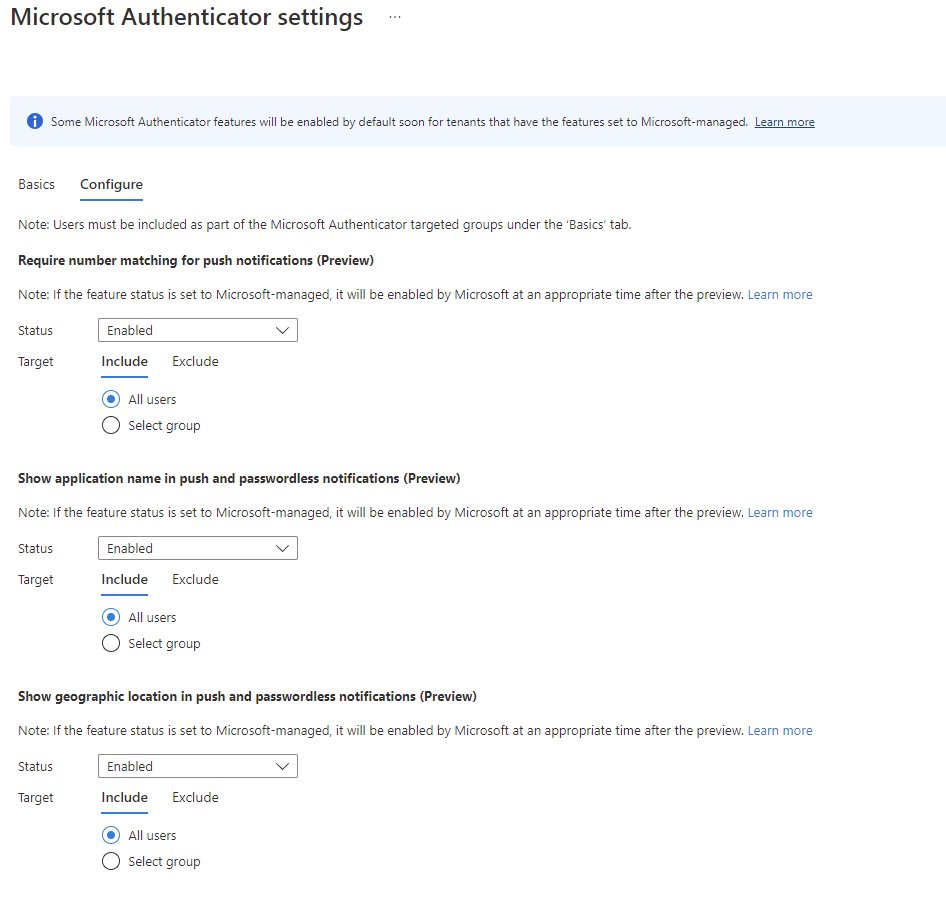
Great thread 🧵 about enabling MFA Number Matching for Azure and Office 365 environments. For organizations that are stuck relying on push notifications this is a good first step towards hampering MFA fatigue attacks that recently compromised companies like Uber, Cisco, et al.
Due to breaches involving MFA bombing (attacker keeps sending MFA requests until accepted) now is the time for organizations with Office 365 to enable MFA number matching in Microsoft Authenticator. You can deploy to a group before configuring for all.
https://t.co/t84oaIyiNH
1/3
🚨ATTENTION🚨
Apple found two 0-days actively in use that could effectively give attackers full access to device.
For most folks: update software by end of day
If threat model is elevated (journalist, activist, targeted by nation states, etc): update now https://t.co/BUEn08260X
Some fallout from the recent successful #phishing attack against #twilio…
If you rely on Signal, today is a great day to consider enabling registration lock on your account!
Recently @twilio, which provides SMS verification services for Signal, suffered a phishing attack. Via Twilio, attackers may have accessed phone numbers & SMS registration codes for 1,900 Signal users. 1/
Great thread 🧵 discussing a sophisticated SMS #phishing attack (very similar to the successful one against Twilio reported yesterday) and how #Cloudflare successfully thwarted it via defense in depth and relying on FIDO security keys as their MFA…
Twilio published an incident here that used social engineering on employees to gain access to credentials then internal systems via SMS phishing. Criminals pretexted as IT Support & used SSO likeness w/in domain. Recommend FIDO security keys for this team! https://t.co/3ymRqwHpny