JUST IN - A suspected supply chain attack on Optimizely loaded malware on Zoom, CNN, Fox News, BBC, Salesforce, GitLab, KLM, Air France, Bitly, IG Group, American Eagle and others, exposing visitors to scripts built to steal payment data and exploit iOS devices.
China has developed kinetic 3D LED displays which have modular panels that physically move forward and backward to create real depth and dynamic animations
This is wild
Writer: Ian
So let me get this straight - Cavemen depicted these ‘Jellyfish’ like Creatures thousands of years & now in 2026 we start seeing clips of them turn up in Earths Skies?
🚨 64,000 BITCOIN MINERS HIJACKED IN MASSIVE ATTACK
An estimated 64,000 Bitcoin miners representing 13 EH/s of hashrate were reportedly hijacked overnight, with their mining power redirected to OCEAN mining pool and payouts assigned to an attacker-controlled Bitcoin address.
The attack reportedly began around 8 PM CT on November 14.
OCEAN’s dashboard shows a sharp spike in hashrate, briefly approaching 50 EH/s before falling back toward 40 EH/s.
CoreX Hosting first raised the alarm, reporting that miners were being redirected without authorization.
One affected operator says their entire mining farm was hijacked and identified Luxor’s Commander mining management software as the source of the compromise.
Other operators reported similar unauthorized pool changes several days earlier, potentially pointing to a broader incident.
CoreX later reported that the attack appeared to be over, with the hijacked hashrate falling from 13 EH/s to approximately 100 PH/s.
The attackers reportedly failed to mine a Bitcoin block during the hijack, meaning no block rewards were collected.
However, affected miners permanently lost the opportunity to earn Bitcoin during the attack. That hashing time cannot be recovered.
The full scope of the breach and whether Luxor Commander was compromised have yet to be independently confirmed.
🚨 BREAKING: Transportation Secretary Sean Duffy just laid out EXACTLY what happened in the nationwide ground stop.
At 3:36 PM, radar and communications at air traffic centers across the country BECAME UNSTABLE.
Systems weren't fully down, but the data stopped being reliable, so the FAA grounded flights.
MORE THAN 3,500 PLANES WERE IN THE AIR. Duffy says fewer than 400 are left now, and they're all coming in to land safely. Medevac flights, lifesaving cargo and law enforcement kept flying the whole time.
His bottom line is that America is running "AN INCREDIBLY OLD AIR TRAFFIC CONTROL SYSTEM."
Trump and Duffy have been warning about this for two years.
Washington needs to quit stalling and fund the fix.
@jun_song Hmm.. if models get bigger (4t, 8t, 10+ trillion , 100 trillion parameters), then only guys with data center level VRAM can run them, even if you make it MOE. So "intelligence" will have a class hierarchy.
Here is an unverified scenario to think about:
An investigation comes out claiming that the hacks on US power grids and telecom systems were carried out by China, Russia, and North Korea using open-weight AI models.
The government then uses this as an excuse to regulate open-weight models and put stricter limits on chip exports.
But their real target is not foreign hackers.
It is to stop regular people like us from owning intelligence locally, locking us into a permanent underclass.
Success: 128GB added to the DGX Spark cluster for $1,000 USD. I'm still tuning, but so far 40GB goes directly to KV in GLM 5.3, with no hit to decode and a small (~10%) hit to prefill when the session context is larger.
It still needs a case but it works.
Cheap hardware: Xeon + DDR3 (!). The ConnectX card is the most expensive bit. This isn't just a way to swap unused KV out - gr8 reads only the rows selected by attention over RDMA.
Parts list 👇
🪙It's like finding gold. An 8GB NVIDIA mining GPU just became an 80GB AI accelerator.
And it's outperforming a retail A100 in an FP16 compute benchmark!
Hardware researcher Kate discovered how to unlock disabled hardware on NVIDIA's CMP 170HX cryptocurrency mining card.
So what's the secret? The 8GB CMP 170HX uses NVIDIA's GA100 silicon, the same GPU architecture as the A100.
And it physically contains much more memory than NVIDIA originally exposed.
👀Look at this ...
Stock CMP 170HX → Hardware-unlocked CMP 170HX
💾 VRAM: 8GB → 80 GiB
🧠 Streaming multiprocessors: 70 → ~120–126
🔗 NVLink: Disabled → Enabled
⚡ PCIe: Gen1 → Gen4
Now look at the reported FP16 compute benchmark:
🟢 Retail NVIDIA A100 → 72.49 TFLOPS
🔥 Unlocked CMP 170HX → 85.86 TFLOPS
According to Kate, of 10x 8GB mining cards examined
✅ 9x had a functional 80 GiB of memory.
✅ 1x had 64 GiB.
Kate's new method uses hardware voltage glitching and permanent fuse modifications to unlock additional memory and compute resources.
Imagine 80GB of HBM on 1x GPU.
Enough raw memory capacity to accommodate a 70B model at 8-bit or a much larger model at 4-bit, depending on runtime overhead.
And Kate has demonstrated 2x unlocked cards connected via NVLink.
From two cards originally sold as 8GB cryptocurrency mining accelerators!
🔗 Research and follow-up details in threads
In-N-Out Burger actually did this over a year ago
It did not just promise a cleaner menu. It changed the ingredients in foods people already order.
Yellow 5 is out of the pickles, chilies, and spread, replaced with turmeric. Red 40 is out of the Strawberry Shakes and Signature Pink Lemonade, replaced with beta carotene and vegetable juice.
High-fructose corn syrup is out of the shake mix, strawberry syrup, spread, and pink lemonade. The ketchup is now made with real sugar instead.
That matters because you can keep ordering a familiar favorite and get ingredients you can actually recognize.
Lets give credit where it is due. When a big chain follows through like this, it is worth noticing.
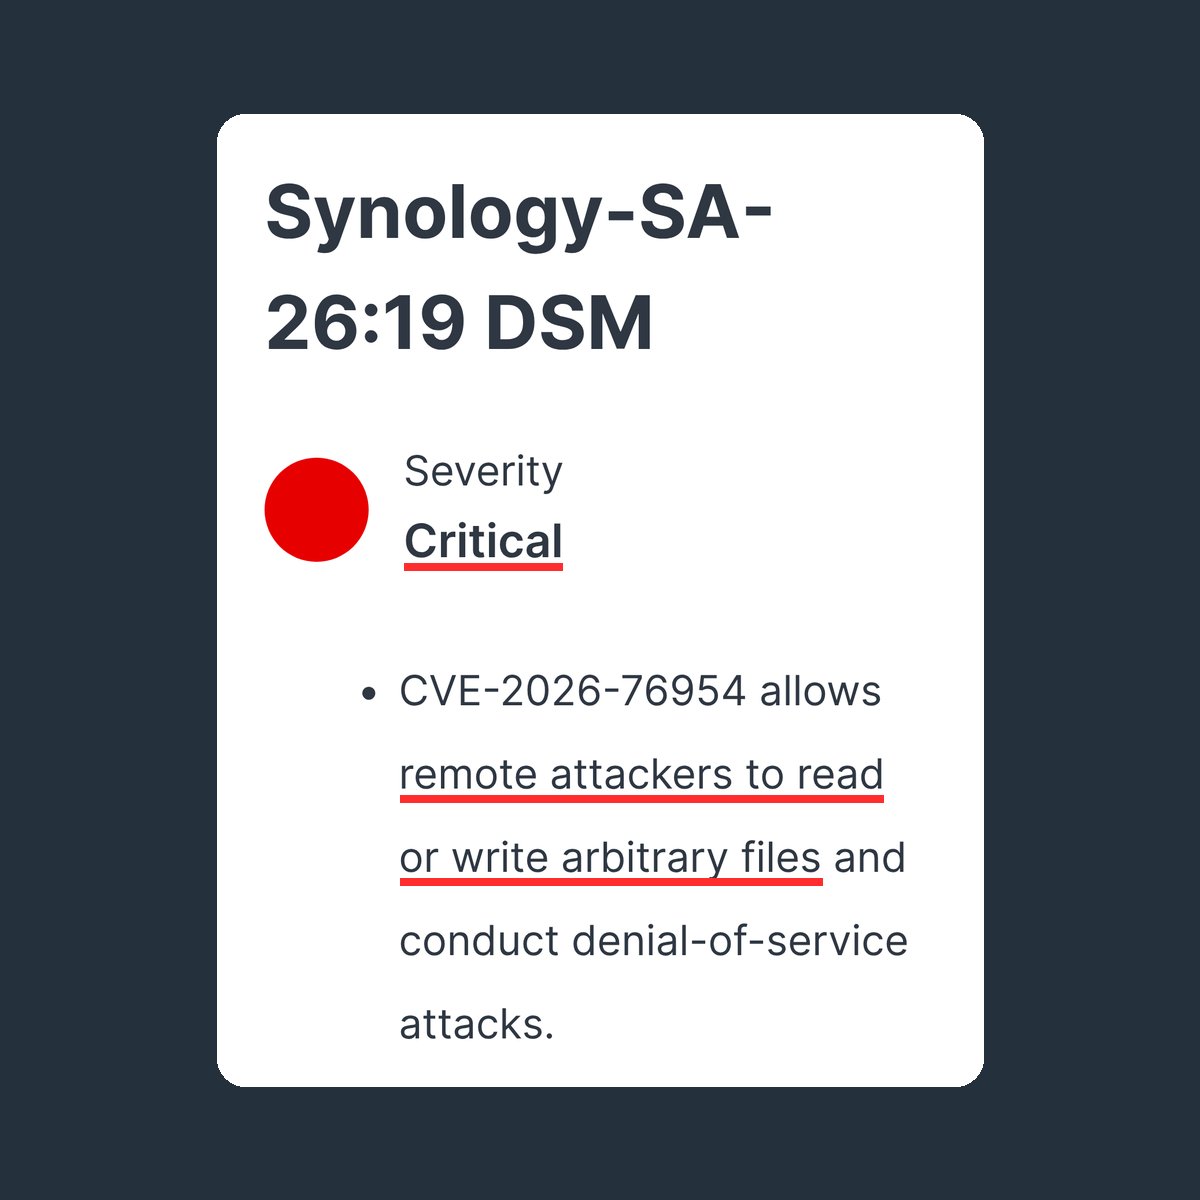
‼️BREAKING: A critical flaw in Synology NAS devices lets attackers read and write any file on them without logging in.
The SQL injection bug in their login system scores 9.8 out of 10. A second flaw, in rsync, skips the login too.
Synology patched both today. Update ASAP.