Der größte Gaslieferant Europas, Norwegens Equinor wird gerade von Hackern angegriffen!
Equinor entdeckte Cyberangriff.
Aktuell keine Auswirkungen auf die Gaslieferung. Jetzt heißt es beten für uns. Fallen die weg, wars das für uns
https://t.co/jOeIFrsw7o
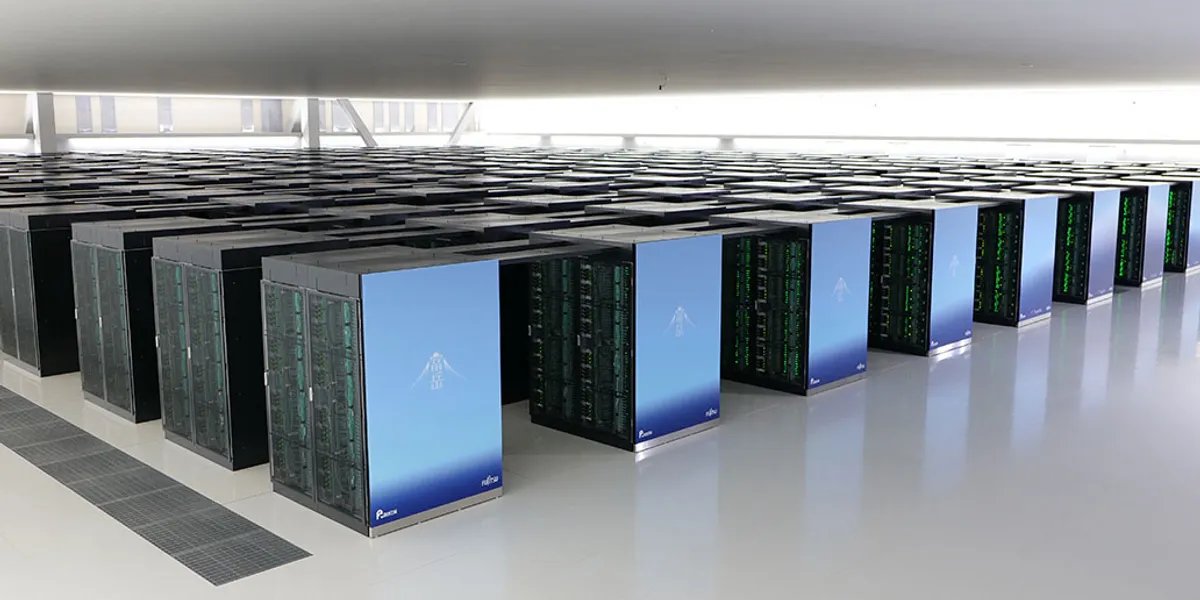
🇯🇵 The Japanese supercomputer Fugaku was hacked
The machine, which was the world’s fastest in 2021, is now offline. Data from nearly 4,600 users is at risk of leaking.
Stolen files include usernames, emails, user IDs, SSH private keys, and access keys. Attackers reportedly attempted to use these stolen credentials to access other systems.
The breach potentially exposed information for up to 4,224 Fugaku users and 375 users of RIKEN’s newer AI for Science supercomputer, RIKYU.
Ranked as the world’s 9th-fastest supercomputer, Fugaku is heavily used for disaster prevention, climate modelling, and pharmaceutical research.
Major Japanese companies, including Toyota, Honda, Nippon Steel, and Sumitomo Rubber, use the system for confidential industrial simulations.
In 2020–2022, Fugaku was considered the fastest in the world. It is now in 9th place with 415.5 petaflops. It was used to model virus spread during Covid and is now used to calculate earthquakes, tsunamis, and weather.
‼️ NATO is using OpenAI's cyber AI to defend Allied networks, burning through up to 300 billion tokens a month.
OpenAI announced it today. The head of NATO's IT agency calls the models, part of OpenAI's Daybreak programme, "a generational leap in cyber security."
At NATO's Crossed Swords cyber exercise, teams even built and ran AI agents for cyber operations.
Poland's cyber agency CERT Polska used the models to help find six flaws in MikroTik routers. The EU's cyber agency ENISA found four bugs in software used across EU institutions.
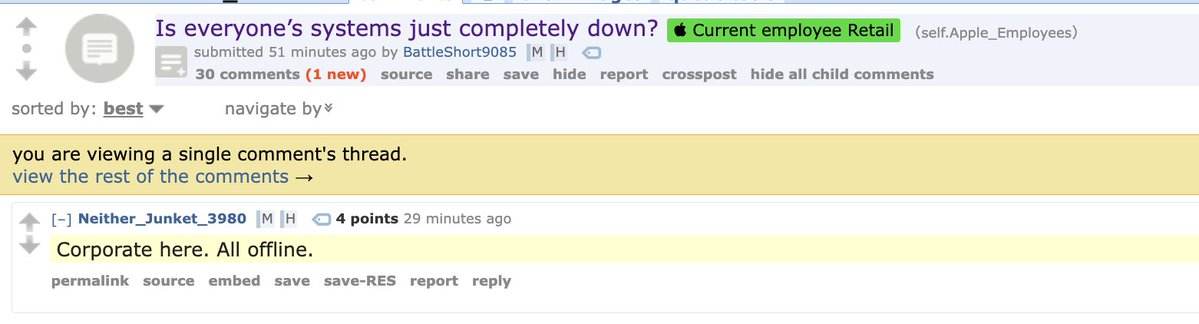
Apple down
Gmail down
Microsoft down
Banken down
Supermärkte werden attackiert
Warnungen von Regierungen
Was passiert hier gerade?
Was kommt da auf uns zu?
Wie bereitest du dich vor?
Alle Informationen in diesem Video
👇
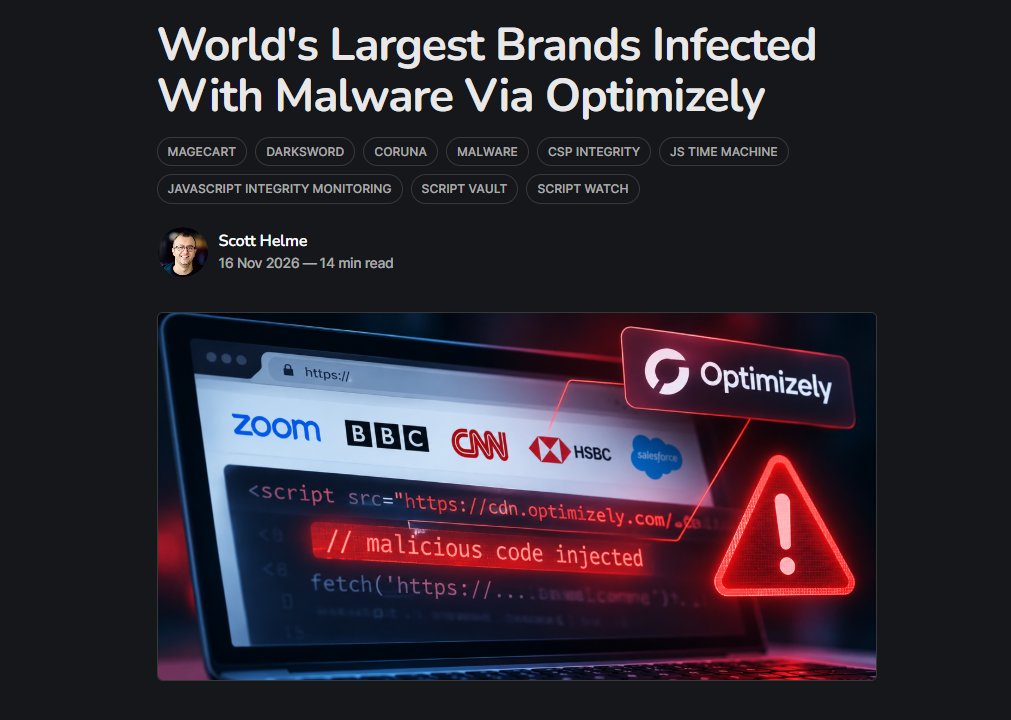
🚨 Großer Cyberangriff auf Websites von 178 Organisationen. Darunter Ledger, Zoom, CNN, BBC, HSBC und IKEA.
Die Angreifer nutzten eine Schwachstelle beim Website-Dienstleister Optimizely. Dadurch konnten sie über ein eingebundenes Skript Schadcode auf zahlreichen Websites gleichzeitig ausspielen.
Besonders brisant für Krypto-Nutzer: Wer auf einer betroffenen Seite eine Wallet-Adresse kopierte, konnte beim Einfügen unbemerkt die Adresse der Angreifer in der Zwischenablage haben. Wer die Transaktion dann bestätigte, schickte sein Geld direkt an die Täter.
Die Software konnte außerdem Kartendaten bei der Eingabe abgreifen. Ein Teil des Angriffs zielte auf Sicherheitslücken in iPhones und iPads.
Laut Report URI sind bereits Kryptowährungen an die Angreifer geflossen. Wie viele Nutzer betroffen sind und wie hoch der Schaden ist, bleibt offen.
BREAKING: FBI ISSUES URGENT WARNING OVER AI-POWERED CYBERATTACKS!
The FBI warns hackers are weaponizing ARTEX, an AI-powered system capable of breaching corporate networks and gaining privileged access in under THREE HOURS.
The technology was used in the ConnectWise supply-chain attack, targeting more than 2,250 Microsoft 365 customer environments.
Businesses worldwide are being urged to strengthen cybersecurity defenses.
Source: FBI FLASH Advisory, November 13, 2026.
⚠️ 🌐 ☁️ ALERT/PREVENTION – MASSIVE GLOBAL TECHNOLOGY SERVICE OUTAGES
Centralized cyber-intelligence systems have intercepted widespread user reports regarding outages and disruptions across multiple global-scale technology services, affecting email platforms, productivity tools, the hospitality sector, and mobile ecosystems:
Google: Reports of outages affecting Gmail.
Microsoft: Failures and connectivity issues within Microsoft Outlook and the Microsoft 365 suite.
Marriott: Incidents reported within the hotel chain’s systems.
Apple: A massive surge in reports affecting Apple Support, the App Store, iCloud, and Apple Pay.
#TechOutage #Gmail #Microsoft365 #ApplePay #CloudSecurity #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
🚨🇺🇸 EILMELDUNG: JETZT AUCH DIE NSA!
Laut CNN ist ein hochgeheimes Kommunikationsnetzwerk des US-Geheimdienstes NSA ausgefallen!
Und das nach einer beispiellosen Serie von IT-Störungen:
🇺🇸 Microsoft 365
🇺🇸 US-Flugverkehr
🇺🇸 Große US-Banken
🇺🇸 Jetzt auch die NSA!
Was zur Hölle ist gerade mit der amerikanischen IT-Infrastruktur los?
Die Website von 13 Billionen Dollar Asset Manager Charles Schwab ist ebenfalls down 👀
🚨 Google: Die Ära der autonomen Angriffe hat begonnen
Der Threat Intelligence Group von Google hat jetzt seinen Quartalsbericht veröffentlicht.
Vor zwei Monaten hieß es dort noch, man habe keine vollständig autonomen Angriffsketten in freier Wildbahn gesehen.
Das hat sich nun geändert.
Gefunden wurde exploit_agent, auf einem offen erreichbaren Staging-Server, angebunden an mehrere Frontier-Modelle und lokal gehostete LLMs.
Was das Ding tut:
→ Es vergleicht laufend den Code populärer Webanwendungen vor und nach jedem Patch
→ Es analysiert, welche Lücke damit geschlossen wurde
→ Es schreibt den passenden Exploit
→ Und führt ihn selbst aus
Kein Mensch in der Schleife. Ziele waren französische Medien-, Unterhaltungs- und Bildungsseiten.
Noch ein Detail, das direkt an die PHP-Lücke vom Oktober anschließt: Nach den Patches kursierte eine Welle behaupteter, aber nicht funktionierender Proof-of-Concepts, vermutlich LLM-generiert. Verteidiger mussten jeden einzelnen prüfen. Auch das ist eine Angriffsform.
Googles eigene Antwort beschreibt das Problem am besten: Verteidigung gegen Bedrohungen in Maschinentempo sei bei menschlichem Tempo NICHT MACHBAR.
Genau das, was ich seit Monaten sage. Defensives Co-Scaling, nicht Regulierung.
Kein EU-Gesetz der Welt wird in der Ära vollautonomer Angriffe helfen.
🚨 NOW: APPLE services are now suffering an OUTAGE, including Apple PAY, users report
iCloud and the App Store are also impacted
Users say they're being signed out of iCloud on iPhone and Mac without warning and can't sign back in
Apple's own status page still shows nearly EVERYTHING AVAILABLE, and the company has yet to acknowledge the broader disruption
Just another addition to the FLURRY of outages in recent days
‼️ BREAKING: Hackers poisoned a script running on BBC, Zoom and other major websites to rob their visitors.
The code hid in scripts served by Optimizely, a website-testing service, and three smaller vendors, and also turned up on CNN, Fox News and Salesforce sites.
Researchers count at least 186 infected sites. The code swapped crypto wallet addresses and sent iPhones to known hacking kits.
‼️ iPhone apps could SECRETLY record you—even after you tapped “Don’t Allow.”
Researchers uncovered an #Apple flaw that bypassed microphone permissions, sometimes without triggering the orange recording indicator.
Here’s how it worked ↓ https://t.co/ghOhhrE8MJ
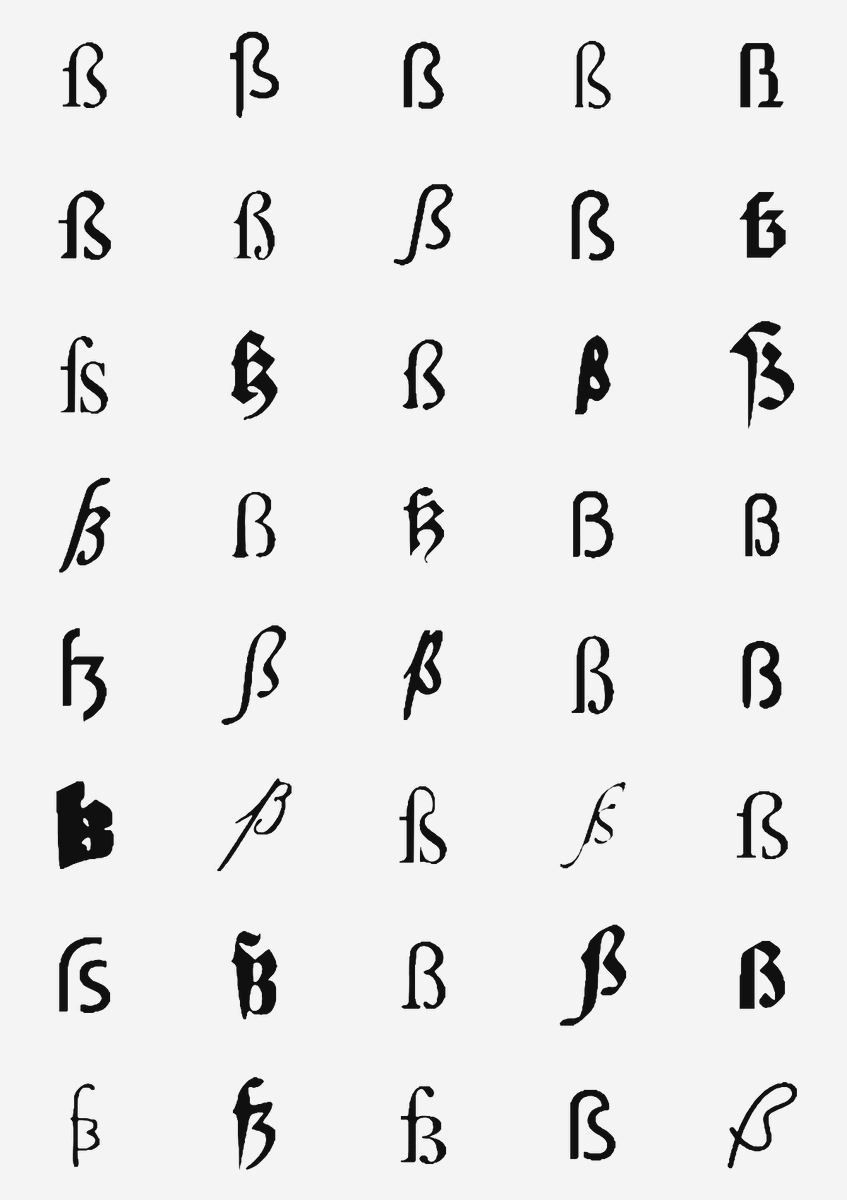
‼️ On a Mac, a German "ß" in a file name can slip past security checks in popular developer tools. US vulnerability centre CERT/CC warned today.
Macs can treat "ß" and "ss" as the same file. Tools from Terraform and Deno to Python's setuptools compared the letters exactly, so a blocked file gets through under the other spelling.
A local attacker could overwrite protected files or sneak secrets into uploads and software packages.
Several vendors have assigned CVEs and shipped fixes.