Thread On🧵:
Testing for Blind/Non-Blind SSRFs using redirection in integrations where there are some filters.
#bugbountytips#BugBounty#ssrf#bugbountytips
1. Hit the integration by using burp collaborator by using random credentials.
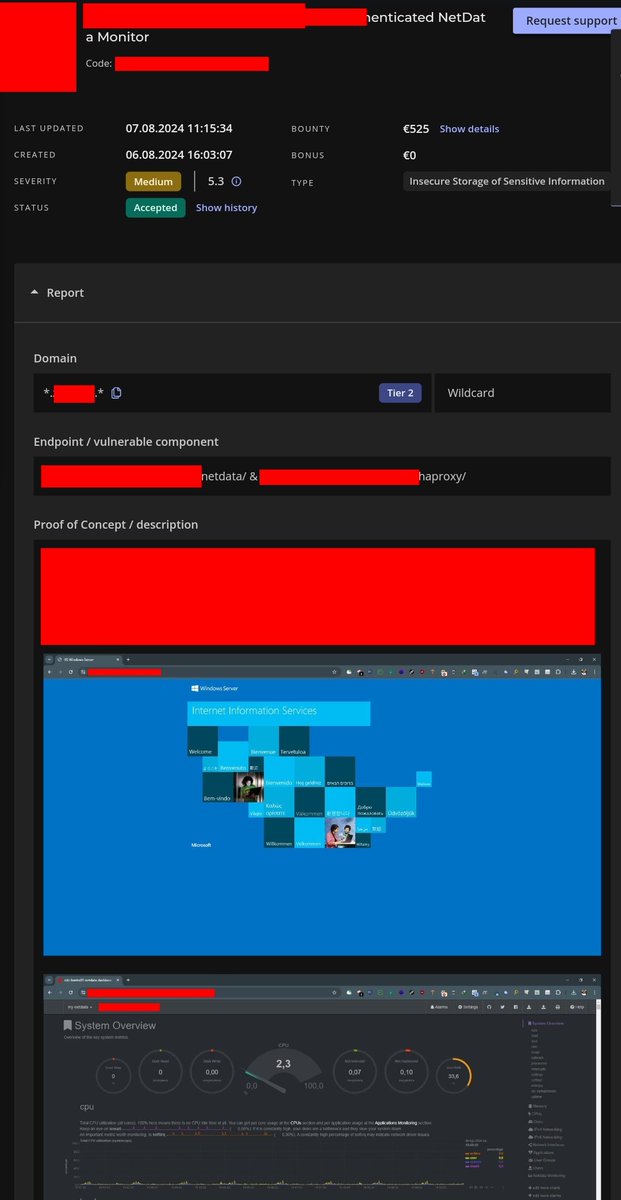
If you encounter the default IIS Windows window, do not forget to add /haproxy and /netdata to your wordlist and scan them, if you gain unauthorized access here, you will earn a reward 🌹🥰
#bugbountytips#BugBounty
Special Offer: Free Access to the PRO PLAN of #IBRAHIMXSS 🎉
I'm excited to announce a limited-time offer for the #IBRAHIMXSS community! You can now get free access to the PRO PLAN and use the tool with a 3-day license key. Follow these steps to get started:
1. Create an Account 📝Visit https://t.co/qvsmsJEfO3 and create an account.
2. Access the PRO PLAN 🔗Go to https://t.co/uHJhDEht4o.
3. Enter Coupon Code 🎟️Use the coupon code: XSSCOMMUNITYCOUPON ,to get the PRO PLAN for FREE.
4. Enter Credit Card Details 💳Fill in your credit card details as required by the website. Don't worry, you won't be charged or subscribed; it's just a requirement of the website.
5. Download Your Files 📥
After applying the coupon code and filling in the card details, you'll find a .zip file under your Products. This includes:The XSS tool and instructions for setup
Tool commands
6. Read the Instructions 📖Follow the step-by-step instructions in the ebook to set up the tool. It's only 3 steps!
7. Setup on Supported Platforms 💻The tool currently supports Windows and Linux (preferably Kali Linux). It cannot be started on Mac and VPS. Run the tool without sudo.
8. Enter License Details 🔑
#Email: [email protected]
#License Key:
CfDJ8GR4RWcdpvVPpJYHepSytWiZ2wJbgVgyJ_oYG41YDx9f3n9u0T2vfKDuoIYYX4cwdYawy0x97q7JTsASlIg8zbVmTRtWD_EvQM_bhIXPKX36Evut9xz8v_-DMORZlKeEdemBDrfvXBboUlXIPift_Cy6Q0UVcJaRpkzlOtH1vZh4-AO0izE7MxYhd7v2UMgSBEnq6cbp_C1bFxduEwKrqsDWtleXavhgWw0iR4AZKee6gYFYKgzP0LwUuBEsymzyDWFZucg1db9toBz-IPa7VQ60i3fRAndlu1-H9sBHfAsEjKVnneT9N92S2dVUQc28OMOBIQGcG5SscyTRUwdZ4lY-m7-Fwv0m5OFWxJEkjmoVPFlR4Yahfzj2hxmrsiNFw_iH0Ew7uo1LX1b8cwS9mLQ
9. Learn the Tool Commands 🛠️Open the other zip file with the Tool commands and follow the steps to learn all the features of the tool.
10. Replace Payloads 📂Replace your PRO plan XSS payloads into payloads.txt.
11. Run the Tool 🚀Start the tool and begin your scanning.
Enjoy using the #IBRAHIMXSS tool and happy scanning! 🛡️✨
#############################
Recent Cyber Security Vulnerabilities on note!
#############################
CVE-2023-4966 NetScaler ADC and NetScaler Gateway
CVE-2023-20198 IOS XE Web UI PE
CVE-2023-20109 Cisco IOS and IOS XE Group Encrypted Transport VPN Out-of-Bounds Write Vulnerability
CVE-2023-22515 Atlassian Confluence Data Center and Server Broken Access Control Vulnerability
CVE-2023-40044 Progress WS_FTP Server Deserialization of Untrusted Data Vulnerability
CVE-2023-27532 Veeam Backup & Replication Cloud Connect Missing Authentication for Critical Function Vulnerability
ALSO
CISCO FIREWALLS: They are being brute forced! (along wth SSH, TELNET, RDP, WINRM, SMB)
also some more fun @shodanhq queries:
Exposed RDP
https://t.co/33eKYCOHDc
Exposed SMB:
https://t.co/ift6Ce3YY6
and well you get the picture!
Lots of exposed stuff!
MILLIONS of RDP and MILLIONS of SMB!
⚠️"Attacking Organizations with Big Scope - from 0 to Hero" was my talk at #HitBxPhdays in Bangkok 🇹🇭. Happy to share the slides and recording with the community.
🔴 Slides: https://t.co/03GfeE5KCR
🔴 Recording:
https://t.co/KpBNtQm6tm
Enjoy!
#bugbounty#infosec #bugbountytips
Hey everyone! I've giving away a student pass for
@BSidesMumbai ! Want it? Drop a comment telling why you need it. Let's make sure this opportunity goes to someone who's really psyched about #cybersecurity! #BSidesMumbai (You need to have a valid and original College ID)