Can't patch PHP2Shell yet? Here's how to build a stopgap with the controls you own.
PHP2Shell comes with a clear instruction: update PHP. But patching at this scale still takes time. In Qualys telemetry, only 199,000 of the 156 million PHP package installations with a known version (about 0.13%) had been patched in the first 12 hours after disclosure.
Here is how to bridge the gap between disclosure and patch, in four steps:
1. Find and Prioritize Exposed PHP
2. Apply the Qualys Mitigation
3. Add Layers from the Security Stack you already run
4. Patch, Restart, and Re-Validate
Learn more and don't forget to access our free PHP2Shell service to help product your environment against this threat: https://t.co/BC94JRD3FQ
#PHP2Shell
Cyber risks belong on the board's agenda. A Risk Operations Center (ROC) links technical vulnerabilities with financial business risks.
https://t.co/5i4y6ZujtL…
#Cybersecurity#KI@qualys
PHP has released security updates for two critical vulnerabilities that can allow unauthenticated remote code execution. Our Qualys Threat Research Unit (TRU) has uncovered that millions of installations are at risk, and attack traffic linked to the vulnerabilities have already been reported.
Here's how we’re stepping up to help. Qualys is offering free services to help organizations identify and mitigate exposure to PHP2Shell vulnerabilities. Our service includes access to products from our TruRisk Platform, including VMDR, TruRisk Management, and TruRisk Eliminate.
Read the full coverage from @techday_au here:
https://t.co/ixH0wHJWez #PHP2Shell #PHP
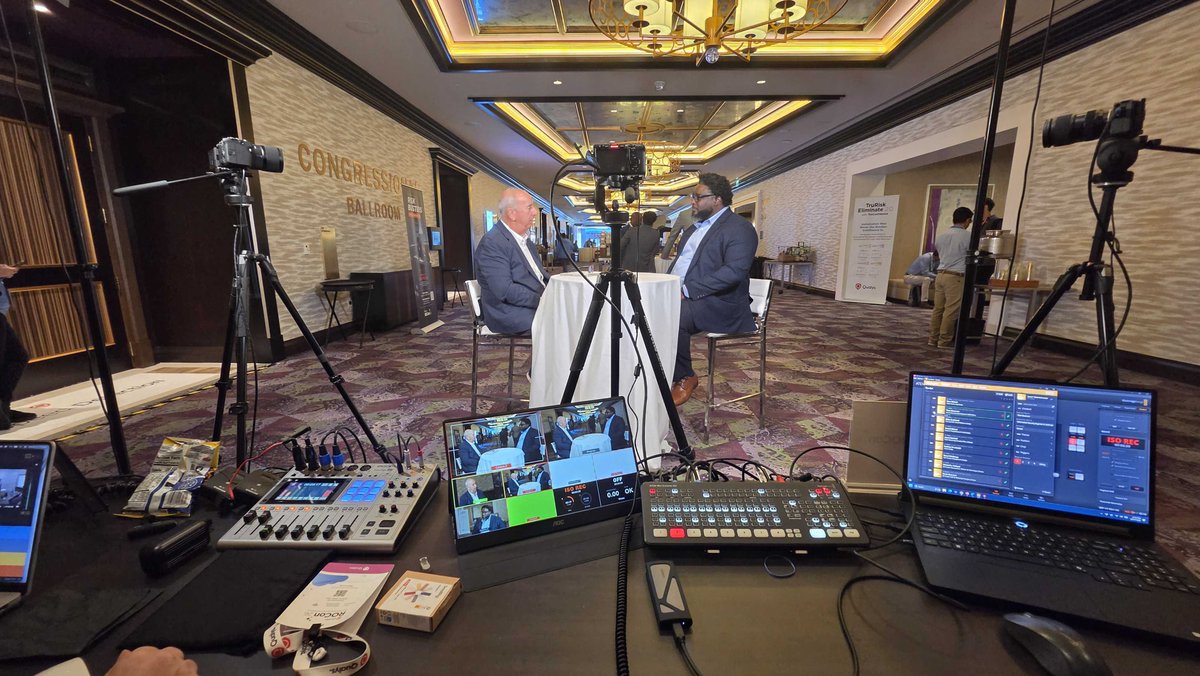
🎬 @TechstrongGroup was on-site at @qualys ROCon 26 Americas in Austin, Texas, connecting with cybersecurity leaders and industry experts to discuss the future of cyber risk management.
Through a series of exclusive interviews, our team explored how AI-powered security, automation and proactive risk management are helping organizations address emerging threats and strengthen their security operations.
▶️ Stay tuned for exclusive interviews and event coverage coming soon to @TechstrongTV.
#ROCon26 #Qualys #Cybersecurity #RiskManagement #TechstrongTV
Qualys ROCon 2026 in Austin is a wrap!
On my podcast, Full Tech Ahead, I spoke with Kunal Modasiya of @qualys about using AI to fight AI and fixing vulnerabilities without disrupting business.
Watch Here: https://t.co/DnosBl1bri
More interviews recorded at the event coming soon. Stay tuned! #ROCon26 #FullTechAhead #Qualys
I’m excited to share a new format for Full Tech Ahead, with interviews filmed directly at conferences and my guests joining me in person! 🎤
In this episode from Qualys ROCon 2026, I sat down with keynote speaker @ssthakar, President and CEO of @qualys, to discuss how AI is changing the way organizations approach cybersecurity and business risk.
A big message at this conference was that fixing thousands of vulnerabilities doesn’t necessarily mean you’re reducing the risk to your business. The focus needs to be on identifying what poses a real threat and taking action faster. 🤔 🔒
Watch my latest interview, (the first of a 3-part special conference series) and stay tuned for the rest of these informative discussions! 💡
Watch Here: https://t.co/ruIKp5f2yA
#FullTechAhead #ROCon26 #Qualys #Cybersecurity #AI #RiskManagement
Who actually owns AI cyber risk in your organization?
The second episode in my three part Full Tech Ahead series from Qualys ROCon 2026 is live!
I spoke with Ivan Milenkovic, VP Cyber Risk Technology at @qualys, about why that question still leaves so many leaders pointing to someone else.
Check out our conversation, and stay tuned for the final interview in this series!
Watch Here: https://t.co/BIwcvZHBZV
#FullTechAhead #ROCon26 #Cybersecurity #AI
@qualys is offering 15 days of free access to its security solutions to help organisations identify and address PHP2Shell vulnerabilities, which carry a critical severity score of 9.2 and have already seen attack activity.
https://t.co/cnkPFvC5bU.
A sharper view of cyber risk was on the table in New Jersey as security and IT leaders discussed the shift from vulnerability management to the Risk Operations Center. #CVisionIntl@Qualys
When autonomous AI can discover and exploit vulnerabilities in hours rather than weeks, board-level cyber governance has to evolve. Measuring theoretical risk scores is no longer enough- directors need visibility into validated, business-context risk.
On October 29, our CISO, Nathan Smolenski, will join the @National Association of Corporate Directors (NACD) for The Mythos Inflection Point: Board Oversight in the Age of Autonomous AI.
Together, they will discuss:
> How autonomous AI changes the window between vulnerability discovery and exploitation.
> Key questions board members should ask management to evaluate operational readiness.
> Shifting governance frameworks toward validated, risk-based decision-making.
Register here to join the discussion: https://t.co/egBbCZ5Ptm
#CyberGovernance #BoardOversight #AISecurity #Qualys
PHP2Shell: Know your exposure. Take action.
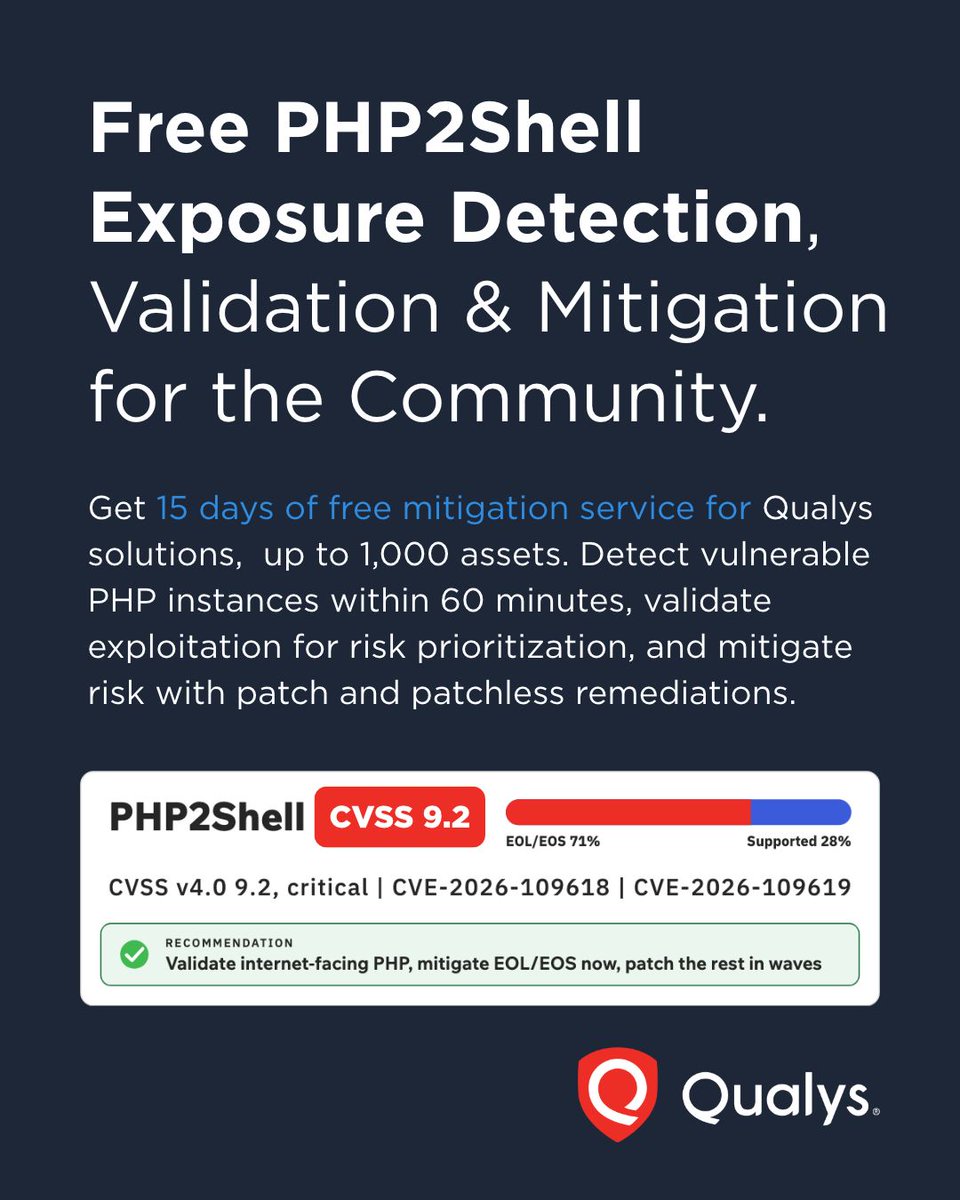
PHP2Shell is CVSS 9.2 critical, and end-of-life PHP won't get a patch. Qualys is offering a free 15-day mitigation service for up to 1,000 assets that can help you:
-Detect vulnerable PHP instances within 60 minutes
-Validate exploitability to prioritize real risk
- Mitigate what you can't patch with patchless remediation
Get Free PHP2Shell Mitigation Service: https://t.co/qyYOA5qhbk
PHP2Shell is two critical PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) that can allow unauthenticated remote code execution, and attack traffic has already been reported. See how Qualys helps you detect exposure with InstaScan, confirm exploitability with TruConfirm, and mitigate before you patch with TruRisk Eliminate. https://t.co/xN6TWNbTpK
The latest PHP flaws have been dubbed the next Log4J with millions of installations affected around the world, including government services, critical infrastructure, and enterprises.
Qualys is offering its solutions for free as a service to the community to help organizations detect their exposure, validate if it's exploitable in each specific environment, and patch or mitigate what remains vulnerable. More info at https://t.co/hzrgPtOnB7
ROCon APAC, the Qualys Risk Operations Conference, is built to address a simple question: how do you run a security program when exposures occur faster than your team can respond?
Join us in Mumbai 18-19 November to see how today's security leaders are moving from enumerating risk to eliminating it.
What to expect:
✔️ Free Hands-On Training & CISO Workshop (Nov 18): Four tracks covering Qualys ETM, scanning/agent troubleshooting, cloud/AI risk, and RemOps.
✔️Executive Keynotes (Nov 19): Insights on building an AI ROC from CEO Sumedh Thakar, and Qualys leaders Shailesh Athalye, Kunal Modasiya, among others.
✔️Technical Sessions: Deep dives on verified risk reduction, exploitability, ITOps remediation, cloud/containers, and new attack surfaces.
✔️Real-World Impact: Customer case studies on prioritizing exploitability and optimizing remediation programs.
Register today at: https://t.co/0seoRT9GIv
#roconapac #qualys #cybersecurity
PHP has released fixes for CVE-2026-109618 and CVE-2026-109619, both rated CVSS 9.2. Researchers demonstrated unauthenticated RCE and memory disclosure, including RCE before application code runs on Apache mod_php. Cloudflare has already observed attack traffic.
Patching is the only complete fix. Prioritize internet-facing systems, restart affected workers, and verify they are running patched PHP. Qualys detection QIDs are now available.
Read the PHP2Shell blog for remediation, temporary mitigations, and detection coverage.
#CyberSecurity #VulnerabilityManagement #AppSec
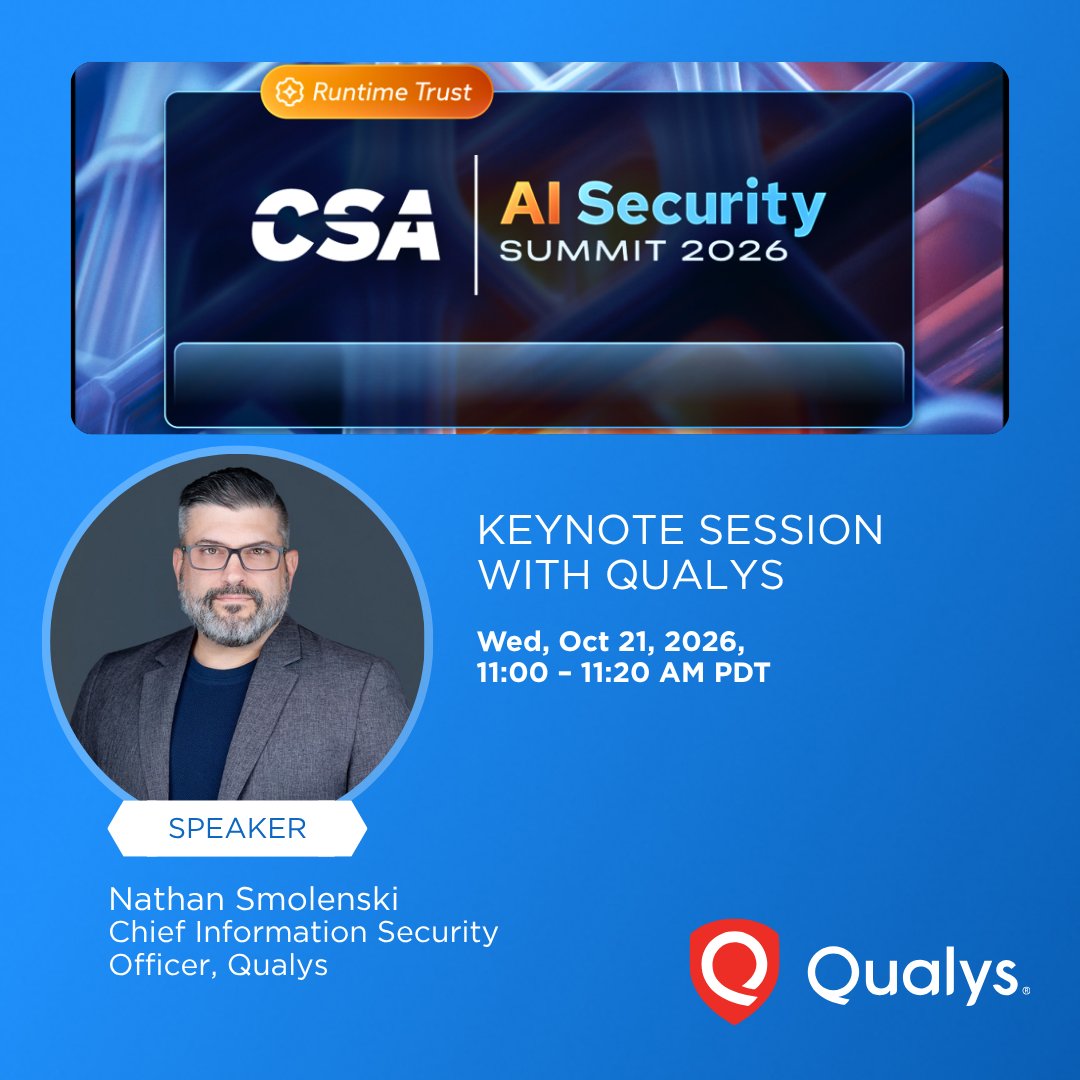
Don’t miss our Keynote Session at the virtual CSA AI Security Summit 2026, featuring Qualys’ Nathan Smolenski.
This session examines the intersection of AI governance, cybersecurity, executive oversight, and regulatory accountability. Find out how autonomous AI changes risk ownership, impacts board responsibilities, and creates new obligations for technology and business leaders. This presentation will outline practical governance patterns, oversight models, and accountability frameworks that organizations can use to safely adopt agentic AI while maintaining compliance, transparency, and stakeholder trust.
Register now and don’t miss this event on Wednesday, October 21: https://t.co/aaPD8INMhB
That’s a wrap on #ROCon26!
We spent three days in Austin with CISOs, customers, partners and practitioners, all working on one question. How do you eliminate cyber risk at the speed of frontier AI?
The energy came from the conversations. Customers shared how they’re moving from measuring risk to eliminating it. Partners showed how they’re scaling risk operations for the organizations they serve. And the hallway debates kept going long after the last session ended.
We launched TruRisk Eliminate with TruConfidence to deliver AI powered remediation intelligence so teams can fix what matters most at machine speed without disrupting the business.
Thank you to everyone who shared their ideas, asked great questions at ROCon and brought their skills and competitive spirit to the RiskBusters competition.
We’ll see you in 2027.
#ROCon26 #Cybersecurity
That’s a wrap on Day 3 of #ROCon2026!
Three days of expert insights, customer experiences, partner perspectives, and conversations on turning cyber risk into action. From Ivan Milenkovic’s Risk Yoga keynote on staying focused amid the chaos of Frontier AI, to @saeed4bbasi demonstrating how Qualys Threat Research uncovers emerging threats, the day brought practical insights into what it takes to manage cyber risk in the AI era.
But understanding risk is only part of the equation. The next step is acting on it. As AI accelerates the pace of exploitation, remediation has to keep up. That means moving beyond patching alone to take the right action, at the right time, with the confidence to reduce risk without disrupting the business.
Thanks to everyone who joined us in Austin!
Stay tuned for our ROCon recap and key takeaways on operationalizing your AI-ROC.
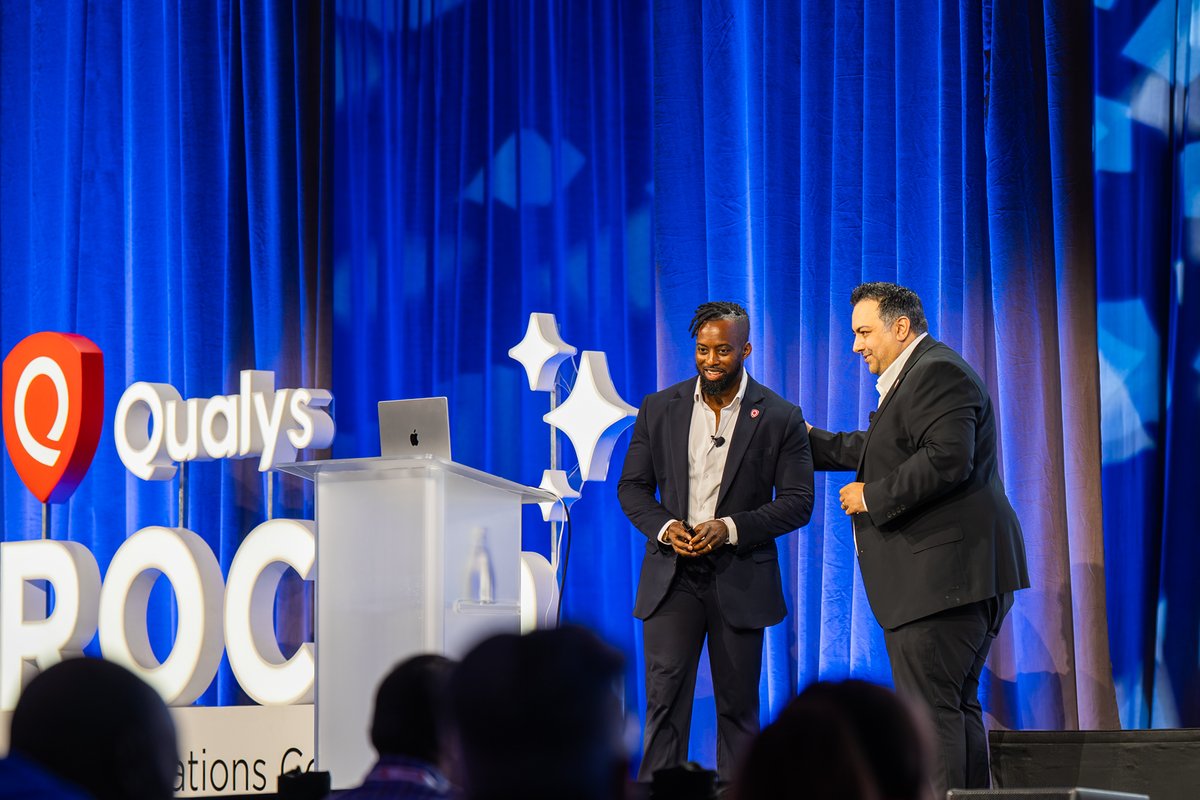
ROCon Americas 2026 mainstage kicked off in Austin today.
Qualys President and CEO Sumedh Thakar opened the day with a clear message. “Autonomous exploitation requires an equally automated remediation.” He then unveiled TruRisk Eliminate 2.0 with TruConfidence, the AI-powered remediation intelligence engine that powers Autonomous RemOps for the frontier AI era.
Built on Qualys’ experience deploying half a billion patches, TruConfidence helps organizations eliminate risk at machine speed without putting business operations at risk. It extends remediation across endpoints, perimeter devices, cloud and applications, applies compensating mitigations when patching isn’t an option, and monitors system health after every action.
From there, attendees went deep in sessions and panels with security leaders, customers and Qualys experts on how to measure, communicate and eliminate cyber risk in the AI era.
Thank you to everyone who joined us today. See you tomorrow for Day 2. #ROCon2026
Learn more about TruConfidence and 2.0 here: https://t.co/ptAJqUa4Cn
#ROCon26 #Cybersecurity #FrontierAI #TruRiskEliminate