More on the PHP side. 17 advisories, seven critical. The headline bug is phpAfterShell.
@Cloudflare WAF rules cover CVE-2026-129289: PHP-FPM request smuggling in the code since PHP 5.6. It needs a front end that reuses backend connections. Plus two SOAP bugs. These need to be enabled. We have set them in log mode on paid plans, so check the matches and switch to block.
Upgrade your PHP to 8.2.36, 8.3.37, 8.4.28 and 8.5.13.
https://t.co/cf6mG5zEiM
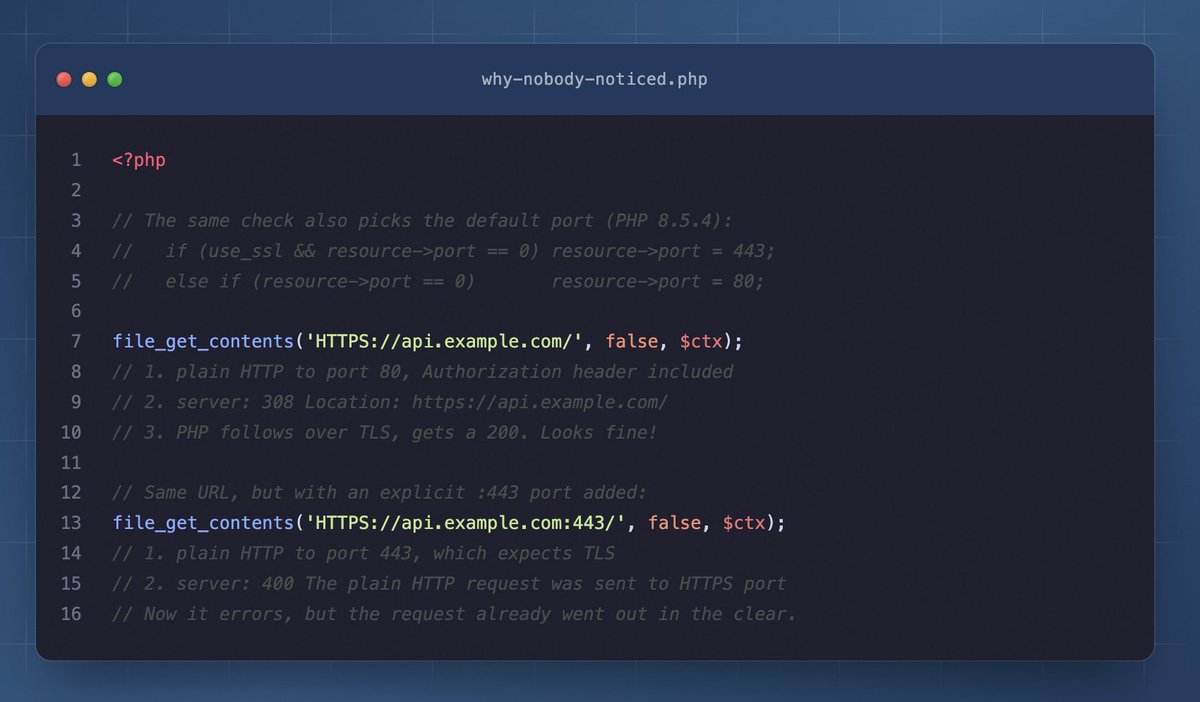
HTTPS:// with no port went to :80 in plaintext. The server redirected to https://, PHP followed over TLS, you got a 200.
But auth headers and POST bodies already leaked on that first request. Only an explicit :443 would have given an error.
Oh boy … PHP sent clear text data when you used uppercased S in httpS:// in a protocol handler 🙈🙈
file_get_contents('HTTPS://…') skipped TLS: tokens, POST bodies and FTPS logins went out unencrypted!
Fixed today in 8.2.36, 8.3.37, 8.4.28, 8.5.13 & 8.6.0.
I think we need a new CVE barometer of what constitutes a 9 or 10 CVE for remote exploitation. Or at least a viability of how bad it could be, like an "oh shit meter".
Most of these 2shells require very specific things to be in play to work. They are still brilliant bugs no question, but companies shouldn't be created a critical incident for every single one of these that comes out daily or weekly.
We are going to destroy all trust in the cybersecurity industry if we keep doing this.
There has to be a better way.
I take it back. GTA is about letting people indulge in fantasies they would never be able to experience in the real world.
Millennial GTA (GTA3 through 5) was about the fantasy of being a badass gangster.
Zoomer GTA (GTA6) is about the fantasy of having a girlfriend.
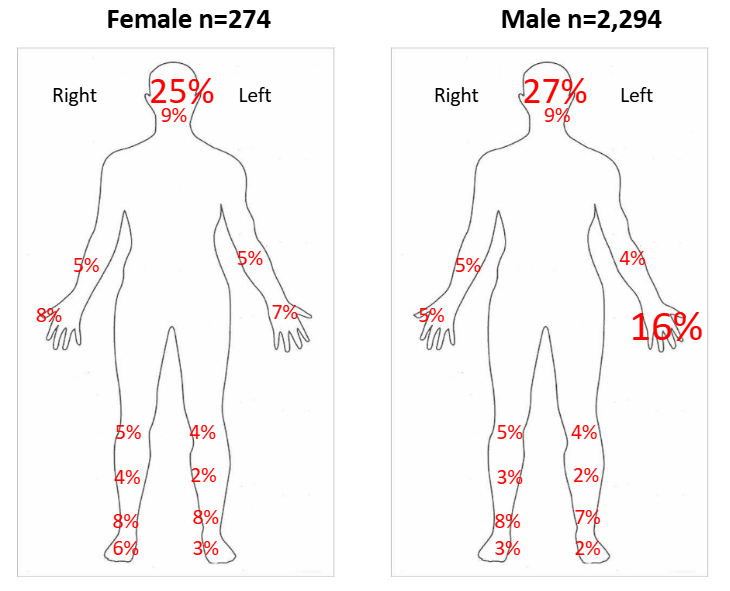
Since ID cards didn't exist in the ancient world, contracts often contained descriptions of the involved parties.
We have thousands of descriptions of Egyptians from papyri contracts that show that 86% carried scars, with most scars occurring on the arms and legs. These were mostly from dangerous farming work, but some were also from violence and disease.
Comprobado. Con la última actualización de los parámetros del IRPF y un año más sin deflactar, TODOS los salarios por encima del SMI seguirán pagando más IRPF en 2027 que en 2019.
Y todos los que están por debajo del SMI pagarán más (por el MEI).
🚨 Today, Nov 18, at 06:59:34 we saw the first instance of ARTEX and Java4Shell being used from the same IP address. This indicates threat actors are combining new vulnerabilities to carry out attacks.
Pre-auth RCE in nginx is the bug every hacker dreams of finding. It almost never happens.
Today we’re disclosing nginx2root: five nginx vulnerabilities, and an exploit that takes an unauthenticated attacker all the way to root.
One of themhits the default config.
If you run nginx, patch now. Then read: https://t.co/rDQQAimLZP
CVE-2026-123007, CVE-2026-123634, CVE-2026-123633, CVE-2026-121810, CVE-2026-113425
Today we disclose CVE-2026-123633 and CVE-2026-123007 (CVSS 4.0: 9.2) - exploitable memory corruptions in NGINX
We achieved reliable remote code execution (ASLR defeated) on NGINX serving static files - no backend or third-party modules 🤯
Both require HTTP/2
Read more 🧵⬇️