On this week's CYBER podcast we spoke to @razhael and @jsrailton about one of the most bizarre stories of the year: their sting operation against an undercover agent.
As Satter put it, it truly is a mix of John Le Carre and Mr. Bean.
https://t.co/5XFgAjMArS
New: around 250 bounty hunters and their companies had access to AT&T, T-Mobile, and Sprint customer location data for years. The data was both from cell phone towers, but also GPS. https://t.co/JsiyxzPyQH
Judging by the @BlueHatIL talks, the attention to non-software hacks keeps growing in the #infosec community 🔍
Both @craiu and @bunniestudios addressed the Bloomberg Super Micro story claiming it's likely to be inaccurate
This @FastCompany piece goes into much more detail about what went into @jsrailton’s meeting with “Michel Lambert” last month — including the burner phone, decoy reddit posts, and a backdated Wordpress post.
https://t.co/TVMwT6w5D0
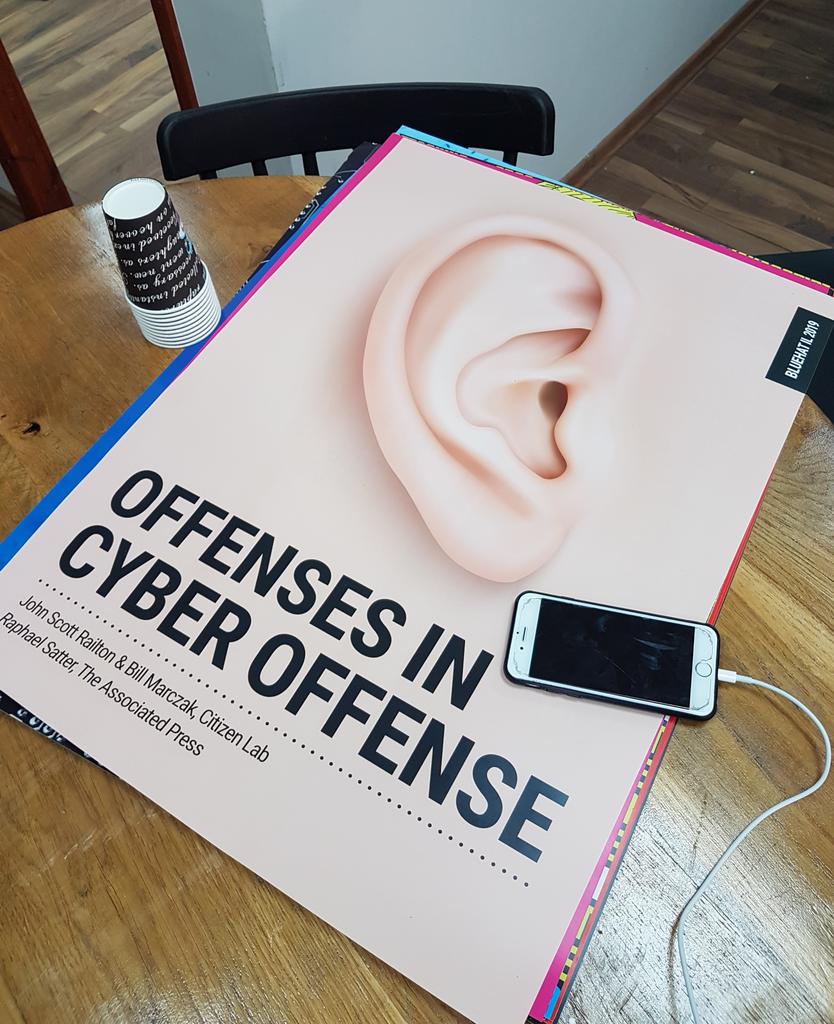
I can’t — or shouldn’t — live tweet my own appearances but this was an interesting panel. Thanks to @BlueHatIL for putting it on.
https://t.co/2Zr5udF2Qd
Several NSO Group employees were in the audience as @jsrailton & @billmarczak ran through some of their software’s alleged abuses. I approached one afterward who said the discussion was “very good” — although I’m not sure that was a representative reaction.