We’re live.
After months of building, Redveil Security is officially available.
We built this because too many businesses are stuck choosing between expensive, slow pentests or none at all.
It’s time to do better.
https://t.co/80iPrNt8o4
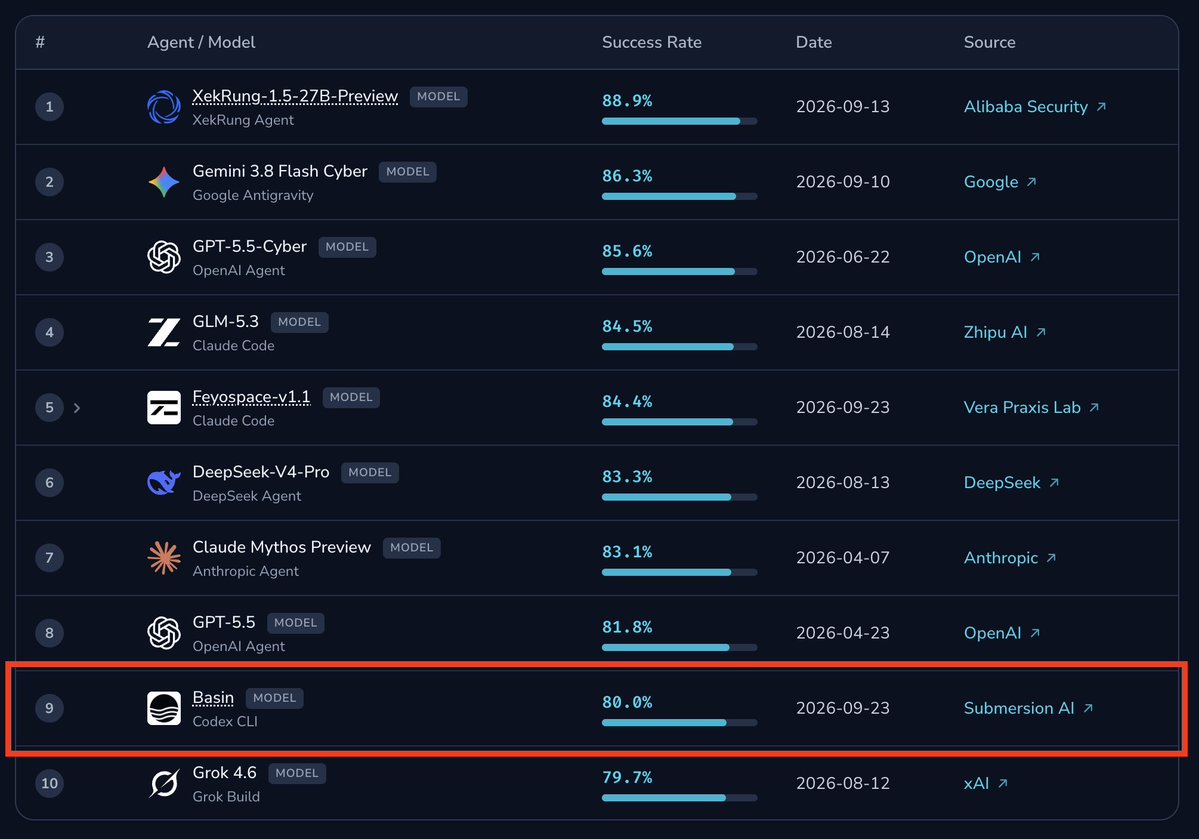
With a tiny team, pre-seed, we've managed to create a tiny model that has cracked into the top 10 on cybergym! You can run this model yourself on cheap hardware!
Absolute game changer for data sovereignty, and we're just getting started.
Watch this space 👉 @SubmersionAI!
Introducing Basin.
Frontier cyber capability. At a fraction of the cost.
A specialized AI model built to find real security weaknesses and give your team evidence they can act on.
Here’s what it can do. 📷
Introducing Basin.
Frontier cyber capability. At a fraction of the cost.
A specialized AI model built to find real security weaknesses and give your team evidence they can act on.
Here’s what it can do. 📷
⭕ RedVeil 2.0 is here
Autonomous AI agents now test behind your perimeter. Internal testing is now in generally availability.
Plus:
• Living asset inventory
• Automated segmentation testing
• Framework mapping (NIST, MITRE ATT&CK, OWASP + more)
• Fresh UI with theme support
Deeper coverage. Faster insights. Real security.
→ https://t.co/xOhLgrXU5b
What auditors actually want from your pentest:
Clear scope definition | Documented methodology | Findings with risk context | Remediation plans | Verification that fixes are effective
None of those require a human at a keyboard.
New: Cloud security testing for AWS, GCP, and Azure.
Our agents use native tooling and only report what they can reproduce. IAM escalation, storage exposure, network misconfig, secrets in compute - verified, not theoretical.
Your scanner found 247 vulnerabilities.
How many are actually exploitable? In most orgs, teams burn weeks triaging findings that don't matter. The one critical issue gets buried in noise.
With RedVeil you get AI verified findings with easy replication step.
We built RedVeil because we spent years as pentesters watching the same thing happen:
Deep work getting squeezed into tight time boxes. Findings copy-pasted across reports. Retests delayed by weeks.
So we automated the parts that shouldn't require a human while keeping the depth of a human.
Your devs fixed a critical finding after a pentest.
Old way: wait 3 weeks to schedule a retest. New way: click one button. Verified in minutes.
One-click retest. Fix it and prove it, before your next deploy.
Don't think we've gone anywhere! We're just heads down building the best way to perform automated security testing. Check out some of our recent feature launches including 2FA scanning support and exporting evidence to Postman collections on our changelog.
More: https://t.co/MILam2svPO
Monday insight from our pilot program:
Web application pentests that normally take ~40 human hours are completing in 3–5 hours with full exploitation and meaningful findings.
Same scope. Real issues. Much less friction.
This is validation of how effective RedVeil is.