here's how i shipped 2,500 PRs last month to production
this was originally supposed to be for Cursor Compile in London. i couldn't make it since i was livestreaming for Grok @Bot Galaxy so i'm making it available for free here on X! watch it on 2x speed, i talk slowly
@HPFCB1997@iMiaSanMia Just small different. Williams is a good player but he is going to fcb. You cant compare kubo and leao, phisically both are good. Obs is much better but brains and make ppl play kubo is 1000 years better.
@rootedcon Pues eso tiene pinta de prevaricación. @Cloudflare debería pasar a la acción y agregar todos los servicios de La liga que estén bajo sus ip's a dicho bloqueo de la liga, y que se bloqueen todos las webs de equipos, la de los sponsors y todo lo relacionado con el fútbol.
@albafella1 Someone being proud of someone's death is something to be proud. Then i dont think anything wrong about the other side taking lives as well.
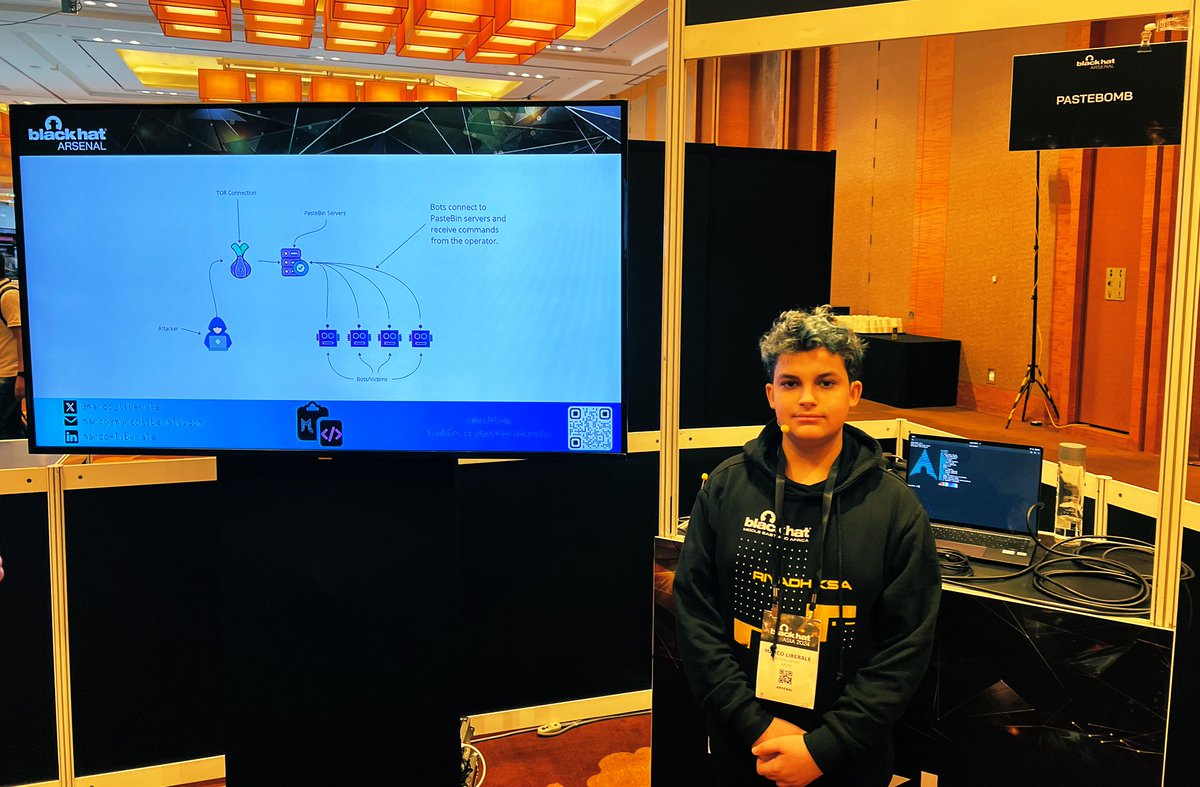
A 13 year old coded a botnet control framework that utilizes pastebin and github for control of hosts in red teaming…
This makes the hacker in me so hopeful.
Check out pastebomb when it’s dropped!
Project idea: someone could frequently pull the „Known Exploited Vulnerabilities Catalog“ from @cyber‘s as JSON, categorize and chart the vulnerabilities and create a wall of shame based on criticality and frequency
A list of some great sites
https://t.co/jAf9Ong2AC
https://t.co/qBnmhTKCmr
https://t.co/PKIKxC9Lsj
https://t.co/Yum2sCZNgf
https://t.co/uJCohbjEyI
https://t.co/zA5tTwbsdD
https://t.co/Es0aANuiRp
https://t.co/Mbg4Kn5EeJ
https://t.co/3X40mX9ubb
https://t.co/G1x8W3iArQ
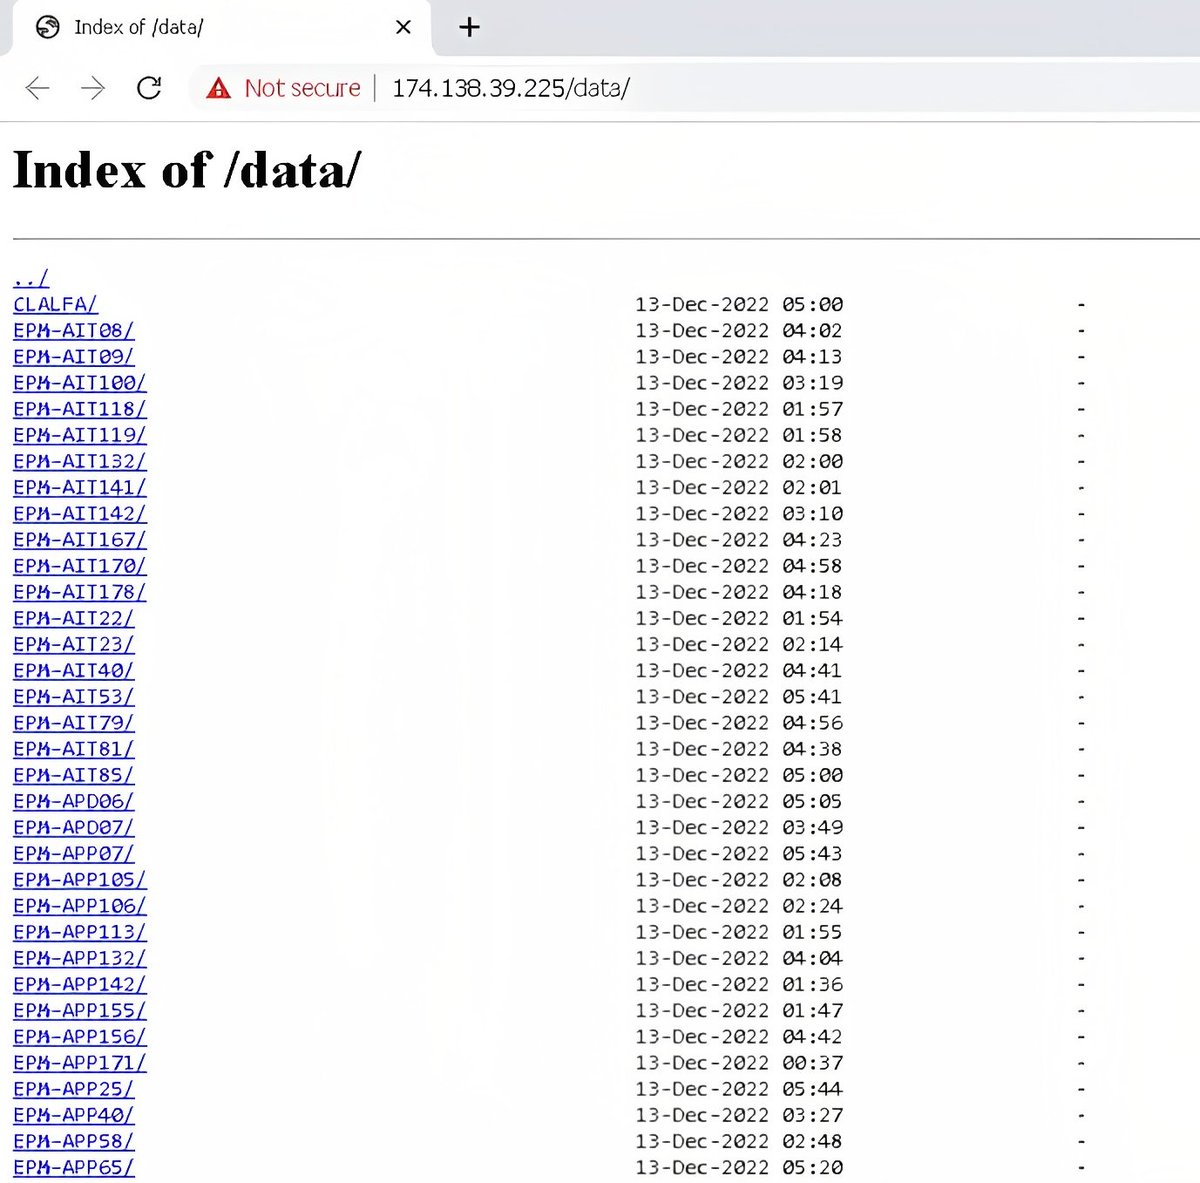
Interesting new sample of #ExMatter, exfiltration tool used by BlackCat aka ALPHV #ransomware (https://t.co/0fTs4XGUKQ)
The sample was uploaded from Colombia 🇨🇴 and the exfiltration server was exposed for a few hours revealing some stolen files 😵
▪ https://t.co/HvMlsLCp6a
"update.ps1": 558334aa04310114c9433cbd33f44bb35b05f6bd0a29be944adc086215f3b65b
FUD, but 2 comments there from @thor_scanner...
👏 to @cyb3rops.
www.bypass[.]today
😂
@StopMalvertisin
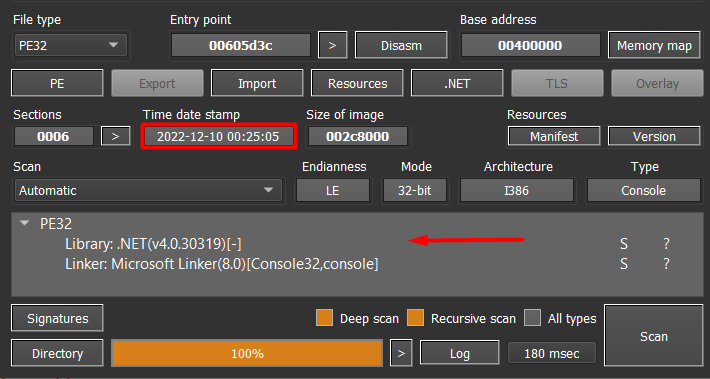
As a malware analyst I sometimes receive Microsoft files which have been manipulated.
E.g. infected by a virus and cleaned afterwards.
Here are some indicators to recognize PE file manipulation. 🧵
@GeecheeThreat
Thanks to your post, I could have found interesting information about threat modeling? Do you know who are the guys you should follow as regards this matters? Looking forward to get into this new interesting world :D