CBO at Unibeam. An account is not an identity. SIM-based, hardware-rooted authentication for banks and operators. Identity, fraud, mobile security. Tel Aviv.
"Blocking agents is not a long term strategy" - @dgwbirch. Agreed.
But the alternative isn't letting them in. It's verifying who stands behind them.
An agent is not an identity. Banks should know, in real time, which human sent it.
https://t.co/UwFkBzf6C1
A phone number alone isn't proof of possession. MediaNama reports India wants messaging apps to re-check SIM binding every 24 hours. The network matters.
https://t.co/WCga86Brvp
FBI warning - FaceStealer: hackers stole $400M+ in crypto replaying recorded webcam videos of real people in fake Zoom calls - until the target installs the "fix" themselves. An account is not an identity. A face on a screen is not a presence. Source: https://t.co/aN7Vwlhxru
New Cloudflare + Tools for Humanity framework: sites can name the agent, not which person authorized the action. High-risk actions get a verified-human tier. Banks: what verifies the human behind the agent in yours? Via Biometric Update: https://t.co/yy9VyeigIC
DOJ alleges SIM swaps and intercepted security codes helped a bank account-takeover ring bypass authentication. For banks: does your login verify the registered device, or just whoever received the code? Insider threats need separate controls. https://t.co/0N6cJu8n9N
T-Mobile reports a 99% drop in successful SIM swaps since 2022. For banks, swap prevention and authentication at login are different problems. What proof does your login rely on? Via Android Authority: https://t.co/YvOijJt8XT
South Africa's regulator proposes real-time ID checks on SIM swaps. Yet alerts stay opt-out - a customer asleep on a flight misses them. If a swap goes through, what does the bank's SMS OTP actually verify? Check the SIM, not the number. Via MyBroadband: https://t.co/TBaS62aDFb
@pymnts Before an agent can pay, the bank needs proof of who delegated the authority and limits on what it can do. A valid approval is not enough if recovery can hand those permissions to someone else. How will that chain of authority be checked at payment time?
This Cybersecurity Awareness Month, our CEO Ran Ben-David in @VMblog: "Security awareness should reinforce authentication, not function as an unwritten requirement for making it secure."
https://t.co/gnQ7AS46MX
Unibeam. Making identity harder to fake.
@pymnts@PaymentusCorp Changing an autopay setting is a useful test: can the system prove who granted that authority, which account it covers and when it expires? A known customer and an authorized action are two different checks.
כ-3,000 לקוחות מיטב טרייד קיבלו קוד SMS שלא ביקשו. לפי גלובס, התוקף ניצל API של ספק ושלף מידע אישי; לא דווחה גישה לכספים. @jonklinger צודק: קוד לבדו לא מוכיח מי מבקש להיכנס. אבל גם אימות חזק ללקוח לא סוגר API חשוף. אלה שתי דלתות שונות. https://t.co/6GNZVnintm
אולי עכשיו סוף סוף הממונה על שוק ההון יוציא הנחיה שהטמטום של "לשלוח קוד חד פעמי ב-SMS" כמזהה בלעדי להתחברות הוא סיכון אבטחה וצריך לעבור לאימות דו-שלבי בלבד?
https://t.co/2uqSsNbBKe
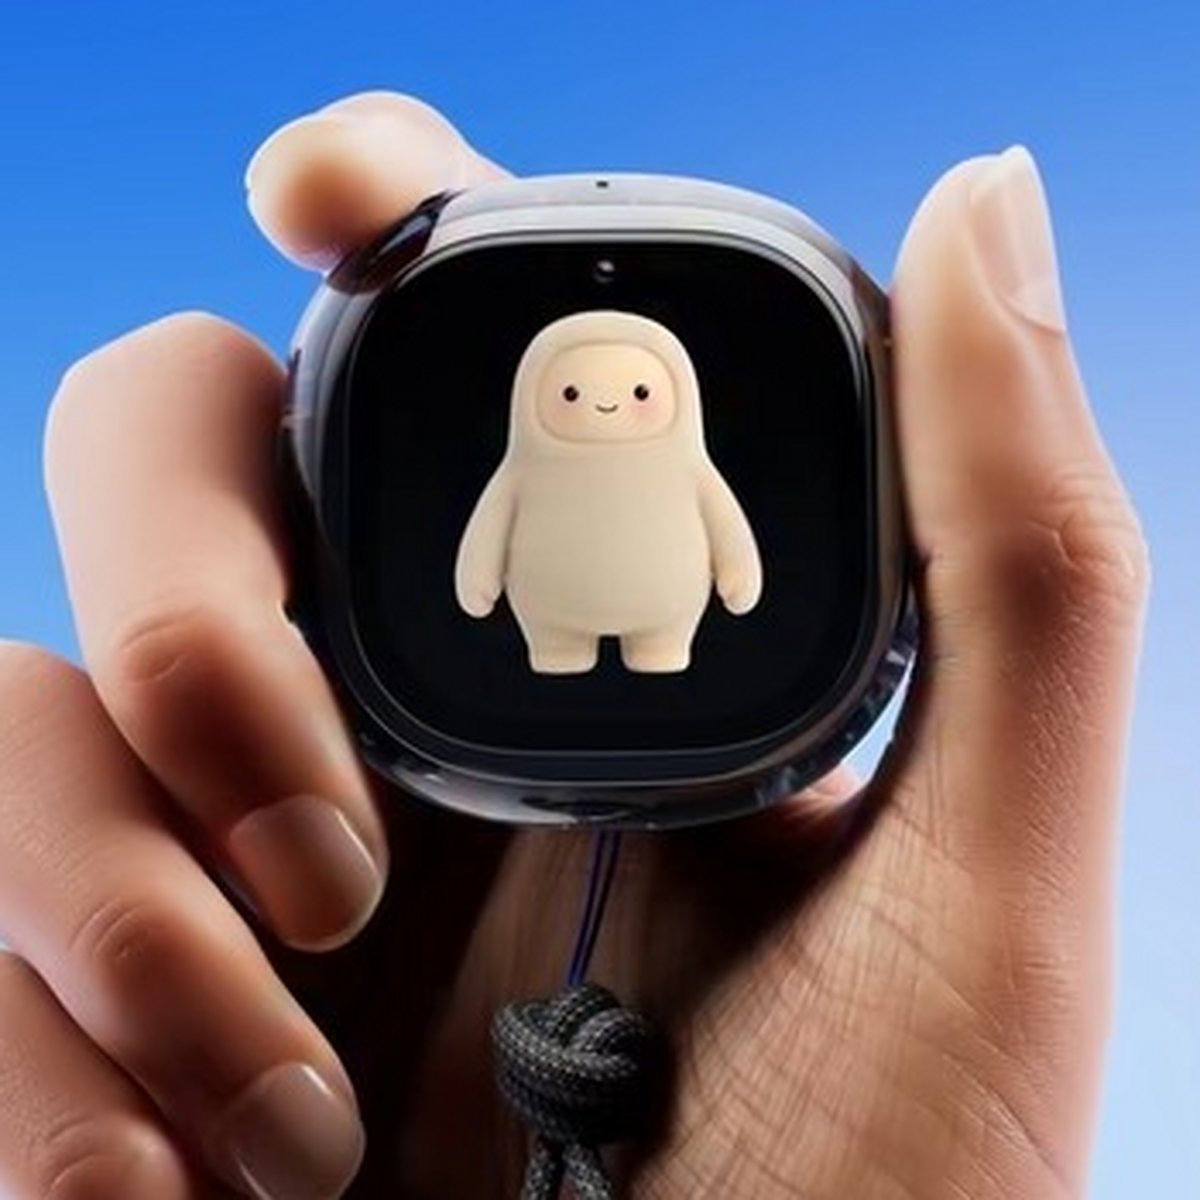
AI agents were supposed to be pure software. Then Meta put Muse in a pocket device. Tamagotchi is back, but this one can shop. Reuters reports 5G; if it uses a SIM/eSIM, that hardware could help tie purchase approval to a known device and a specific order.
@sytaylor Simon, KYA gets real at checkout. Muse Charm asks to buy. Register the agent to its owner and device's SIM/eSIM. Then challenge that SIM and bind its answer to the specific purchase the owner approves. https://t.co/rOM4yt0Miu
@ThePaypers@Riskified@ixopay Most of that loss comes from challenging people the issuer can't recognise. A silent check against the device and SIM the customer already holds lets good buyers through, and saves the challenge for the ones that actually look wrong.
EvilTokens got into 12,000+ Microsoft inboxes without needing passwords. Victims entered a real code on a real Microsoft page and approved the attacker's session. MFA passed. It proved someone clicked approve - not whose device was asking.
A bank denied a $52,800 business fraud claim because the login used the right password from a same-country IP (via Reddit). That's a risk score treated as proof - residential proxies make 'same country' a commodity. The proof of a person is device, session, and payee history.
@ThePaypers@ixopay@Riskified Integration fixes handoffs, not the root signal. If the identity proof at the top of the stack can be relayed or replayed, orchestration just moves a bad decision faster. Worth asking what the whole stack is anchored to.
@ThePaypers@Zelle Fraud rates also hide the denominator: every false decline and abandoned checkout is fraud cost that never lands in the loss column. 'No reported fraud' can mean the friction worked, or that the customer gave up. Prevention should be measured on both sides.