Hey Its Friday
* OpenCode Hacked
* php screwed the internet
* node said hold my beer
* ruby said hold my beer
* curl said hold my beer and eMudhra held that beer
* Railway said hold my beer
* OpenCode again
helluva week and I only mentioned literally 1/2 of what I know about
‼️ BREAKING: An active npm supply chain attack has compromised at least 868 packages carrying over 2 billion monthly installs with a credential-stealing worm. Shai-Hulud is back.
It started with the compromise of the GitHub account of the maintainer behind keyv, a library with roughly 127 million weekly npm downloads.
A preinstall hook fires on npm install and drops a stealer that sweeps npm, GitHub, AWS, Kubernetes and Vault secrets, and then spreads to more maintainers.
Introducing SubQ - a major breakthrough in LLM intelligence.
It is the first model built on a fully sub-quadratic sparse-attention architecture (SSA),
And the first frontier model with a 12 million token context window which is:
- 52x faster than FlashAttention at 1MM tokens
- Less than 5% the cost of Opus
Transformer-based LLMs waste compute by processing every possible relationship between words (standard attention).
Only a small fraction actually matter.
@subquadratic finds and focuses only on the ones that do.
That's nearly 1,000x less compute and a new way for LLMs to scale.
🚨 CRITICAL: Active supply chain attack on axios -- one of npm's most depended-on packages.
The latest [email protected] now pulls in [email protected], a package that did not exist before today. This is a live compromise.
This is textbook supply chain installer malware. axios has 100M+ weekly downloads. Every npm install pulling the latest version is potentially compromised right now.
Socket AI analysis confirms this is malware. plain-crypto-js is an obfuscated dropper/loader that:
• Deobfuscates embedded payloads and operational strings at runtime
• Dynamically loads fs, os, and execSync to evade static analysis
• Executes decoded shell commands
• Stages and copies payload files into OS temp and Windows ProgramData directories
• Deletes and renames artifacts post-execution to destroy forensic evidence
If you use axios, pin your version immediately and audit your lockfiles. Do not upgrade.
Matt Maher tested frontier models in Cursor v. other harnesses. Cursor boosted model performance by 11% on average:
Gemini: 52% → 57%
GPT-5.4: 82% → 88%
Opus: 77% → 93%
His benchmark measures how well models implement a 100-feature PRD. @cursor_ai consistently outperformed.
X just quietly moved X Pro behind the higher Premium+ paywall with zero notice.
One day it was there, the next day it’s “subscribe or lose it.”
No email. No warning. No respect for existing users.
This is how you treat the people actually creating on the platform?
Meet the new Stitch, your vibe design partner.
Here are 5 major upgrades to help you create, iterate and collaborate:
🎨 AI-Native Canvas
🧠 Smarter Design Agent
🎙️ Voice
⚡️ Instant Prototypes
📐 Design Systems and DESIGN.md
Rolling out now. Details and product walkthrough video in 🧵
The real benefit of giving your agents persistent memory isn't productivity. It's that you stop repeating yourself to something that should already know what you want.
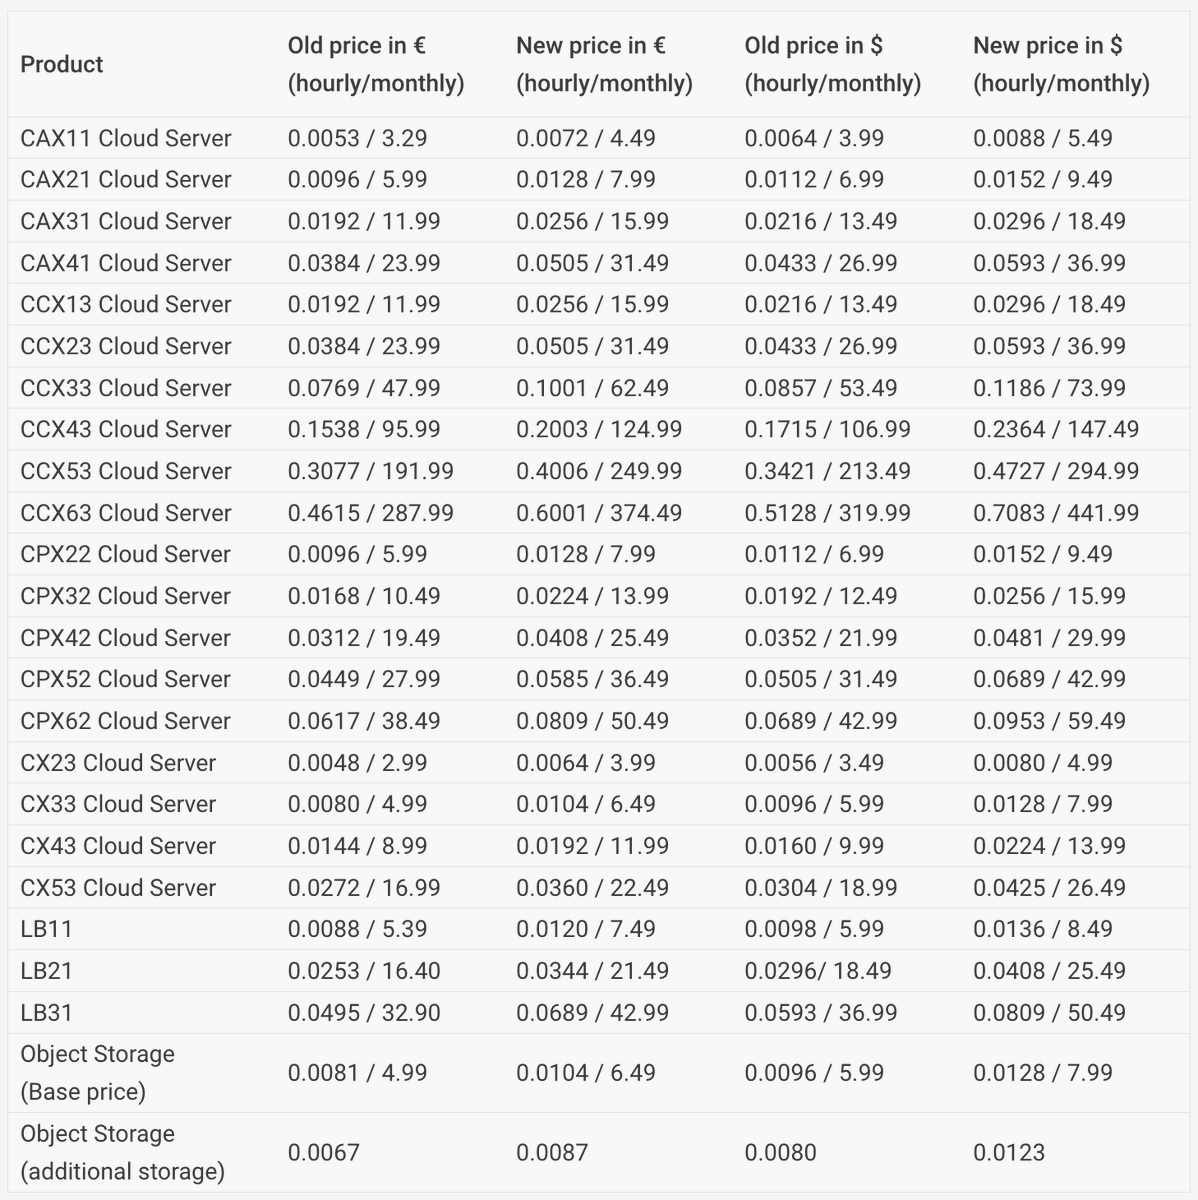
Hetzner has announced price adjustments across several of its services, citing rising energy costs and general inflation. If you are using their cloud or dedicated servers, you may want to check how these changes impact your infrastructure costs.
https://t.co/4DNzAXL5Bj 📈💻
I genuinely believe that we're becoming the bottleneck for AI agents. The progression has been incredible: at first, we just chatted with AI, then we used them as collaborative programmers (instructing them on what to do), but now, with models so advanced and agents able to orchestrate subagents, we're pretty much the bottleneck if agents have to ask us for anything. They're now capable of figuring things out on their own and resolving issues without our involvement.