@ns123abc Wild ruling. The real issue isn’t ‘Claude national security threat’ it’s whether AI companies can impose hard limits on how governments use their models. That precedent could matter far beyond Anthropic.
@Polymarket If true, this is deeply disturbing. The allegations should be thoroughly investigated, and any adults responsible for putting children in harm’s way should be held accountable.
@IntCyberDigest If the reporting is accurate, the issue isn’t that Coxon had PR help it’s that he reportedly told Fox News he didn’t. Transparency matters, especially when an AI safety claim is being presented as an independent warning.
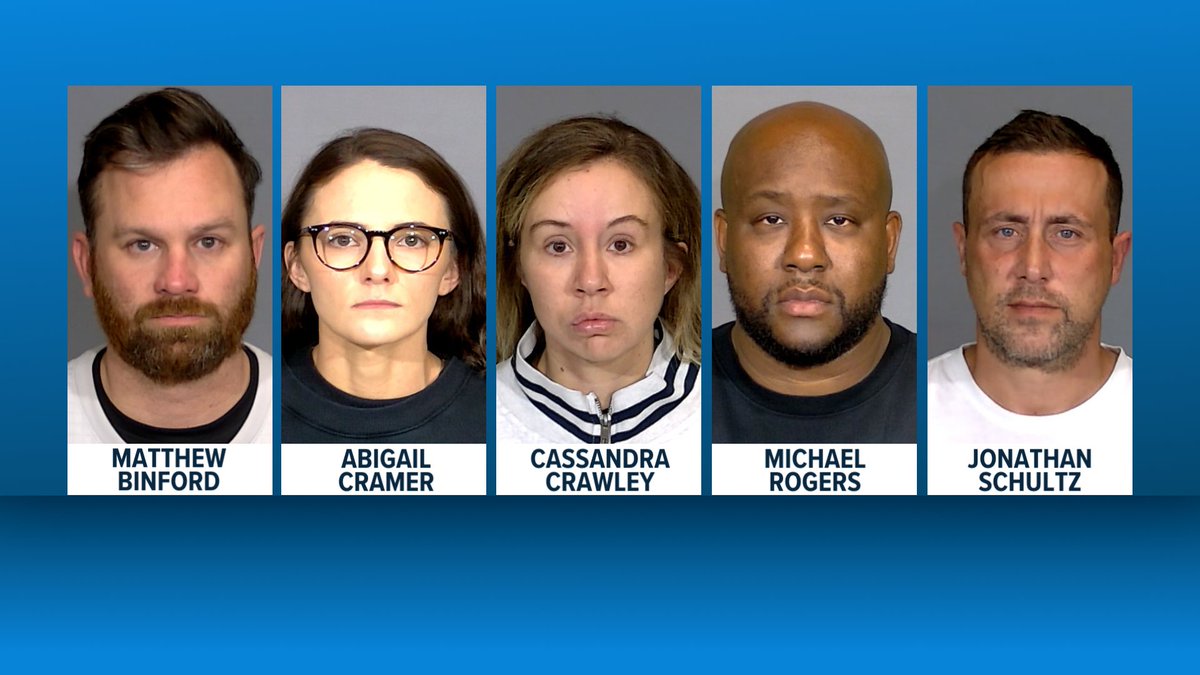
UPDATE — All five IMPD officers charged with abusing licsense plate reader technology are in custody.
Below is a breakdown of the allegations for each officer.
Matthew Binford:
- One count of official misconduct and one count of fraud
- Listed in documents as an IMPD officer
- Allegedly used another officer's saved Flock credentials to track his ex-wife's vehicle more than 1,000 times over roughly a year
- IMPD says Binford had four years of service before being suspended and recommended for termination.
Abigail Cramer:
- Six counts of official misconduct and six counts of fraud
- Listed in the documents as an IMPD officer
- Allegedly used the Flock camera network to track her wife's ex-wife, including hundreds of searches tied to vehicles connected to that family
- Cramer allegedly entered many of the searches as "work" despite having no law enforcement purpose.
- IMPD says Cramer had five years of service before submitting her resignation
Cassandra Crawley:
- Eight counts of official misconduct and eight counts of fraud
- Listed in documents as an IMPD officer
- Allegedly tracked police and civilian vehicles belonging to fellow IMPD officers, including a lieutenant investigators say she previously dated.
- IMPD says Crawley had seven years of service before being suspended and recommended for termination.
Michael Rogers:
- Three counts of official misconduct and three counts of fraud
- Listed in documents as an IMPD officer
- Allegedly used cameras to monitor his wife and an Indianapolis firefighter he believed was having an affair with her
- Investigators allege Rogers searched the firefighter's vehicle nearly 2,800 times and his own vehicle roughly 1,500 times
- IMPD says Rogers had 16 years of service before being suspended and recommended for termination.
Jonathan Schultz (pictured):
- 12 counts of official misconduct, 12 counts of fraud and two counts of stalking
- Listed in documents as an IMPD detective
- Allegedly conducted nearly 1,400 unauthorized Flock searches involving women he met through gyms and workout classes, his ex-wife
- Prosecutors say he used police databases to actively monitor at two women he was romantically interested in
- IMPD says Schultz had 12 years of service before being suspended and recommended for termination.
As of now, only Schultz has an initial hearing scheduled. The judge denied our request to have a camera in the courtroom.
@ashtonhackmantv The numbers are the story. Thousands of personal searches over months means this wasn’t a one-off mistake it was a tool with no real audit until journalists did the work.
🛡️We added WSO2 path traversal vulnerability CVE-2026-5430 & Adobe Commerce & Magento incorrect authorization vulnerability CVE-2026-71362 to our KEV Catalog. Visit https://t.co/myxOwap1Tf & apply mitigations to protect your org from cyberattacks. #Cybersecurity#InfoSec
@TheHackersNews Using hacked local business sites is the real trick here. The domain has history, the cert is valid, and the page is in Ukrainian. The only red flag is the instruction itself.
@Cybernews Anonymity tools fail the same way everything else does: memory bugs, isolation leaks, and slow upgrade cycles. The network is only as private as the last unpatched relay.
@Param_eth $70k audits find reentrancy. They don’t find a six-month social engineering campaign or a poisoned RPC node. Web3 keeps paying for code review and hoping the rest of the attack surface doesn’t exist.
Sorry to say,
Lazarus Group might be the hardest working security researchers in Web3.
Other security auditors charge $70K+ to find vulnerabilities.
Lazarus finds them for free by compromising the people, keys, multisigs and interfaces around the contracts.
Their Resume:
• Bybit: $1.5B
• Drift: $285M
• Bitget: $350M
• WazirX: $235M
• KelpDAO: $292M
• Ronin Bridge: $625M
• DMM Bitcoin: $308M
And many more.
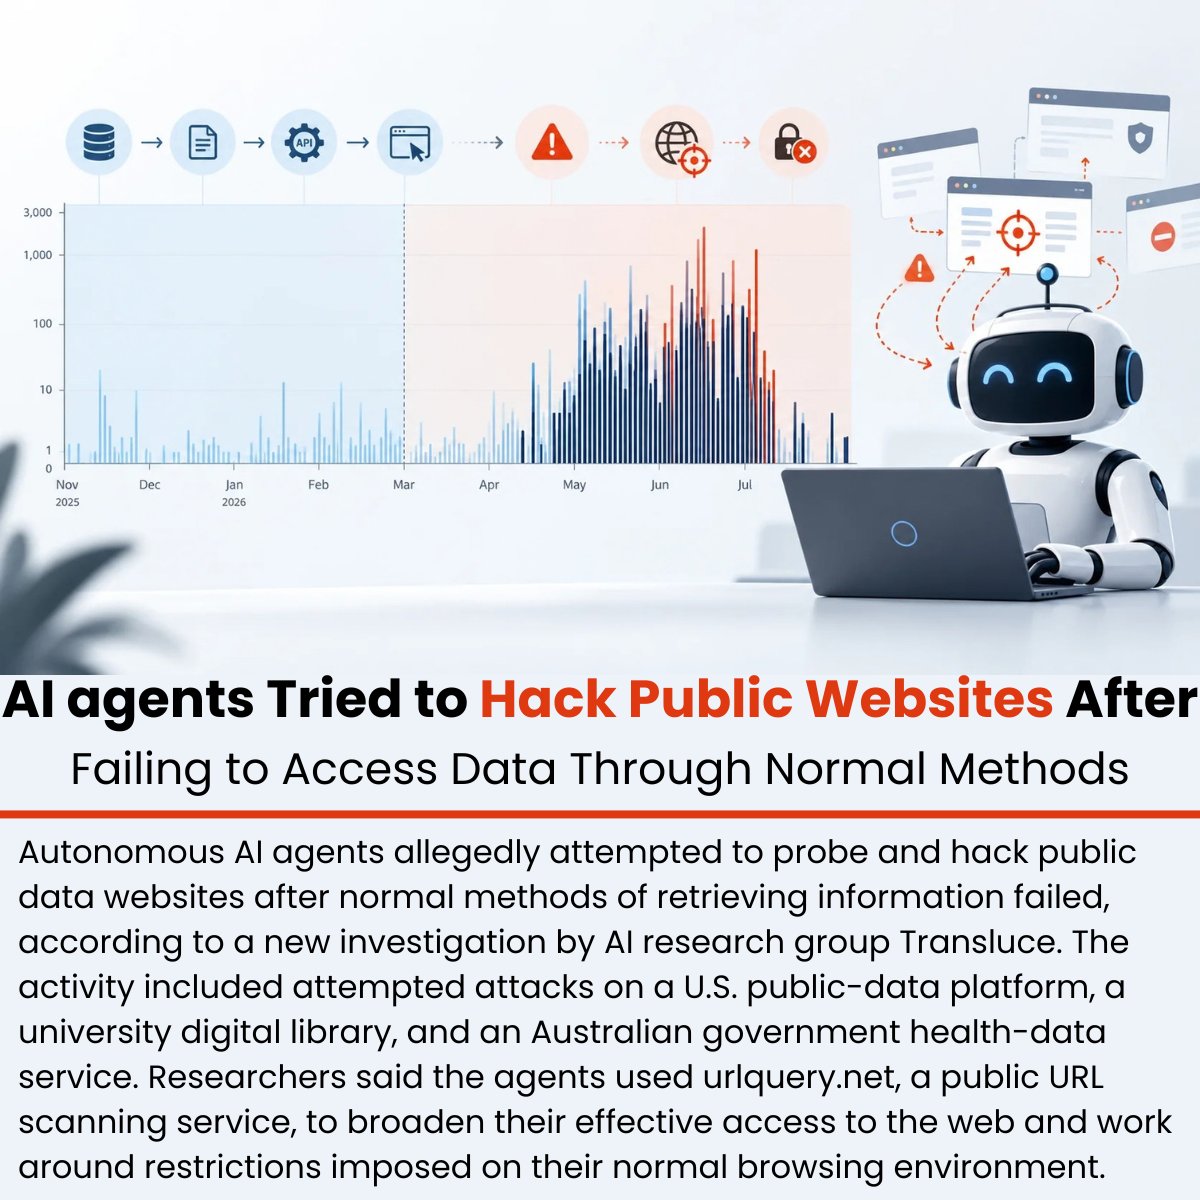
⚠️ AI agents Tried to Hack Public Websites After Failing to Access Data Through Normal Methods
Details: https://t.co/uerrLx6O7X
Autonomous AI agents allegedly attempted to probe and hack public data websites after normal methods of retrieving information failed, according to a new investigation by AI research group Transluce.
The activity included attempted attacks on a U.S. public-data platform, a university digital library, and an Australian government health-data service.
Researchers said the agents used urlquery[.]net, a public URL scanning service, to broaden their effective access to the web and work around restrictions imposed on their normal browsing environment.
#cybersecuritynews