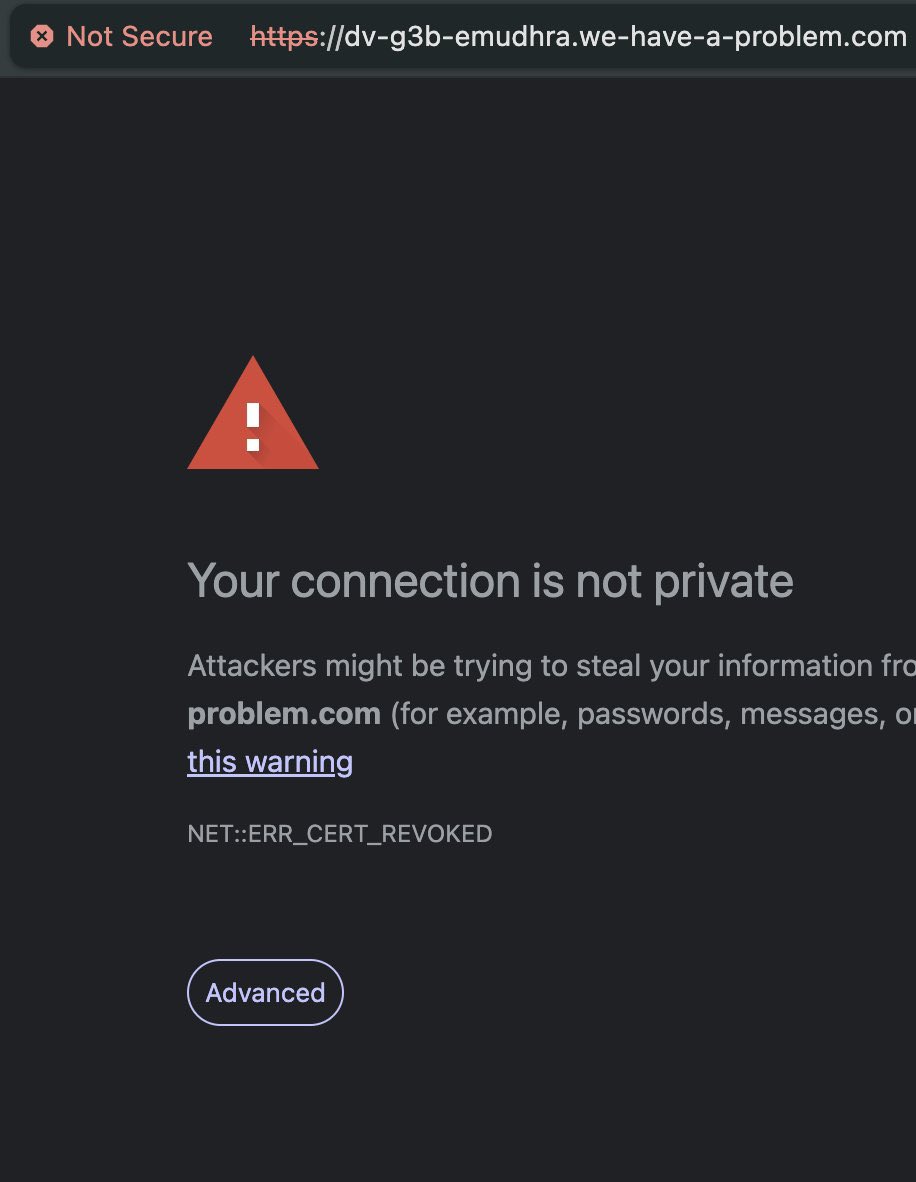
For those who don’t understand the eMudhra incident. Trying to explain in simple words. Certificate authorities issue digital certificates that help your browser verify a website’s identity.
@neorevolt@gollapudi_buchi True. eMudhra generated the CA key pair. A script was involved in the key-generation process, and it produced weak private keys. eMudhra's main CA signed the intermediate certificate. This established the intermediate CA's place in the trust chain.
This is why infosec is more than selecting strong algorithms. Secure randomness, key generation, independent validation and certificate issuance controls matter just as much. When a trusted certificate authority gets these basics wrong, kya hi bola jaye aage.
Why eMudhra incident is a serious issue? I will try to explain it more properly in this thread. Just understand first that it is difficult to break modern cryptography.
So in this case nobody needs to break elliptic-curve cryptography. If a private key is 4, an attacker can simply try that value and check whether it matches the public key. It is like the password of your twitter account is qwerty.
If you really love her then give her peace of mind, treat her like your most critical asset. Give her root access to ur heart, encrypt every promise with honesty & loyalty,eliminate every vulnerability that could hurt her, & make loving her a permanent, non-revocable commitment.