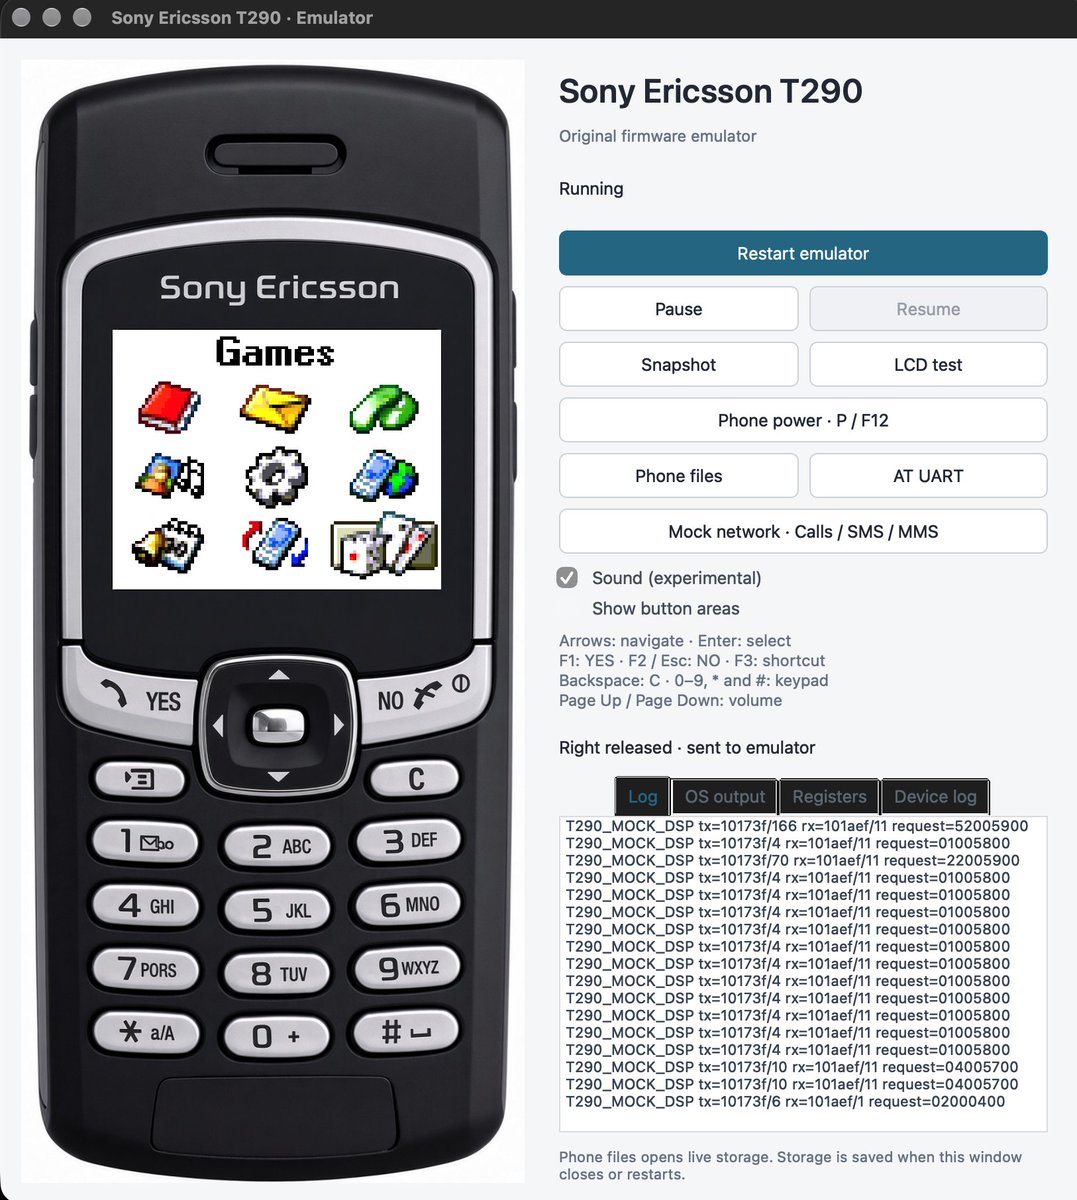
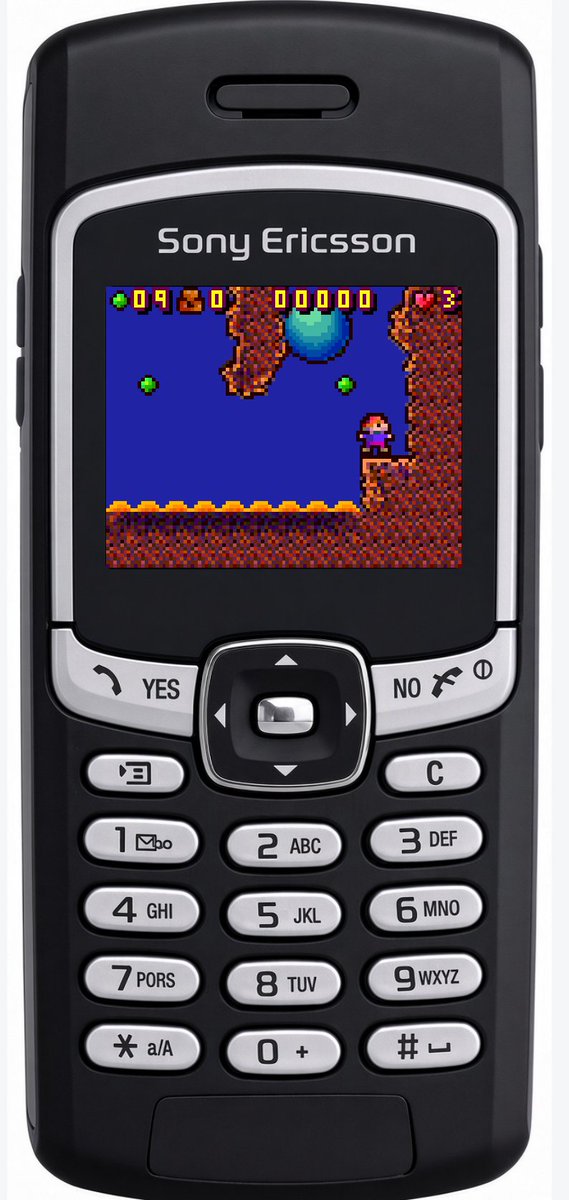
@jumarmacato@Tickford_daniel@bookazoid_ I will share the code for T290 same as I did for W800 probably in following days, need to clean it up a bit. I see it as digital archive for our nostalgic childhood memories, physical devices won't exist for too long. I just saw @bookazoid_ tweets and started experimenting :)
@jumarmacato@Tickford_daniel@bookazoid_ Heh, the same T28 platform :) Everything works more or less. Had to vibe code runtime functions, as it seemingly does not exist in publicly available firmware, but GPT-6 Astra didn't had issues with that, fixed all issues one by one. Sound, games, UART works.
@Tickford_daniel@bookazoid_ I am trying to vibe code the same with Sony Ericsson phones, works nice so far, with some bugs obviously :) https://t.co/RKOVmy9OQP
Currently also have working Sony Ericsson T290, with Mophun games running mostly without issues.
💪🔐@SecGPT's cybersecurity arsenal has been upgraded with hundreds of new resources:
- writeups, reports
- cybersecurity documents
- cheatsheets for testing and prevention.
More data is added weekly!
#SecGPT#AI#cybersecurity#pentesting
We've just used Stepper to solve a new @WebSecAcademy lab.
https://t.co/sJv4m2rVe8
It's a great BApp that allows you to construct multi-step sequences and extract data from any step and re-use that data. This is all done using repeater style tabs.
https://t.co/r1qlErWcVt
A new fully disclosed HTTP Request Smuggling ATO report from yours truly. Thanks @prateek_0490 and @Zomato for working to help kill this nasty bug. 🙏
Want to crack some hashes but your VM is too slow? Here's a cool tip: you can (ab)use Google's Colaboratory to spin up two beefy graphics cards to do the cracking for you. It's free, and works really well! Get started here: https://t.co/T4dESE10jy
During my interview with @NahamSec I've shared a very handy #BugBountyTip for wide-scope #BugBounty programs:
Look for Google Analytics Tracking IDs (UA-XXXXXX-X) and use i.e. https://t.co/2dTg4vV9it to discover more assets sharing the same ID.
just a little mindmap summarizing this great write-up of several ways that can be used to elevate privs from sensitive-priv to system:
https://t.co/Ky6FTImTn2
I just love hacking..
The thrill of black box app testing for me is trying to figure out the pieces, sorting the puzzle, understanding the logic, the design, the purpose, and then.. force it do thing is wasn’t supposed to.. love it!
#h1415#bugbounty#CyberSecurity
Did some fun hunting today & actually had to pinch myself. What great times we live in. Times when all we need is a internet connection and a laptop to go hack on some of the biggest corps of our day. Without the risk of legal repercussion & instead get paid. Epic times indeed..
When everyone in .corp is going on about APTthis and APTthat and your “what do you do about things like Emotet and Trickbot?” is met by blank stares.
Which doesn’t invalidate worrying about APT, but if you can’t root out Emotet you have slim chance against APT.
Baby steps.