[HACKER TIP] If you are testing Open Redirect but there is a blacklisted character, you can test it with a chinese dot to bypass it or any other Unicode Character.
example:
redirect_to=////evil%E3%80%82com
#bugbounty#hackertips#openredirect
New Writeup - Circumventing Browser Security Mechanisms For SSRF. In this blog post we find our way around browser's mixed content policy to perform a SSRF against headless Chrome. Ft. @S1r1u5_@iamnoooob@rootxharsh
https://t.co/Ma7OSFL24C
Managing #safety remains a vital task in #construction, but it’s a job that involves heavy record-keeping and constant training for success.
How 3 construction companies use #tech to improve safety ✅👉 https://t.co/K6jt5GO3tk
#RINNO#deeprenovation@constructdive
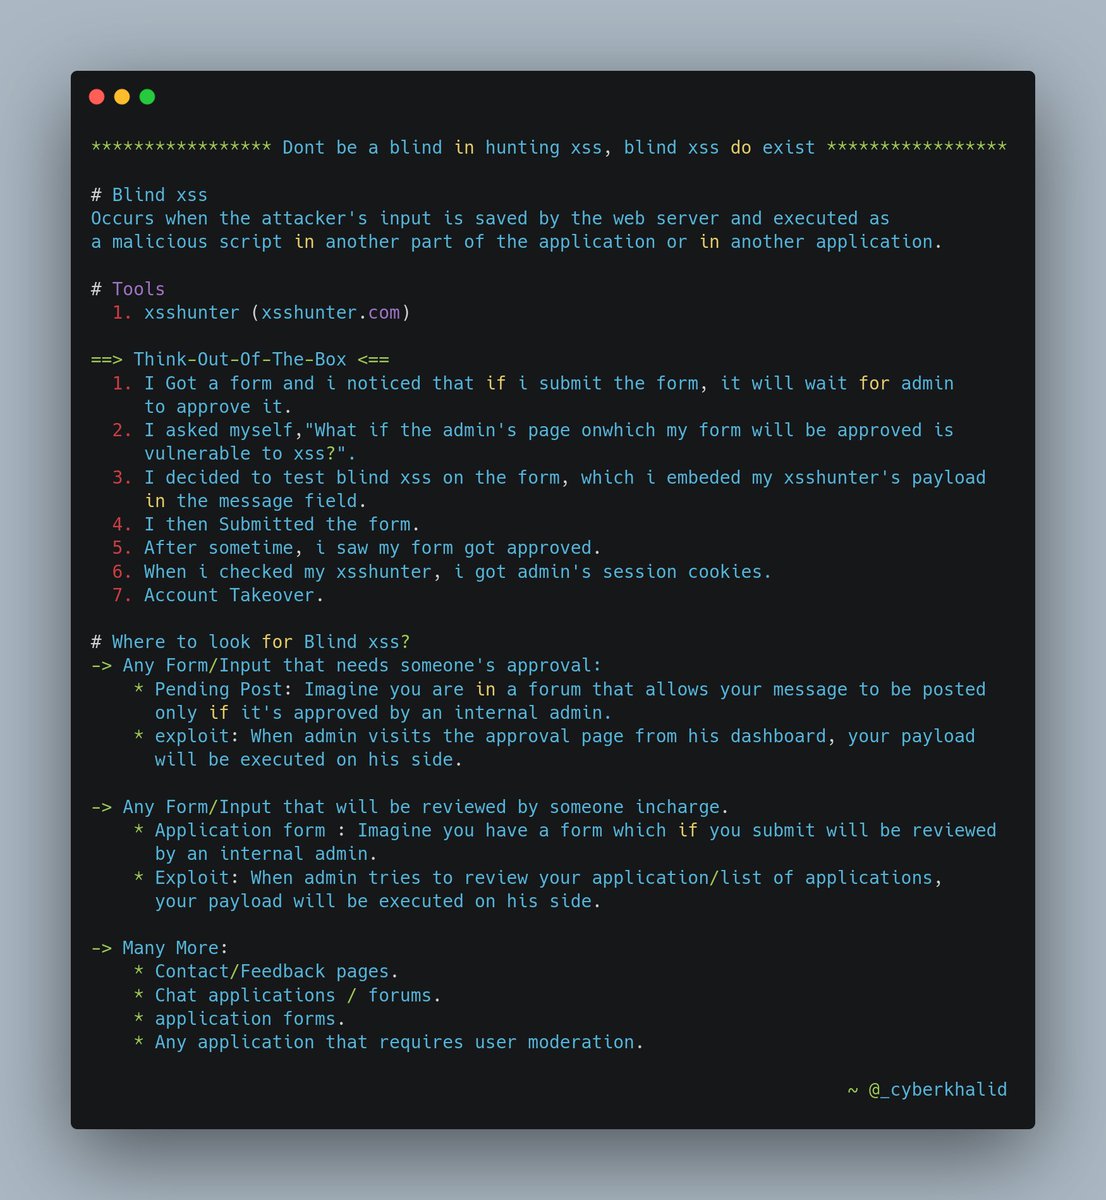
Blind SSRF vulnerabilities arise when an application can be induced to issue a back-end HTTP request to a supplied URL, but the response from the back-end request is not returned in the application's front-end response.
#cybersecurity#infosec#ethicalhacking#infosecurity