Synack Red Team / Addicted to Python / Bug Hunting / InfoSec / Whiskey. Master of the dark art of 10 finger hacking. Views do not represent my workplace.
EXPOSED: 200+ AI Agents have been LEAKED...
These Agents SELL for $5,000+ per build and cover 20+ industries...
Inside the file you’ll get:
→Social Media Agents ($8k+)
→Creative Content Agents ($3k+)
→Cold outreach Agents ($3k+)
→Lead Booking Agents ($6k+)
→Customer support agents ($5k+)
→Data & Scraping Agent ($8k+)
→Lead qualification agents ($4k+)
→Productivity, HR, Analytics, DevOps & legal Agents also!
100s of plug & play systems that save you time AND money.
Follow + RT + Comment “AGENTS” and I’ll send you the drive for FREE!
BONUS: An n8n Masterclass, so you know how to run, customize, and scale every workflow.
PS: I'm only keeping this live for 48 hours. After that, it's back to $5k+ per agent. Your move.
super hot technique for preventing EDR dll loaded into the process from Marcus Hutchins (malwaretech): https://t.co/1gnuueZPL4 just tested it successfully ;)
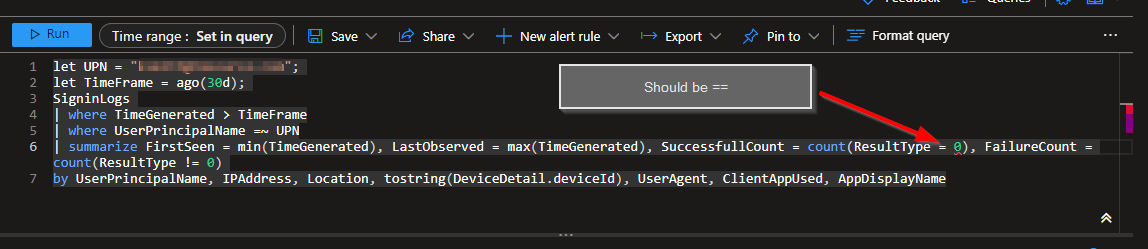
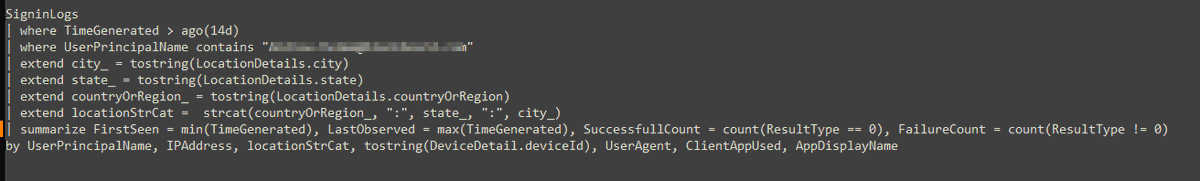
@castello_johnny I believe there is an issue with one of your KQL queries. I believe this should be "ResultType == 0". The results returned are incorrect if you use one "=". I find adding location details helps me too. BTW I really enjoy your site.
https://t.co/ibokPjAe8C
my favorite (and might be the most complete) wifi hacking guide (+pwnbox setup) by @Xst3nZ:
https://t.co/XAt2rvuBzX
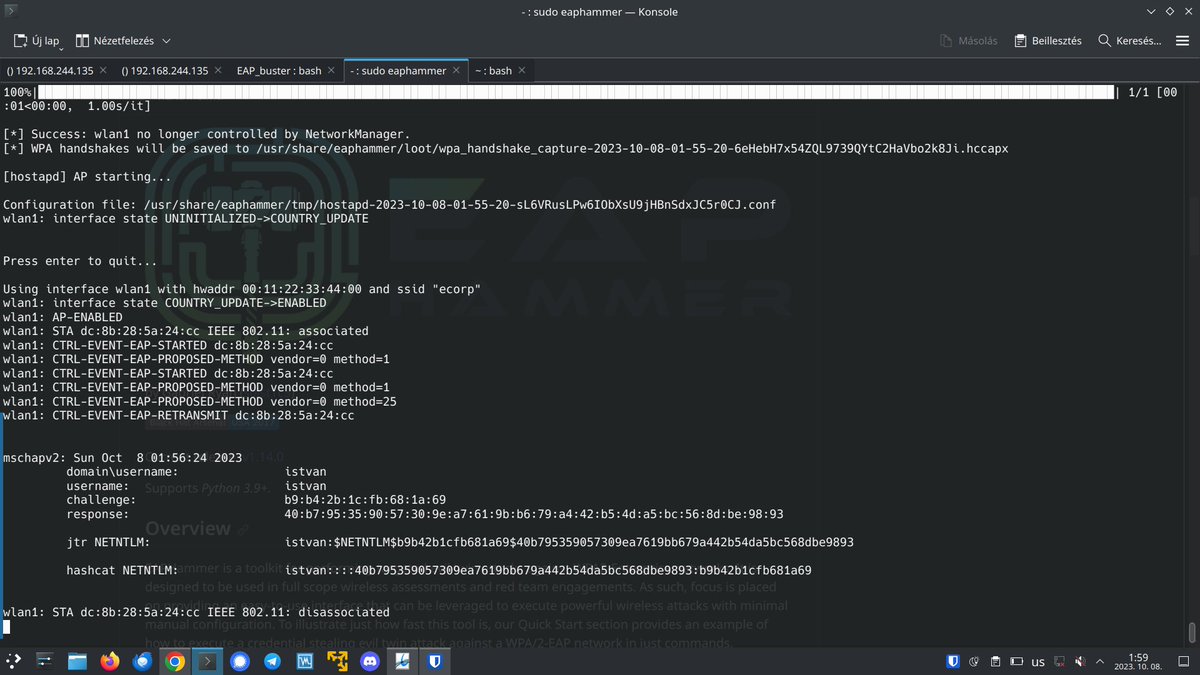
following this it was relatively easy to perform an evil twin attack after setting up a wpa-eap home lab (managed to capture a challenge using eaphammer 🙂).
Warning: People’s Republic of China (PRC)-linked cyber actors known as BlackTech have demonstrated the ability to hide in router firmware. Learn about mitigations to detect this activity and protect devices. https://t.co/QeO6vS7ThI
I have updated my course significantly!
Fresh new content and cheat sheets for:
👁️ IDOR
🕸️ SSRF
🍷 recon techniques
🏹 Red team cred tactics
And added a bunch of contextual places to look for most of the vulnerabilities!
Can’t wait for Nov/Dec!
https://t.co/AfbSF6kHGP
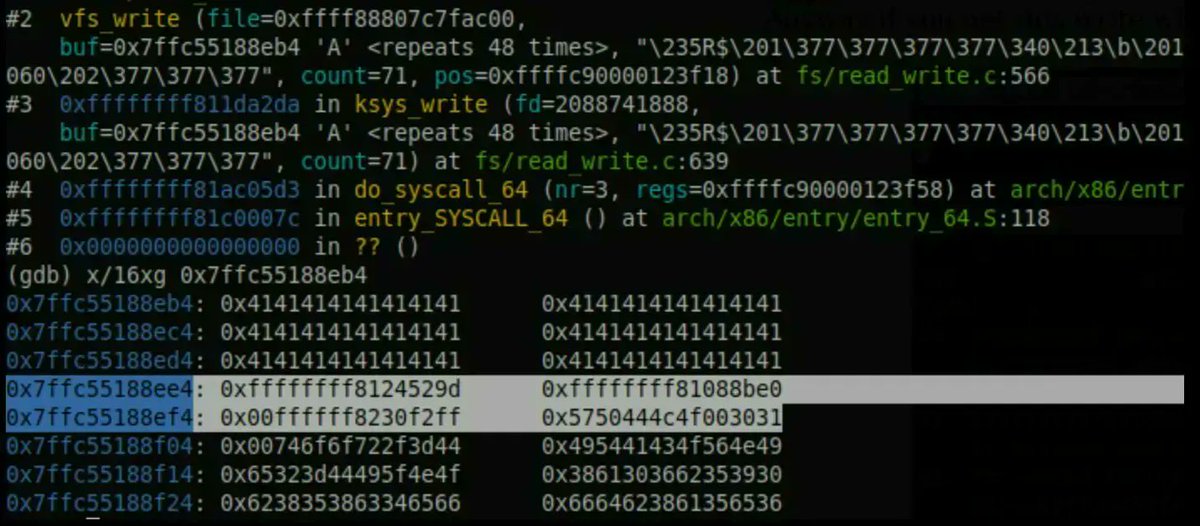
Learning the basics of Linux kernel exploitation
Excellent series by @k3170Makan
Debugging with QEMU: https://t.co/MFkoXhjCXP
Stack Overflows: https://t.co/E6meVjl5ub
RIP control: https://t.co/mIdgQs4F0f
#cybersecurity#infosec#Linux#kernel
Common parameter names vulnerable to SSRF 👇
dest
redirect
uri
path
continue
url
window
next
data
reference
site
html
val
validate
domain
callback
return
page
feed
host
port
to
out
view
dir
show
navigation
"RedCloud-OS: RedCloudOS is a Cloud Adversary Simulation Operating System for Red Teams to assess the Cloud Security of Leading Cloud Service Providers (CSPs)"
#infosec#pentest#redteam
https://t.co/bD8OxKP4jZ
some ways to bypass 403
1- using space symbols
exmaple:
/admin -> 403
/admin%09 -> 200
/admin%20 -> 200
2- use traversal
Example:
/admin -> 403
/..;/admin -> 200
you can fuzz with traversal sometimes that's end with results
Example: /..;/FUZZ
#bugbountytips#BugBounty
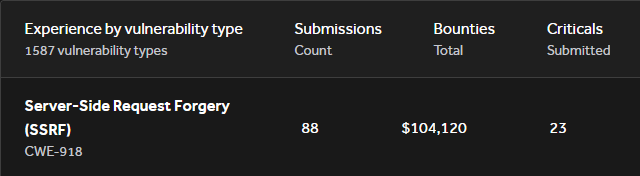
I've made over 100k on SSRF vulnerabilities.
They aren't always as simple as pointing it at localhost or AWS Metadata service.
Here are some tricks I've picked up over the past 5 years of web app testing: