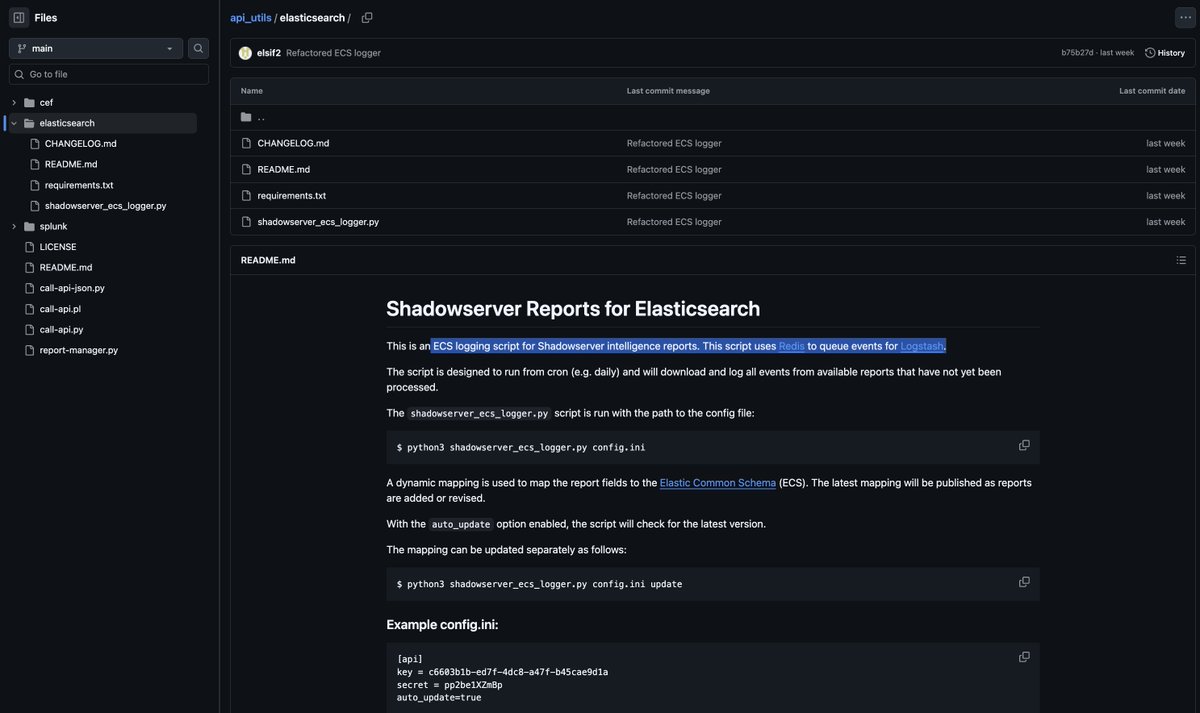
Using ELK & interested in automating ingestion of our threat intel for your network/constituency via our API?
We have introduced an ECS logging script for our intelligence reports. This script uses Redis to queue events for Logstash.
Check it out at https://t.co/feZj5D03uV
Data shared in https://t.co/BDRM77a34k
World Map view:
https://t.co/huCfYbzh3V
Tree Map view:
https://t.co/8AnT9YiEat
Exposure tracker: https://t.co/c66KjzOWyP
See also @CERT_FR https://t.co/jctvkBkPhv
Additional info: https://t.co/3Lzkr3NtJT
Copeland/Dixwell XWEB refrigeration web controller incidents: As in the case of Danfoss, for a long time we have been sharing exposed Copeland XWEB Pro & Evo panels in Device ID reporting. We see around 1200 instances daily - these should of course not be publicly accessible.
Data shared in https://t.co/1uPaaDBimE
World Map view: https://t.co/geQYm6aIH5
Tree map view: https://t.co/ghkRnUbRHu
Exposure tracker:
https://t.co/wvSBuIbMqS
Background: https://t.co/ItRkV4iApt
We are working on possible CVE tagging too
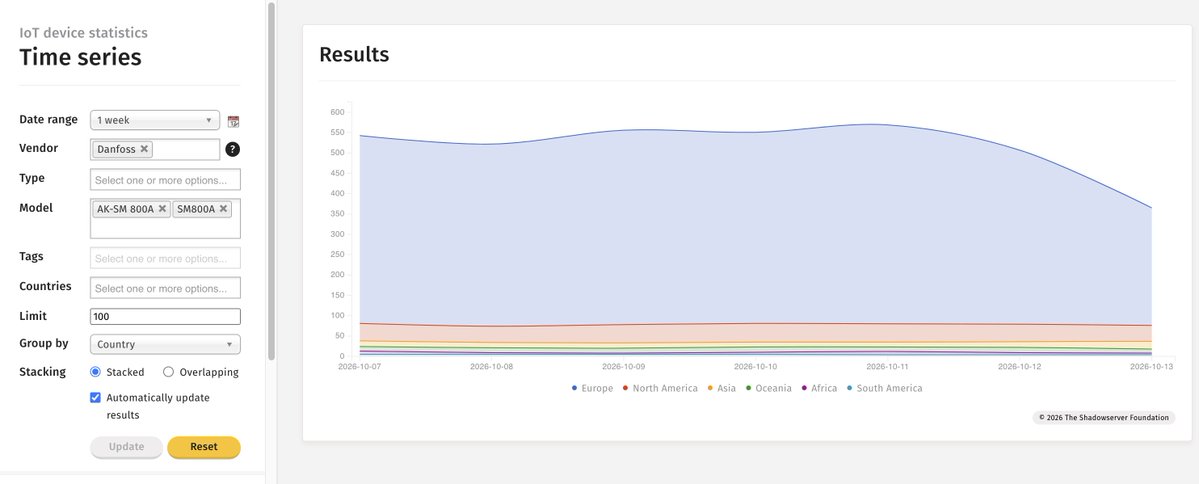
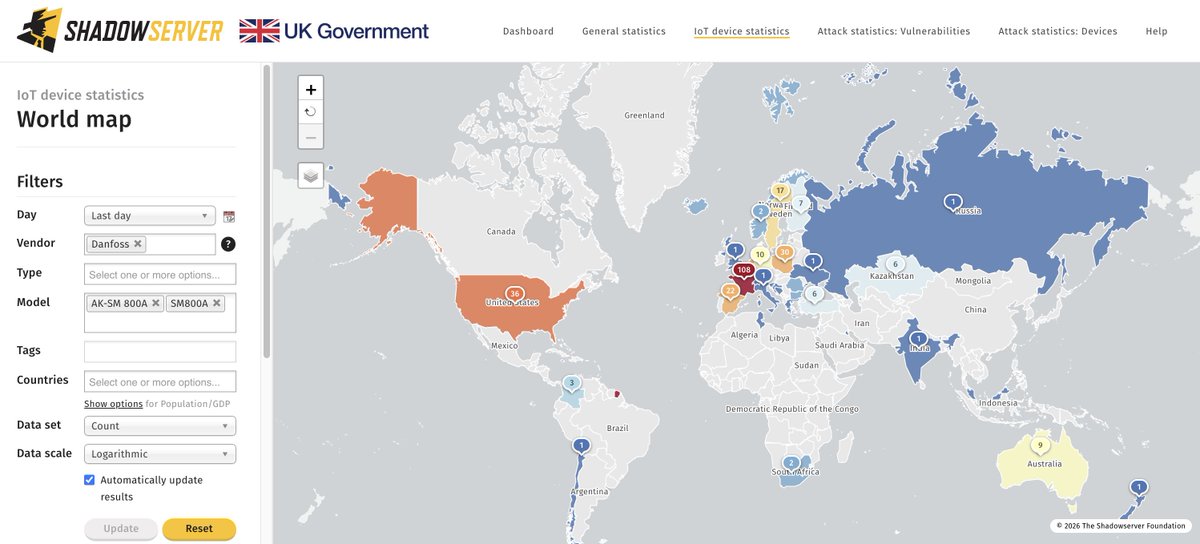
Danfoss refrigeration incidents: We are sharing exposed instances for a long time in our Device ID reporting, daily. For Danfoss AK-SM800A we still see at least 365 unique instances daily (drop from over 550 last few days) exposed. These need to be taken off the public Internet!
For MikroTik with SSH enabled, check out our Accessible SSH reporting (https://t.co/pLCz27PyMB), with the tag 'mikrotik' https://t.co/iy5eqYvrTw - just over 119K seen daily currently
Background: https://t.co/5SbLuwuZ1L
We have started reporting out (daily) MikroTik instances with exposed proprietary services, such as WinBox & Bandwidth Test server (btest): https://t.co/s8ibIXWw4M
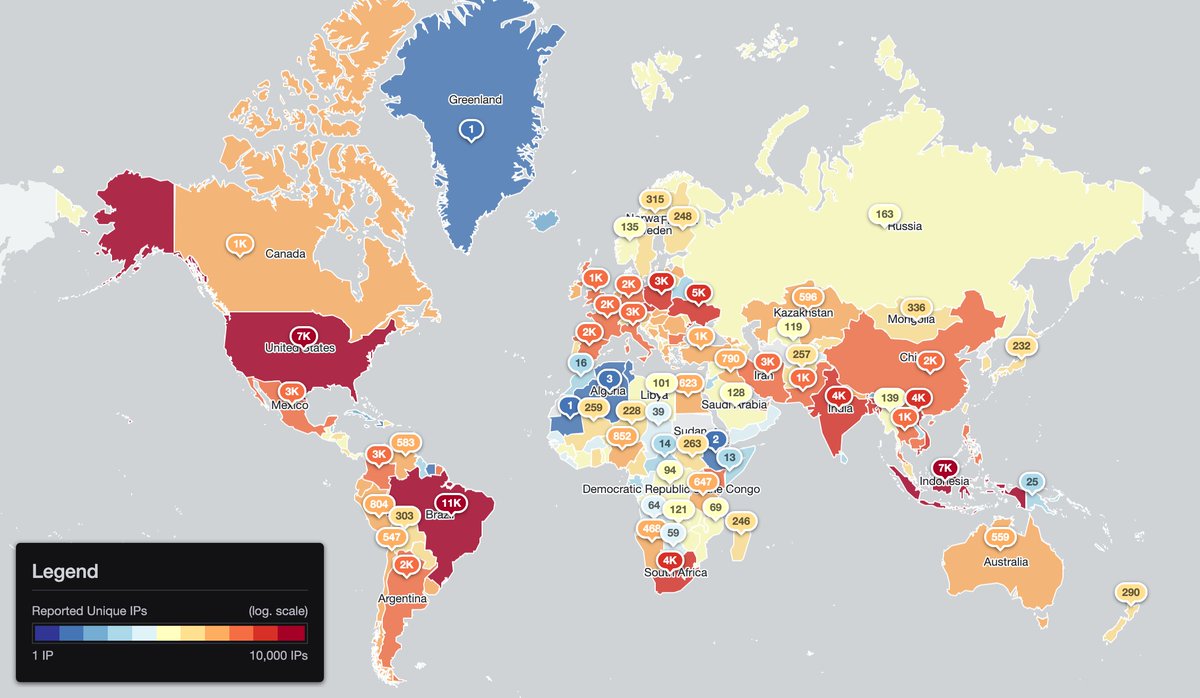
Around 2.6M exposed instances shared daily. Top: Brazil, Indonesia, USA.
Tree map stats: https://t.co/fvchcFJ2zM
These should not be publicly accessible on the Internet due to potential vulnerabilities, such as the recent CVE-2026-67277 https://t.co/IiWG9VsMIU
You can find all our MikroTik detections in Device ID report https://t.co/1uPaaDBimE (around 3M daily): https://t.co/ilWjNmiz5k
IP data in Vulnerable HTTP reporting tagged 'cve-2026-86218': https://t.co/qxv0Gv5ELc
218 out of 1399 seen in total. This is one week after exploitation activity was first reported publicly.
Patch info: https://t.co/Z1lWNfAD3Q
Background on incidents: https://t.co/gi4tvLPuwQ
Still 218 instances of N-able N-central seen unpatched to CVE-2026-86218 pre-auth RCE that is exploited in the wild & on @CISACyber KEV. Top: US (141)
Stats - World Map view: https://t.co/X0pOrgWfPQ
Tracker: https://t.co/XoqROt23pN
Compromised Website Report: https://t.co/D1KZAGvfTr
Thank you to @GreyNoiseIO for the share! Background with info about the AI-orchestrated campaign behind the compromises (includes IOCs): https://t.co/DL5pzdVThw
We shared a one-off share of over 400 compromised PaperCut NG/MF instances (via CVE-2026-81578/CVE-2026-82078) observed by @GreyNoiseIO. IP data in our Compromised Website reporting for 2026-09-11, tagged 'papercut-compromise'.
Dashboard Tree Map stats: https://t.co/8AQlPZIEgr
@onyphe@BleepinComputer Yes, looks like we undercounted due to a bug - we already shared out more complete results for the day and will have full results going forwards which will be similar to the numbers you mentioned
Since 2026-09-04 we are scanning/reporting daily unpatched versions of Plex Media Server in response to an advisory issued by Plex https://t.co/gpyHdUhmAM for v1.43.2 & earlier. Over 36K instances found still unpatched! Top affected: US (16K)
World Map: https://t.co/sWvbE93nQ1
No CVEs have been issued meaning the vulnerabilities are essentially invisible to the security community limiting an effective response.
We tag the raw IP data shared 'vulnerable-plex' in Vulnerable HTTP reporting: https://t.co/qxv0Gv5ELc
Tracker: https://t.co/kvvSYPCnMT
We added MikroTik SSH identification to our daily scans on 2026-09-04, in response to MikroTik's patches https://t.co/VqlBOo0C8G. As discovered by @CERT_Polska_en https://t.co/5SbLuwuZ1L unpatched MikroTiks can be compromised, if device supports remote access using SSH protocol
At least 122,500 MikroTik devices with SSH accessible found per 24 hour scan window on 2026-09-05 (no vulnerability check).
IP data shared daily in Accessible SSH reporting https://t.co/pLCz27PyMB tagged 'mikrotik' & Device Identification reports: https://t.co/1uPaaDBimE
Make sure to install Emergency Patch (Release 3) - but assume compromise.
Background on PaperCut incidents: https://t.co/KblQ50FLS5
Detection based on Nuclei template by darses - https://t.co/LeyECbNx6E
#CyberCivilDefense
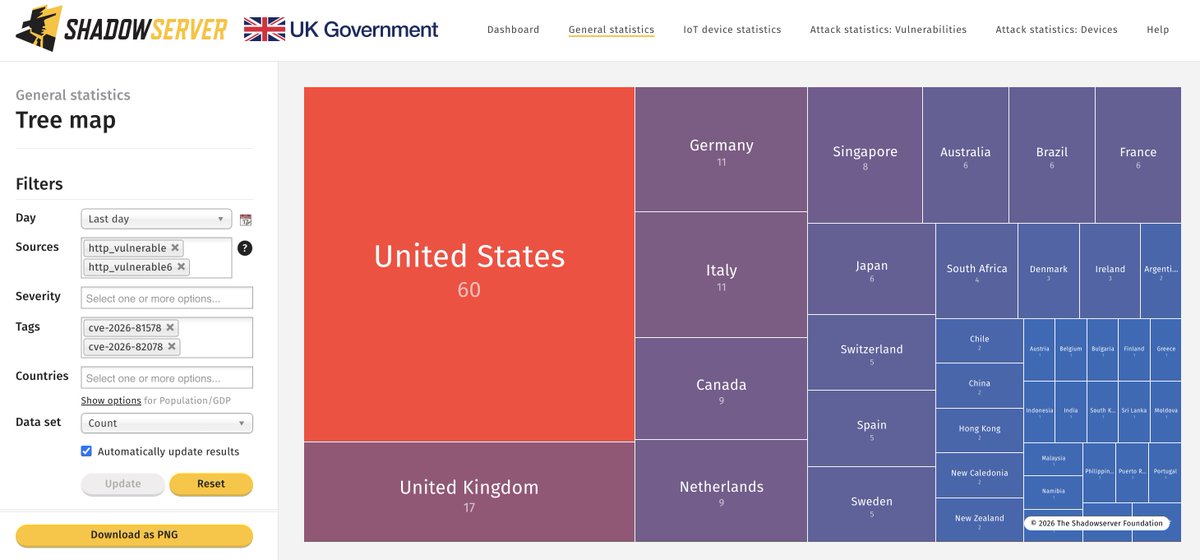
PaperCut MF/NG incidents: At least 204 instances found on 2026-08-31 still vulnerable to CVE-2026-82078/CVE-2026-81578 RCE that is exploited in the wild. Make sure to check for compromise & patch. Top affected: US (60).
Dashboard World Map view stats: https://t.co/ysTAPux1X6
Daily IP data now in our Vulnerable HTTP reporting, tagged 'cve-2026-82078' & 'cve-2026-81578': https://t.co/qxv0Gv5ELc
Tree map view: https://t.co/eo5poY2rb8
NVD entry:
https://t.co/DgUNWhvEKR
https://t.co/H5EdoUxVjH
Patch info: https://t.co/NeoJfMe0JD