Instead of watching Netflix tonight… 🍿
Spend just 1 hour with this. ⏳
Claude AI — a FULL course that teaches you how to build, automate, and get more done with AI. 🤖
The people who watch this tonight could wake up tomorrow with a brand-new skill.
Your future self will thank you. 🚀
🔔 Follow @Shubham10_26 for more AI, Cybersecurity & Tech content, projects & learning. 🤖🛡️💻
🐧 7 Linux Commands Every Cybersecurity Beginner Should Know 🔐
If you're starting your journey in cybersecurity, Linux is one of the first things worth learning.
Here are 7 commands to practice 👇
1️⃣ ls
→ List files and directories
2️⃣ cd
→ Navigate between directories
3️⃣ pwd
→ Show your current directory
4️⃣ cat
→ Read file contents
5️⃣ grep
→ Search for specific text
6️⃣ ps
→ View running processes
7️⃣ chmod
→ Change file permissions
💡 Why learn Linux?
Because Linux is everywhere in cybersecurity:
→ 🖥️ Servers
→ ☁️ Cloud infrastructure
→ 🛡️ Security tools
→ 🚨 SOC environments
→ 🔎 Digital forensics
→ 🐧 Penetration testing
Don't just memorize commands.
Open a Linux terminal and practice them. 💻
📌 Save this post if you're learning cybersecurity.
What's the first Linux command you learned? 👇
#Cybersecurity #Linux #InfoSec #EthicalHacking #Coding #CyberSecurityBeginners
🔔 Follow @Shubham10_26 for more AI, Cybersecurity & Tech content, projects & learning. 🤖🛡️💻
🐧 7 Linux Commands Every Cybersecurity Beginner Should Know 🔐
If you're starting cybersecurity, Linux should be one of the first things you learn.
Here are 7 commands to practice 👇
1️⃣ ls
→ List files and directories
2️⃣ cd
→ Navigate between directories
3️⃣ pwd
→ Show your current directory
4️⃣ cat
→ Read file contents
5️⃣ grep
→ Search for specific text
6️⃣ ps
→ View running processes
7️⃣ chmod
→ Change file permissions
💡 Why learn Linux?
Because Linux is everywhere in cybersecurity:
→ Servers
→ Cloud infrastructure
→ Security tools
→ SOC environments
→ Digital forensics
→ Penetration testing
Don't just memorize commands.
Open a Linux terminal and practice them. 💻
🔖 Save this if you're learning cybersecurity.
What's the FIRST Linux command you learned? 👇
Follow @itsdheerajvt for:
🔐 Cybersecurity • 🤖 AI
☁️ Cloud • 🐳 DevOps • 📚 Tech Resources
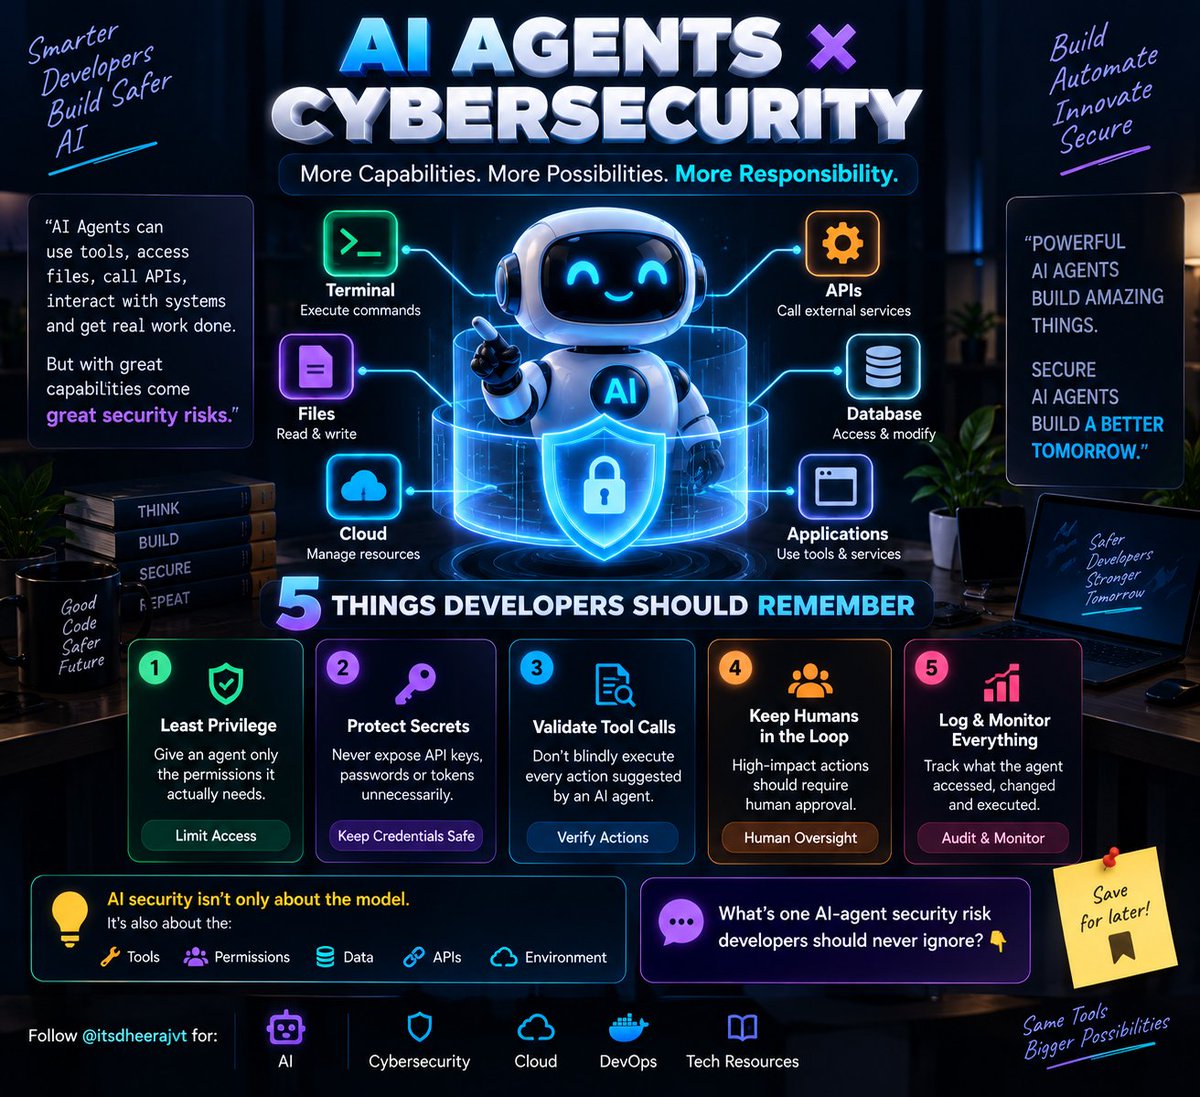
🤖 AI Agents are changing how developers build software.
But giving an AI agent access to tools, files, APIs or terminals also creates new security risks. 🔐
5 things developers should remember:
1️⃣ Least privilege
Give an agent only the permissions it actually needs.
2️⃣ Protect secrets
Never expose API keys, passwords or tokens unnecessarily.
3️⃣ Validate tool calls
Don't blindly execute every action suggested by an AI agent.
4️⃣ Keep humans in the loop
High-impact actions should require human approval.
5️⃣ Log & monitor everything
Track what the agent accessed, changed and executed.
💡 AI security isn't only about the model.
It's also about the:
→ Tools
→ Permissions
→ Data
→ APIs
→ Environment
Build AI systems that are useful AND secure. 🔐
What's one AI-agent security risk developers should never ignore? 👇
🔖 Save this for later.
Follow @itsdheerajvt for:
🤖 AI • 🔐 Cybersecurity • ☁️ Cloud
🐳 DevOps • 📚 Tech Resources
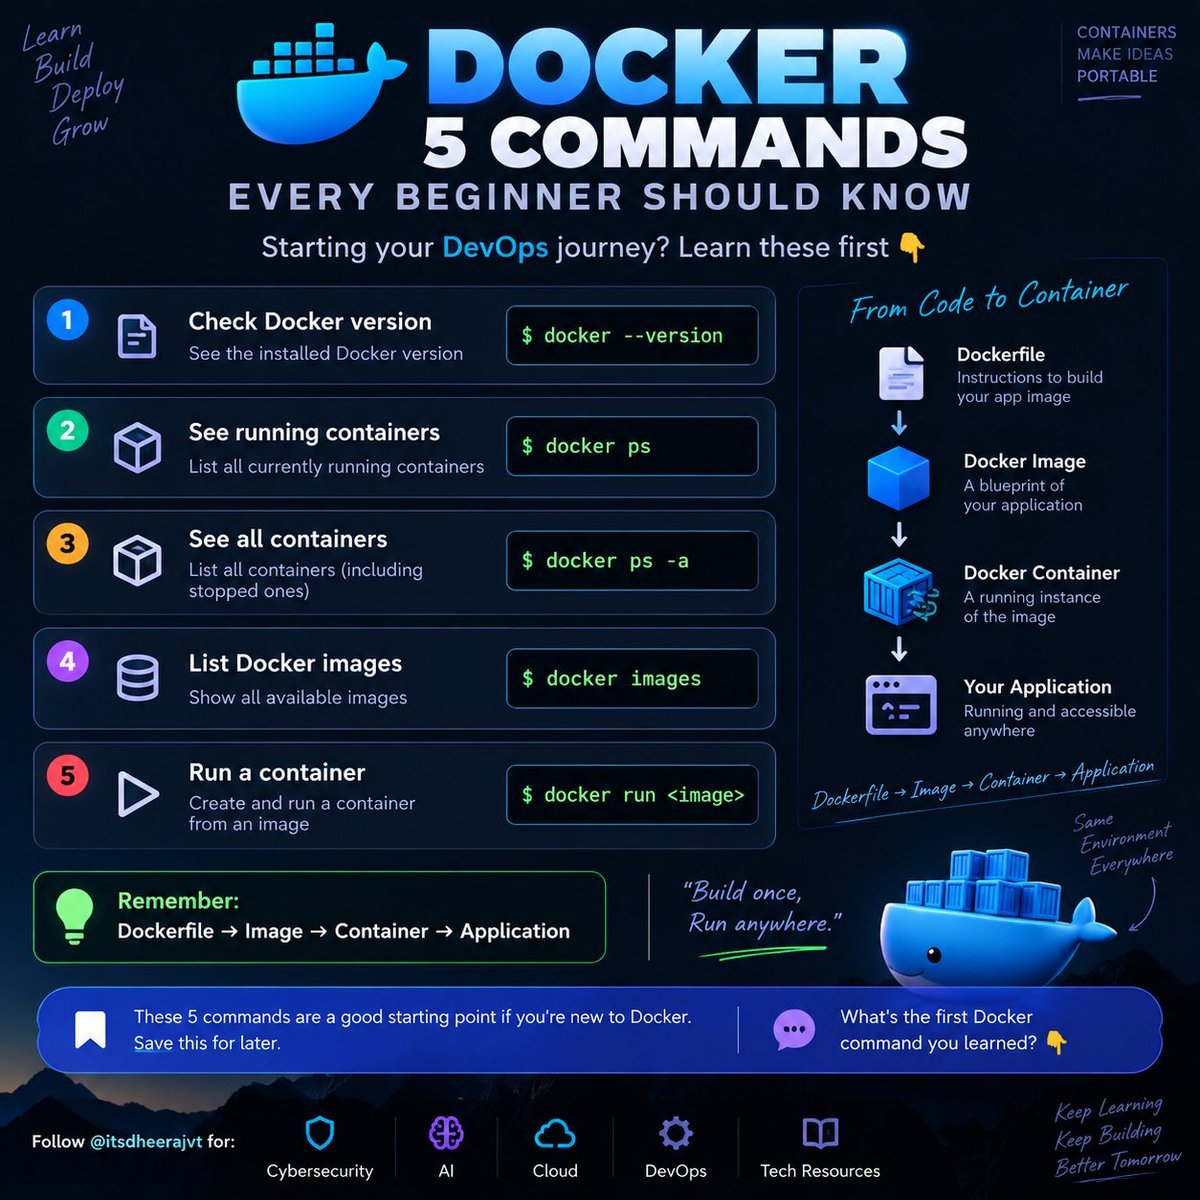
🐳 Docker: 5 Commands Every Beginner Should Know
Starting your DevOps journey? Learn these first 👇
1️⃣ Check Docker version
docker --version
2️⃣ See running containers
docker ps
3️⃣ See all containers
docker ps -a
4️⃣ List Docker images
docker images
5️⃣ Run a container
docker run <image>
💡 Remember:
Dockerfile → Image → Container → Application
These 5 commands are a good starting point if you're new to Docker.
🔖 Save this for later.
What's the first Docker command you learned? 👇
Follow @itsdheerajvt for: 🔐 Cybersecurity
🤖 AI
☁️ Cloud
🐳 DevOps
📚 Tech Resources
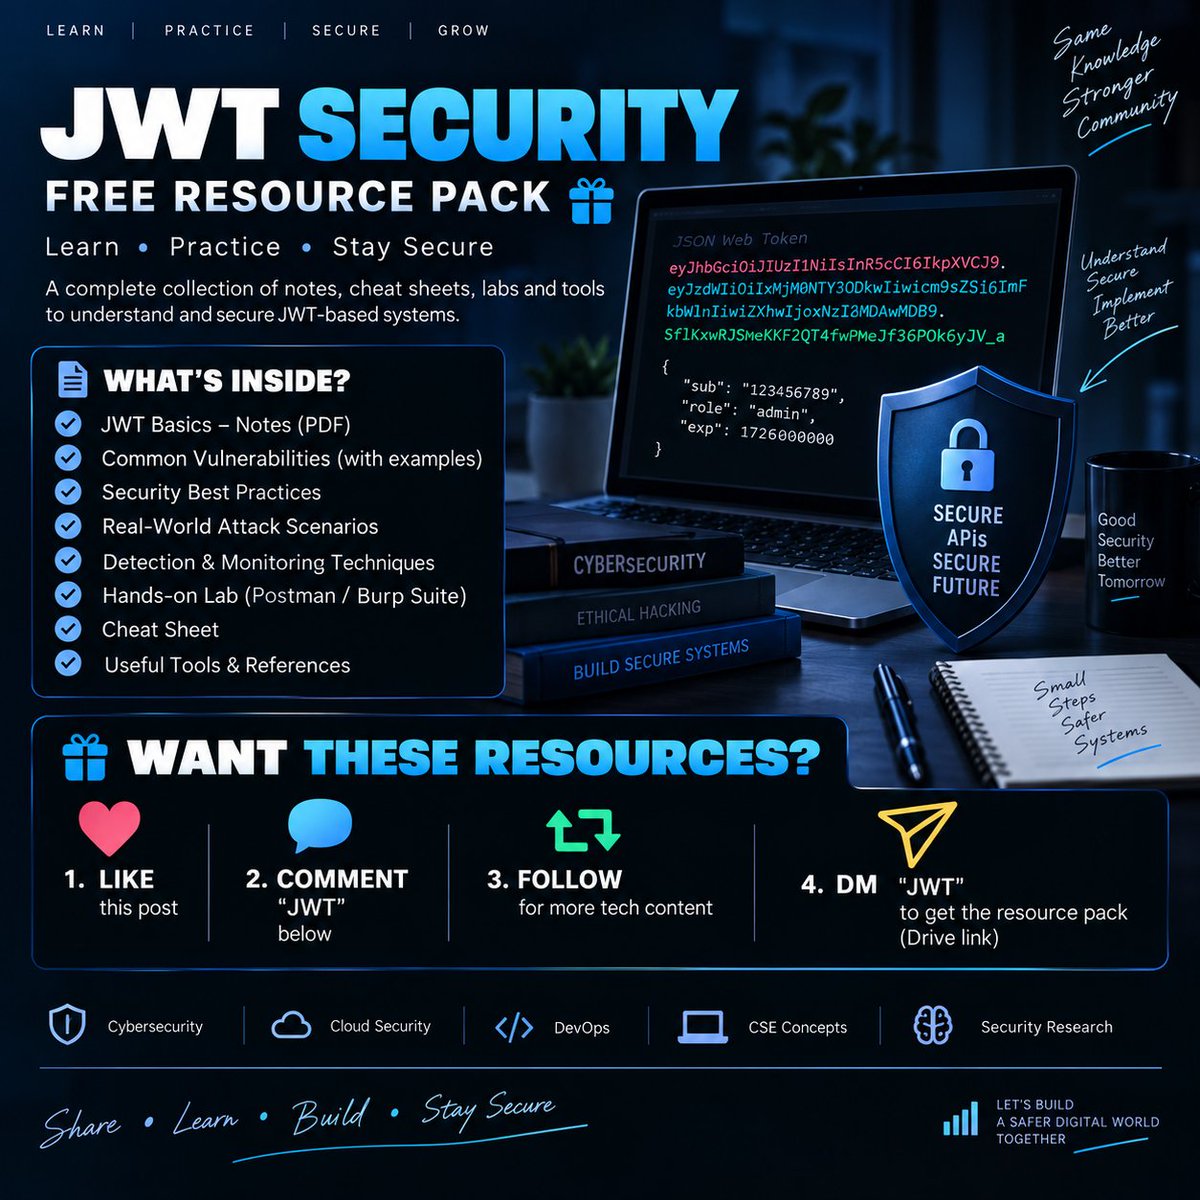
🧵 JWT Security: 7 Things Every Developer Should Know 🔐
JSON Web Tokens (JWTs) are widely used for authentication—but incorrectly implemented JWTs can create serious security risks.
Here are 7 things to remember 👇
1/7 🔑 Never store sensitive information inside a JWT.
JWT payloads are Base64URL-encoded, NOT encrypted.
Anyone who obtains the token can decode its payload.
2/7 ⏳ Keep access tokens short-lived.
A stolen token can potentially be used until it expires.
Use short expiration times and secure refresh-token mechanisms.
3/7 🔄 Protect refresh tokens.
Refresh tokens are high-value credentials.
Store them securely, rotate them when appropriate, and detect reuse.
4/7 🌐 Validate the token properly.
Your server should verify:
• Signature
• Expiration
• Issuer
• Audience
• Required claims
• Expected algorithm
Never blindly trust JWT claims.
5/7 🚨 Detect suspicious token usage.
Useful signals include:
• Sudden IP changes
• Device/browser changes
• Unusual geographic locations
• Multiple simultaneous sessions
• Abnormal request patterns
6/7 🧠 JWT ≠ Session Management
Using JWT does not automatically make authentication secure.
You still need:
HTTPS + secure storage + proper validation + expiration + revocation/reuse strategies.
7/7 🛡️ Security is not just about creating a token.
It's about controlling the entire token lifecycle:
ISSUE → STORE → USE → MONITOR → ROTATE → REVOKE
Follow for more:
🔐 Cybersecurity
☁️ Cloud Security
🐳 Docker & DevOps
💻 CSE Concepts
🧠 Security Notes
#CyberSecurity #InfoSec #AppSec #WebSecurity #JWT #DevSecOps #CloudSecurity