Good write-up by Unfold on detecting CVE-2026-41940, the #cPanel & WHM auth bypass analyzed by watchTowr
What I like about it: they don’t stop at detecting the PoC
They look at the exploit flow and focus on the parts that are harder to avoid:
- GET / with Basic auth in cPanel access logs
- redirect behavior exposing the cpsess token
- later authenticated session use without a matching successful login
Also nice to see someone use Sigma correlation rules properly here
Temporal ordering, grouping by source IP, negative condition, false positive notes
https://t.co/1BDdkHkDT6
Here‘s a good new write-up on #MongoBleed 🩸 detection by Tamir Zimerman (Unfold Security)
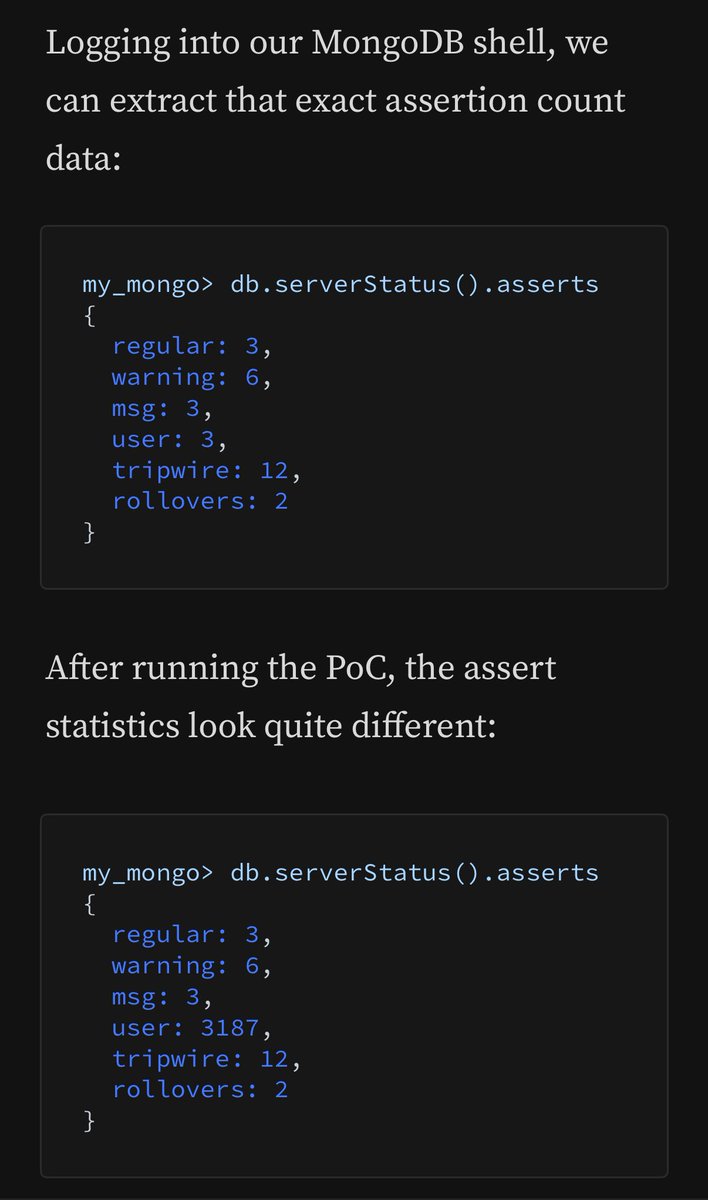
The missing metadata is a POC artifact. They discovered another way to identify exploited instances by looking at the AssertionCount values.
https://t.co/6PhAL6ZYXy
I’m gonna update my detector tool asap