‼️ BREAKING: Your LG TV is eavesdropping on you. It transcribes what you say, copies what is on your screen, and scans every device on your network, and researchers say the collection keeps running after you disconnect it, uploading the moment it reconnects.
LG's ad-tech arm says it out loud: "We own the glass." It pitches marketers on the ability to "own the living room," using data harvested from the TV you paid thousands for.
Gamers Nexus, working with Level1Techs and independent researchers, compromised an LG G5 and turned it into a listening device: it recorded room audio while the screen appeared off and the Ethernet cable was unplugged, then exfiltrated the file once the TV was back online.
LG has publicly said its TVs "do not collect, record, or store ambient conversations." Gamers Nexus found the TV converts speech to plain text and stores it in on-device logs, and that the mic window stays open 10 to 15 seconds after talking stops, sweeping up bystanders who never addressed the TV.
These sets are everywhere: hospitals, waiting rooms, boardrooms, hotels. ACR keeps running even when the TV is a dumb HDMI monitor, and a compromised set can pull the audio of a call off that HDMI feed. A surgeon asked Gamers Nexus where that leaves patient confidentiality.
Researchers advise disconnecting LG TVs from any network.
BSides San Diego is officially migrating to Bluesky to continue building our infosec community.
As we sunset this X account, join us on Bluesky for updates, discussions, and event announcements!
Follow us here: https://t.co/RNePojosd9
@SecurityBSides
We’re thrilled to announce @KelliTarala as the keynote speaker for #BSidesSD 2025
A pioneer in cybersecurity & compliance, Kelli brings unmatched insights to the infosec community. Don’t miss her keynote!
1st Annual BSides SD Event Art Competition is in full swing. Show us what you got by helping us create this year's event graphic!
This graphic will be used for this year's event sticker as well as our event t-shirt.
https://t.co/1rFyiOsR5G
@SecurityBSides
BSides San Diego 2025 Tickets Are Now On Sale!
Don’t miss your chance to join San Diego’s premier InfoSec community event! Last year, we sold out, so grab your ticket early and secure your spot.
@SecurityBSides
https://t.co/cHsY6IN5BJ
I strongly recommend turning this off.
It's unbelievable that they quietly enabled this while everyone was focused on their 'Recall' AI feature. Now they're collecting and using everyone's Microsoft Word and Excel data to train their AI models.
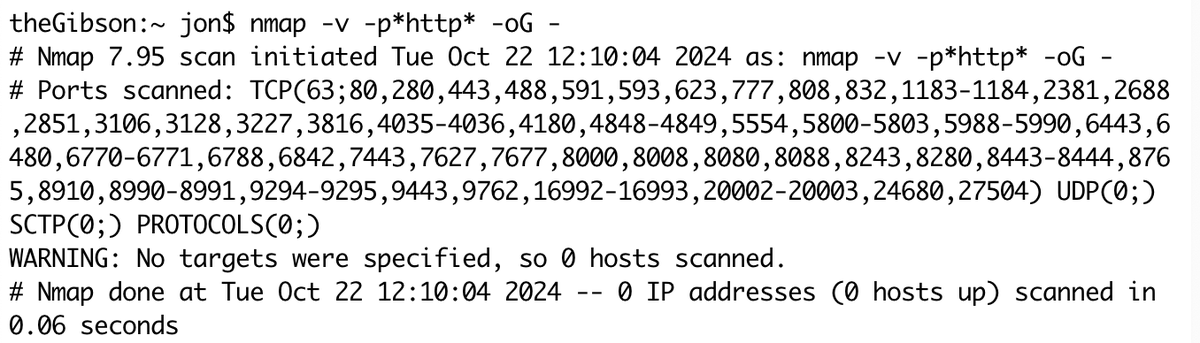
TIL: You can scan ports commonly associated with a protocol with @nmap like this, which scans common HTTP ports:
$ nmap -p*http* host
You can see the ports it will scan with the following:
$ nmap -v -p*http* -oG -
Do you have knowledge to share, stories to tell, or tips to drop? The #BSidesSanDiego CFP is OPEN! Whether you’re seasoned or just starting out, we want YOUR ideas!
Apply now to speak and make an impact: https://t.co/qd9QZ3ZLZ3
#CFP#Cybersecurity#BSidesSD@SecurityBSides
The White House's National Cyber Director Office recommended tech firms adopt memory-safe languages like Rust to boost software security. Come take "Blue Crab Shells: Getting Started with Offensive Rust Programming" with @mttaggart to stay ahead.
https://t.co/GEdjpZS8C3
#BSidesSanDiego Call for Papers (CFP) is open. Calling all infosec enthusiasts, experts, and thought leaders in San Diego and beyond – share your insights with our vibrant community.
@SecurityBSides
https://t.co/YVXn2WyoDh