Head of Security Operations and Yandex Cloud Detection and Response @ Yandex Cloud Protecting everything digital. Daily. Can find things. Twits are my own
@TheSAScon In case someone stuck with the one right after this one - we've updated the task a bit, feel free to redownload and reanalyse the jpg file ;)
Wanna prove you are the best threat hunter? #SASatHome Mini #CTF welcomes you!
First 3⃣ winners will get full access to Hunt APTs with #Yara like a GReAT Ninja by @craiu for free.
Solve the puzzles and join us at #SASatHome to know who won!
👇👇👇Ready! Steady! GO-GO-GO! 👇👇👇
The #SASatHome is coming... and there is a point in agenda that sounds intriguing "A moderately big announcement" by @2igosha and @_marklech_ Believe me ;)
Overview of big threat actors who has Linux implants for desktop and servers: https://t.co/7yNtwBv3QU
Should be interesting for organizations users who are running Linux
Tomorrow we will be showing importance of YARA, some tricks from real-life indecent analysis and how you can master it using our new training. Please come to discuss and maybe even win one ticket to the training:
https://t.co/uIYqYGEtWL
Starting today our training: "Hunt APTs with yara like a GReAT Ninja" is available online on-demand!
63 videos + 200 hours of virtual lab access (20+ APT hunting exercises)
Your trainer will be mr @craiu
More info: https://t.co/1P1xROgVXj
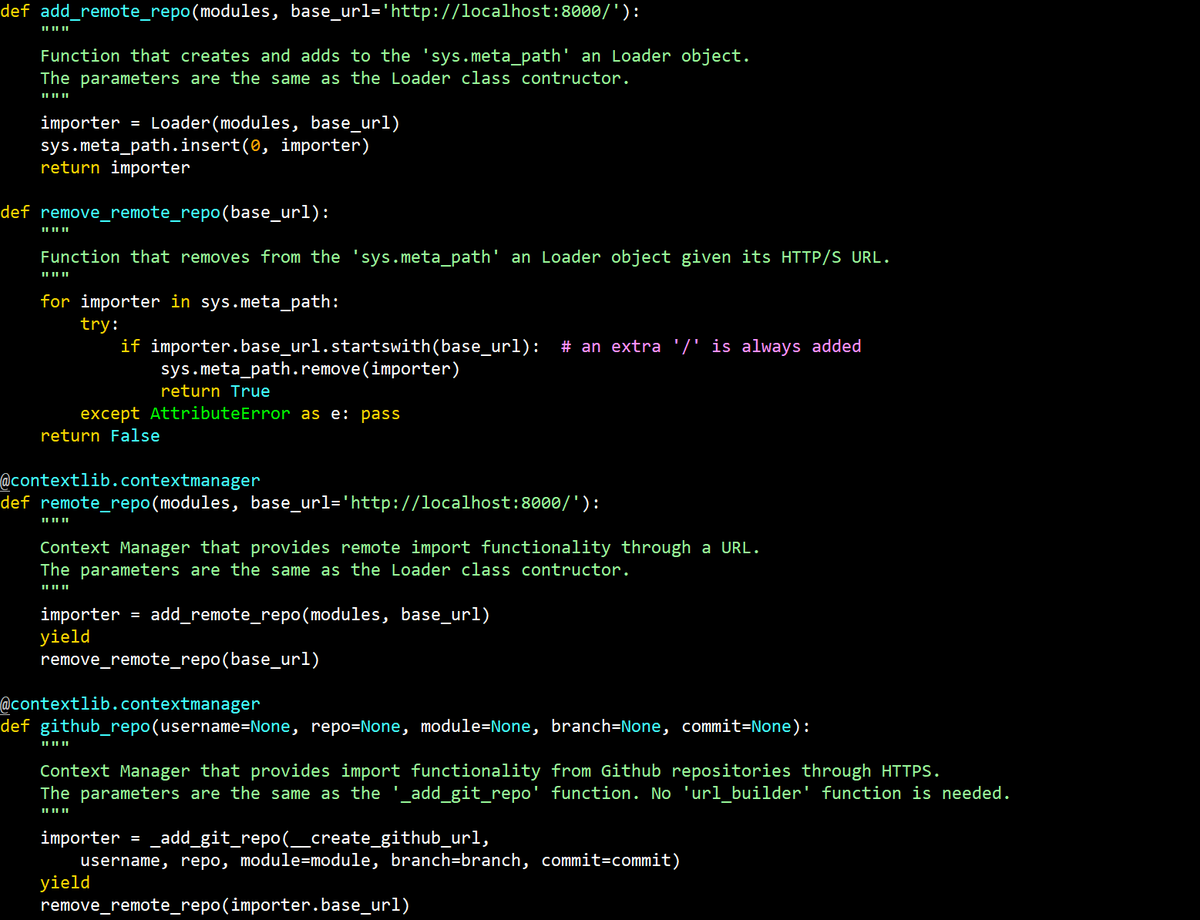
It steals emails, mines coins, remotely loads Python modules from Github, has a dashboard, supports Windows/Linux/MacOS, is open source, and is written in #Python 🦎
🌐https://t.co/RnsUhGeyGv
🔗https://t.co/kKlPAZcKbF
��https://t.co/X92h7zhlCt
Tomorrow we will held one more GReAT Ideas session. A lot of things starting from cyber mercenaries, traditional APTs and some OSINT tricks. Please come tomorrow: https://t.co/2I05grevIG
Our research on the new(?) mercenary APT DeathStalker is finally out! https://t.co/wJlDIJ1Twq
Please take a look if you're interested in Evilnum or Janicab!
(cc @securechicken)