So with all the negative talk about Microsoft security recently it occurred to me it's interesting to remember that MS also achieved one of the most consequential security successes of the last decade. A success that no one--including MS--ever talks about.
Hardening Office.
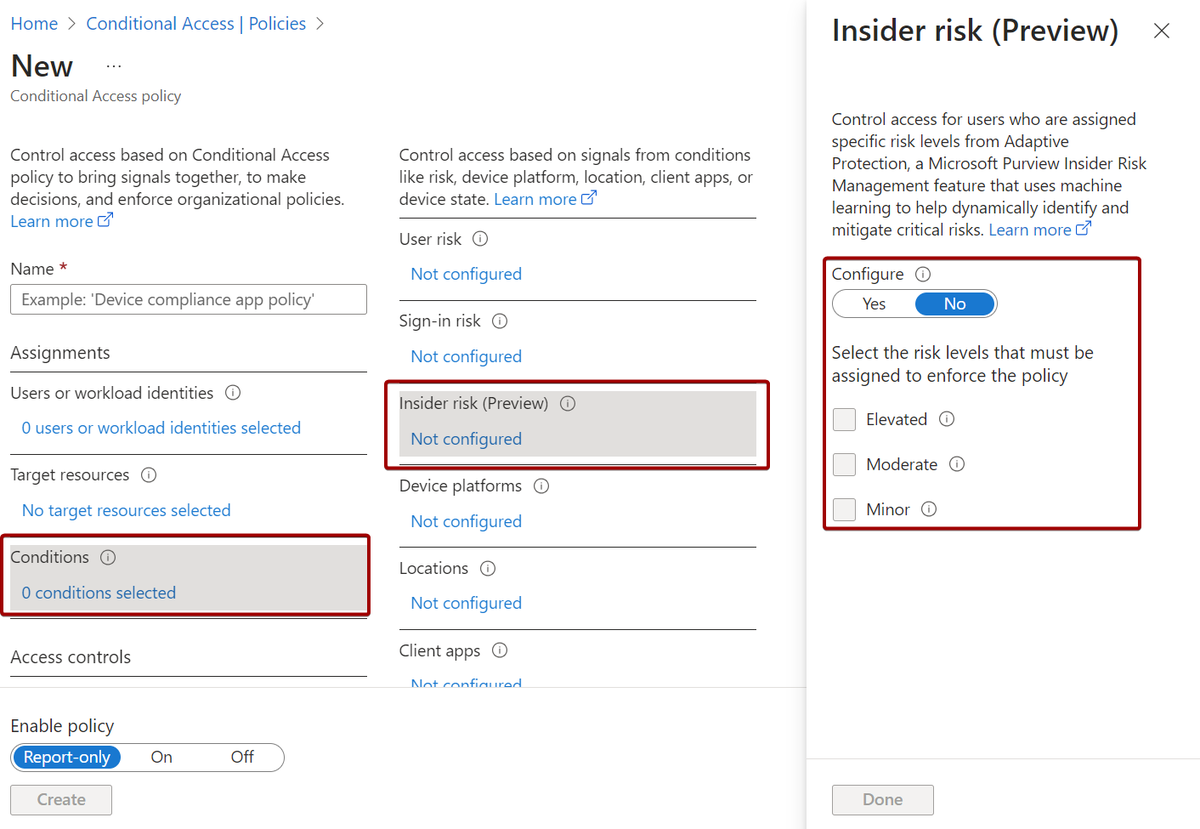
There is a new Condition for #EntraId Conditional Access in town
Microsoft has made available a new Condition for use in Conditional Access. The new Condition allows you to leverage Insider risk coming from Purview in your Conditional Access policies.
We could for example block access when someone has an "Elevated" risk level, or require an compliant device when the risk level is set to moderate.
Microsoft Purview Insider Risk Management is a compliance solution that detects, investigates, and acts on malicious and inadvertent activities within an organization. It correlates various signals to identify potential risks such as IP theft, data leakage, and security violations. Microsoft Purview Insider Risk Management is licensed through the Microsoft 365 E5 Compliance or Microsoft 365 E5 Security and Compliance plans.
Within Conditional Access we can leverage 3 risk levels or Insider risk:
Elevated
User performed activities that might indicate a high degree of risk. Typically requires an insider risk admin to take proactive measures to prevent further risky activity from occurring.
Moderate
User performed activities that might indicate a moderate degree of risk. While not as severe as an elevated risk, insider risk admins will still take appropriate actions to prevent further risky activity from occurring.
Minor
User performed activities that might indicate a minimal degree of risk. Typically, insider risk admins will continue to detect risky user activity to determine whether further action is required.
Need to find out who has highly privileged OAuth API access to your Microsoft 365 tenant?
I just published a new cmdlet that will generate a detailed report down to individual permission scopes.
All the details in this YouTube video
https://t.co/hKEwdKkCw7
Big news today: Automating user lifecycle management with Microsoft Entra ID just got WAY easier. With our new inbound provisioning API, it's straightforward to provision users from cloud or on-premises HR systems! https://t.co/9SjFkSqjZk
NEW T-Series are now on TOUR. 👀
The next generation of the most played irons on the PGA TOUR will make their debut at this week's @MemorialGolf.👌
Stay tuned as the world's best kickstart the validation process of NEW T100, T150, T200 and T350 irons.
#TSeries
"I'm living a dream. I'm making sure that I enjoy this moment. I've learned that after my 46 years of life, it's not going to get better than this. There's no way."
Michael Block is cherishing every moment of a storybook PGA Championship.
I'm looking for MDI customers who would like to talk with my engineering team and the detection developers and walk them though their MDI experience. Any volunteers? Good opportunity to meet the engineering team and not just me!
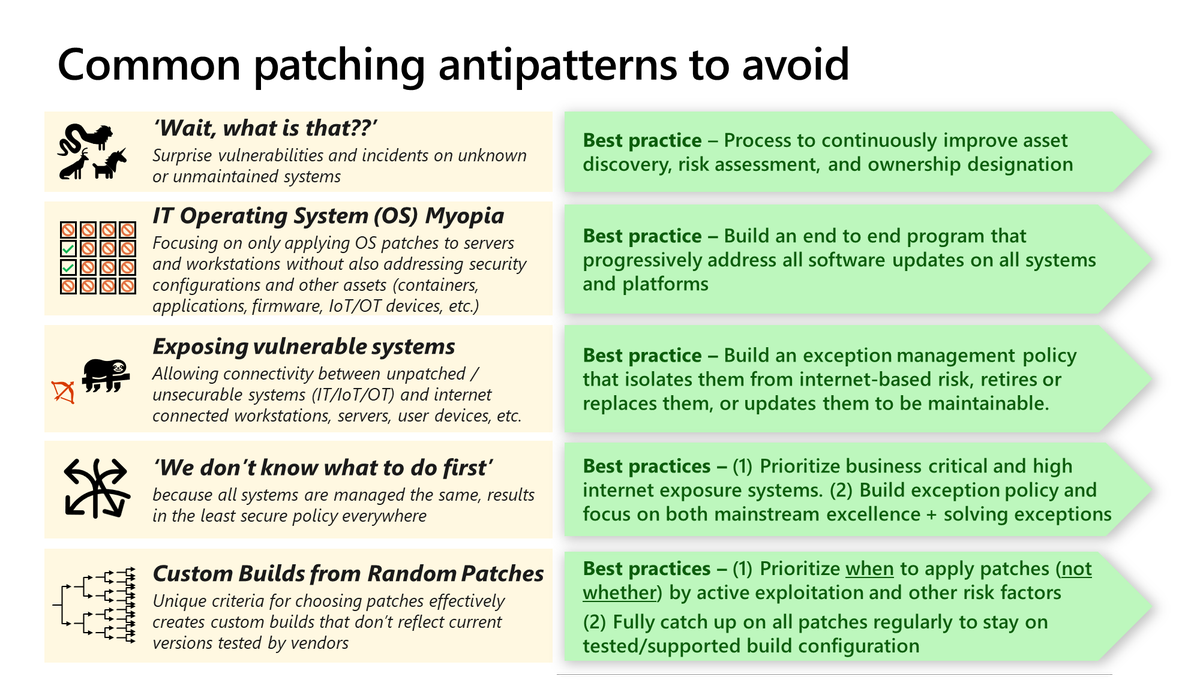
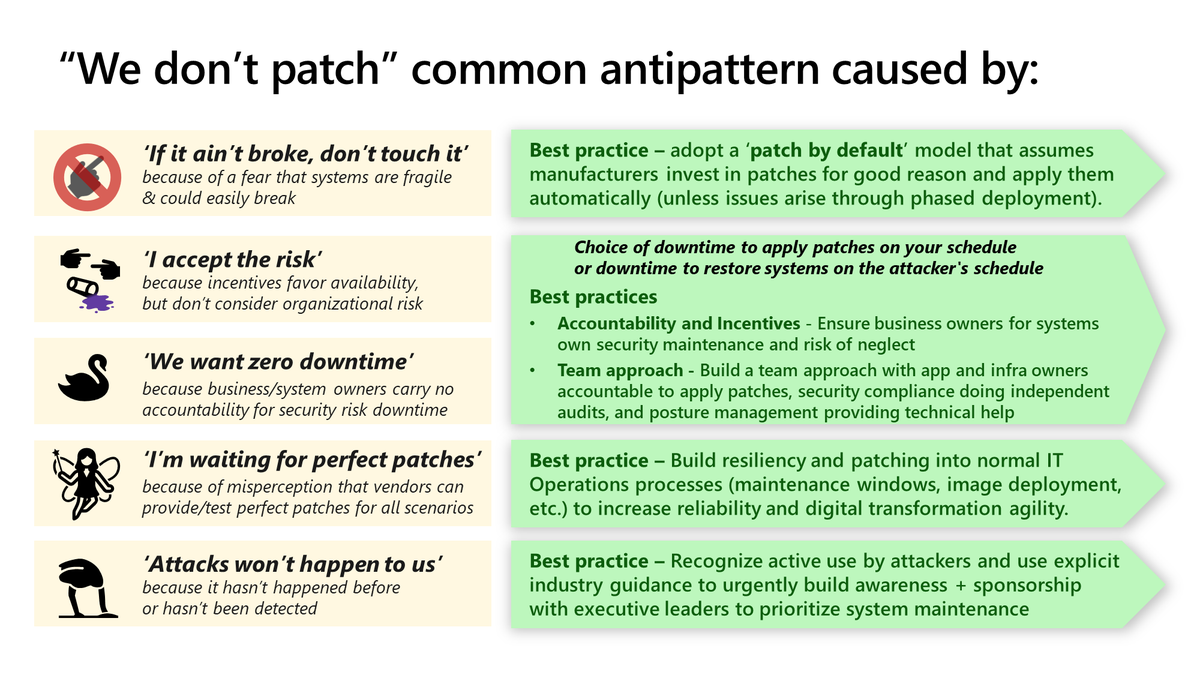
What are your top security Antipatterns? (opposite of best practice)
(https://t.co/fuHxuOgpFg)
I have these so far
- 10 patching antipatterns
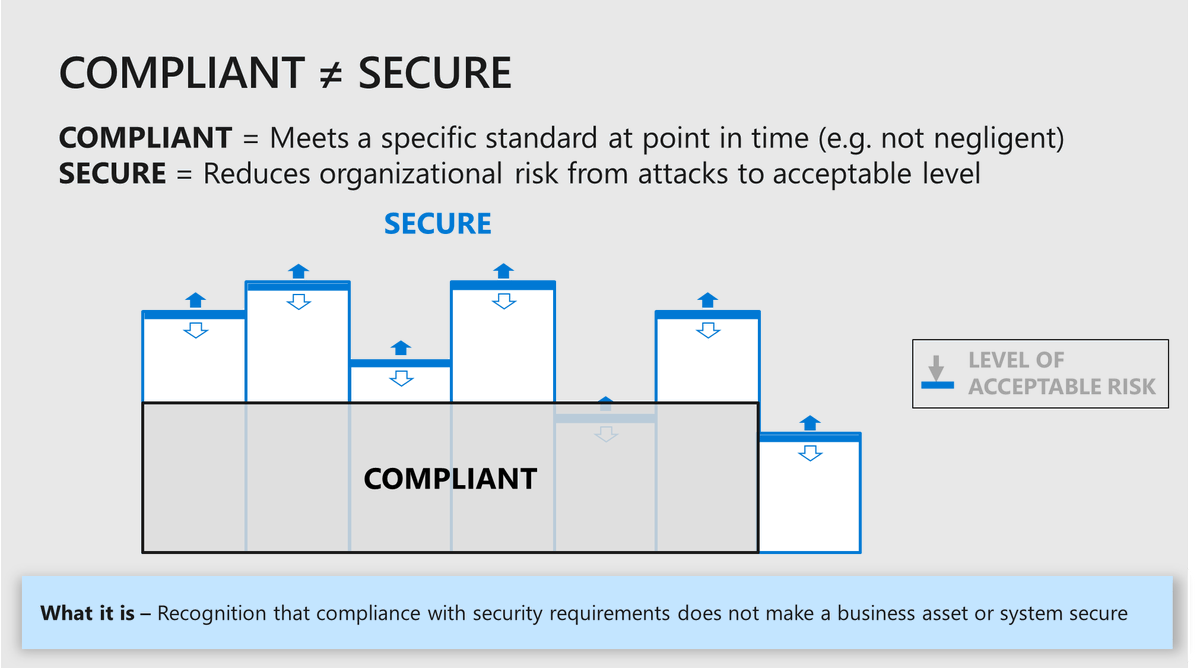
- "compliant is not secure" @scritches
- "Collection is not detection" for log data
- re-using the same password
what else?
What are your top security Antipatterns? (opposite of best practice)
(https://t.co/fuHxuOgpFg)
I have these so far
- 10 patching antipatterns
- "compliant is not secure" @scritches
- "Collection is not detection" for log data
- re-using the same password
what else?
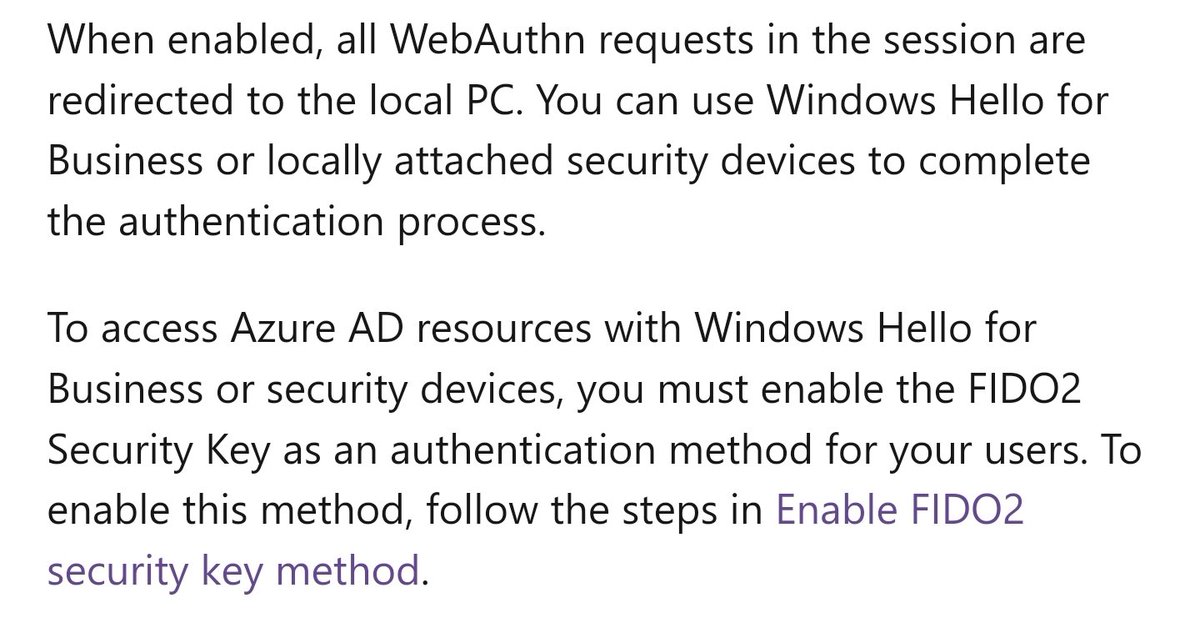
This is BIG news for FIDO2 and RDP!!!
✅️ Enable a SSO experience to Azure AD-joined and Hybrid Azure AD-joined session hosts
✅️ Use passwordless to sign in to the host using Azure AD
✅️ Use passwordless inside the session
https://t.co/QvnCSzPLCU
1/3
I have been informed by my supervisors that it is National Dog Day. On this day, their number one piece of advice is - enable MFA for 100% of your users 100% of the time. In addition, they encrourage you to be on a path to passwordless.
This makes me very sad. Thank you @jsnover for all of your kindness, wit and of course PowerShell. You will be missed big time. Wishing you all the best in your future endeavors.
After 22+ awesome years at Microsoft (18+ of which were awesome in a good way 😂 ), it is time for me to try something new.
I feel blessed to have had the opportunity to work with such incredible people and to work on things that matter.
My last day will be Friday, July 1st.