Exploit for CVE-2021-25741 in #Kubernetes. You can mount Node filesystem inside of a new POD with read-write privileges. #cve#exploit#k8s https://t.co/oTFDBHZevv
I got tired of manually switching monitor inputs between my work laptop and home PC, so I built a simple system with DDC/CI, few scripts, and a $5 keypad. Works smooth.
#DIY#TechTips#Productivity#WorkFromHome#HomeOffice#LifeHacks
https://t.co/iBuvC5bICe
A simple (and powerful) trick for tracking file changes in a mobile app’s data directory during a security review using Git to snapshot, compare, and clearly see what’s happening on both Android and iOS
#MobileSecurity#AppSec#Pentest#BugBounty
https://t.co/24aKQxJAKb
We're revealing details of an obscure debugging feature in the Apple A12-A16 SoC’s that bypasses all of the hard-to-hack hardware-based memory protections on new iPhones. Its not used by the firmware and we don't know how the attackers found out about it. https://t.co/hsQo6JIPMJ
APT groups in Asia attack the greatest number of countries and industries. Learn about this and more in our latest report, where we share the most valuable intelligence we've gathered on Asian APT groups ⇒ https://t.co/WBACxyytbG
#Cybersecurity#Threatintelligence#APTgroups
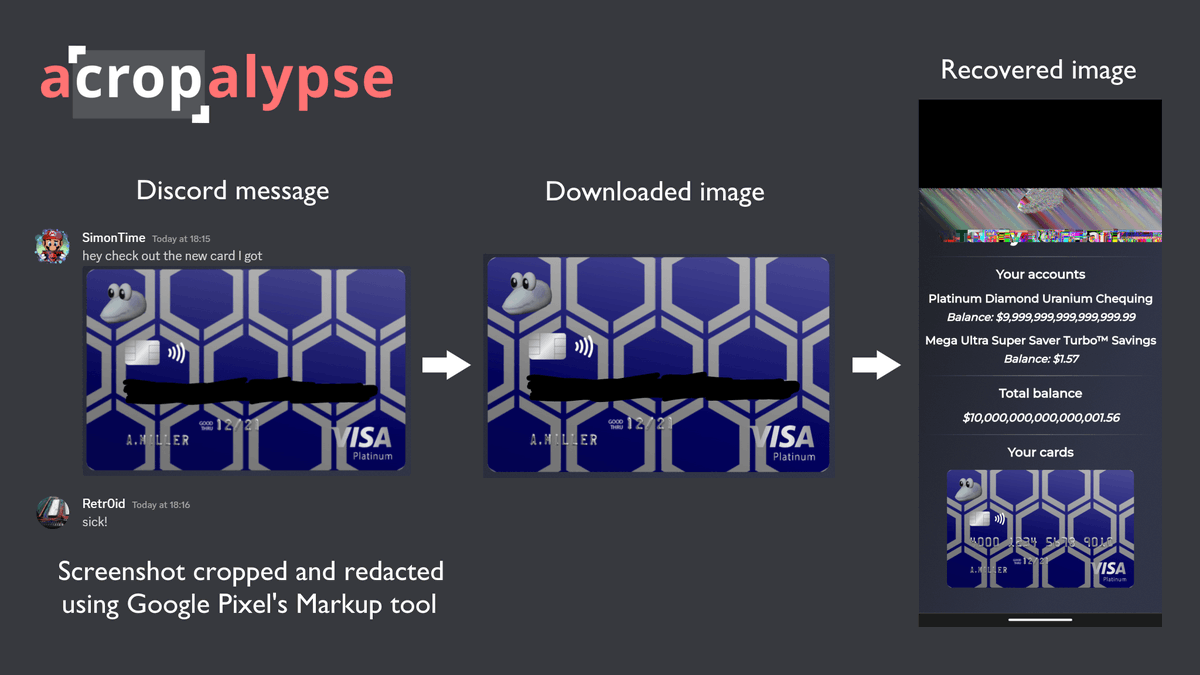
Introducing acropalypse: a serious privacy vulnerability in the Google Pixel's inbuilt screenshot editing tool, Markup, enabling partial recovery of the original, unedited image data of a cropped and/or redacted screenshot. Huge thanks to @David3141593 for his help throughout!
Certipy just received a major upgrade. The new version includes BloodHound integration, 5 new domain privilege escalation techniques, Shadow Credentials, Golden Certificates, and more.
https://t.co/J9Wr7dzQMR
💥 New article "Fuzzing for XSS via nested parsers condition" by our researcher @Psych0tr1a.
This techniques allowed us to find a bunch of vulnerabilities in popular web products that no one had noticed before!
https://t.co/7SpknkeMsO
Big news today! 🚨 We're releasing a first-of-its-kind transpiler to make it radically easier to use 🔐 fully homomorphic encryption🔐!
Put regular C++ code in, get FHE-ready C++ code out. Magic ✨
Check our our code! Or keep reading for more info 😀
https://t.co/bqt1CutsAc
It's been long overdue, but my part 2 blog on Active Directory forest trusts is finally here! This blog is about trust transitivity and on the finding on CVE-2020-0665 which was a trust bypass by faking a domain. Enjoy the (long) read: https://t.co/4CACl2pbpY
Registration for CTFZone 2021 is opened! We have a brand new hybrid format this year: A/D + Jeopardy + Game task!
Please note that registration will be closed at 10:00 (UTC) on June 23!
https://t.co/sI3Wp1ohSj
I'm super excited to release Kubernetes Goat with updated scenarios. Designed to be an intentionally vulnerable cluster environment to learn & practice #Kubernetes#Security
⭐GitHub:https://t.co/7omjqBTYLr
📑 Guide:https://t.co/xXoWfWIaah
#Pentesting#InfoSec#K8S#CloudNative
We had such a fun time last year 🥴🥳 we decided to do it again! #cfp for the #paymentvillage is live https://t.co/jsWQHO2bJF You have until the 15th of July to apply. All talks will be made available online as part of @defcon@cfp_time#defcon29
A small appendix for my PhDays talk: a way to turn HTTP Request Smuggling into controlling the backend response using a HEAD request.
This method has many prerequisites but may allow easier cache poisoning and even SSRF in some rare cases (e.g. H2O + X-Reproxy-URL enabled).
Slides from my talk "HTTP Request Smuggling via higher HTTP versions" at #phdays10!
Several previously undisclosed flaws in real open-source software are discussed near the end.
https://t.co/U45wXegefo