The official Twitter account for the worlds NFT Day project created by @ccrock1533 @adanielhill AND @mrrusselldavis -bringing together all the #nftcommunities -
The NFT Community Day is starting to get visibility after months of working. Follow @TheNFTDAY for updates. Many people behind this amazing project, among them @ccrock1533@MrRussellDavis and @ADanielHill
Click below to join our TWITTER COMMUNITY!
https://t.co/JjLnYACZtj
🇺🇸 UAlberta . ca Deep Dive: Institutional Technical Debt, Peer Apathy & The Cybermidnight Lens.
https://t.co/ZHrZEKUJfY
https://t.co/o841SZuoHY
https://t.co/JQVtqVq8MQ
🇫🇷 Cas uAlberta . ca : Dette Technique Institutionnelle, Apathie des Pairs et l'Axe Cybermidnight.
https://t.co/ZHrZEKUJfY
https://t.co/o841SZuoHY
https://t.co/n9TQaM7J44
One is enough to learn, and fix, I feel guilty I thought there were not going to be more Alberto's in Uruguay, but the new Alberto is 19 years old and he was arrested on May 26th... I do not know why I feel so fucking guilty, frustrated, and...
Nine hundred and thirty pages. That is the depth of the vulnerability report behind the recent UAlberta leak, a stark case study on the architecture of institutional apathy.
While automated machines identified over 4,500 vulnerabilities in just twenty hours, the institution took three years to respond, buried under the weight of silent technical debt.
We are often told these crises stem from sophisticated nation-state actors. The reality, however, is simpler: automated scanners exploiting years-old vulnerabilities, facilitated by routine institutional negligence.
LISTEN TO THE WHOLE VIDEO, DISTRIBUTE IN #ALBERTA @UAlberta ETC.
CCC: @IEEEorg@WIRED@CCC@Linuzifer@JackRhysider@WatchmanPrivacy@VECERTRadar@GGILD1983@troyhunt
🎬 Video> What happens when multi-year technical debt meets institutional opacity in public infrastructure?**
Our latest documentary-style video explainer, **"Cybermidnight: Inside the Hacker Underground,"** delivers a calm, data-driven autopsy of the multi-year forensic cybersecurity research affecting public networks across Alberta—from higher education to healthcare and provincial systems.
#### **Key Takeaways Covered in the Video:**
* **The 4,561 Findings:** Inside the 930-page BeeHive Systems vulnerability assessment of `https://t.co/vLcRUH0ZUP` (unauthenticated ColdFusion reads, Pentaho bypasses, and unpatched web endpoints).
* **Cloud & Identity Exposure:** Azure AD guest account abuse, pending invitations, and endpoint infostealer logs cataloged via THOR APT scanner output.
* **Supply Chain Ripples:** How third-party incidents—like the global May 2026 Canvas LMS compromise—expose institutional reliance on external software.
* **Data Over Drama:** How independent researchers, including Treaty 8 analysts and Alberto Daniel Hill, utilize TLP-aware disclosures and PGP cryptography to preserve digital truth without sensationalism.
---
* **Primary Target Handles:** `@UAlberta` | `@UAlbertaNews` | `@YourAlberta`
* **Research & Platform Handles:** `@ADanielHill` | `@cybermidnight`
* **OSINT & Intel Community:** `@DataBreaches` | `@VECERT_Analyzer` | `@CanvasLMS`
@UCPGoA23@medsci_yb3r@userlolxxl@skocherhan@KulinskiArkadi@CreesOnCBC@MondoABx@Furnace_roofho@UAlberta@jodi_stonehouse@nenshi@IEEEorg@ccc@Linuzifer@JackRhysider
---
### **#️⃣ High-Impact Hashtags**
**Institutional & Regional (Target Audience Discovery):** `#UAlberta` `#UniversityOfAlberta` `#YEG` `#Edmonton` `#Alberta` `#CanadaCyber` `#HigherEdIT`
**Technical & Security Focus:** `#Cybersecurity` `#OSINT` `#ThreatIntel` `#DataBreach` `#TechnicalDebt` `#InfoSec` `#CyberCrime` `#PatchManagement`
**Campaign & Brand Identity:** `#Cybermidnight` `#CybermidnightClub` `#DataOverDrama` `#RadicalTransparency` `#HackingIsNotACrime`
🔒 "Scammers aren’t hacking systems—they’re hacking trust."
For Cybersecurity Awareness Month, Delaila breaks down how threat actors exploit common weak spots across social platforms:
🎣 The Bait: Fake NFT collaborations, sponsored project DMs, and "instant payout" promises.
⚠️ The Hook: Malicious links designed to harvest credentials or drain Web3 wallets.
🛡️ The Rule: Know what you’re clicking, verify who you associate with, and never take unverified DMs at face value.
If something feels off, verify before you click. Reach out to Delaila directly or connect with @ADanielHill for forensic guidance. Thanks @NFTPrincess21 !
#CybersecurityAwarenessMonth #SocialEngineering
🇪🇸 🏛️ EXPEDIENTE EUROPEO ACTIVADO: ROMA REGISTRA DENUNCIA ARTÍCULO 144 🏛️
La vulnerabilidad de estado señalada en el informe del 16 de septiembre ("Sin confirmación de expediente público") queda oficialmente resuelta.
El Garante per la protezione dei dati personali en Roma ha registrado formalmente la denuncia bajo el Protocolo N° GPDP.0142186/26 (Fecha: 07/10/2026 08:46:35 CEST).
Aspectos clave:
1️⃣ Entrega directa vía PEC Italiana: Evadió los bloqueos telemáticos del Estado uruguayo (SMTP 550 y Connection Refused).
2️⃣ Supervisión Transnacional: El aparato regulador europeo inicia la revisión formal sobre el incumplimiento sistemático de Hábeas Data y escuchas ilegales ("El Guardián") bajo el Art. 144 del GDPR.
3️⃣ Riesgo de Adecuación: Cuestiona la Decisión de Adecuación de Uruguay ante la Unión Europea (2012/484/EU).
El dictamen de auditoría forense certificado en PDF ya está disponible para descarga y archivo. 📄🔍
*INCONGNITO MODE, EN @EKOPARTY **
https://t.co/qUaPW8kYDK
#DataOverDrama #GDPR #GarantePrivacy #HabeasData #ElGuardián #Ciberseguridad #InfoSec #Uruguay #Doctrina999 @WIRED@TeamNAIT@DigitalArmyio@grazianopascale@SeUruguay@GGILD1983@CERTUY@AGESIC@compresidencia@OrsiYamandu@INTERPOL_HQ@ANTEL #BHU @LuisLacallePou #URCDP @CCC@Linuzifer
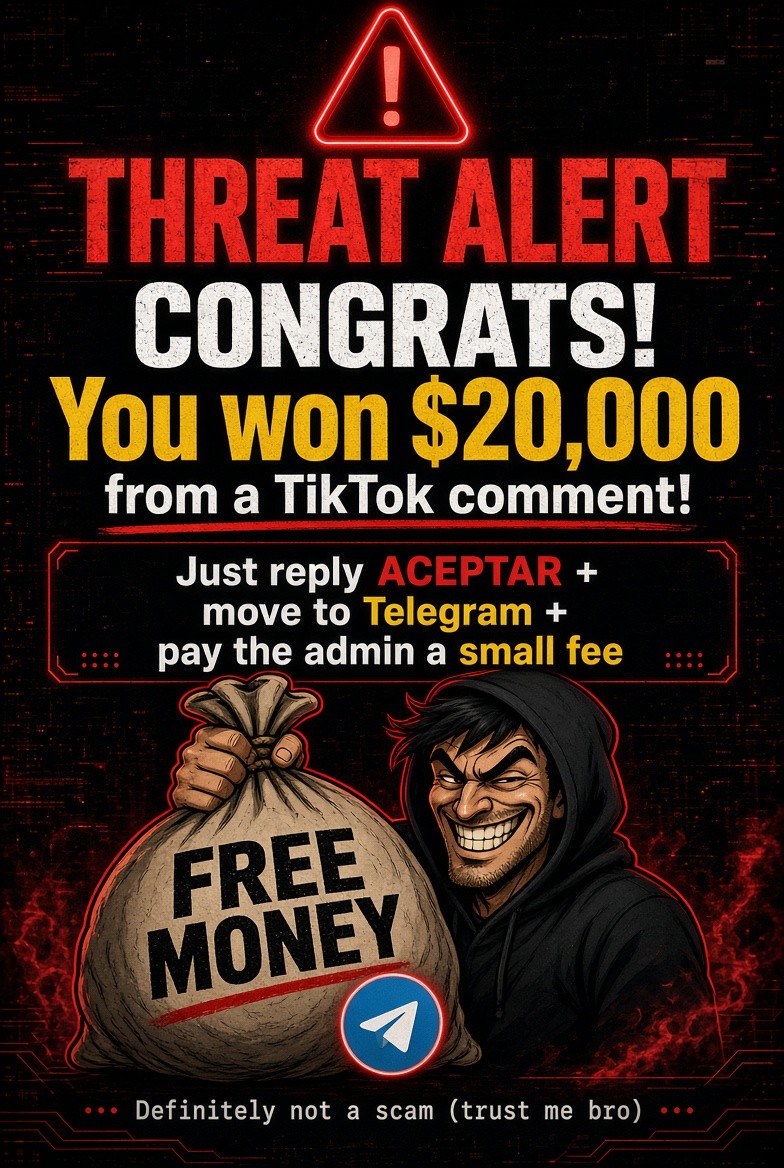
🚨 THREAT ALERT 🚨
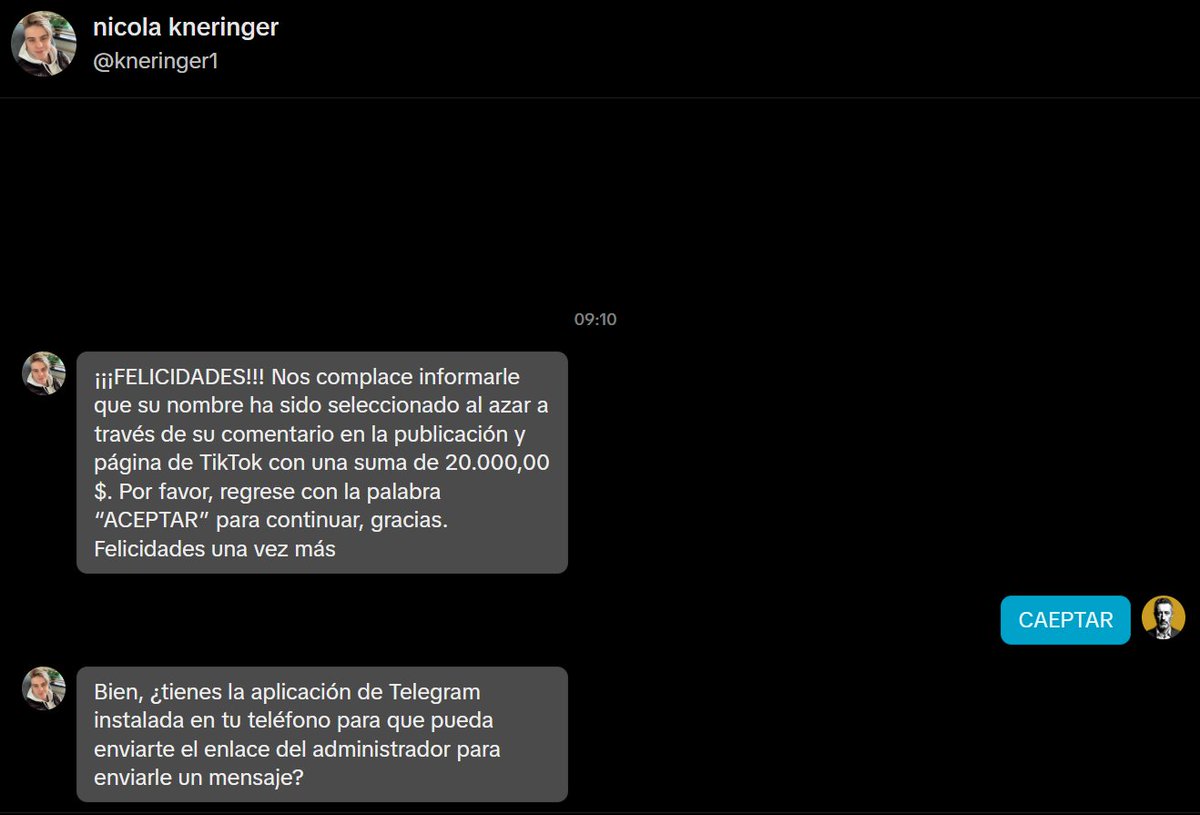
Congrats! You’ve been randomly selected via a @TikTok comment to win a life-changing $20,000
Just reply “ACEPTAR”, move to Telegram, and send the “admin” a tiny little verification fee.
Totally real.
Definitely not a copy-paste scam sent to 40,000 other people at the same time.
The guy in the photos is definitely the one running the operation and not a stolen profile.
Free money never comes with a Telegram link.
But sure… go ahead and reply “ACEPTAR” if you enjoy funding Nigerian princes and Eastern European call centers.
Wait but I misspelled "ACEPTAR...." UMMM
#ScamAlert #TikTokScam #FreeMoneyIsNeverFree #ACEPTARAtYourOwnRisk
When Scanners Don't Sleep: The
University of Alberta Vulnerability
Report and the CyberMidnight Club
Awareness Mission
A Public Interest Article on Institutional Cybersecurity, Responsible Disclosure, and Cross
Border Digital Transparency
General and cybersecurity-aware audiences
| 2026-10-06
Introduction
In October 2023, an automated cybersecurity scanner swept across the digital
infrastructure of the University of Alberta — one of Canada's largest public research
universities. What it found was a 930-page report cataloguing thousands of potential
vulnerabilities. Three years later, that report has resurfaced in public discussions across
Alberta and beyond. This article explains what happened, why it still matters, and how an
independent cybersecurity awareness initiative called CyberMidnight Club is helping bring
these systemic issues to light — responsibly, transparently, and without sensationalism.
DISCLAIMER This article is based on independent OSINT (Open Source Intelligence) analysis and
publicly available information only. It is produced for public awareness, education, and advocacy of
better vulnerability-disclosure practices and digital rights. No affiliation exists with any government
agency, law enforcement body, university, dark-web actor, marketplace, or ransomware group in
Canada, Uruguay, or elsewhere. The 2023 BeeHive scan report and any third-party datasets
referenced here do not constitute proof of current compromise, active exploitation, or confirmed data
breach. Readers with personal data concerns are directed to official channels: [email protected] or
[email protected].
https://t.co/yyfzmH3l73