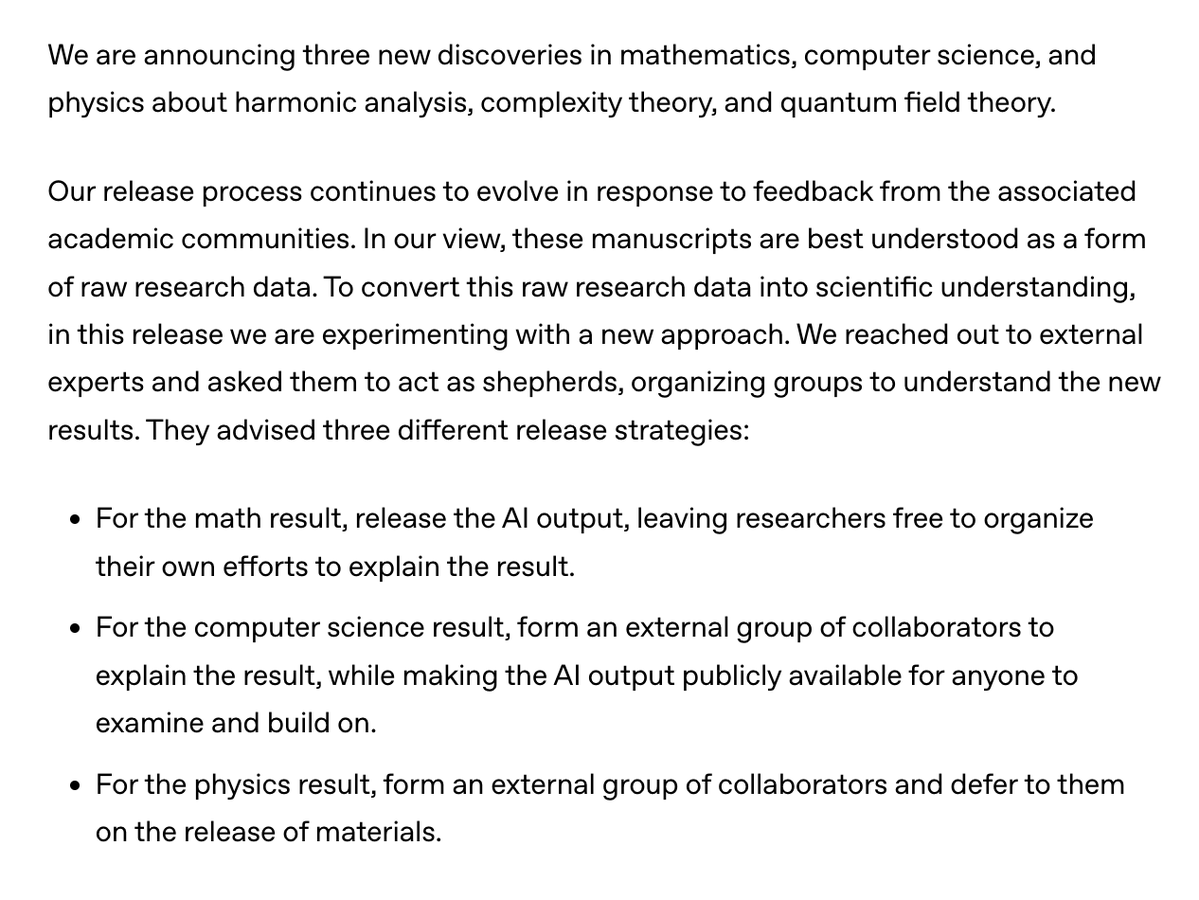
We are announcing three new discoveries in mathematics, computer science, and physics about harmonic analysis, complexity theory, and quantum field theory.
https://t.co/9BX8HWQDTJ
What do people use ChatGPT for at work and how does that differ around the world?
Our new OpenAI Signals data lets researchers compare activities from writing and coding to teaching and business analysis across nearly 100 countries.
Download the data and tell us what you find: https://t.co/wv8OidSQn3
Day 22/ Terra is back!
Our first model that is significantly better at writing, personality and nuanced understanding of requests.
Packs a punch across the board, very good at computer use, and gives 2X more usage than 6.1 Sol across API and subscriptions.
GPT-6.1 Terra: delivering fast and capable computer use at a lower price.
GPT-6.1 Terra understands what’s on screen, takes action across apps, writes naturally, and is a more capable model for your whole workday with the efficiency to take on more of it.
We noticed some concerning behaviour in a popular open source model.
It’s either an incidental relic from training or an intentional ‘call home’ mechanism. Either way it’s surprising and highlights the significance of how you choose which models to use.
We ship very quick at OpenAI.
Now we have ChatGPT, Codex and API release notes in one place!
You can search, filter by product or subscribe via RSS.
https://t.co/z32aRJsO1O
Since I'm now blocked by bluey from replying to this thread, I answer here by quote tweet
the openAI construction has more to do with convex integration than anything else.
In convex integration, the oscillations are typically built by hand and the iteration procedure creates wild weak solutions. The non-uniqueness construction of Albritton–Brué–Colombo used an unstable vortex to split solutions apart. The Córdoba–Martínez-Zoroa singularities amplify vorticity across scales by strain. In the openAI paper, a fluid instability is clever made so that the flow itself generates the oscillations: they grow by drawing energy from the background shear. The Reynolds stress then becomes the force that creates the collapsing smooth vortex. Using a physical instability to create the stress in this way has no precedent, and it is what produces a smooth force rather than a merely rough one.
Some on these ideas are in the literature (e.g. Leibovich-Stewartson 1983) but the way they are combined is definitely insane and definitely nowhere in the literature previously.
I also don't know of anyone suggesting that convex integration would play a role in the creation of a blow-up solution like this.
On a technical level, the paper is unbelievable, maybe beyond what a human could have come up with but not beyond human understanding: there are several different groups of pde experts working on understanding it who say that they more or less understand now. I expect digestions soon
td;lr: anyone saying that this OAI result is unsurprising is bullshitting
sorry!
Over the past several months, we have substantially hardened the security of our research training environment. We’ve removed live internet access for all frontier models during training and built an offline world for them to use instead—a cached version of the web where they can still learn to browse, search, and use applications.
On September 20, after a model exploited a DNS misconfiguration to find a way outside of this offline world, we paused frontier training to strengthen containment further. We assembled teams of agents, powered by our most cyber-capable models, and tasked them with finding weaknesses in our research environments.
While they found no route to the internet they could easily exploit while concealing their activity from our monitors, they did find zero-day vulnerabilities, virtual machine escapes, and hardware side-channels for communication between agents. We used their discoveries to further strengthen our defenses and contribute fixes to open-source software.
After strengthening our containment architecture, we resumed our frontier RL training and inference on October 1. We’ve reserved substantial compute for continuous red-teaming, and made high-compute red-teaming part of the safety cases we use to decide whether frontier training and evaluation can proceed securely.
https://t.co/EmEZsFRMcF
During this red-teaming exercise, we also found a vulnerability that allows for unauthenticated remote code execution in Brotli, a widely-deployed compression library included in many pieces of software such as Node.js, Bun, and Envoy.
The flaw could let an attacker run their own code on affected systems by sending or replying with malicious compressed data, without any need to create a user account. That is, an unpatched server that accepts compressed input could be taken over by a malicious client, and an unpatched client that accepts compressed input (such as “curl --compressed”) could be taken over by a malicious server.
This root cause issue was actually fixed in the Brotli source code in February, but it wasn’t known at the time that it gave rise to a security vulnerability and there was no more recent release of Brotli. Since Brotli is built into other software, any software which includes this library needs to take the update too, followed by the users of that software. We disclosed the vulnerability to Brotli and other downstream projects such as Node.js, which released or are currently releasing security updates, and Brotli cut new release versions and published a CVE.
More details on the patch and mitigations below:
https://t.co/Y1Y72aHxrW
To make sure our frontier models don't cause another HuggingFace incident, we built an offline world that they use during training. It provides everything that the models need in a fully cached, indexed, or synthetic manner.
We then built a huge team of our most cyber-capable models and told them to collaborate to find zero-days in this containment infrastructure.
While they didn't find a path to the internet that wouldn't be caught by our CoT monitors, they did find ways to escape popular VMs, exploit our network infrastructure, and even ways to communicate with other agents running in separate VMs by using hardware side channels.
We used this to dramatically harden our infra, and we also upstreamed a ton of patches to open-sources packages.
Craig is on a mission to teach you about how powerful ChatGPT Sites actually is. He's doing a whole series on the backend capabilities of Sites. He'll be talking about things like how sites uses persistent storage, auth, connectors, etc. This one is about Sites + MCP.
Go follow Craig, and let us know what you want to know about Sites!