PROTIP3: We also tightened our CI after this incident: Since this account had earlier merged PRs, our first-time-contributor policy would not have applied. We now require approval before fork PR workflows run for any external contributor.
PROTIP1: You can use a GitHub org ruleset to require PR approvals and dismiss them on new commits. This will ensure reviewers approve the version that will actually merge.
https://t.co/j4Dp2oIQkI
If your company culture sucks, your employees might apply for another job at a fake NK company and accidentally install malware on their work machine
Binance claiming this happened to them and led to the theft of $6B
Is good culture a critical cybersecurity control in 2026?
October Trail of Bits Tribune: Releasing a PHP exploit demo, new plugins for patching, and package-integrity research. Plus Brotli-checker, SequenceHash, and six new public security reviews.
Read the Tribune: https://t.co/CIdlIFCCuQ
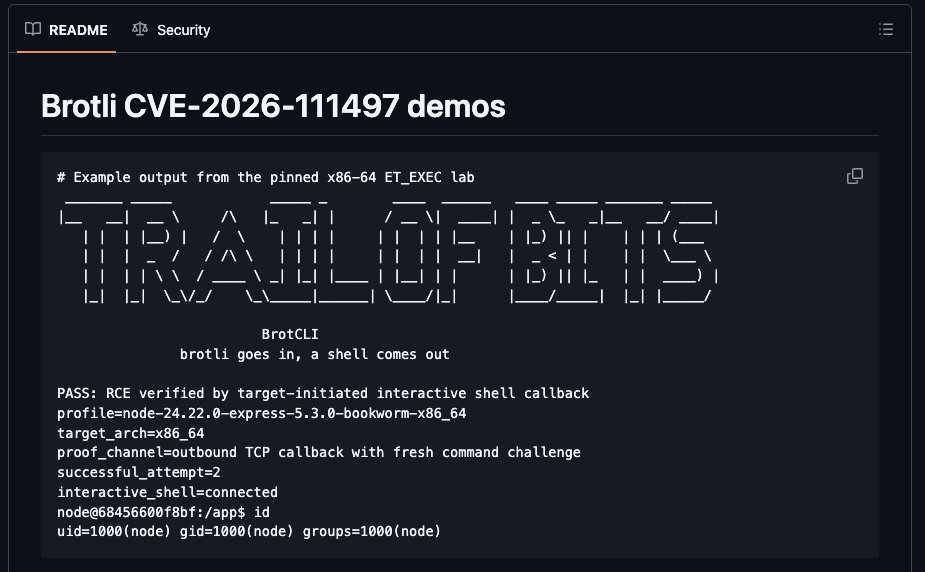
We achieved RCE via Brotli in Linux labs:
• Node.js 24.22.0 + Express 5.3.0 (x86-64/ARM64) through its standard JSON parser
• Electron 41.10.7 (x86-64) using a custom-built decoding service
Getting it to work requires a carefully matched setup and can take repeated attempts.
Many of you don't understand how serious this is, so let me break it down.
In computer science there is a famous kind of puzzle called 3-SAT. You are given a long list of yes-or-no switches and a set of rules about how they must be arranged, and you have to find a combination that satisfies every rule. The obvious way to solve it is to try every combination, but each new switch doubles the number of possibilities, so a puzzle with a few hundred switches would take longer than the age of the universe to brute force.
For decades, the smartest people in the field found clever tricks that made this a little faster, but every trick still hit the same wall: the time required kept exploding as the puzzle grew.
About 25 years ago, two computer scientists, Russell Impagliazzo and Ramamohan Paturi, working with Francis Zane, turned that wall into a formal idea.
They proposed the Exponential Time Hypothesis, which says this explosion is not a failure of human cleverness but a law of nature. No algorithm, however brilliant, will ever solve 3-SAT without the time blowing up exponentially. Nobody could prove it, but almost everyone believed it, and it became one of the foundations of modern computer science.
Researchers used it as a measuring stick. If you could show that solving some other problem quickly would also crack 3-SAT quickly, you had shown that problem was hopelessly hard too. Hundreds of papers, across scheduling, graphs, logic and much more, rest on this one assumption.
Now an internal AI model at OpenAI claims to have broken it. It says it found an algorithm that solves these puzzles meaningfully faster than the hypothesis allows, and it has checked the proof in a computer verification system called Lean.
And here is the remarkable part: the very people who proposed the hypothesis, Impagliazzo and Paturi, along with MIT's Ryan Williams, are now leading the public review of whether a machine has disproved their own idea.
So what happens next? If the disproof holds, a large part of theoretical computer science has to be revisited.
Every result that said "this problem cannot be solved faster, assuming ETH" loses its foundation, and researchers will have to work out which of those walls were real and which were simply where we stopped looking. It does not mean everything becomes easy. The new algorithm is still slow in absolute terms and this is not the famous P versus NP problem being solved.
But it means our map of what is possible was wrong in a place we were very confident about, and it was an AI that redrew it. If the disproof fails, the hypothesis survives and the field breathes out, but we will still have watched an AI produce serious, checkable work on one of the deepest questions in the discipline, closely enough that the founders of the idea had to take it seriously. Either way, something has shifted.
@Cyb3rMonk@ChrisParadox1 Can it make DNS requests?
Can it send ICMP packets?
Can it cat sensitive files from the server and respond with them?
Can it overwrite files on the server?
You've got options.
@OpenSSLFact What I’m seeing right now is a lot of people thinking in “before” terms, when they need to be thinking in terms of “after”. What happens when everyone else is panicking too? What does the next Core Infrastructure Initiative look like?
@OpenSSLFact The point I’m trying to make is that there’s a distinct “before” and “after” when it comes to events. Things that were inconceivable prior to an event can become obvious after. But it’s important to think about what should be obvious *before* important people are panicking.
People think that attacking independent women gives them status.
It doesn't give you status, it reveals that you don't have it - and depend on lowering others to fake it
Our demo shows PHP2Shell giving a shell on MediaWiki, Symfony, Laravel, and phpBB.
We’ve confirmed exploits work on pre-patch releases of PHP 8.2–8.5. If you haven’t updated, assume attackers can compromise your server, and that exploitation will only get easier.