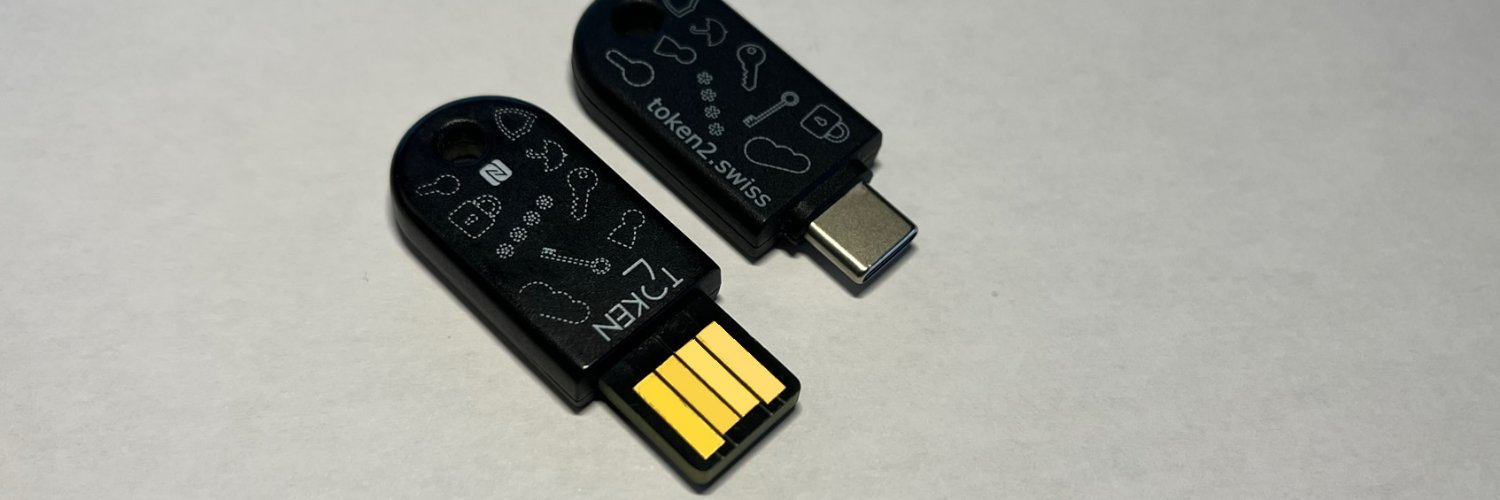
The PIN+ Dual Ace is out! Stainless steel frame, front/back touch sensor, metal USB-A and Release 3.4 firmware. Use code ACETDQ8VM5 for 8% off
-> https://t.co/V2Yvj29QQf
@loncothad@HSVSphere@caballerobrah Fido2 applet and all management tools are fully open source. PGP and PIV are based on open source projects, but not yet published as such (coming soon )
Update from FIDO Alliance: If you have implemented FIDO MDS on your server, the GlobalSign root certificate has been updated from R3 to R46. The new root certificate can be found on https://t.co/RqDxJD6t6H
Decided to do a small write-up on YubiKey NFC support in Linux. Takes about 2 minutes to setup if you have the right hardware. @Yubico@TokenTwo
https://t.co/vRoFn0ci11
@Gleycygats Hello. Yes, “https://t.co/2JnBKGToTl” is our email domain, as our HQ is indeed in Switzerland. I would recommend removing that screenshot, as it publicly exposes an employee’s name and email address.
The customers are free to use whichever tool they prefer. There are many, including standard packages available as well. Regarding Keyroost, we manually review the code and provide fixes where needed - at least for the parts related to Token2 functionality. The Linux version of our own Companion App is also being finalized; it’s just been delayed. Keyroost is designed to work with any device, not only Token2 devices.
@Dingshai It just works, all you need is to upload the uf2 from the releases. We may think of having RS-Key as the default firmware for the next batch (TBD)
Linux won't let browsers use FIDO2 keys over NFC or smartcard : only USB. So we fixed it.
token2-fido-bridge: a tiny open-source C++ tool that makes contactless & chip FIDO2 cards work for WebAuthn on Linux. Works with Chrome AND Snap Firefox - https://t.co/UDXHhh37S8
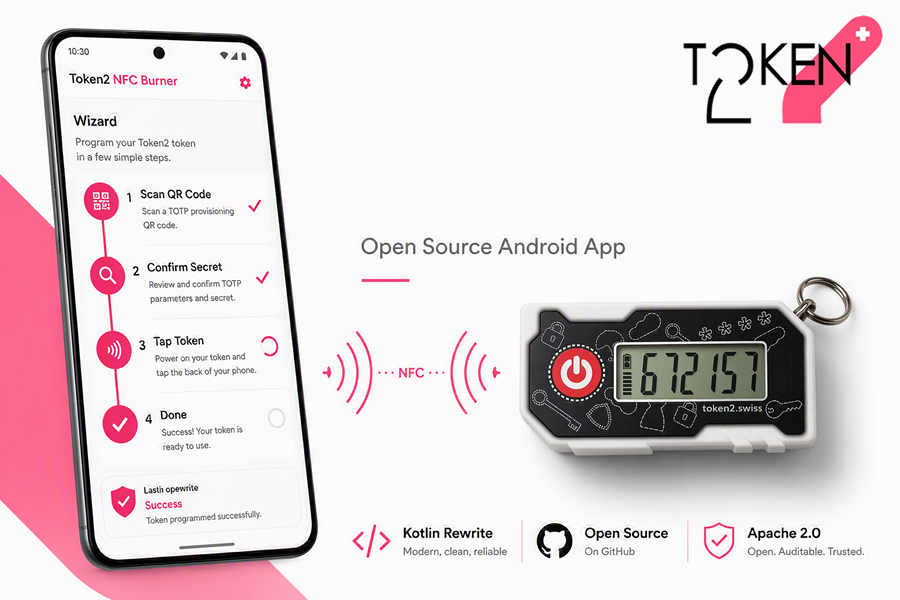
We've open-sourced the Token2 NFC Burner app.
The full source code of our Android app for programming single-profile TOTP tokens (miniOTP-2/3, OTPC-P1/P2, C301/C302) is now on GitHub under the Apache 2.0 license. Version 3.0.0 is a complete rewrite in Kotlin, with a step-by-step wizard, clearer error messages when the wrong QR code or device is scanned, and an expert mode with a manual console for advanced users. The NFC protocol itself is a byte-exact port of our reference implementation. We believe a tool that writes secrets to security hardware should be auditable. Now anyone can review the code, build the app themselves, or contribute.
https://t.co/jKUM02a9BG
Introducing Libre Key Companion - our new open-source Android app for managing FIDO2 security keys over NFC & USB. After open-sourcing much of our code in Keyroost (desktop), it's Android's turn. Cleanly written in Kotlin, manufacturer-agnostic, but Token2-first.
https://t.co/9yWnhzk45B
Introducing Token2 Companion – Rust edition (a.k.a. “Keyroost”)
An open-source, cross-platform desktop tool for managing FIDO2 keys - not only from Token2 but hardware security keys from other vendors too.
It runs on Windows, macOS, and Linux, and the entire project is fully open source: you can read it, audit it, build it, and extend it yourself.
Built on the open ecosystem, it brings a transparent and modern way to manage FIDO2 and multi-protocol security keys.
Read more: https://t.co/v0gDRUsMsv
@UneCafeAuLait @lxstf1sh @uwukko Bio3 being re-engineered to add PIV and fingerprint protection for PIV and TOTP, so we've kept the current generation at minimal stock levels. We're also finalizing a more robust successor based on the Dual platform with a metal casing, which addresses durability concerns
@0xVSultan@JohnStrongHodl@the_smart_ape@shynkariukIllia Not sure how it relates to us, but Google Authenticator is a standalone TOTP authenticator app and is not bound to any Google account (except for optional cloud synchronization, if the user chooses to enable it). The issue here is of a different nature.