@likethecoins The biggest step, that many can't seem to take is to at least have the personal willingness to try to understand. To me it is very similar to religious discrimination.
@PogoWasRight I think the individual is the owner of that SSN from cradle to grave and the parents are just authorized custodians until the owner reach's proper age. Just like when I share my SSN for professional reasons who I share it with is just an authorized custodian for that period
Added to my philosophy list:
#6 - Lead to Outcomes
Today I am reminded that what an organization deems as "success" is not true success in many instances. Most organizations especially large bureaucratic ones, generally set most people up to fail in som…https://t.co/QpGItHC4lQ
I am aware of a Program Manager position available at NAS Patuxent River, MD that would be a great fit for someone with 8-12 years of technology leadership experience. Would also be a good fit for transitioning military who have led technology teams while…https://t.co/k2SR0vkKKl
I have multiple Journeyman level ISSO vacancies located at NAS Patuxent River, MD that I am recruiting for. If you are in the market for a change, don’t hesitate to reach out!
We get lots of questions about the threat data indexed in ATT&CK, using it to show frequency of technique use, and how to prioritize. This can be a useful application of ATT&CK, but it is only a rough approximation due to biases resulting from the available data. Several reasons:
#infosec The one vendor tool that enjoys 100% market share for cybersecurity around the world and that all programs are dependant on is the spreadsheet.
#infosec TBT - A graphic I made that supported good discussions on capability, opportunity, and intent (Opportunity = "how they will get it") still one of my favorites. Focus on the green boxes to reduce adversary dwell time https://t.co/x65h3KMkXR
#infosec The only product out there that enjoys 100% market share for every cyber security program in the world is the spreadsheet you likely have open right now as you read this.
#infosec When I started getting exposed to cloud efforts, API hooks and AAA quickly become a more focused area of concern. During my electronics courses in the Navy we used to have to trace electron flow on a circuit diagram and draw arrows as it changed…https://t.co/hgalJfoIda
#infosec Almost every incident I have been exposed too, originated from the partner/supplier zone. Whether you realize it or not you have delegated a portion of your brand and reputation risk to your supply chain. Make sure you are putting some analysis e…https://t.co/qy6e5DWOmC
Orchestration- The junction where people, process, and technology all come together. It's where people build automation into process and consume information and insight generated by technology.
----->Orchestrate to reduce adversary dwell time in your en…https://t.co/ZVoJR9mWbD
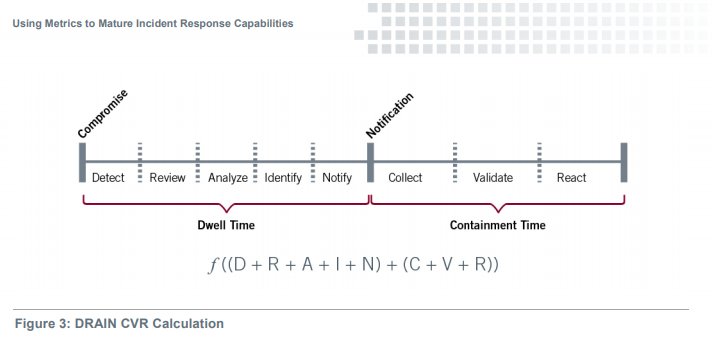
I'm such a fan of the @mandiant#draincvr incident response metrics, developed by @GradyS and #GECIRT. I refer to it constantly when building CIRTs. #DFIR https://t.co/rbxNBkQ3X2
#infosec
A few thoughts I subscribe to:
1. Compliance does not result in good security but good security does result in compliance
2. When evaluating new tech I care about "how much capability do I get per dollar spent"
3. Instead of worrying about "Nex…https://t.co/r0CMIWuEgu
#infosec I am a fan of having mission statements as it is basically the civilian version of commander’s intent and it helps team members understand goals. My version(s) is not really statements either, but questions that we have to answer (the mission is…https://t.co/ouUbHIrvZp
Visualizing the @MITREattack framework with @tableaupublic . This POC has drill-down capabilities at the tactic, technique, platform, and data source levels. https://t.co/C18Av8J8Pg #threathunting