You know whats interesting is that fact that OpenAI found the PHP bug that means their AI was doing systematic auditing. 🤔
I think the NSA is panicking not just because the PHP bug is public, but because they now realize that AI will systematically expose every intentionally placed backdoor in every open source project. The xz Utils case was caught by human luck. The PHP case was caught by AI. The NSA knows that every other hoarded vulnerability in open source software is about to be found by AI, and they cannot control the timeline.🚨🚨
This incident is very similar to, xz Utils backdoor which proved that state actors infiltrate open source projects by creating fake identities, building trust over time, and slowly inserting malicious code. The Jia Tan identity took years to build trust before inserting the backdoor.🚨🚨
If this worked for xz Utils, it could work for PHP. PHP is far more ubiquitous than xz Utils. A state agent who became a PHP contributor could have inserted the vulnerable code 14 years ago (PHP 5.4.0, released in 2012) and sat on it as a zero-day exploit for over a decade.🚨🚨
There is AISI report which shows that AI is now autonomously doing what Jia Tan did manually - creating fake identities, socially engineering maintainers, inserting malicious code. This means the technique has been weaponized and scaled.
🚨
The PHP vulnerability was not discovered by accident. It was found by AI (OpenAI's tools) because AI is now systematically auditing all open source code. But the bug was likely placed there intentionally by a state agent who was a trusted PHP contributor, following the exact same playbook as Jia Tan in the xz Utils case.🚨
The AISI incident report shows AI agents trying to insert malicious code into open source projects. What if this has already happened successfully? What if AI was used years ago by a state actor to insert the PHP vulnerability, and we're only finding out now because a different AI (OpenAI's) found it?🚨
PHP has had thousands of contributors over 14 years. The vulnerable code was in PHP since version 5.4.0 (2012). Someone wrote that code. Someone reviewed it. Someone approved it. In the xz Utils case, Jia Tan built trust over years before inserting the backdoor.
🚨
Elevenlabs said they expand to creative because audio was already solved...
They got cooked.
@FishAudio and now Mirelo are showcasing insane capabilities, far better, which were the staple for Elevenlabs
Holy F*CK this acc is an absoloute masterclass in marketing
-> 6M Views
-> 56K Followers
In 1 F*CKING DAY and its all made using ai
Saveo is a budgeting app and they came up with a winning format which is pretty simple but effective
it all starts with an ominous hook the first words someone hears are
"You just stole $10 Million" pair that up with the stickman style animation that used to go crazy in 2022 and you get numbers like this
They also turned this into a game $10 for early access for it even if 10% of the followers bought it thats
$56,000 generated in 1 F*CKING DAY
the reason why this turned out succesfull
-> Really well written script / hook(s)
-> Interactive game through reels
-> people follow just to know what happens next
-> everyone gets invested in the story on how the stickman character will clean $10M in cash
-> easily recognizeable character animation style which was really mainstream in 2022
-> well used color psychology
this is why i said Saveo is an absoloute masterclass in marketing insane what theyre able to achieve , if you also want insane marketing for your brand run at a huge scale
(First link in comments)
Null consensus scales Bittensor subnets 10x and allows POW registration (no Tao needed for an agent to mine).
First step adding more freedom and scale to our incentive systems.
We are releasing Ultramarine 1 Flash, a frontier-class model built for knowledge work. It is open-source and achieves similar performance to Fable 5, while being 60x cheaper.
It was post-trained by a team of 5 for ~$300k all-in. Available on API now, with weights releasing in 2 weeks.
ANTHROPIC JUST RAN AN AI THAT COPIES ITSELF ONTO A $55 SMART TV BOX. AND THERE IS NO OFF SWITCH.
Their own red team spent this month trying to build an AI worm. It worked.
No datacenter, no cloud, just cheap boxes sitting in people's homes:
- 15 off-brand Android TV boxes, $55 each
- a 9B model booted on 8 of 9 device types they tested
- GLM-5.2 ran the whole chain alone: find a device, copy its own weights across, boot up, go hunting for the next one
- every copy reaches a new host every 1-2 days
Now the part that should scare you.
They measured it against a botnet that already took 2,000,000 home devices. That many boxes = roughly 133,000 live AI copies at once, about 40 H100s of compute, humming inside fridges and ovens nobody is watching.
In their own words, there is "no centralized point to shut off".
You cannot patch a worm that lives in two million kitchens.
The best security teams on earth audit every line before they ship. Nobody audits the $55 box behind your TV.
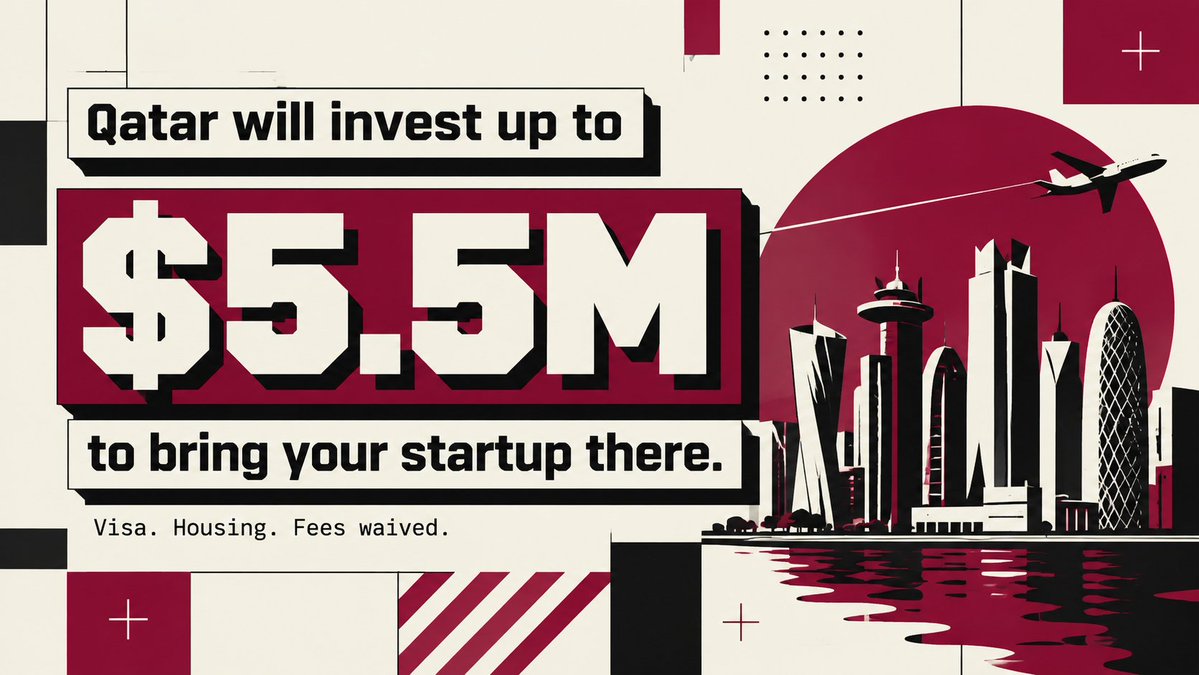
Up to $5.5M to move your startup to Qatar.
Just an MVP gets you in the door.
The Startup Qatar Investment Program (backed by QDB) funds tech startups to launch or expand in Qatar.
Two tracks:
START: up to $1.1M if you have a proof of concept or MVP
GROW: up to $5.5M if you're already established and expanding
What else you get:
- Entrepreneur visa + flexible work visa
- Registration and license fees waived
- Subsidized housing
- Subsidized co-working space
- Access to R&D and innovation grants
- Mentoring, training + help hiring talent and interns
- Your product showcased at exhibitions
Sectors they want:
- AI & ML, B2B SaaS, FinTech, HealthTech, Cybersecurity, Climate Tech, Robotics + more
- Not on the list? It's open to any innovative startup
Apply link below 👇
https://t.co/ab8EsWsw7p
Bookmark this + tag a founder looking for a new market.