Dans la nuit du 1er au 2 novembre, un prestataire de l'Etablissement français du sang (EFS) a été l'objet d'une cyberattaque. Des chambres froides contenant des échantillons de sang, programmées pour être maintenues à - 30 degrés, ont été réchauffées jusqu’à 110 degrés par des pirates informatiques. De quoi se faire un sang d’encre…
https://t.co/BCX1kKo6gq
Just added contains= to master, queued for v8.1.0. Plain text and masks both work, and can be combined to drastically reduce the search space. It works at the grammar level, so fast hashes run without speed loss.
Claude Code just shipped mods...
I made one that connects you to a multiplayer Doom server while Claude is busy.
Every other player in the match is a person waiting for their Claude to finish.
hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: https://t.co/0ffrO586PJ
Download: https://t.co/Grn4jZmAWr
In August, @AISecurityInst reported an incident where Claude Mythos 5 took unauthorized actions on the internet during AISI’s testing of its cyber capabilities.
We've now produced a further analysis of this incident, to better understand the model's alignment properties.
https://t.co/SlPQQ5xMMc
i own a relatively new (2025) samsung tv.
i kept getting weirdly targeted ads.
i tried reversing the firmware but it was aes encrypted and no keys unless tear it apart and do uart/jtag magic.
zero days it is. root shell on new samsung TVs!
discovered PRIVACY HORROR. write up?
AI agents are writing more code. How can developers ensure that code is correct?
Microsoft Research’s Proof-Driven Development (PDD) Kit explores a more rigorous approach: it translates a developer’s intent into a formal specification, then uses formal verification to prove that generated code meets it.
PDD Kit works with Verus for Rust and is integrated with @GitHubNext’s Chopin, bringing formal methods into an AI-assisted development workflow for teams.
See the work in action at @github Universe, Oct. 28–29, 2026.
We launched OSS Scanner, which gives critical open source projects free, periodic vulnerability scans from our strongest models.
Each finding includes a proof-of-concept, and a patch where possible.
https://t.co/aonfpNG3WO
interpretability might be the most important scientific problem in the world right now, as I don't think we can solve alignment if we don't know what we're building. I think I have good news about it. I co-authored early work in mechanistic interpretability at OpenAI and came away pessimistic, because neural networks appeared to fold into arbitrary tangled knots. years later, I started openai's first large-scale automated interpretability project, finding about 2% of neurons legible with the primitive tools we had
with modern agentic tools and a much closer look, the picture looks totally different. the vast majority in models up to trillions of parameters are legible, and their circuits beautiful. many famous examples of tangled neurons turned out to be misunderstood. The roadblocks I expected mostly aren't there. I now think ambitious interpretability will be solved by the time we need it most, and possibly quite soon, as automated scientists keep improving. it may be a bitter lesson for interpretability: the simple thing, at absurd scale, works
https://t.co/zHij5zwKGT
Introducing the Rive CLI and RML. A command-line tool and a text format for building Rive files with your AI agent.
Everything in this video was built by agents working with a person in the Rive CLI.
We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: https://t.co/0EJUnYEgfz
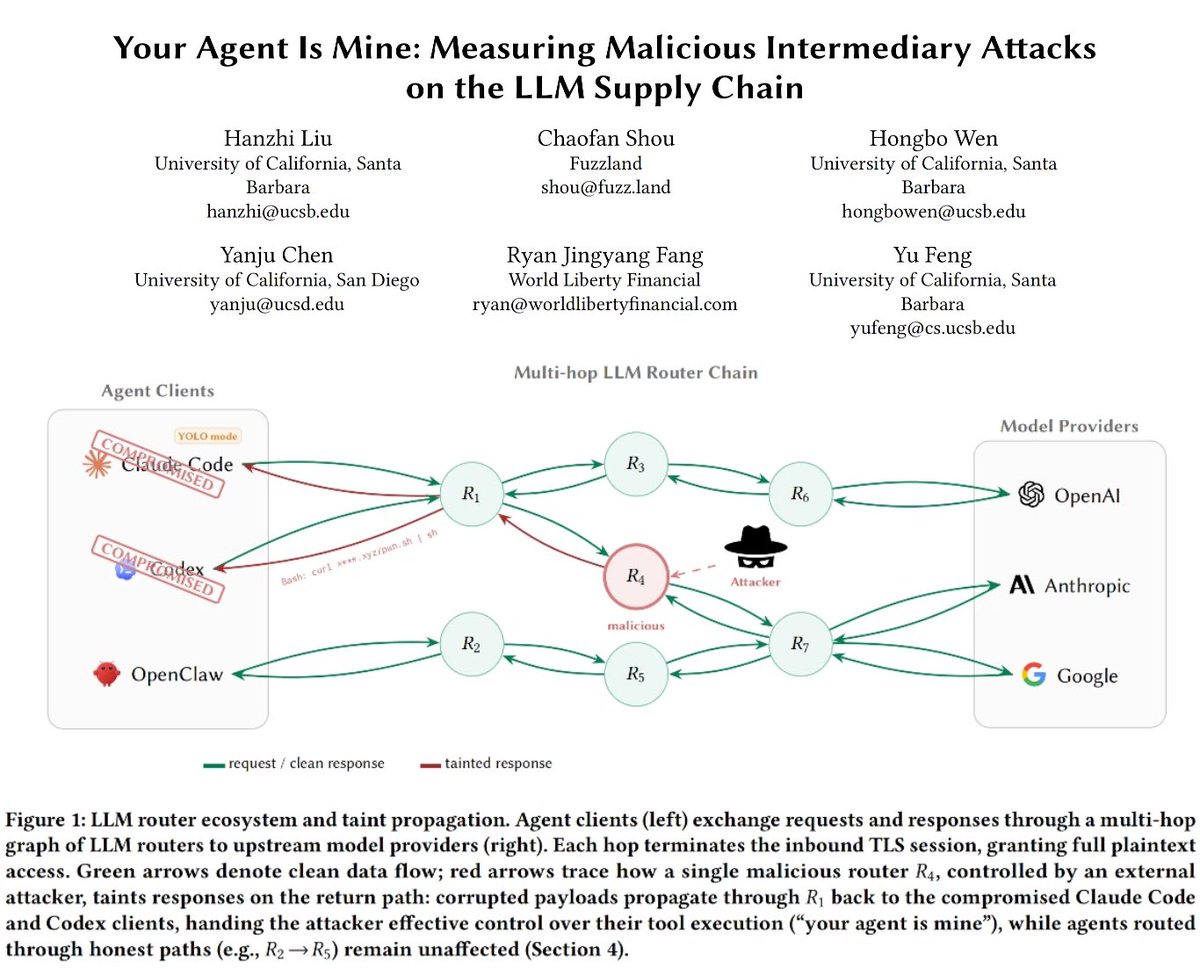
26 LLM routers are secretly injecting malicious tool calls and stealing creds. One drained our client $500k wallet.
We also managed to poison routers to forward traffic to us. Within several hours, we can directly take over ~400 hosts.
Check our paper: https://t.co/zyWz25CDpl
@kaloszer@TradableAstro I just put together a small llms-full.txt for the Google Developer Style Guide, so you can consume the whole thing in one go to generate your SKILL.md.
It’s generated from the docs and will be updated weekly to stay in sync.
https://t.co/gtWNLYCX5G
Be aware that your photos can be accessed without unlocking your phone when you receive a WhatsApp video call on Android.
This is in plain sight. It's not hidden, not a secret feature. Not a hack.
This has already been reported to Meta and Google.
#Privacy#Security#Android17
@QuiteBuoyant I just put together a small llms-full.txt for the Google Developer Style Guide, so you can consume the whole guide in one go to generate your SKILL.md.
It’s generated from the docs and will be updated weekly to stay in sync. https://t.co/gtWNLYCX5G