CEO, Software Developer, Military Contractor • 30m+ Customers • Jesus is God (YHWH) — Im a pinch of clay baked in the furnace, yet somehow still retaining water
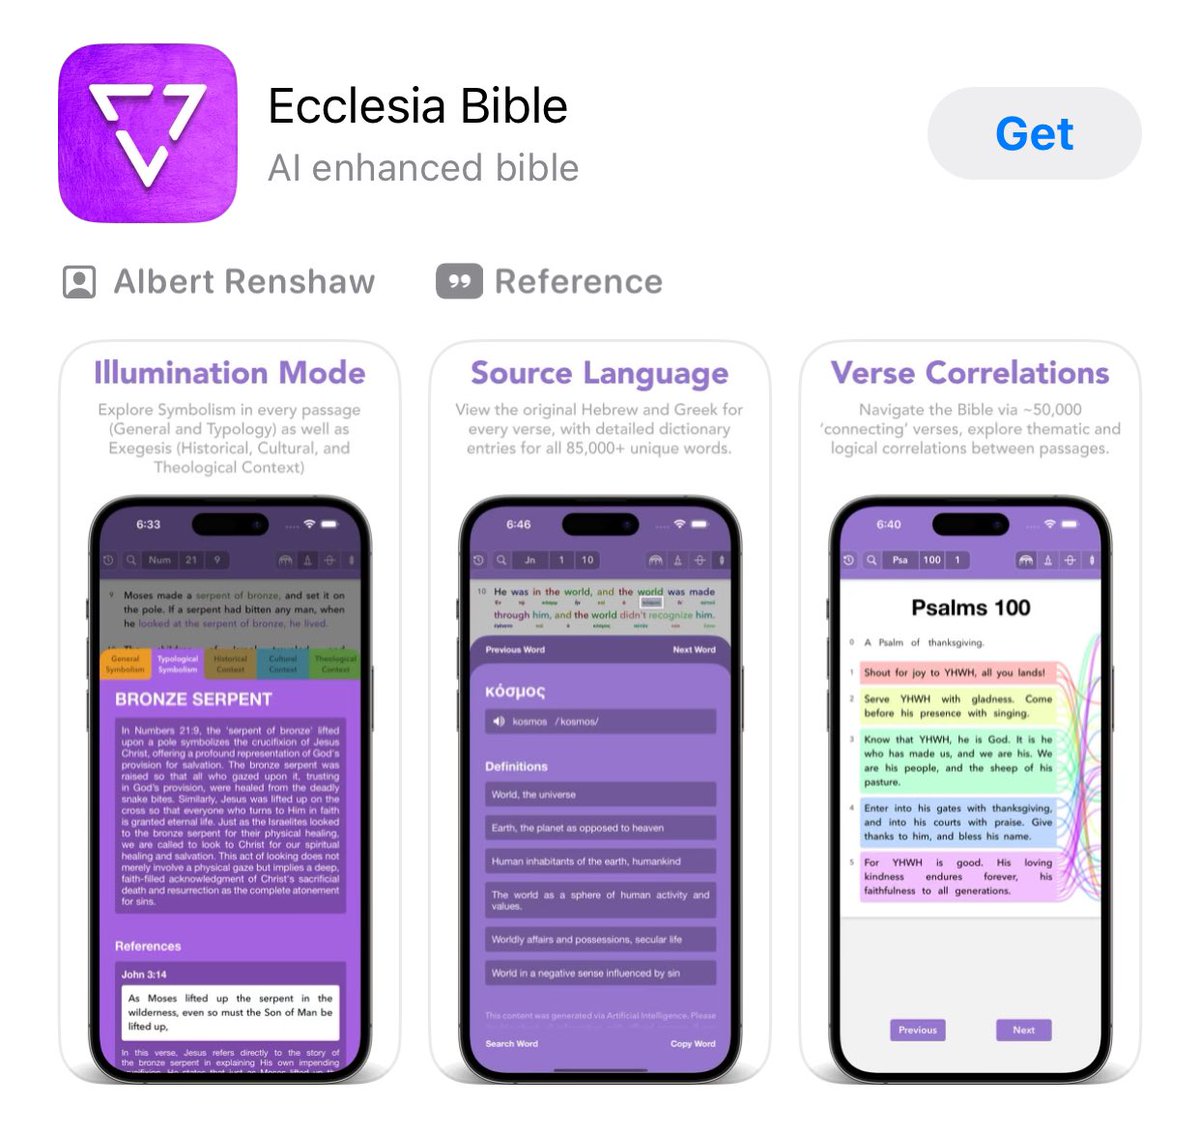
My app @Ecclesia_Bible is now live!
Built in Ai powered symbolism and exegesis, total translation from source language, verse correlations, in-line translational variations, and more.
This is the first app from my newest startup, Tanzanite
This is why I liked “0x…” format before hex. It denotes hex but it’s also an explicit marker of size boundary if you do end up converting to string or not. This is irrelevant from a code perspective but if you’re reading it printed out you can notice mismatches visually easily
When I was coding Ethereum’s signing mechanisms for mobile env, I found a quirk in SHA-3 how it handles S and V values when they have leading zeros, and I only noticed it because the explicit 0x form, rather than pure number form, caused the strings to not be the same length, and I saw that leading zeros were getting stripped by some low level cryptography operation dependency. I had to add the zeros back in (though I was too worried that this is a bad practice and there may be some reason these were being dropped, and this was before you could just ask an LLM what gives [and there was no real documentation for these high level abstract internal libs] so instead I just would fail it and generate a new signature lol [ethereum’s ECDSA is non deterministic and different RSV values happen each time, …surprisingly])
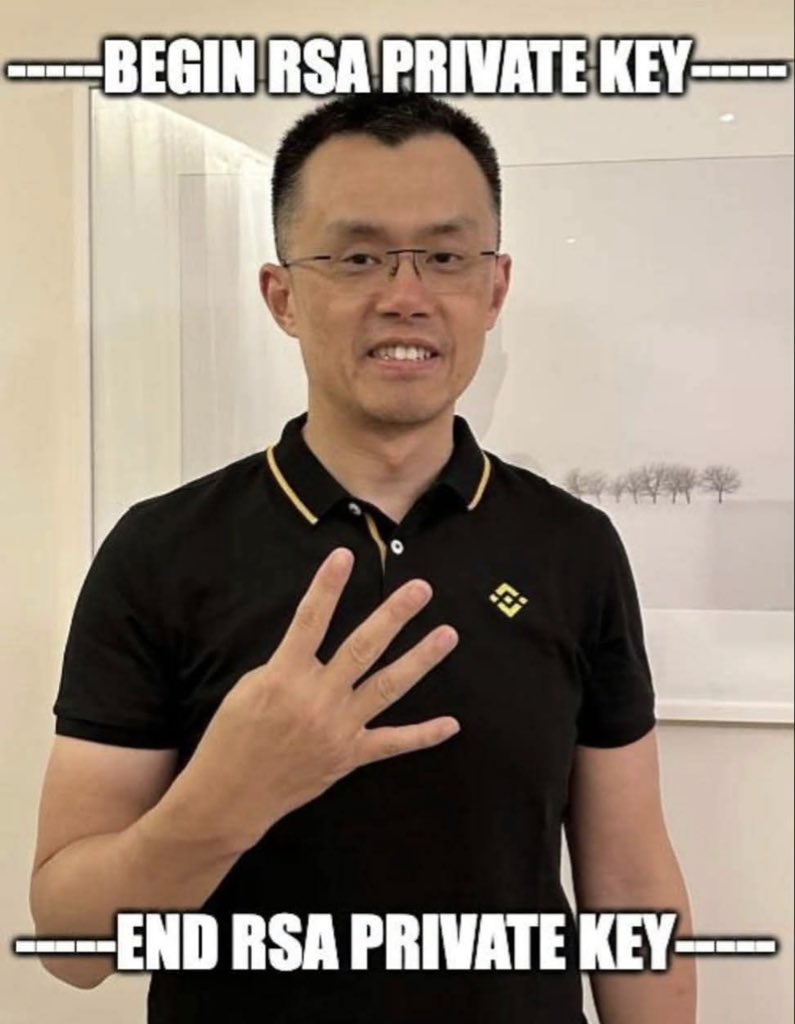
Technically it wasn’t 4 (as in 0000…00004)
but was 4 as in 004
But encoding mechanisms then normalized it to the valid size 00000….0000004
Leading zeros give you an exact size (these PKs are meant to fit the size of 2^384), they were generating rng(256)
If the encoder had flatly rejected it as wrong size it would have been fine. These technically are arrays/sets but we use integer math libraries when presenting the results, as it’s easier
If encryption functions requires typed arrays only and didn’t allow incompatible sets at all, this wouldn’t have happened. But because they cast from array to integer and back due to various ease of use functions (and the padded zeros just get added in freely) this information is lost.
It’s a bad practice; but it’s also totally fine if you’re not making extreme bone-headed mistakes like this. The devs making these libraries presume that those who use them will stay in a consistent size
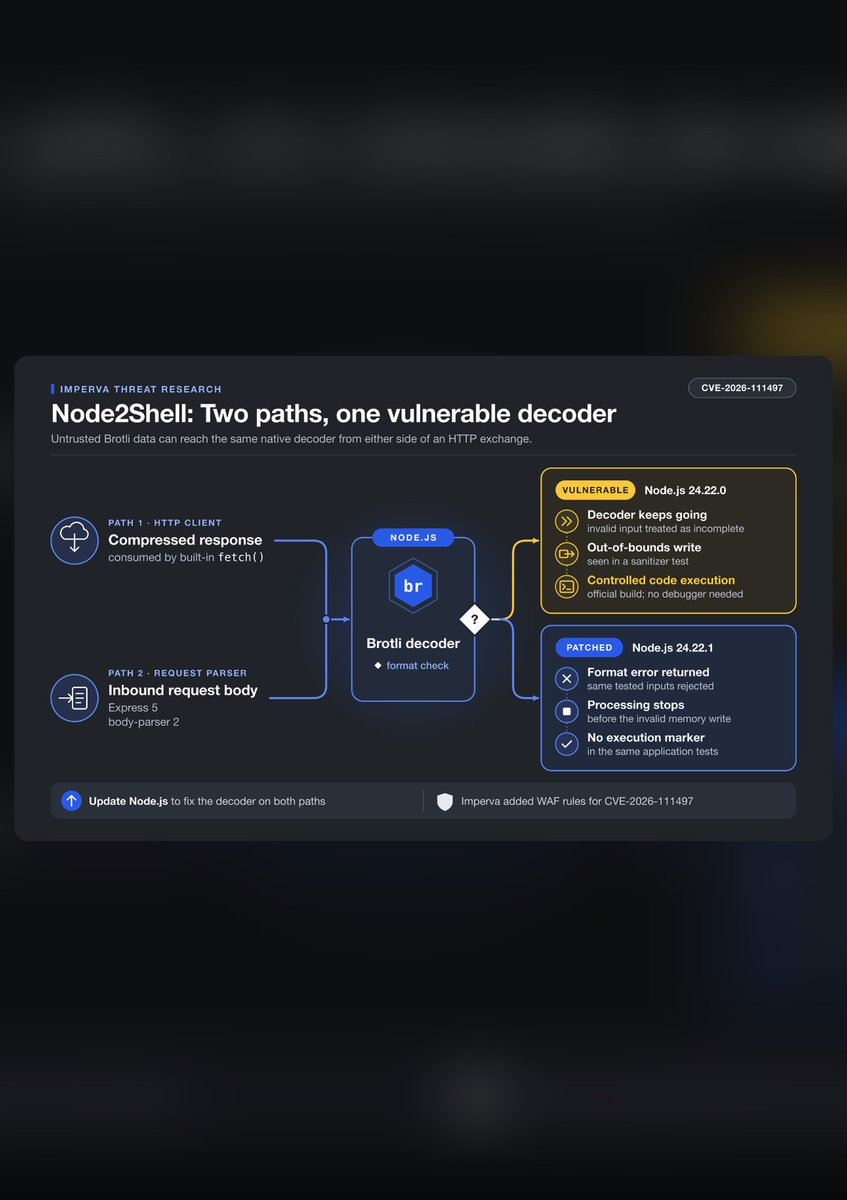
‼️ After PHP2Shell comes Node2Shell, a critical bug found by OpenAI's Codex Security that can let attackers run code in Node.js apps.
It was successfuly demonstrated on the official Node.js 24.22.0 image.
Node 20, 23 and 25 (all EoL) get no fix.
This won’t work.
One attacker with $10m in compute can attack endless individuals dynamically
Endless individuals can’t have $10m in compute each
The incentives are asymmetric
Your proposal would force centralization
ie - Our computers all join a giant cloud provider with one aggregate defender network who can afford to out compete any one attacker
It may be the case that for networked computers we simply have to head this way. Personal computers become airgapped or if they need networking capabilities they have to pass through these cloud fortress endpoints for safety (which means no encryption…. or else how can it possibly defend you; can’t know the difference between a horse and trojan horse when they look identically random)
What's your private key? 1?
>...what? No?
2?
>It's 384 bits you dumbass. That's 35 orders of magnitude larger than the estimated number of atoms in the known universe.
...3?
>[visibly sweating] Th-this is ridiculous...
I feel we have gotten extremely far off topic from my original claim "work is for the machines"
Status games that may involve threats of death exist in all scenarios; this isn't something only related to this future scenario; this is already a thing, I'm not sure how it relates to my claim, and I don't have time/desire to go down a whole different tangent, so I think I'm going to conclude the chat here 🤓
It is surprising no one checked!
Any keypair I’ve ever generated, I visually see it on the screen. If I saw 4 I’d regen but I’d also freak out and go buy a lottery ticket lol (assuming no bug in key gen script)
I’m guessing this was fully automated therefore, and some typo in the automated key generator caused it to be like csRNG(384) instead of csRNG(2^384)
[although technically not every value between 0 and 2^384 is valid anyways; 0 for example; and the marginal set of values above the order of the curve]
Even still, baffling no one saw this bug when the automated key generator code was being made and tested…
…implies decent chance this was intentional backdoor able to be shared with no communication or paper trail evidence
@dmitrykrachun@ereliuer_eteer If math statements like this were true, ECC would have a major vulnerability in attack surface
(Which is how we know math statements like this are not true)