🎤 Heute auf der Bühne der @PECB Conference 2026 in Rom: Valeri Milke, CEO der VamiSec, beim Panel „DORA Reality Check“.
Ein Jahr #DORA zeigt: Entscheidend ist nicht die Policy, sondern ob die Evidenz einer Prüfung standhält. 🇮🇹
#PECBConf26#GRC
I was told NIS2 would be a checklist.
It's 10 risk-based measure areas with management accountability (NIS2 Art. 21; § 30 and § 38 BSIG).
Take the stairs. Or take the elevator. -> https://t.co/shFnR4OgsF
100% AI-generated. Security-approved. #GRCslop
Key fact: PlayStation paid out the maximum $50,000 bug bounty to researcher Jordy for reporting a critical security vulnerability, who joked he could finally buy GTA 6 with i
5. Passkeys are not a trap, says Helme — the security researcher pushes back on passkey skeptics: they protect login, not the session. https://t.co/mBY0zm3IKn
The death of a research scientist in Irkutsk in early October forced the FSB to operate out in the open where it usually prefers to remain undetected. Over the last few years, the security service has seen its role strengthened in the fight against epidemics, high-risk laboratories and international cooperation over the plague and other pathogens handled by the deceased researcher.
➡️ https://t.co/0RxJnSpfnA
Lovable has dedicated IP’s on their load balancer.
The issue is they were hosting pages on their dev sub-domain which was getting people to download an InfoStealer Trojan.
Their IPs were substantially blacklisted and if your domain website A record pointed to them, then you would have problems with your own domains email deliverability since major email service providers also consister website reputation when making algorithmic email threat decisions.
Tl:dr: loveable need to implement a proactive anti-abuse team.
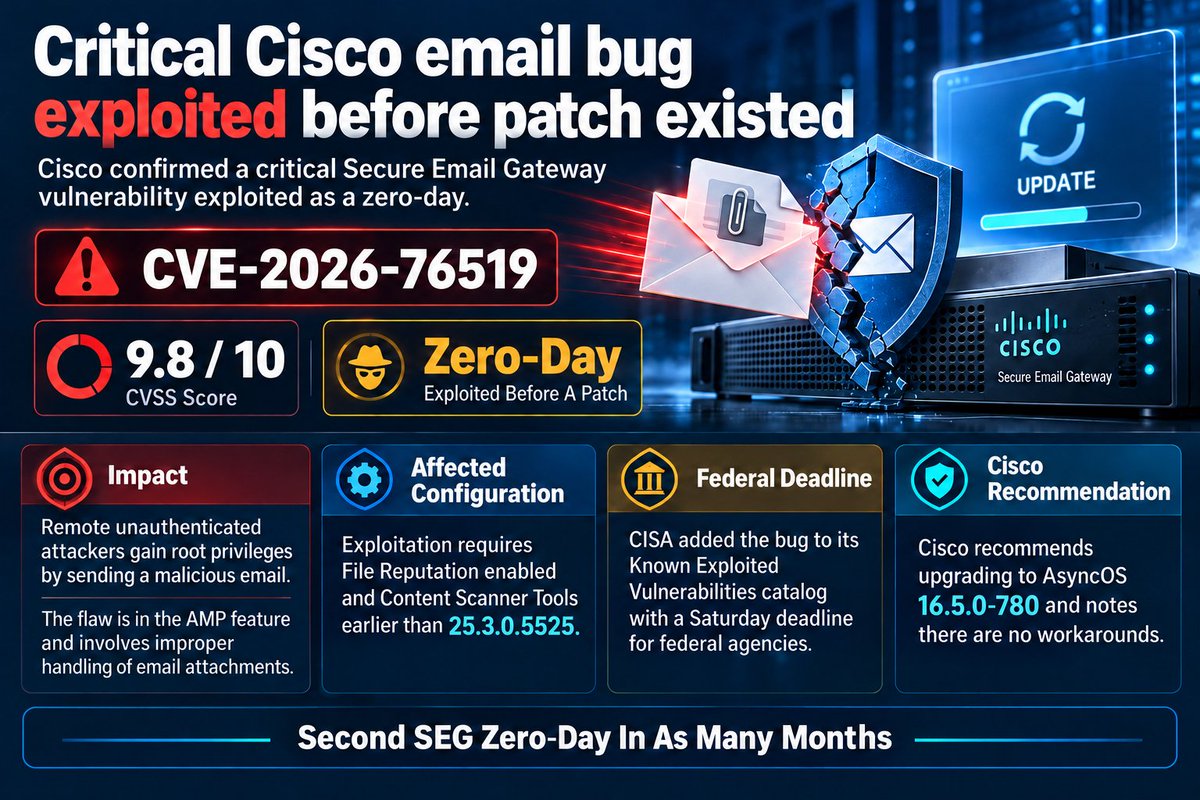
Cisco SEG zero-day exploited with root access via email
Cisco urged customers to patch a critical vulnerability in its Secure Email Gateway that has been exploited as a zero-day.
The bug is tracked as CVE-2026-76519 and received a CVSS rating of 9.8 out of 10. It allows remote unauthenticated attackers to write files and execute commands with root privileges by sending a malicious email.
The flaw exists in the Advanced Malware Protection feature and stems from improper handling of email attachments.
Both Cisco and CISA issued separate advisories on Wednesday warning of active exploitation.
CISA added the vulnerability to its Known Exploited Vulnerabilities catalog and set a Saturday deadline for federal agencies to apply fixes.
The vulnerability affects physical and virtual appliances when the File Reputation service is enabled and Content Scanner Tools is earlier than version 25.3.0.5525.
Cisco recommends customers running AsyncOS Software earlier than v16.5 migrate to 16.5.0-780 and states there are no workarounds.
🚨 Hackers Exploit Palo Alto PAN-OS 0-day Flaw to Gain Root Code Execution on Firewalls
Details: https://t.co/hmMy1Z9dsB
Hackers are exploiting a high-severity flaw in Palo Alto Networks PAN-OS that allows authenticated attackers to run code with root privileges on affected firewalls.
Tracked as CVE-2026-0322, the vulnerability affects the management interface, with the company confirming “very limited exploitation” and urging customers to apply fixes as soon as possible. The flaw is a code injection weakness, classified as CWE-94.
An attacker must have authenticated access with high privileges and network access to the management interface. Successful exploitation allows code execution as root, giving the attacker the highest level of control over the affected firewall.
#cybersecuritynews
CrowdStrike collaborated with the @FBICyberDiv to identify and disrupt individuals associated with the North Korean IT worker scheme, designed to infiltrate U.S. companies and generate revenue for the regime.
The operation dismantled more than 40 laptop farms and seized nearly 200 devices, disrupting the infrastructure behind these schemes, raising the cost of doing business for the adversary.
CrowdStrike's Head of Counter Adversary Operations Adam Meyers shares insights with The New York Times on the growing scale and sophistication of these operations.
Read more: https://t.co/HRuhYLkuqI
ICYMI: CrowdStrike worked alongside the @FBICyberDiv to identify and disrupt individuals tied to North Korea’s IT worker scheme, which places operatives inside U.S. companies to generate revenue for the regime.
The result? More than 40 laptop farms dismantled. Nearly 200 devices seized.
Learn more about CrowdStrike’s role: https://t.co/S97w0oASkB
On-device scam classification with a fine-tuned small model is the right architecture: no message leaves the phone. This is the pattern privacy regulators will reward; cloud-scanning every SMS was never going to survive GDPR scrutiny. Small models will own the privacy-sensitive niches.
Workflow lockfiles close the tag-drift hole in GitHub Actions: pinning by tag was advisory, locking commits is enforceable. After GhostAction-style workflow attacks this belongs on every repo-hardening checklist next to OIDC federation. Supply-chain controls are finally becoming defaults, not addons.
@dascoolequartz@whitewingsuits Stimmt: eine Masseninfektion aller Router waere teuer und laut. Die realen Faelle sind gezielter; Firmware-Integritaet und der Update-Kanal sind die Pruefpunkte, nicht die Panik. Fuer Unternehmen lohnt der Blick auf verwaltete CPEs: wer signiert dort die Firmware?
@Ventibeev Token theft via infostealer is why 'reset the password' is not recovery: sessions survive. After infostealer incidents, revoke all sessions and rotate API tokens; cookie theft bypasses every password control you have. Session-inventory is the IR step most playbooks still miss.
@joe4security Fake Hopper DMGs delivering infostealers hit the reverse-engineering community itself; ironic and effective. Tool downloads need hash verification even for security software; attackers know exactly who skips it. Homebrew and package-manager provenance checks are the cheap fix.
@Fittyxofficial Clipboard hijackers and fake trading apps thrive because users cannot verify what they pasted. Hardware-wallet 'verify on device' exists for exactly this; the same pattern is coming to enterprise payment approvals. Out-of-band confirmation beats any in-app warning banner.
Legal identity for non-human actors is becoming a real gap: agents transact, but liability still anchors to humans. Registers of agent identity with accountable owners would close the loop; expect this in AI Act implementation debates. Today the deployer carries it — document accordingly.