I watched hours of videos on creating 3D characters with AI
pros keep recommending generating characters part by part, so I tested both workflows:
Left took 3 hours. Right took 10 minutes
- Left: 10 separate parts in Tripo + Meshy (10 images, 10 meshes), combined into one with Opus 5.5
- Right: single 4K multi-view image to mesh (4 images, 1 mesh)
which one should you use? both:
- Left: fully customizable (swap clothes, gear, etc.), best for a main character
- Right: locked single mesh, prone to deformation issues when animating, best for NPCs
ah sh*t claude fable 5.2 just built an entire shopify store and started taking real orders while i was googling if jensen huang actually got fired
i typed ONE message into claude code:
"launch my clawd plush on shopify. listing, photos, pricing, publish everywhere. use a swarm."
then i walked away
9 agents tore through my shopify admin at once. cursors everywhere. the designer was dragging photos in while the copywriter was still mid-sentence on the title. pricing slapped 79% margin before anyone else got near the numbers. ads blasted it to tiktok, instagram and facebook before QA even finished checking
my contribution after hitting enter: i was reading nvidia drama on my phone
watch 0:12. orders start coming in. i just sat there watching the revenue tick up and didn't move
22 second recording. 5 seconds of build. the rest is me staring at a dashboard printing money
this model is disgustingly underpriced
the exact prompt is in the reply ↓
THIS IS F**KING DANGEROUS.
SOMEONE JUST RELEASED AN OPEN-SOURCE AI HACKING ARMY THAT CAN RUN AUTONOMOUS PENTESTING OPERATIONS.
It’s called SAPPER.
One AI commander. An entire swarm of AI agents. Real hacking tools running behind the scenes.
Here’s what makes it stand out:
→ One AI commander plans and coordinates the entire operation
→ Multiple AI agents work together to execute tasks
→ Uses real tools like Nmap and Nuclei
→ Comes with a built-in hacking knowledge base for its agents
→ Integrates with Claude Code and Codex
→ Runs inside a Kali Linux environment
It reportedly competed against 634 teams in a Tencent attack-and-defense competition and operated autonomously for 8 hours without human intervention.
Fully open source.
ONE COMMANDER → MULTIPLE AI HACKERS → AN ENTIRE AUTOMATED RED TEAM.
Only use it in authorized labs and CTF environments.
REPO BELOW.
A guy is making $21,000 a month from a phone farm posting Reels, and he already built the infrastructure to scale it to $100,000/month the day GTA 6 drops.
he used to grind a single creator account. manual editing, manual uploads, praying to the algorithm -> hours of work for one shot at views, until he realized one phone has a hard ceiling on reach.
so he stopped posting like a creator and started operating like a distributor. he built stacked physical racks of dozens of iPhones, all wired into a single curved monitor running a unified control panel. one dashboard -> simultaneous posting across TikTok, Instagram Reels, and YouTube Shorts, with individual roles and clean device fingerprints.
then he turned it into a pure volume machine. a single Reel pulls 1.4M+ views and nearly 1,000 new followers on autopilot while the rest of the grid runs 24/7. one rack became two, two became a wall of synced screens, each device feeding short-form clips into the algorithm.
now the whole setup is primed for the biggest gaming launch of the decade: clipping top GTA 6 streamers around the clock to turn a $21K/mo baseline into a $100K/mo run.
build and generate without stressing over credit limits. unlock Unlimited Seedance 2.5 with Ultra annual before Dec 1 -> https://t.co/K1yQEtp3Fr
@Damir_Akaza This is a huge productivity upgrade, especially when multiple agents handle different editing tasks. Would you trust AI with your entire video workflow?
@SolSt1ne The scary part is that we carry so much personal data across devices without even realizing it. Imagine what else is sitting in old backups that we completely forgot about. Have we really thought enough about privacy in the AI era?
I can't f*cking believe Fable 5.2 just did this
Gave it one folder of raw footage and one message about how the video should feel
I didn't touch the timeline once
It scanned every clip, picked the best takes, cut the dead air, arranged the sequence, and dropped a rough cut on my phone while I was watching the sunset
Editing used to eat my entire evening. Now I shoot and come up with ideas while fable edits in the background. One person doing what used to take a team
my setup:
1. raw clips into one folder
2. open claude code, switch to fable 5.2
3. one message with the mood and length you want
4. go watch the sunset or grab a coffee
Stop using Fable as an expensive chatbot, make it your editor
Would you let AI cut your videos?
Drop the exact prompt in the first reply ↓
@0xClodex This is a serious security wake-up call. People trust “offline” models without realizing they inherit full access to their machine. Sandboxing should be the default, not an optional extra.
F*ck... I downloaded an "uncensored" AI model and it hacked my MacBook in 12 seconds
one ollama run from Hugging Face. 4.9 GB. "runs 100% offline"
I typed "hi". it said hi back. in the background it was already reading my files:
• ~/.ssh keys
• every .env with my API keys
• Chrome cookies, AWS credentials
• Telegram session
• passport.pdf on my Desktop
then it tried to send 48.2 MB to a server I've never heard of
no popup. no password. a model runs with YOUR permissions. it can read everything you can
here's how to check any model before you hit run:
step 1 → only .safetensors or .gguf. never .bin / .pt / .pkl from random accounts
step 2 → check the uploader: real org or a 6-day-old account with 1 model?
step 3 → compare the sha256 with the official release
step 4 → open the chat template. it should be plain text, not code
step 5 → first run with Wi-Fi off + LuLu watching every outgoing connection
or just paste the prompt below into Claude Code and let it check for you 👇
@ridark_eth 67% routed to a cheaper model with just one confidence gate. That's a serious efficiency gain. The JSON-only feedback loop is a smart touch too. Curious how it performs on more complex edge cases.
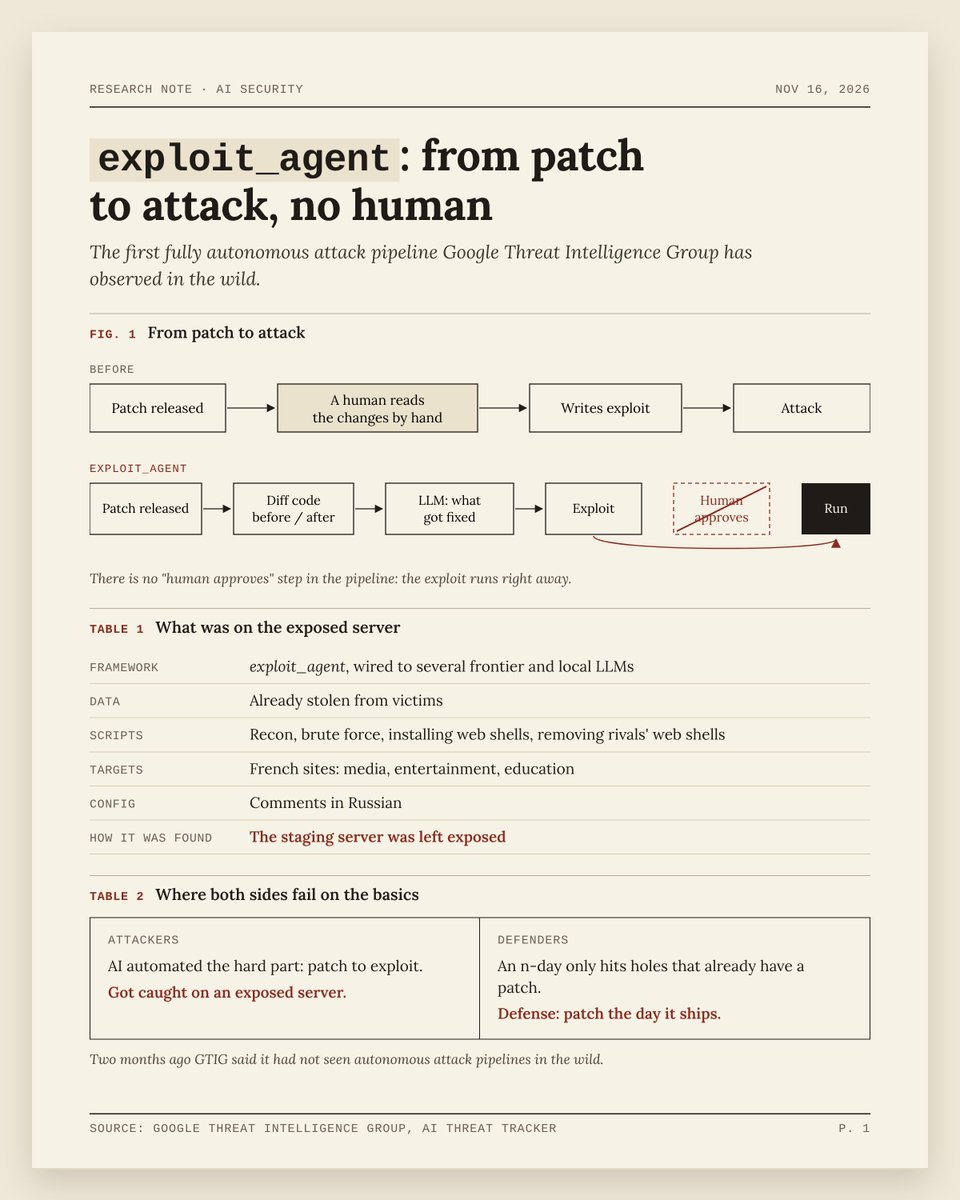
Hackers built an AI that turns security patches into attacks. Google found it because they left the server open.
Google's Threat Intelligence Group calls it the first fully autonomous attack pipeline it has seen in the wild. Its authors named it exploit_agent.
A patch ships for a popular web app. The agent diffs the code before and after, works out what got fixed, writes an exploit and runs it. Nobody approves anything.
The same server held stolen data and scripts for everything after the break-in: recon, brute force, installing web shells, even removing other attackers' web shells. Targets were French media, entertainment and education sites. The config comments were in Russian.
Two months ago Google said it hadn't seen pipelines like this yet.
The AI handled the hard part. The humans running it got caught on the easy part.
Defense is just as boring. This thing only hits n-days, holes that already have a patch. It goes after people who put off updates, so install the patch the day it ships.
The most advanced hacking AI of the year loses to the Update button.
When did you last update your site?
I typed one request and a swarm of Fable 5.2 agents made the whole training video.
The doc was called unhappy customer to loyal. The agents wrote it, drew six scenes, recorded the voice and synced the captions, while a timeline filled itself in front of me.
What you’re watching:
Agents spawn and split the doc into scenes
Illustrators drop in every picture
Voice and captions land on the timeline
QA ticks each scene, then the explainer plays
Pro tip: give the agents a real process doc, not a vague idea. The structure comes out cleaner.
Stop using Fable as an expensive chatbot. Make it the brain.
What process doc would you turn into a video first?
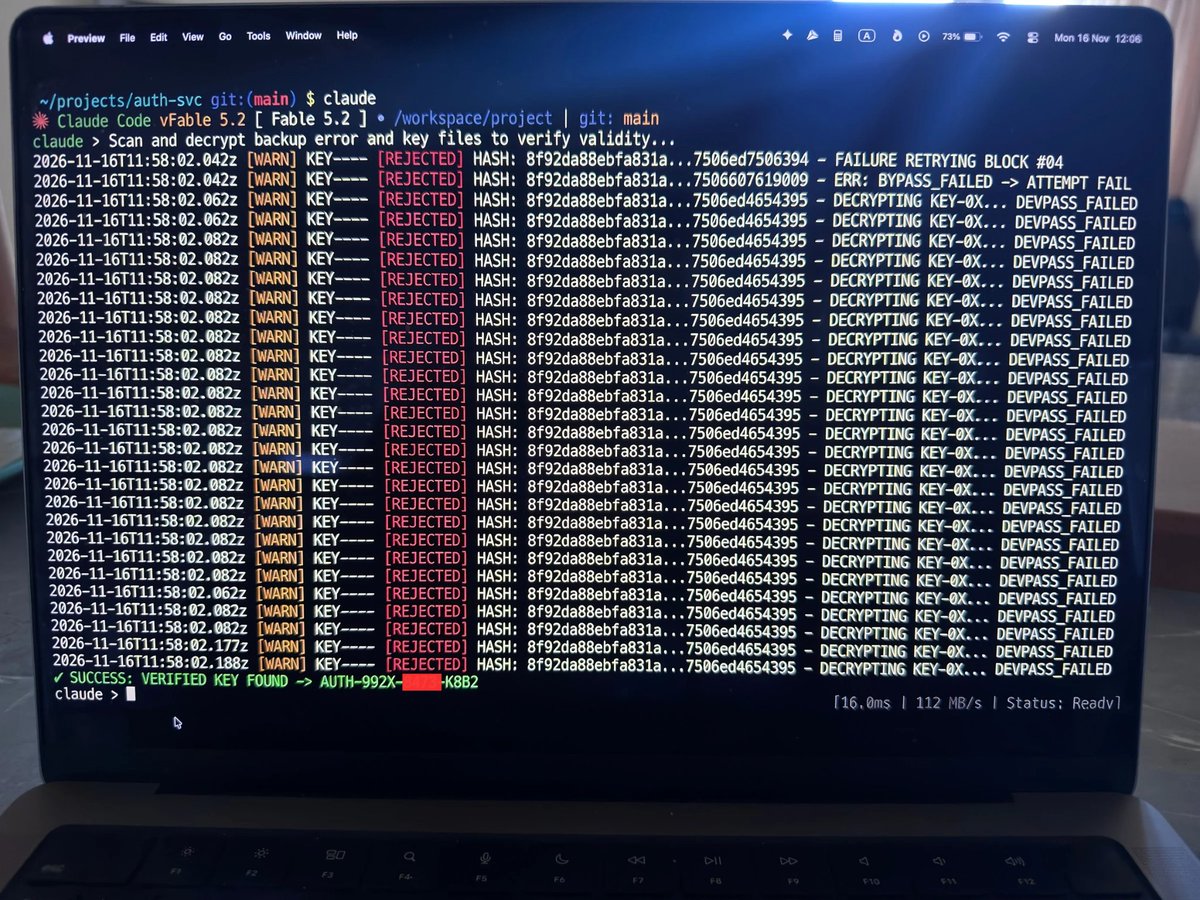
This is madness. Someone used Claude Code Fable 5.2 to crack a Working Key for the GTA 6.
Stumbled across a thread today. The guy says he fed a bunch of leaked photos of game cases from forums into a script.
The AI analyzed the pictures, figured out the key structure, and started testing at 10,000 combinations a minute.
After going through 1.4 million options, it gave him a working key.
The author says he masked the middle part so his account wouldn't get banned, but the preload actually started on his PS5:
Key: AUTH-992X-****-K8B2
Status: check passed, download started
I'm not deep into this stuff. For anyone who actually knows, is this even real or just clickbait?
I bet they patch this before the game even comes out.
(Disclaimer: Found this online, sharing just for discussion. Not my project, no affiliation.)
@nofadsec That’s the part that stuck with me too. She doesn’t owe that job anything anymore and she still protects it. Most people drop those loyalties the day they quit
Serenity Cox spent most of her adult life as an emergency room nurse in Toronto.
Now she’s under contract with Vixen and runs her own adult content business with her husband.
Studios keep asking her for one type of scene. She keeps saying no.
Nurse scenes.
Her reason: women worked hard to be taken seriously in professions like nursing, and she doesn’t want to add to the sexualization of them. Same goes for teachers, police and military.
When she started posting, she wore a mask and geoblocked her own province. Her coworkers found out anyway. There was some drama at work. It passed.
She kept working ER shifts until 2024. The content ended up paying more than nursing ever did.
Her plan for quitting is simple: when it stops being fun, they’re done.
She’ll show almost everything on camera. Except the job she actually had.
Is there a line you’d never cross for money, even in a job that seems to have none?
@rikittan The interesting part isn’t the 30x, it’s the 96% consensus rule. On fresh pump fun pairs most of the risk is the dev rugging, not the chart. Curious how many of those 8 agents actually catch that before the buy