Are you ready to revolutionize your organization's approach to #cybersecurity?
We are proud to announce the upcoming launch of our groundbreaking threat modeling platform, FORK .
Stay tuned for more:
https://t.co/xz00vbwngm
#threatmodeling#appsec
LiteLLM’s release pipeline: compromised in March, compromised again in October.
The lesson isn’t “avoid AI libraries.” It’s that CI holds the keys to everything downstream, and most teams still don’t threat model it.
#SupplyChainSecurity#DevSecOps
AI pentest vs. human consultant, same app and same scope.
20 findings total. They agreed on 2.
Each caught what the other missed 👇
#PenetrationTesting#AppSec#AIinSecurity
The first ten HIPAA settlements of 2025 all traced back to one thing: the risk analysis.
Finding vulnerabilities is half the job. Explaining what they mean for patient data is the other half 👇
PCI DSS 4.0, DORA, and FedRAMP cover three different industries, but they’re all asking for the same thing: test as often as your systems change.
Here’s what each one expects 👇
Cisco SD-WAN, Citrix, Atlassian: attackers keep hitting the infrastructure everything else trusts. Map your trust boundaries before they do.
#infosec#zerotrust
Patched ≠ clean. Web shells are surviving firmware updates on 1,200+ patched Citrix NetScaler devices. If you patched, hunt for persistence and rotate creds. #Citrix#infosec
Healthcare threat modeling should do more than produce a ranked list of vulnerabilities.
A useful risk assessment needs to explain how technical findings affect PHI, patient care, availability, and the application’s actual trust boundaries. It also needs to stay current as architecture, integrations, testing results, and threat intelligence change.
PASTA helps by establishing business and clinical context before technical analysis begins, giving teams a consistent way to connect findings to impact rather than relying on generic severity alone.
For healthcare AppSec teams, the objective is not more findings. It is a defensible, current explanation of risk.
Read the full article in the first comment.
#HealthcareSecurity #ThreatModeling #AppSec #PASTA
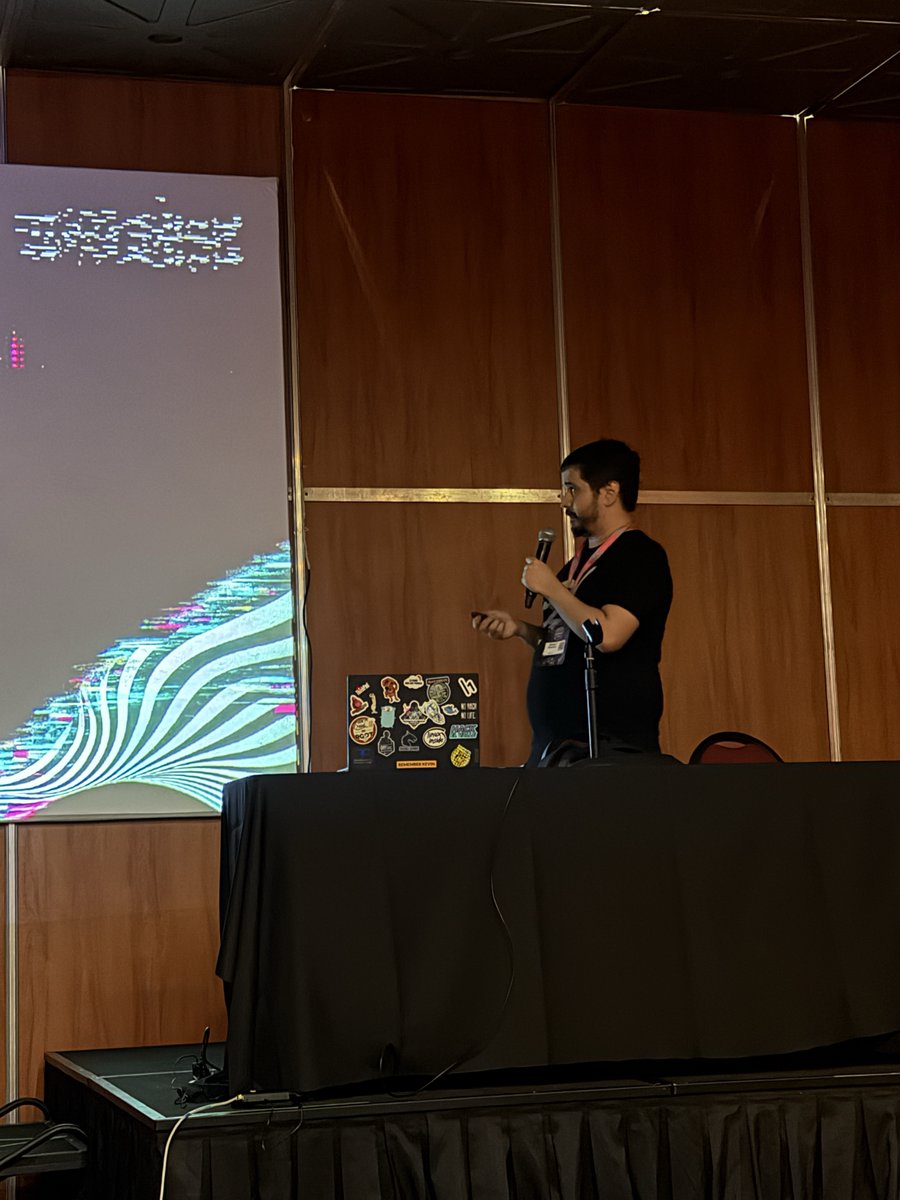
That’s a wrap on #Ekoparty 2026 🔪 Congrats to Oxguardians, provart & Mortadela’s, our Red Team Space CTF champions! Thanks to everyone who competed, came to Matias Ramirez’s hardware hacking talk, and stopped by to meet Knife. ¡Hasta el año que viene! #CTF#VerSprite
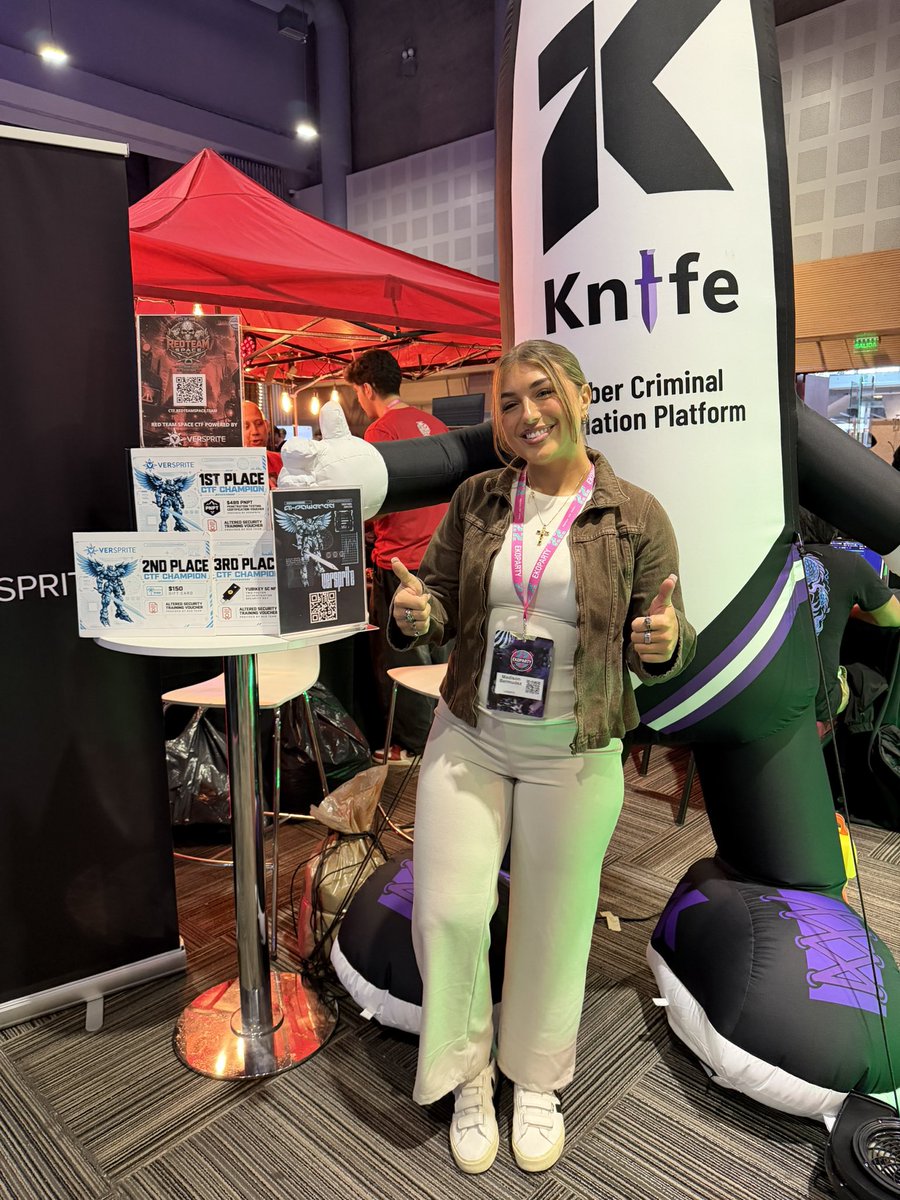
Knife emulates cyber criminals for a living. But in person? Total softie. 🤗
Come take a photo with our giant inflatable (and very huggable) Knife mascot at #ekoparty. Thumbs up guaranteed 👍
The energy at the CEC is still off the charts 🔥
Talks, villages, CTF, live hacking... the LATAM hacker community showed up BIG this year.
Last chance to catch it all today in Buenos Aires! #ekoparty
The competition is fierce! "La Moneda Estoica" is currently leading the CTF board, but there’s still plenty of time to catch them. Who's stepping up next? #ekoparty