I've shared the list of malicious models detected by MLTracer, along with a systematic analysis of techniques for evading existing model scanners, in the following GitHub repo.
https://t.co/cO0SCi3VOF
In short, the AI supply chain security field still likely has a lot of room for improvement.
Friends, @allthingsida was a fun experiment while it lasted.
The account is now parked and links to @BinaryWizards.
The AllThingsIDA YouTube channel will no longer receive updates. Going forward, new videos will be published on the Binary Wizards channel:
https://t.co/v51kMGVASA
I’m still focused on learning, teaching, and sharing what I find interesting. The difference is that the scope is now broader than just IDA. Expect workshops, training courses, videos, articles, and discussions covering reverse engineering, binary analysis, low-level programming, systems, tooling, and other topics that fit under the Binary Wizards umbrella.
Thanks to everyone who followed AllThingsIDA. I hope you’ll continue the journey with me at BinaryWizards.
@mopisec and I are thrilled that our training has been accepted for HITCON Training 2026!
https://t.co/VZyOEXyz9f
Join us for a deep dive into reversing Rust malware and Rust internals through hands-on labs and real-world samples.
#HITCON#ReverseEngineering#Rust#Malware
📣 The VB2026 programme is live!
Three days. Many voices. One Seville. 🇪🇸
Explore the sessions, speakers and ideas shaping this year’s event, and start planning your VB2026 experience.
📍 Seville, Spain
📅 14–16 October 2026
View the full programme 👉 https://t.co/eXY8T9oqUL
Call for Papers is now open for #VB2026!
We're looking for engaging, insightful, and original talks for the 36th VB Conference, taking place 14–16 October 2026 in Seville, Spain 🇪🇸
📅 Deadline: 9 April 2026
📝 Submit your abstract 👉https://t.co/ZxKMxHznWw
Missed a session? Or want to relive your favourite #VB2025 moments?
The VB2025 presentation playlist is now live on YouTube.
Catch up on 49 talks now available to watch for free.
👉 https://t.co/cSwUj8NROF
(Some talks are not included at the request of the speakers)
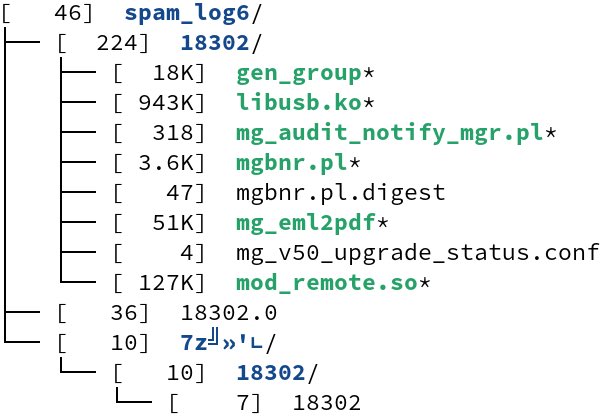
#ESETresearch discovered unique toolset, we named QuietEnvelope, targeting the MailGates email protection system of Taiwanese company OpenFind. The toolset was uploaded in anarchive, named spam_log.7z, to VirusTotal from Taiwan 🇹🇼. It contains Perl scripts, three stealthy passive backdoors, an argument runner, and miscellaneous files. 1/7
We are excited that we were once again part in the coordinated international operation #OpEndgame 📣, taking action against the notorious information and credential stealer #Rhadamanthys 🕵️ We assisted in the takedown of threat actor infrastructure and share a full list of #Rhadamanthys botnet C2s on ThreatFox 🦊
Full list of Rhadamanthys botnet C2s:
📡https://t.co/ttLmj6dpRs
Europol press release:
🚨 https://t.co/DUXXmrHR37
My latest blog post about a campaign exploiting the LANSCOPE vulnerability (CVE-2025-61932) has been published. / BRONZE BUTLER exploits Japanese asset management software vulnerability – Sophos News https://t.co/5MRWjeEy3r
Found ELF_PLEAD / SSHTD (aarch64) samples uploaded to VirusTotal in June 2025. Might be used for campaign in 2024.
#BlackTech#APT#malware#iocs
a653ae9e9906c0e5a5b5ba6330e10c9bb6b42e71abd6e80198eaa1386ea03cfb
- Campaign Code: x240129-1
- C2: csp.fortinetline[.]com:443
(1/2)
Last chance to share your research at VB2025.
Whether you have fresh research, practical insights, or real world case studies to share, now is your moment to step into the spotlight.
📅 24 Aug 2025 — only 5 days left
📍 Berlin. 24–26 Sept 2025
👉 https://t.co/1voLDwMafT