Friends, @allthingsida was a fun experiment while it lasted.
The account is now parked and links to @BinaryWizards.
The AllThingsIDA YouTube channel will no longer receive updates. Going forward, new videos will be published on the Binary Wizards channel:
https://t.co/v51kMGVASA
I’m still focused on learning, teaching, and sharing what I find interesting. The difference is that the scope is now broader than just IDA. Expect workshops, training courses, videos, articles, and discussions covering reverse engineering, binary analysis, low-level programming, systems, tooling, and other topics that fit under the Binary Wizards umbrella.
Thanks to everyone who followed AllThingsIDA. I hope you’ll continue the journey with me at BinaryWizards.
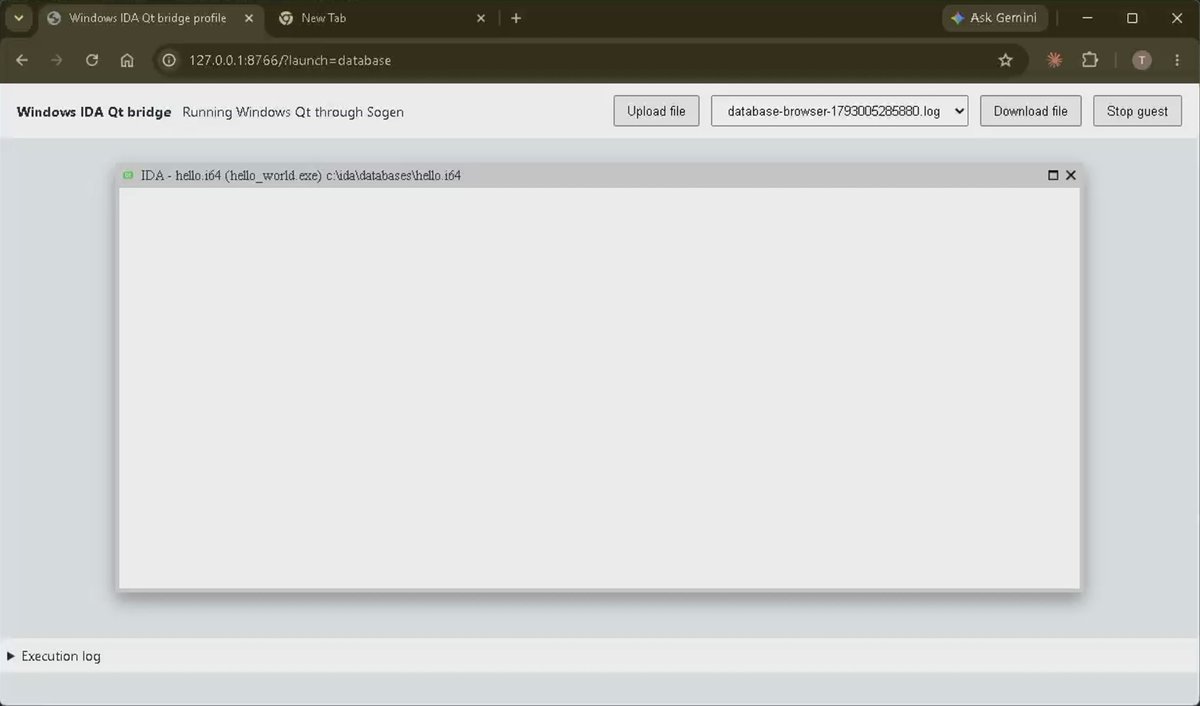
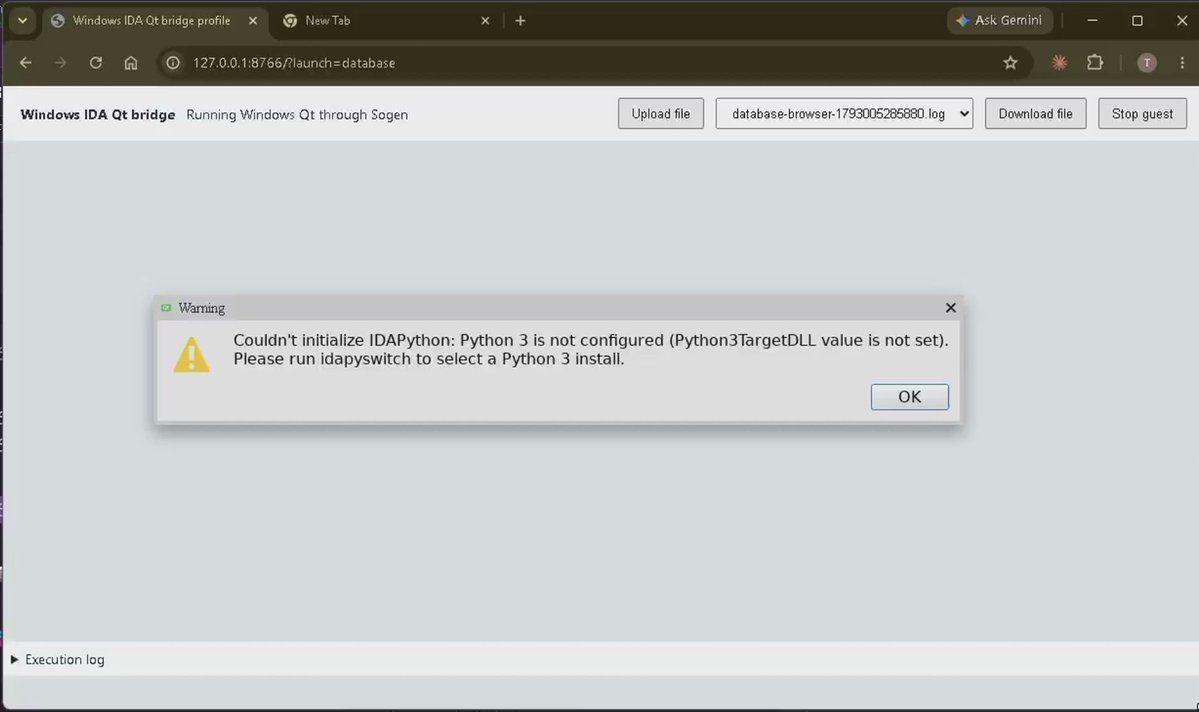
IDA via WebAssembly + Sogen (Unicorn backend).
Very slow. Trust me it works, but I don't have the patience to wait 30 minutes for the full UI to load ;) I will post one tomorrow. If IDA did not waste cycles, this would be usable TBH :P
But yeah, you can technically run full IDA (Windows) from your web browser (iPhone, iPad, PC, etc.) with this combo.
IDA or any Windows app for that matter. No rocket science.
@momo5502
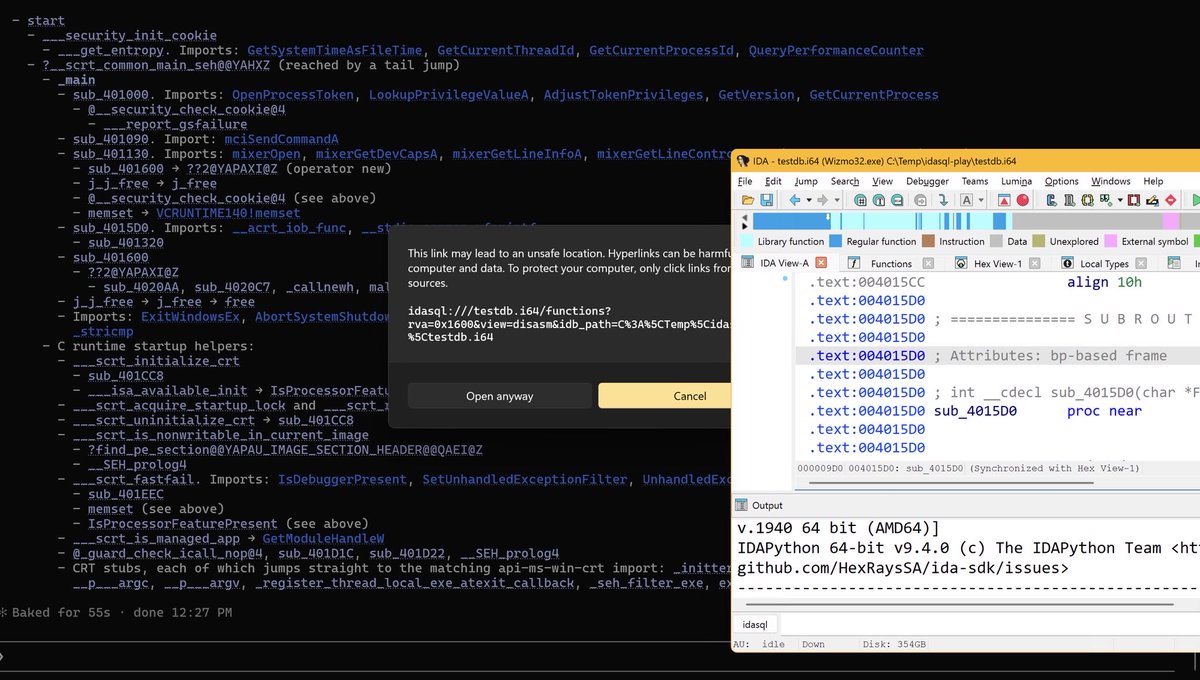
Noticing @momo5502 new PR for Sogen https://t.co/5jGMmiX3Y2 , I had a private patch for that but for KVM from a couple weeks ago! :)
IDA + Sogen + Linux/KVM backend
Cool project for AI/vibe reverse engineering .net apps built on top of libxsql and inspired by IDASQL and GhidraSQL by Rakan AlDuwaysan.
Give your AI agent this tool and see it RE smoothly.
https://t.co/oAI3HfwB8i
I've been happily and productively collaborating with @radareorg and the team for a while now, and I'm excited to announce that **r2xsql is finally live!**
R2 was already incredibly feature-rich and AI-friendly, but now you can also let your AI agents interact with R2 databases using SQL queries compatible with the xSQL family (like IDASQL, GhidraSQL and Binary Ninja SQL)
https://t.co/WZt5UGVTxs
Huge thanks to @radareorg and the team for this opportunity!
I made a bunch of videos on IDASQL but still I get asked: what’s the difference between it and IDA MCP and that if it does not have the word “MCP” in it then it must be some slop or something ;)
Maybe I should put IDASQL and IDA MCP side by side and post the results ;)
13 seconds.
It will help dispel the misconception about IDASQL and show its true power and flexibility.
Some folks, if they don’t see the word “MCP”, they become so dismissive. :(
And hey, if you don’t like IDA, GhidraSQL is equally powerful and we’ll maintained. Just give it to your AI agent and go touch grass. It just works ;)
Under the hood: libghidra 0.0.8 adds program options, transaction history and cancellable analysis jobs to its C++, Python and Rust clients. The ghidrasql agent skills are updated to match.
https://t.co/rTq9Kpucec
ghidrasql 0.0.7 is out: control Ghidra's auto-analysis from SQL.
UPDATE program_options to turn analyzers off, INSERT INTO analysis_passes to re-run analysis, DELETE to cancel it. Or skip slow analyzers at import with --analyzers-off.
https://t.co/z0D4eu7ohH
@inflearner Great write-up! IDASQL can do a lot more than export function names and sizes. Its multi-database support, xrefs, call graphs, decompiler queries, type recovery, and annotations could handle most of this patch-diffing workflow.
Stop reverse engineering by hand.
New video: I introduce IDASQL, the first tool in the xSQL family. It exposes IDA Pro's database and API as live SQL, so your AI agent can query a binary the way it queries a database.
Headless RE, source recovery, multi-binary queries.
https://t.co/LEB3uvgJ2k
@inflearner Now you can do the same for just the tokens cost too, no other licensing fees needed: Vibe Reverse Engineering #2: GhidraSQL, all you need to know!
https://t.co/4vv11ugf92
Vibe Reverse Engineering #2: GhidraSQL, all you need to know!
Multiple binaries at once, type recovery, source recovery back to disk, database annotation, headless workflows, and a few real Windows security research scenarios.
https://t.co/9MJ0w7uJC8
For the Windows research examples, I use kernel drivers, vulnerable drivers, and at one point casually pick the Windows hypervisor with basically no prior knowledge just to see how far the workflow can take it.
And yes, there is a frontier-model rant in there too.