@gopakumj@bihar_police@samrat4bjp@PatnaPolice बोया पेड़ बबूल का तो आम कहाँ से होए
Aur lo ₹10k aur becho vote, aur isse man bhar jaye to religion aur caste pe de dena, jb mukhiya hi apraadhi hoga to Gundagardi to badhega hi
A malicious release of LiteLLM on PyPI stole passwords and keys from machines, even if your code never used LiteLLM. Here is how it worked...
First, how it got in. The attacker added one line to the build config: `data = "cook"`. That line caused three extra files to be included in the package during the build. The public GitHub repository did not contain this line, so the source code looked clean. Only the published package was malicious.
Second, why it ran without being imported. Python has a feature where a `.pth` file in `site-packages` can execute code every time Python starts. The attacker added a `cook.pth` file containing a single line: `import cook`. From that point on, almost any Python process on the machine could trigger the stealer: your app, pip, your editor, or your CI jobs.
Third, what it stole. It went after almost every secret a developer machine might have:
- SSH keys and shell history
- AWS, Azure, GCP, k8s, and GitHub credentials
- Claude Code, Cursor, and Codex Keys
- Saved browser passwords
- Environment variables
- LLM API keys stored in a LiteLLM proxy database
Fourth, how it pushed data out. It encrypted everything so that only the attacker could decrypt it, then uploaded it to a `/healthcheck` URL, making the traffic look like a routine health check.
Turns out, we cannot trust the source repository alone.
We need to also, pin package versions (classic) with hashes, give new releases time to be scrutinized before adopting them, and inspect the actual artifacts you install.
Security is more critical than ever! The software supply chain is a different beast. You can audit every line in a repository and still end up running malicious code.
Interesting times.
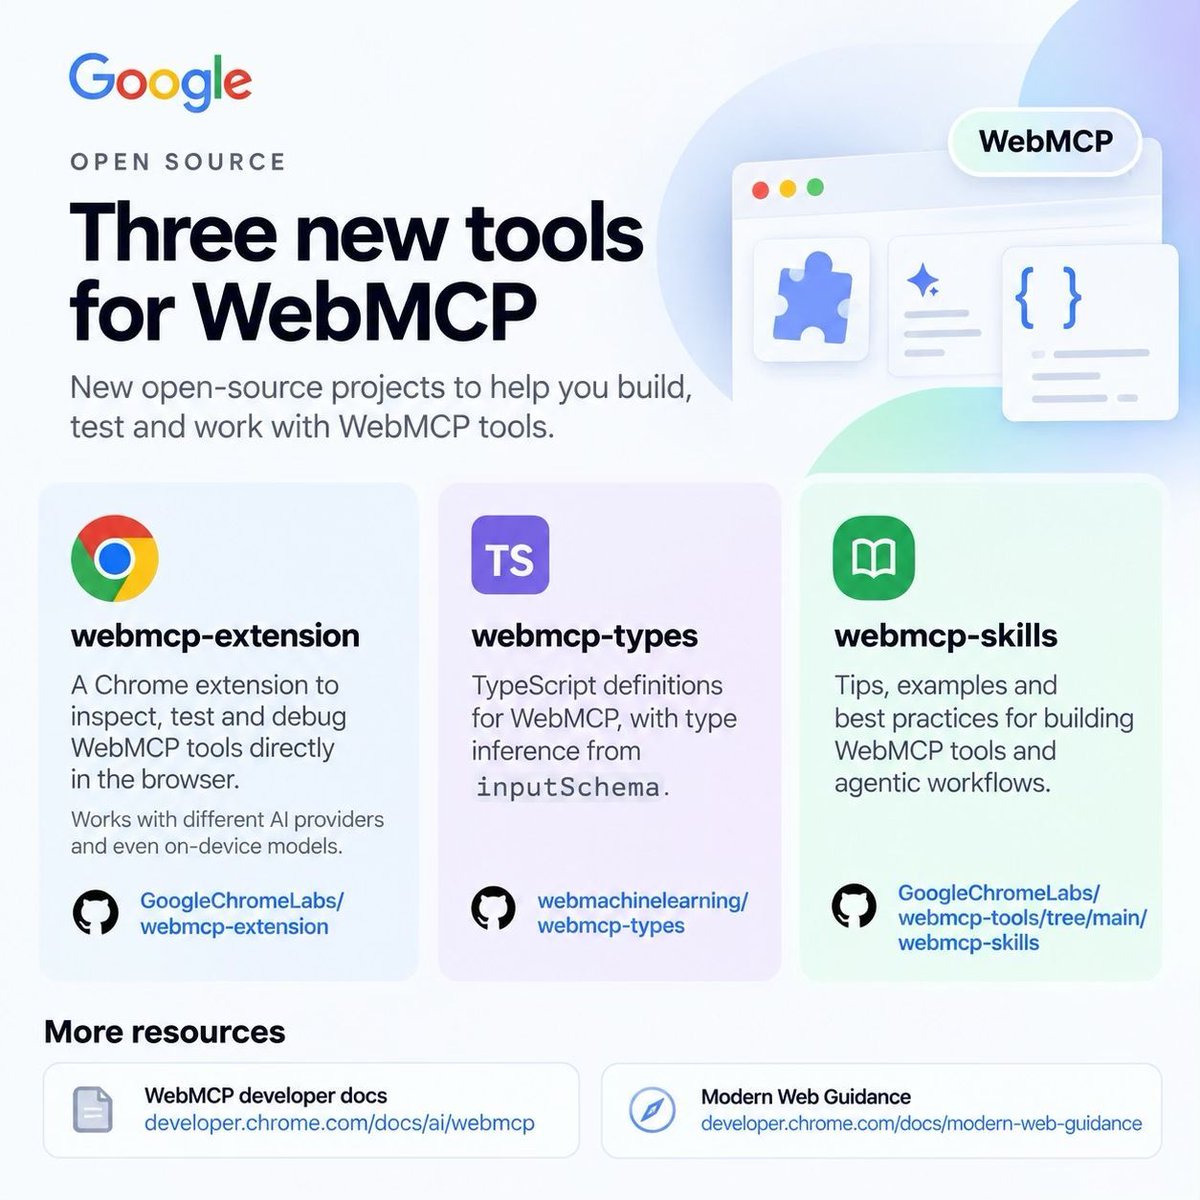
We have presents for you! 🎁
- A new WebMCP Skill with best practices for security, development, & consequential flows
- WebMCP Types: TypeScript definitions, with type inference from InputSchema
Give em to your agent, it helps scaffold out WebMCP so fresh and so clean clean
I love how anpad BJP goons and some Silicon Valley right wing bros both got offended by this tweet.
Goes to show that having the ability to write code isn't the pinnacle of intellectual achievement.
People in tech need to get more into Humanities.
2047 age in years
Modi 97
Rajnath 96
Jaishankar 92
Gadkari 90
Nirmala 88
Amit Shah 83
Good luck people 👍
They will answer all your queries and give solutions in 2047 ... please do not disturb till then
@yadavpawan1307@CaVivekkhatri Hmm, Elon will himself do the setup
Any tech is good, if we cant make it, we dont need to block them bcz our Govt wants to protect the interests of Gujarati chanda donors