If you recently started following this account & interested in Offensive Security #offsec, then plz check my Offensive Software Exploitation Course below. There is more than 8h of recorded content & everything could be downloaded from my Github repo too.
https://t.co/dGD92g8yEG
The agenda of the EU ATT&CK Workshop on 22 October is online: https://t.co/Zwwohx3FiF. Super lineup and packed with inspiring lightning talks. Participation free but registration required. @MITREattack@sigma_hq@circl_lu@CERTEU @MITREengenuity
When people cry about offensive tools with no practical solutions or acknowledging how they are used today it’s simply the Nirvana fallacy, glossing over the details of our real world and expecting a perfect one: https://t.co/qkb1YRCXL9
One lesson that I see to folks new and old in the industry struggle with is:
Remaining humble and recognizing that you are always learning and need to continue to learn from others.
Trust me, you don't know everything, and never will.
Be humble, kind, and help others.
A wise man once said: "the more you know, the more you realise you don't know". Our industry has the toxic attitude of "achieve and brag about it", which can erase people humility. No matter how good you think you are, there is always space for growth
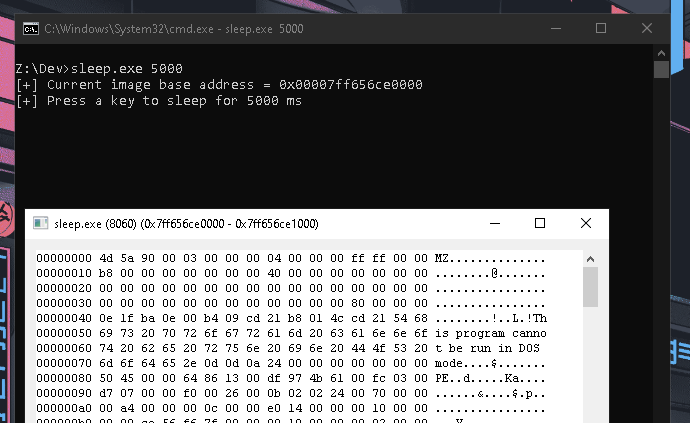
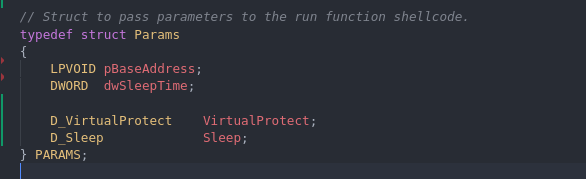
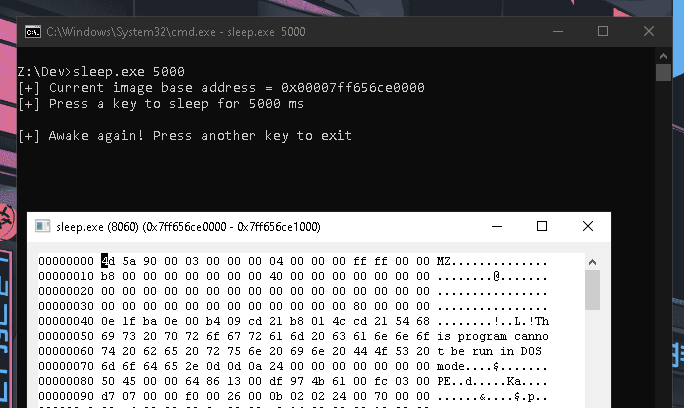
Had a lot of fun playing with SleepyCrypt by @SolomonSklash. Even modified the original code to pass the WINAPI functions ( VirtualProtect and Sleep ) to the shellcode so that it doesn't need to load them dynamically. In that way, I managed to reduce the shellcode to 1k bytes.
My personal favorite Cypher query:
MATCH p=(n:Group)-[:AdminTo*1..]->(m:Computer) WHERE not n.admincount RETURN DISTINCT n[.]name, n.admincount, COUNT(m[.]name) ORDER BY COUNT(m[.]name) DESC.
(Remove the brackets [])
I made a post about research I did recently for fun on learning how to encrypt the Cobalt Strike heap. https://t.co/x3XZF4XS2H
Learned a lot of interesting things along the way and I'd like take it further.
Special Thanks to: @_ForrestOrr@ilove2pwn_ and @MrUn1k0d3r for the help
Lots of free virtual training days coming up! Some include free exams such as the azure fundamentals exam.
Be brave and learn something new. Details below 👇
Microsoft Virtual Training Days https://t.co/4Ab4xgjVhp
WerFault.exe is not only a common FP for process creation ("any" proc that crash spawn werfault.exe), but also ImageLoads related detections (i.e monitoring unusual abc.dll loads, if a process that normally loads abc.dll crashes then WerFaut.exe will be logged as loading abc.dll
I’m looking to give away a voucher for the #OSCP PEN-200 w/ 30 day lab access ($999 value) for those in #InfoSec looking to grow their career! To enter for a chance to win, make sure to follow me AND retweet or like. The winner will be randomly selected on October 1st!
[thread] Isn't it annoying when you have a working shellcode, but the wrong rights in the spawned shell ? Newer versions of UNIX shells no longer transfer SUID rights by default. Here is the shells affected by this, as well as a new shellcode for tclsh:
https://t.co/TLbdjahuES
In tomorrow's stream, we will dive into the inner workings of the SharpCollection project. Sharing my pipeline template so you can set up your own auto compiling pipeline. Join me Sunday at 16:00 UTC ( 12:00 EDT ) https://t.co/WH6HfeoTDJ
Learning about cybersecurity technology?
This (free) interactive guide teaches basics of information security/cybersecurity + history/evolution using the Microsoft Cybersecurity Reference Architecture (MCRA) capabilities diagram. (~36 minute course)
https://t.co/10PyafoEFF