XDRIP Academy is free, and you can read Year One without making an account.
Not sure where to start? The 20-minute placement check shows your level across six areas of self-custody and security, so you can skip what you already know. https://t.co/OYvHNsuBXP
When a wallet or exchange makes the news for a breach, a second wave follows. Fake emails and texts from "that company" ask you to verify or migrate your wallet right away.
Don't click. Open the app or type the site yourself, and never enter your recovery phrase anywhere.
If something happened to you, would your family find your crypto, and reach it without getting scammed?
Jim's Digital Asset Inheritance Guide lays out a plan in six steps, with worksheets that never ask for a seed. Educational, not legal advice.
https://t.co/6MuWDowPcU
Thousands of Keplr wallets were exposed, and not one victim lost a seed phrase. They never had one.
On Nov 6, some Keplr users who signed in with Google or Apple found their wallets drained. Here's what happened, and the one rule every digital asset holder should take from it.
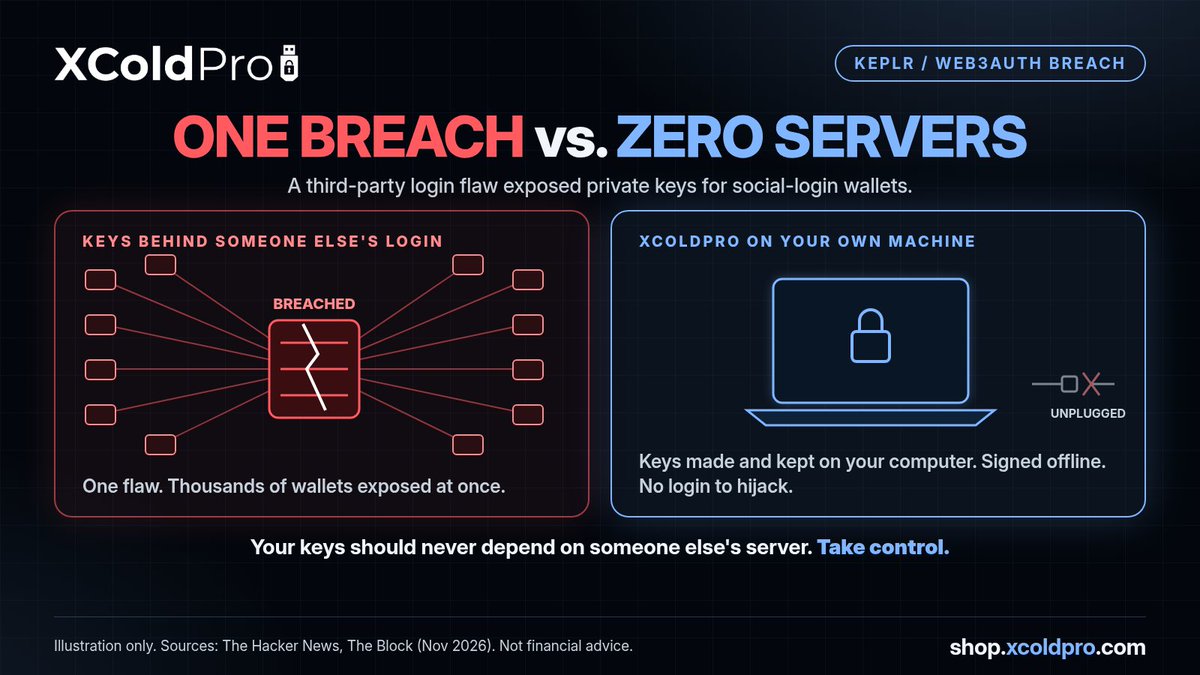
1/ Keplr let users skip the seed phrase and log in with Google or Apple. That sign-in ran through a third-party company, Web3Auth. Keplr says a flaw at Web3Auth led to a "private key breach" for some of those users.
2/ Whoever holds a private key can move the money. An attacker got in first. Web3Auth then used the same path to sweep other at-risk wallets into its own recovery wallets before the attacker reached them. Its 12 recovery addresses held about $5.6M as of Nov 8 (The Block).
3/ So how much was actually stolen? Nobody has published a full number. GoPlus puts confirmed theft at $1M or more. Bitquery first counted $6.01M leaving more than 44,000 wallets, then corrected that most of it went to the recovery wallets. Keplr's co-founder estimates about 20% of Google and Apple login accounts were affected.
4/ Keplr paused Google and Apple sign-in and told users to move their funds. Wallets made with a recovery phrase or a hardware wallet were not affected. Only the "convenient" logins got hit.
5/ The lesson: your keys should never depend on someone else's server. When a company sits between you and your key, one flaw on their side puts thousands of wallets at risk at once, and even the rescue means someone else is holding your money.
6/ That's what XColdPro is built for:
🔒 Your key is created and kept on your own computer, and no third party ever holds a piece of it
🚫 No Google or Apple login to hijack
📴 Transactions are signed offline, with a network kill switch
🛡️ There's no central server to breach, so attackers would have to go after users one machine at a time
7/ Convenience is how they get you. Take control of your digital assets.
🔐 XColdPro: https://t.co/T4GIrx2Iyt
🛒 Shop: https://t.co/7IXIg2jotD
📘 2026 Inheritance Guide: https://t.co/X2yh9HKNP4
❄️ Frost Elite: https://t.co/b3eS5tdxb5
💧 XDRIP: https://t.co/5AUQhjcfyy
🧩 Solutions: https://t.co/oQ30EWgRMF
🌐 XDRIP Central: https://t.co/Q3mCyrquRH
📰 Get the weekly security brief: https://t.co/Nta5tNRkZ1
Sources: https://t.co/fkWbfDHeDm | https://t.co/iajrUXPjNX
We're live now on The Drip Report.
Watch right here on X, or on Rumble and YouTube. Brad, Flo, Jim and Liam are taking questions from chat in plain language.
Jump in while we're on. With @FlorianoRighett, @XColdProCDO and @Hog_192.
ONE TIRED CLICK SHOULD NOT BE ABLE TO EMPTY YOUR WALLET.
Think about how most people hold digital assets. One device. One person. One approval. If that person is rushed, tricked, pressured or just having a bad night, the money is gone and there is no undo button on a blockchain.
Businesses solved this problem decades ago. Big payments need two signatures. Your digital assets deserve the same rule.
That is what the Citadel Protocol in XColdPro does.
Here is how it works:
1. You set the rule. For example, any 2 of 3 devices must approve before a transaction can be finalized.
2. Each approval is a signature over the exact transaction, made with a separate identity key on each cosigner's device. Change one detail and the approval no longer matches.
3. XColdPro checks every signature at finalization. It verifies them, it does not just count them.
4. Proposals and approvals move offline, by QR code or USB. No server. No API. No smart contract in the path.
5. It runs on all 22 supported networks, including chains that have no multisig of their own.
Straight talk on what it is and is not: Citadel is enforced by XColdPro on your own devices, not by the blockchain. Anyone holding the seed can still spend outside the app, so protect the seed too. Want a threshold Bitcoin itself enforces? The BTC Edition builds a P2WSH multisig vault validated by Bitcoin consensus (beta, not on sale yet; follow and reply "beta").
Who this is for: partners who share a treasury, families who want a second set of eyes, and anyone who knows a single point of approval is a single point of failure.
Citadel ships in the Nyxor edition of XColdPro.
Stop letting one click decide everything. Get Nyxor: https://t.co/7IXIg2jotD
The 2026 Digital Asset Inheritance Guide: https://t.co/X2yh9HKNP4
XColdPro shop: https://t.co/7IXIg2jotD
XColdPro: https://t.co/T4GIrx2Iyt
Frost Elite ambassador program: https://t.co/b3eS5tdxb5
XDRIP: https://t.co/5AUQhjcfyy
XColdPro solutions: https://t.co/oQ30EWgRMF
XDRIP Central: https://t.co/Q3mCyrquRH
Get the weekly security brief: https://t.co/Nta5tNRkZ1
Source: https://t.co/uhLynqaghe. Not financial advice.
BREAKING: 🇺🇸 COINBASE JUST RECEIVED FULL FEDERAL APPROVAL TO OPERATE AS A NATIONAL TRUST BANK
THE BIGGEST US EXCHANGE IS NOW A REGULATED BANK
WALL STREET IS COMING FOR #BITCOIN
THIS IS MASSIVE 🚀
IF YOUR BITCOIN KEYS LIVE ON A MACHINE THAT IS ALWAYS ONLINE, YOU ARE ALREADY ON SOMEONE'S LIST.
Here is what that list looked like last week.
Between October 30 and November 2, blockchain analytics firm Bitquery traced 18.38 BTC and 3,405 LTC swept out of BTCPay Server hot wallets. 682 separate sweeps. About $1.63 million. 87% of it moved in a single afternoon and evening.
Attackers exploited a known vulnerability on outdated servers. The spending keys sat on machines that never went offline, and someone came and took what they unlocked.
Now read the line that matters. BTCPay Server's own incident report says funds in wallets whose spending keys were held off the server were unaffected.
Keys off the machine. Signing offline. That is the whole game.
So we built a Bitcoin-only edition of XColdPro around exactly that. One chain, on purpose. Fewer moving parts in the signing path.
XColdPro BTC Edition:
1. Air-gapped signing. Your keys are created and used offline, on a storage device you supply.
2. PSBT (BIP174). Build the transaction in Sparrow, Specter or Bitcoin Core, sign it offline in XColdPro, broadcast from the online side.
3. Your own node. Point it at your own Esplora or mempool endpoint instead of someone else's infrastructure.
4. Watch-only export for Sparrow, Electrum, Specter and Bitcoin Core, so you can watch balances without exposing a key.
5. Multisig enforced by the Bitcoin network itself (P2WSH M-of-N), not by an app's promise.
6. Standard derivation: BIP44, BIP49, BIP84 and BIP86 address types, Taproot key-path signing.
7. Coin control and RBF fee bumping. Spend the exact coins you pick.
8. Optional dice entropy, mixed with the operating system's generator, so you can add your own randomness to your seed.
9. Lazarus inheritance protocol and SeedVault Shamir backup, so your Bitcoin outlives one sheet of paper and one person.
10. No account. No sign-up. No telemetry.
Status, straight: the BTC Edition beta is ready. It is not on sale yet, and we are opening it to testers first.
Want in? Follow this account and reply "beta" below. That is the list you want to be on.
Holding more than Bitcoin? The multi-chain editions of XColdPro are available right now: https://t.co/7IXIg2jotD
Sources: Bitquery investigation and BTCPay Server incident report. Not financial advice.
Get the weekly security brief: https://t.co/Nta5tNRkZ1
ONE SHEET OF PAPER IS ONE POINT OF FAILURE.
Fire. Flood. Theft. The wrong person opening the right drawer. If your entire recovery phrase lives in one place, that place owns your digital assets.
Making more copies does not fix it. Every copy is another complete key. You just multiplied the places someone can find you.
XColdPro's SeedVault changes the shape of the problem.
Here is how it works:
1. SeedVault splits your recovery phrase with Shamir secret sharing.
2. You choose the threshold. For example, any 3 of 5 shares reconstruct the wallet.
3. Fewer than the threshold reveal nothing usable. That is a property of the math, not a policy you hope people follow.
4. Put shares in different places, or with different people. No single location, disaster or individual is enough to lose the wallet or take it.
Be honest about what this is and is not. SeedVault is built for losing a seed, not for someone who already holds enough shares. Protect the shares you create.
SeedVault ships in the Nyxor edition of XColdPro, and in the BTC Edition (beta, not on sale yet).
Stop betting everything on one piece of paper. Get Nyxor: https://t.co/7IXIg2jotD
The 2026 Digital Asset Inheritance Guide: https://t.co/X2yh9HKNP4
XColdPro: https://t.co/T4GIrx2Iyt
Frost Elite ambassador program: https://t.co/b3eS5tdxb5
XDRIP: https://t.co/5AUQhjcfyy
XColdPro solutions: https://t.co/oQ30EWgRMF
XDRIP Central: https://t.co/Q3mCyrquRH
Get the weekly security brief: https://t.co/Nta5tNRkZ1
Source: https://t.co/vy5GWfjHsm. Not financial advice.
A wallet is only as safe as the device it sits on.
Two good habits when phone malware is in the news. Keep the phone updated. Keep long-term keys off a device that is online every day.
XColdPro keeps those keys on a machine that stays offline, so there is no live connection for malware to reach.
https://t.co/0TVDiSRZtq