Introducing XINTRA Enterprise Live!!!!
Real-world threat simulation with live infrastructure.
Our team took nearly 8 months to build it, and it's finally here :)
We designed it for SOC/IR teams, with the power to collect evidence, deploy your own tools, and assign tasks... along with:
🔹 Fully private infrastructure per customer
🔹 RDP into compromised systems
🔹 Sentinel + ADX integration
🔹 Deploy your own EDR/XDR
🔹 Velociraptor for forensic collection
🔹 Assign hosts to analysts
🔹 Insights hub for team performance
Enquires → [email protected]
https://t.co/d85AQVBxOK
You’re no longer confined to solving challenges inside a locked-down VM 😉.
With full internet access across all hosts, you can download evidence, upload files, and deploy any tool directly into the environment
@XintraOrg
Want to watch an electrical grid get hacked in real time? ;)
We simulated an electrical substation, then ran a Sandworm (APT44) inspired attack against it.
Starting with an edge device compromise, we moved through the IT network, crossed into OT, reached the substation controls and tripped the circuit breakers.
Watch the breakers open and the simulated city go dark.
https://t.co/T9Iafy31fJ
You can explore this environment in @XintraOrg Twin, and a version will also be published on Labs.
We found nearly 15,000 refrigeration and cool systems still exposed.
Several of them with control panels still internet exposed.
https://t.co/kdHuvH48T7
We are hiring a meme lord.
Can be part time, or casual.
Funny, 50% degenerate, has cyber experience.
Bonus points if they have ever been a discord mod.
Send interest here, with evidence of memes:
[email protected]
I started digging into Win32k callbacks while looking for a PatchGuard bypass. That lead went nowhere, but it raised a better question: how does the Windows kernel choose the callback for session-specific GUI work? https://t.co/vQTOPKNjDT 1/3
completed virus vipers: reconstructed a full breach from a phishing delivered shellcode loader through registry hive & LSASS credential dumping, VPN/RDP hopping from an MSSP into a client's network (supply chain attack), timestomping, and into data exfiltration. great lab @XintraOrg
#DFIR #IncidentResponse
completed waifu university. reconstructed a full breach from an Entra ID password spray and MFA fatigue through RMM abuse, a Cobalt Strike beacon, malicious service persistence, anti forensics, and into ransomware staging. great lab @XintraOrg
deep dive on the ransomware: https://t.co/gF0cUWJ66I
#DFIR #IncidentResponse
@inversecos reached out to me a few months ago to work on this APT28 lab, and I finally had the chance to collaborate with the legendary @ZephrFish to make it great and entertaining. And now it's LIVE! 👀
Really enjoyed analyzing Andy's emulation while building out the IR questions, especially regarding IoT compromise, ADCS, and the classic Outlook CVE.
Come check it out at XINTRA
https://t.co/7NviKXKX5m
#dfir #APT28
This lab is modeled on tradecraft associated with APT28, the Russian GRU-linked espionage group commonly tracked as Fancy Bear / Unit 26165.
The closest public analog is CISA’s May 21, 2025 advisory on Russian GRU targeting of Western logistics entities and technology companies supporting Ukraine.
https://t.co/CS8J2yqe9W
NEW LAB: Global Freight UA 🚛
We emulated a CISA report on APT28/Russian GRU targeting Ukrainian logistics .
This lab is packed with IoT compromise, CCTV and surveillance platform access with:
- Outlook / CVE-2023-23397 forced authentication
- HEADLACE-style staging + DLL sideloading
- AD CS abuse + certificate-based privilege escalation
- CCTV, IoT and camera compromise
- Anti-forensics techniques
Contributors
@ZephrFish@r3nzsec
Solve it here 👇
https://t.co/TJHYNhyWjM
After more than a year in the making it is finally out and available here: https://t.co/pN4XluF2vf :)
I will always do open source and publish papers but I've been working for a long time to create a course for people that want structured and in-depth content 1/
NEW XINTRA COURSE!!!🥳
Windows Kernel: Offensive, Defensive & Reverse Engineering by @Idov31
https://t.co/3qiJyib7ro
Build an EDR and rootkits from scratch while mastering the Windows kernel.
Over 70 videos and labs covering:
> Build your own EDR (detection + prevention)
> Rootkits & offensive tradecraft
> Reversing Windows kernel & drivers
> Kernel callbacks, ETW, minifilter and more
There are preview videos too if you wanna see some snippets of the course content ;)
This course is instructed by Ido Veltzman (@Idov31), a senior security researcher specializing in reverse engineering, operating system internals, vulnerability research, and exploit development.
His work spans UEFI, hypervisors, kernel, and user mode, where he has developed advanced evasion, persistence, and injection techniques.
@XintraOrg
Working on the upcoming @XintraOrg lab 🇷🇺 while shipping new features for the Mac timeline analysis tool.
Using these simulated attack scenarios to stress-test the gear before it hits the field. Almost there... 😅
#dfir#Xintra
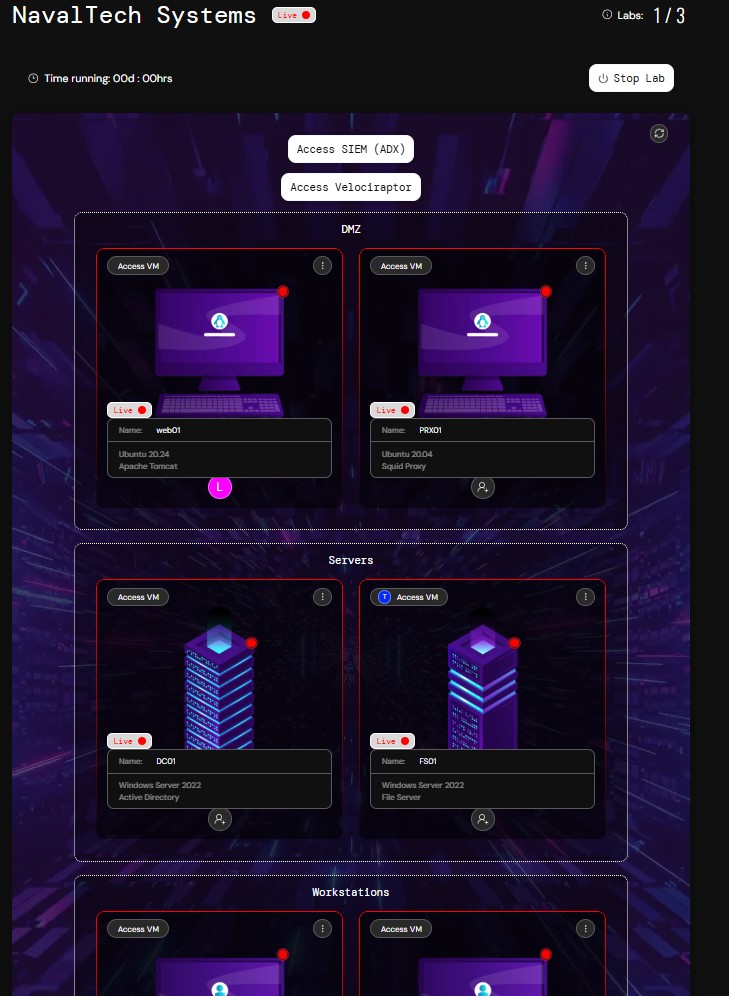
NEW LAB: NavalTech Defense Contractor ⚓
We emulated a North Korean (DPRK) cyber espionage campaign targeting a submarine contractor’s vessel-tracking systems.
Based on CISA’s reporting on DPRK operations to advance military and nuclear programs.
Contributors
@django88_@svch0st@XintraOrg
Solve it here 👇
https://t.co/3yo41LBhOh
What separates Chinese cyber ops from Five Eyes?
Three things that shifted my thinking about this topic:
1. Early cyber training (90s-2000s) happened on live targets.
Not sandboxes, not simulations...actual foreign infrastructure. The "practice" was the operation. Operational errors caught during IR back then weren't failures of tradecraft... they were the cost of learning on production.
2. The private sector operates as APT infrastructure.
Cybersecurity companies founded by former 2000s hackers (Topsec, i-SOON, Integrity Tech) were later publicly linked to state-directed operations. The line between "legitimate vendor" and "APT contractor" is deliberately blurred (by design).
3. Operators don't stay siloed in their APT group.
They rotate across teams for decades, carrying often the exact same tools, tactics with them. What we label as "different APT groups" is often the same people with different hats.
This makes attribution way messier than the tidy narrative we see in threat reports.
Worth reading this epic report published by the Zurich Centre for Security Studies if this stuff keeps you up at night:
https://t.co/aGgMyPniWF
We've been a little quiet on our end but we have some huge things cooking for 2026 that we can't wait to share with you.
We also have a new lab coming out in the next couple weeks 😏...
But in the meantime, enjoy this feedback we got today.